

CVE-2025-6563
 praksokchea/cve-2025-6563
Reflected XSS vulnerability in MikroTik Hotspot login page
educationvulnerability-analysisweb-application-exploitation+1
praksokchea/cve-2025-6563Reflected XSS vulnerability in MikroTik Hotspot login page
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier
 mcorybillington/suitecrm-rce
Writeup on CVE-2020-28328: SuiteCRM Log File Remote Code Execution plus some bonus Cross-Site Scripting
 simonschoeni/cve-2020-7247-poc
Proof of concept for CVE-2020-7247 for educational purposes.
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
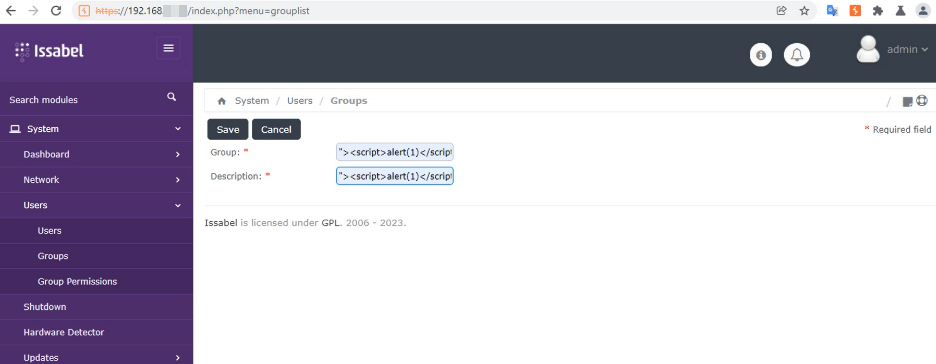 sahiloj/cve-2023-37191
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel PBX version 4.0.0-6. This allows an authenticated attacker to inject arbitrary…
 blueteamsteve/cve-2020-0601
Curated list of CVE-2020-0601 resources
 sahiloj/cve-2023-33732
CVE-2023-33732 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console, version…
 razielx64/cve-2025-69606-gsvoip-xss
Proof-of-concept for a reflected XSS vulnerability (CVE-2025-69606) in GSVoIP Web Panel v2.0.90, demonstrating unauthenticated arbitrary JavaScript…
 xmyronn/cve-2026-11518-xss
Proof-of-concept for unauthenticated stored XSS in SourceCodester Inventory System, demonstrating admin session hijacking via crafted registration…
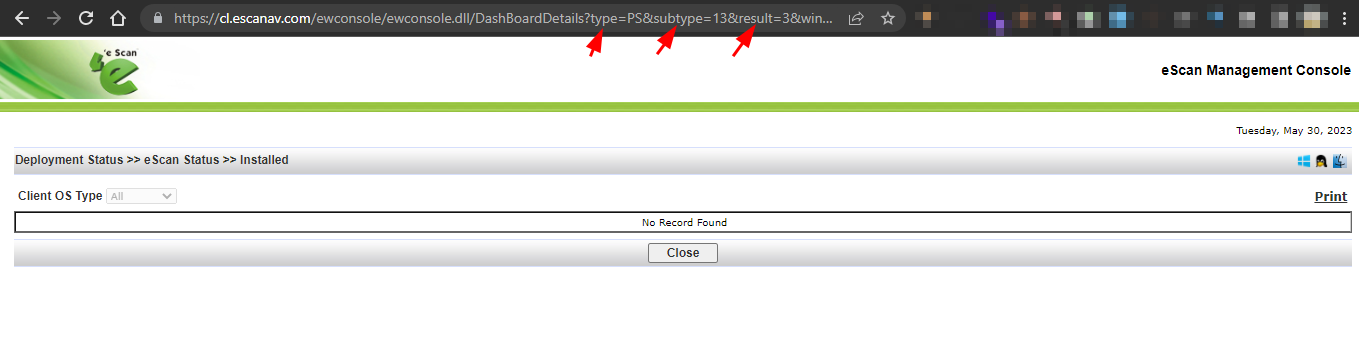 sahiloj/cve-2023-33731
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the eScan Management Console (version 14.0.1400.2281) developed by Microworld…
 dharmstm/cve-2026-30502-openkm-6.3.12-reflected-xss
Documentation and proof-of-concept for CVE-2026-30502, a reflected XSS vulnerability in OpenKM v6.3.12. Includes technical analysis, root cause,…
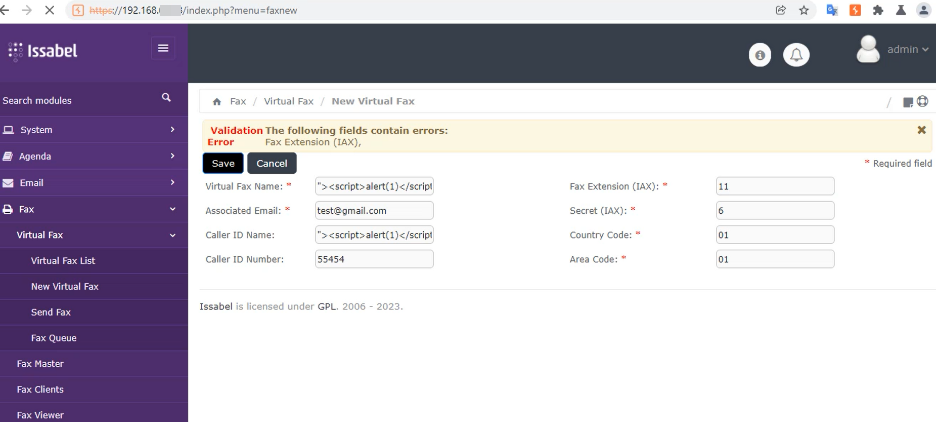 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
 anandjogawade/cve-2026-48849-roundcube-webmail-stored-xss
This repository documents CVE-2026-48849, a Stored Cross-Site Scripting (XSS), HTML Injection, and CSS Injection vulnerability discovered in…