2FA-Bypass-using-a-Brute-Force-Attack-CVE-2025-60424

Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…

Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…

Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…

CVE-2023-1665 - Twake App

Online hash checker for Virustotal and other services

Gets plaintext Active Directory credentials if you're on the internal network but outside the AD environment

Software to identify the different types of hashes -

A POSIX-compliant, fully automated WPA PSK PMKID and handshake capture script aimed at penetration testing

Nail in the JKS coffin - Cracking passwords of private key entries in a JKS file

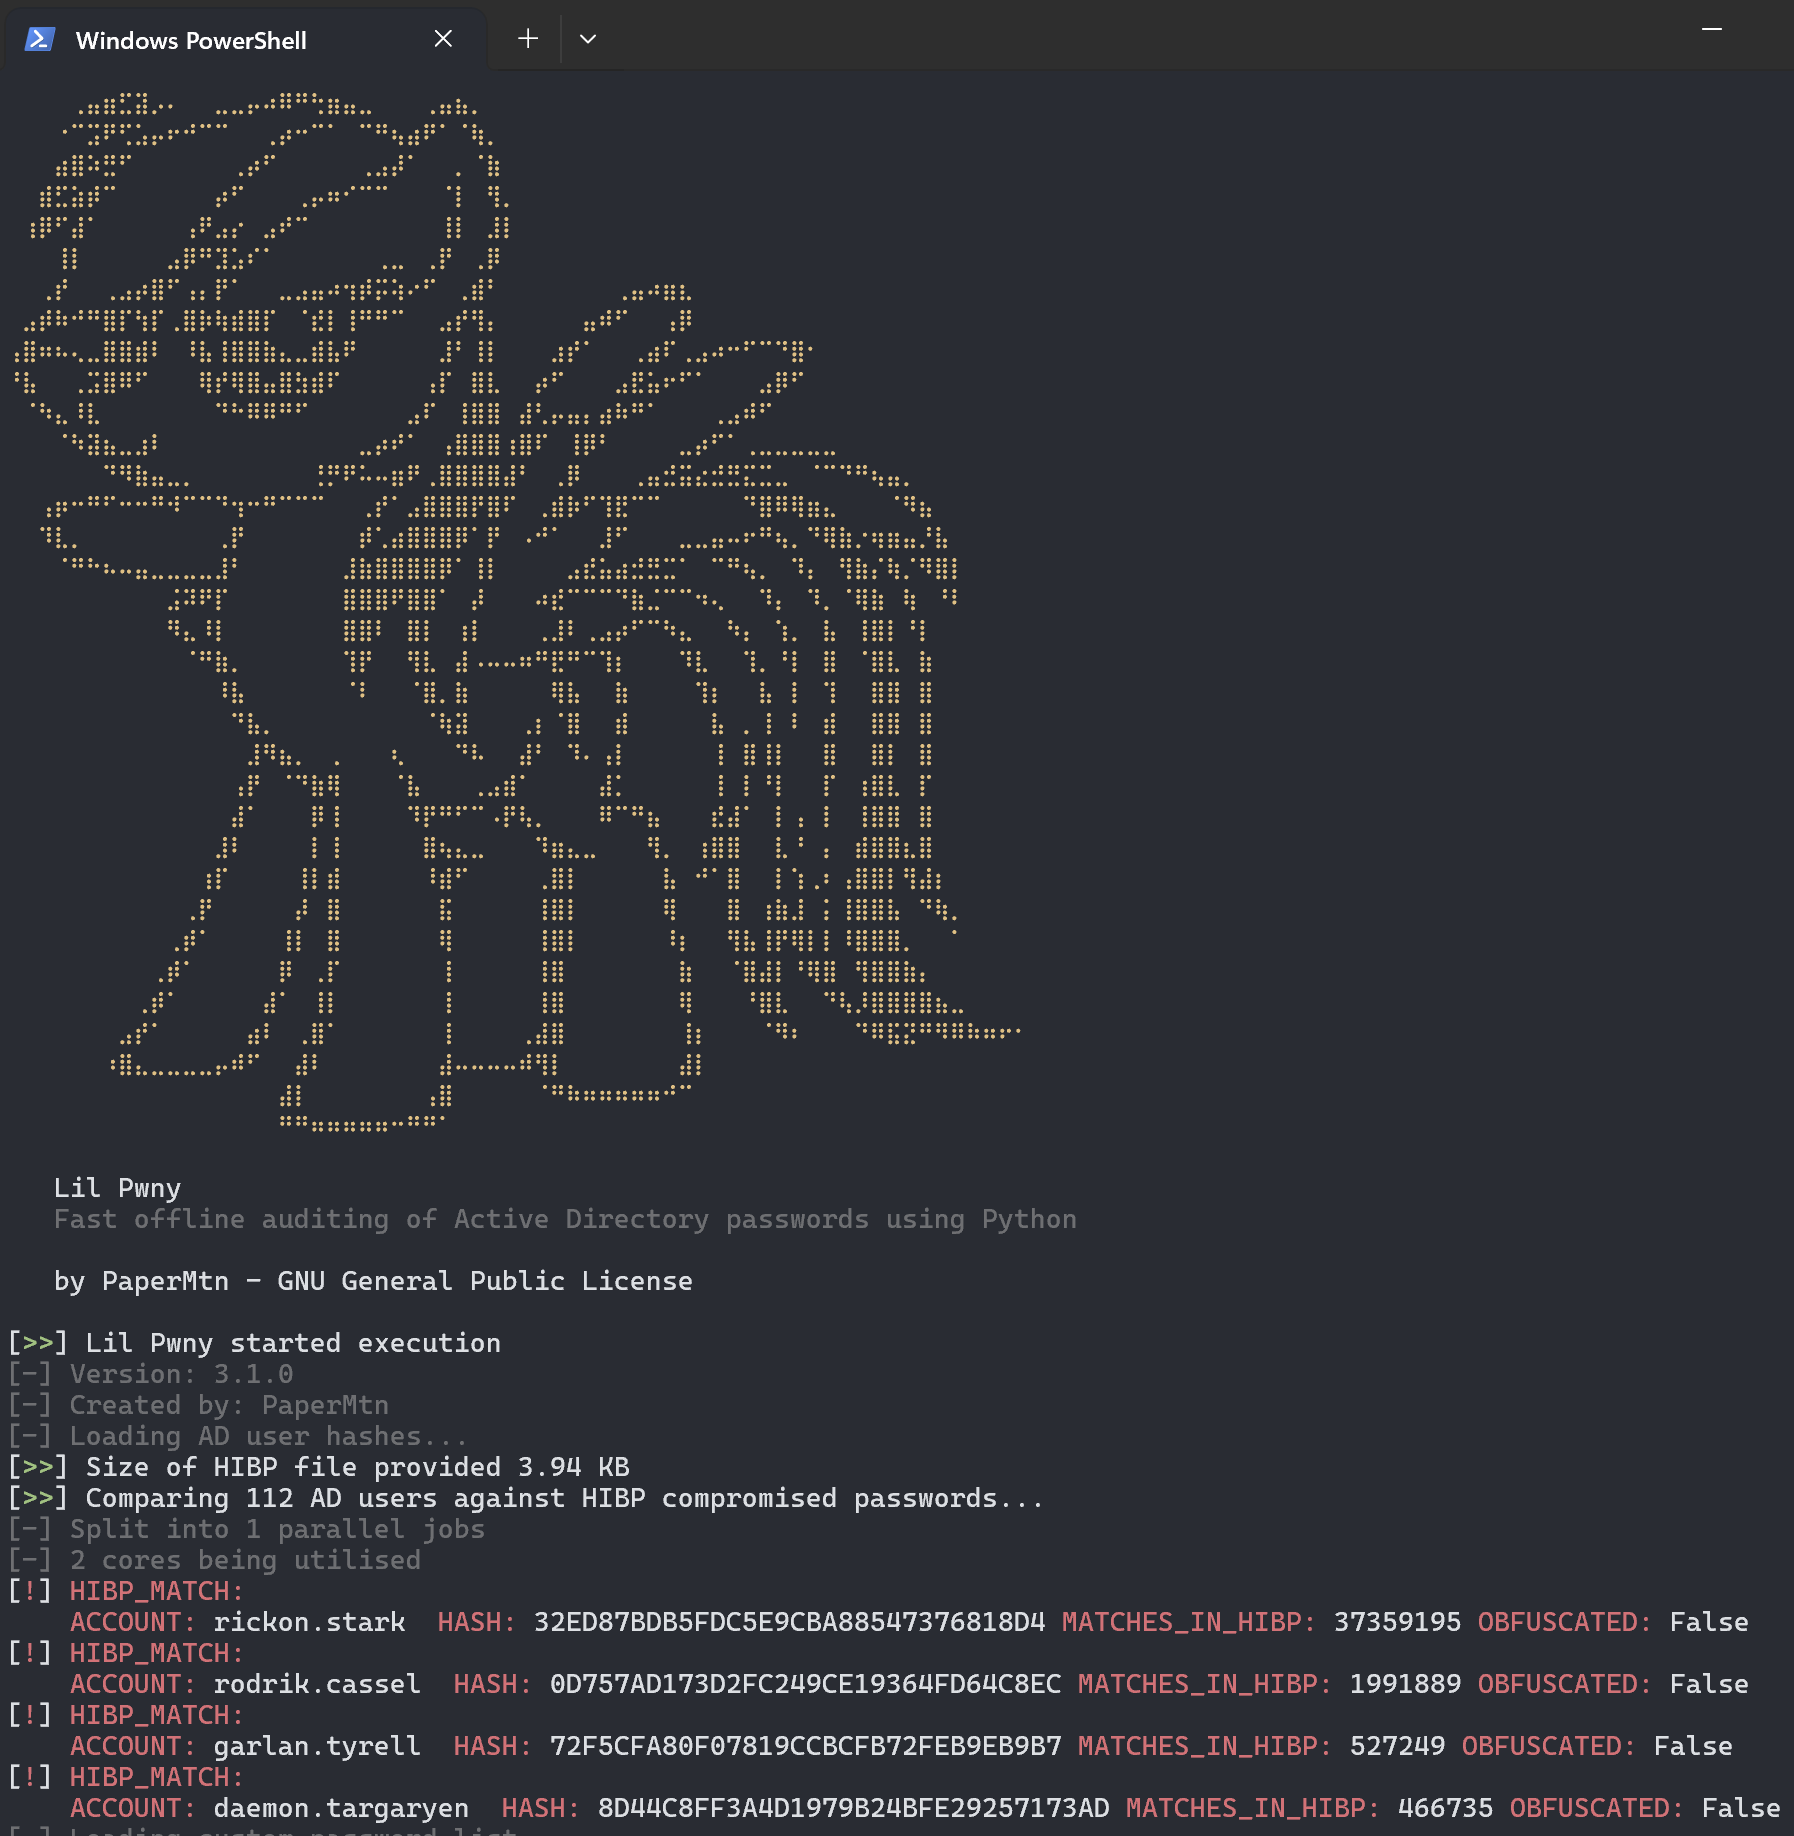
Fast offline auditing of Active Directory passwords using Python.

针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)


cve-2020-1472 复现利用及其exp

Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)

Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…

CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.

The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.

Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…

Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…