

fisy-fuzz
 0xricksanchez/fisy-fuzz
This is the full file system fuzzing framework that I presented at the Hack in the Box 2020 Lockdown Edition conference in April.
exploitationfuzzingvulnerability-analysis
0xricksanchez/fisy-fuzzThis is the full file system fuzzing framework that I presented at the Hack in the Box 2020 Lockdown Edition conference in April.
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 chopicalqui/kaliintelligencesuite
Automated intelligence-gathering framework that orchestrates Kali Linux tools and public APIs to collect, store, and analyze reconnaissance data for…
 tam-k592/cve-2024-53677-s2-067
A critical vulnerability, CVE-2024-53677, has been identified in the popular Apache Struts framework, potentially allowing attackers to execute…
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
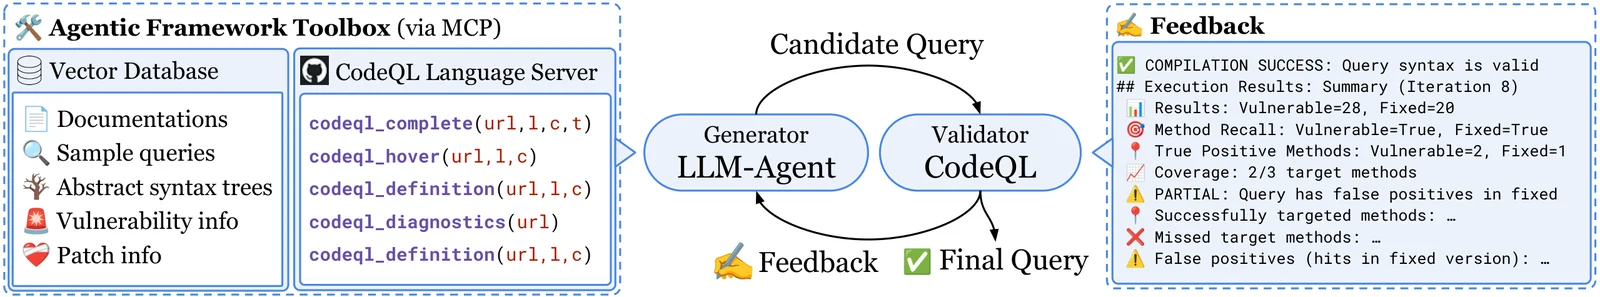 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
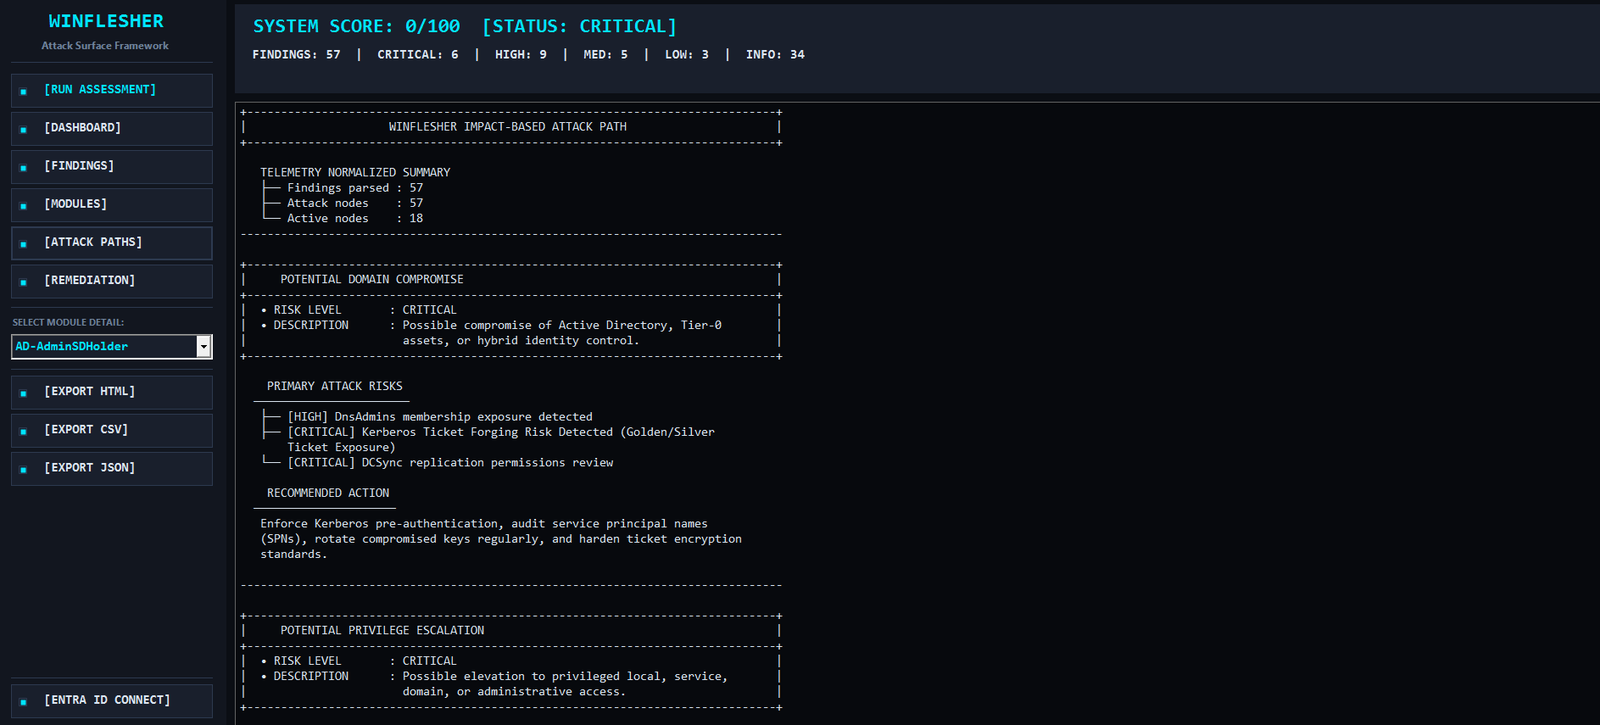 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 cispa/trevex
Automated Vulnerability Detection Framework for Transient Execution Vulnerabilities (IEEE S&P '26)
 alt3kx/cve-2022-22965_poc
Spring Framework RCE (Quick pentest notes)
 j0ey17/cve-2022-22963_reverse-shell-exploit
CVE-2022-22963 is a vulnerability in the Spring Cloud Function Framework for Java that allows remote code execution. This python script will verify…