

oss-fuzz-gen
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
ai-securitydevsecopsdynamic-code-analysis+3
google/oss-fuzz-genLLM powered fuzzing via OSS-Fuzz.
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
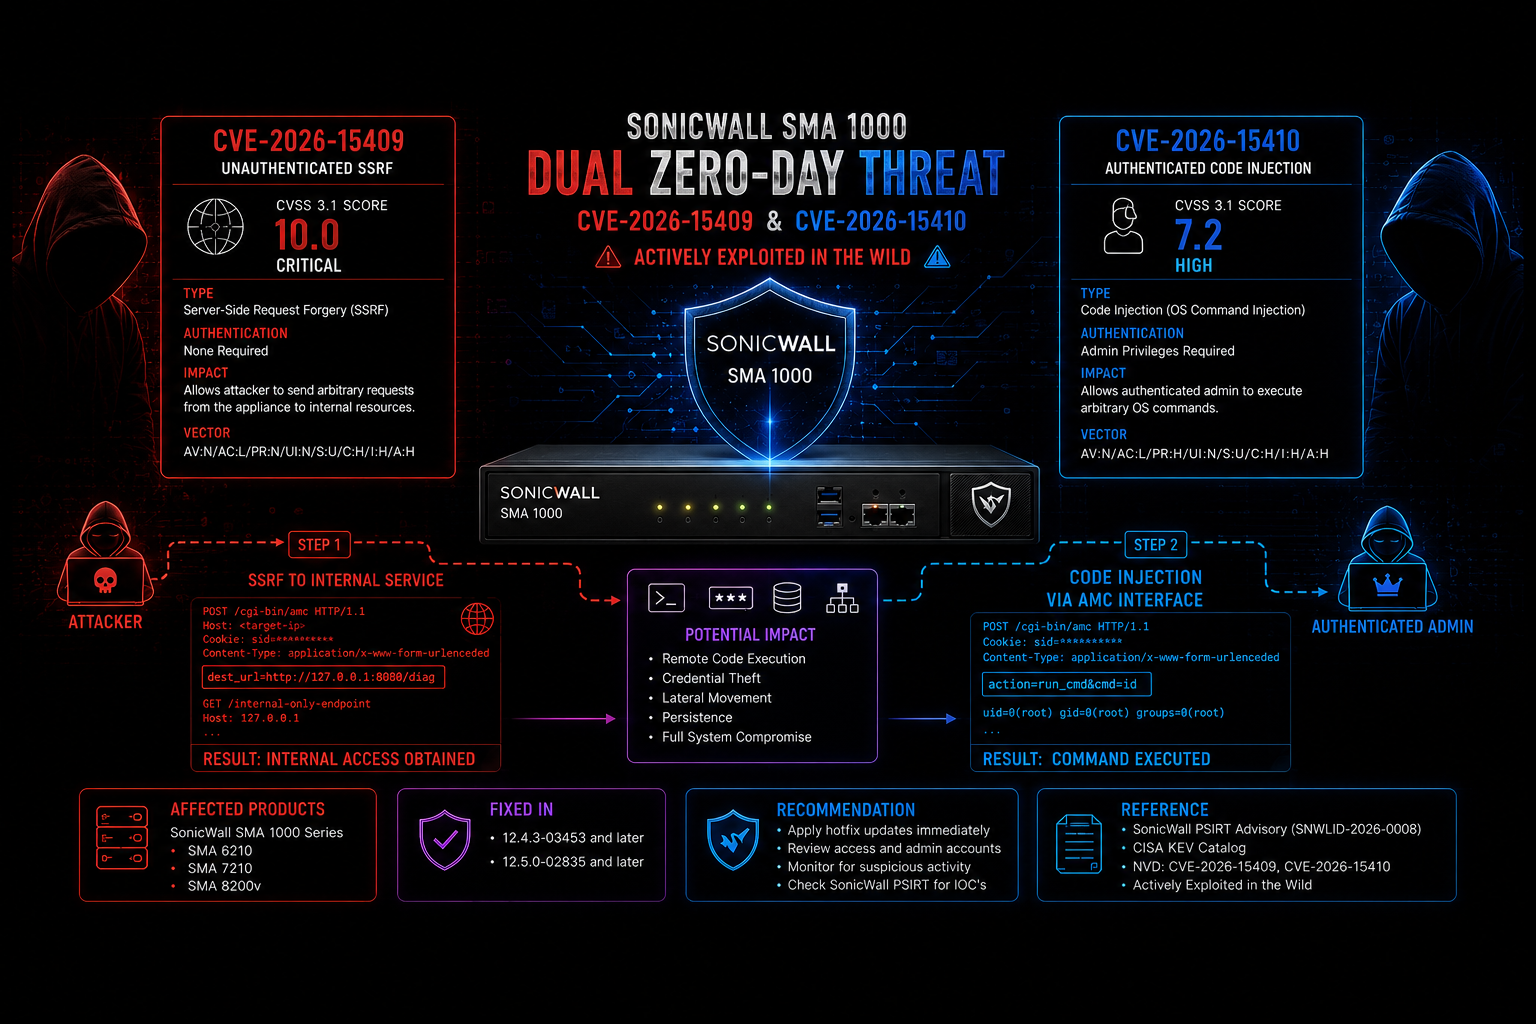 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
 aniqfakhrul/cve-2022-22954
Python exploit for CVE-2022-22954, a VMware Workspace ONE SSTI vulnerability, with batch scanning and Shodan integration for vulnerable host…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 nkeshawarz/cve-2023-46604-rce
Python-based remote code execution exploit for Apache ActiveMQ deserialization vulnerability (CVE-2023-46604) with multi-threaded scanning and XML…
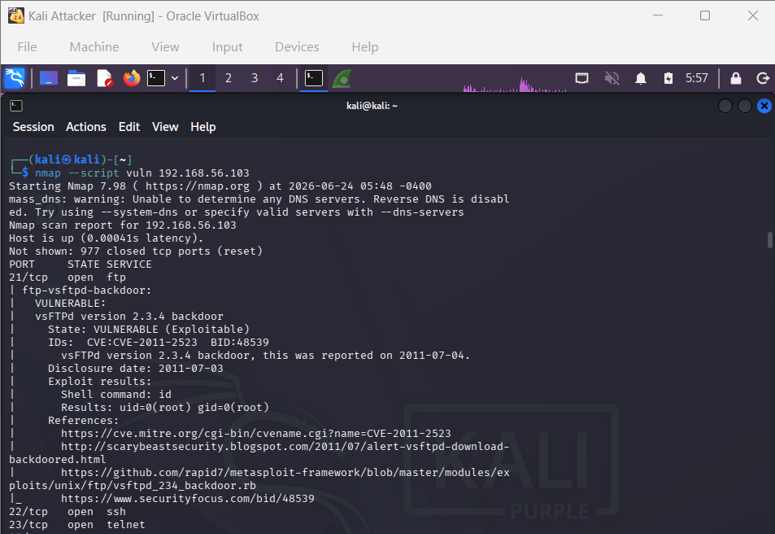 sonalisarkar-2003/ftp-vsftpd-cve-2011-2523-vapt-report
VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…
 mngunibanda1-prog/jozini-network-scanner
Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.
 murrez/cve-2026-6433
PoC for CVE-2026-6433: WordPress FlipperCode Custom CSS, JS & PHP (≤2.0.7) — unauthenticated SQLi to RCE. Python 3 stdlib; single target or bulk…
 phirojshah/cve-2024-4577
Proof-of-concept exploit for PHP CGI argument injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers with scanning…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 superswan/cve-2024-55963
CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…
 sahmsec/cve-2026-5615
Python proof-of-concept for CVE-2026-5615, a stored XSS in VvvebJs, demonstrating SVG upload exploitation with multi-threaded scanning and validation.
 luisdalmolin/recon-test-livewire
Test target: fresh Laravel 12 app with Livewire pinned to vulnerable 3.6.3 (CVE-2025-54068) for recon scanning