
SilentSniffer
 ahmadhassan-bted/silentsniffer
A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
educationinformation-gatheringosint+7
5.6k
ahmadhassan-bted/silentsnifferA professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
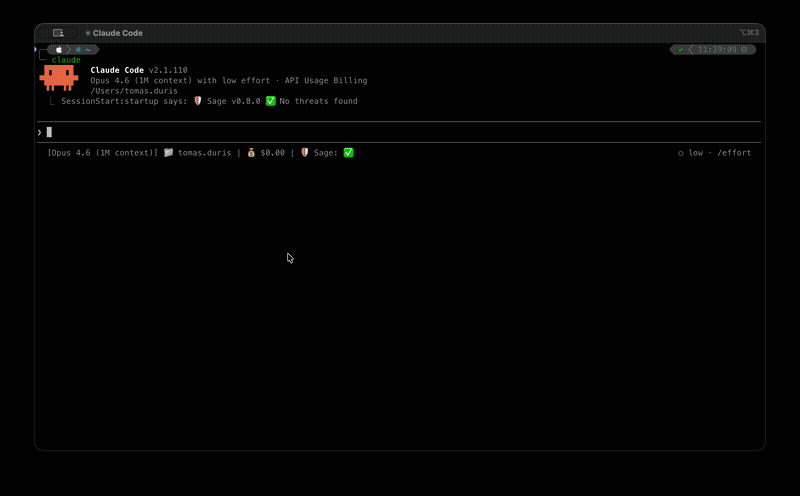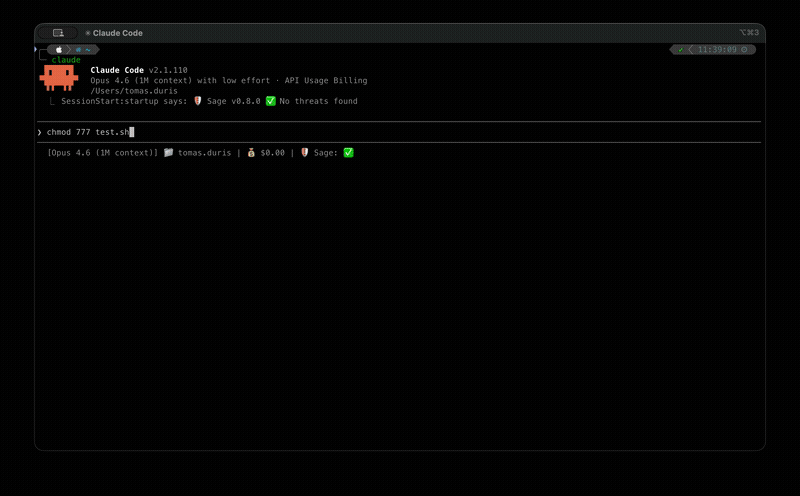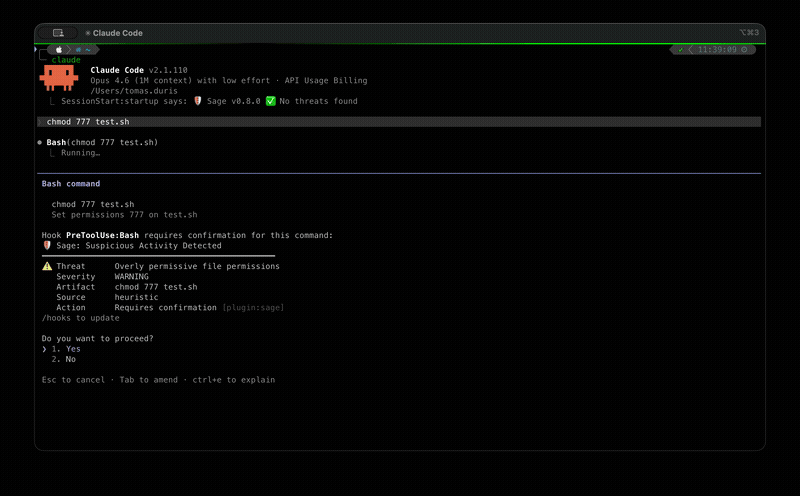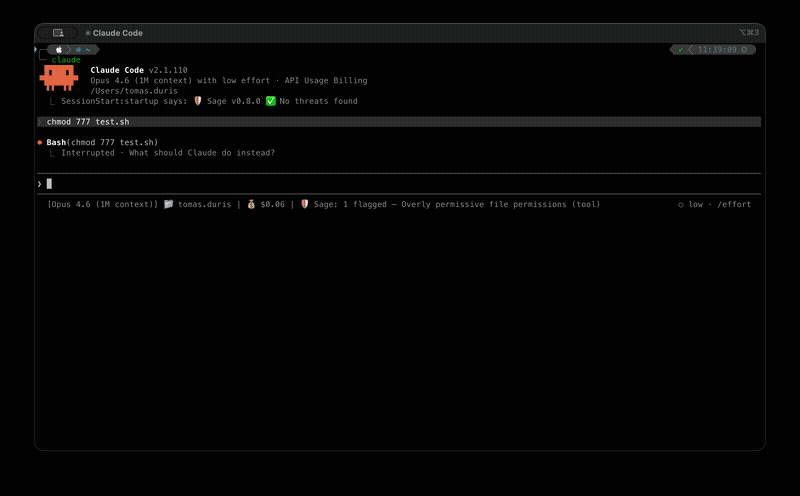 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
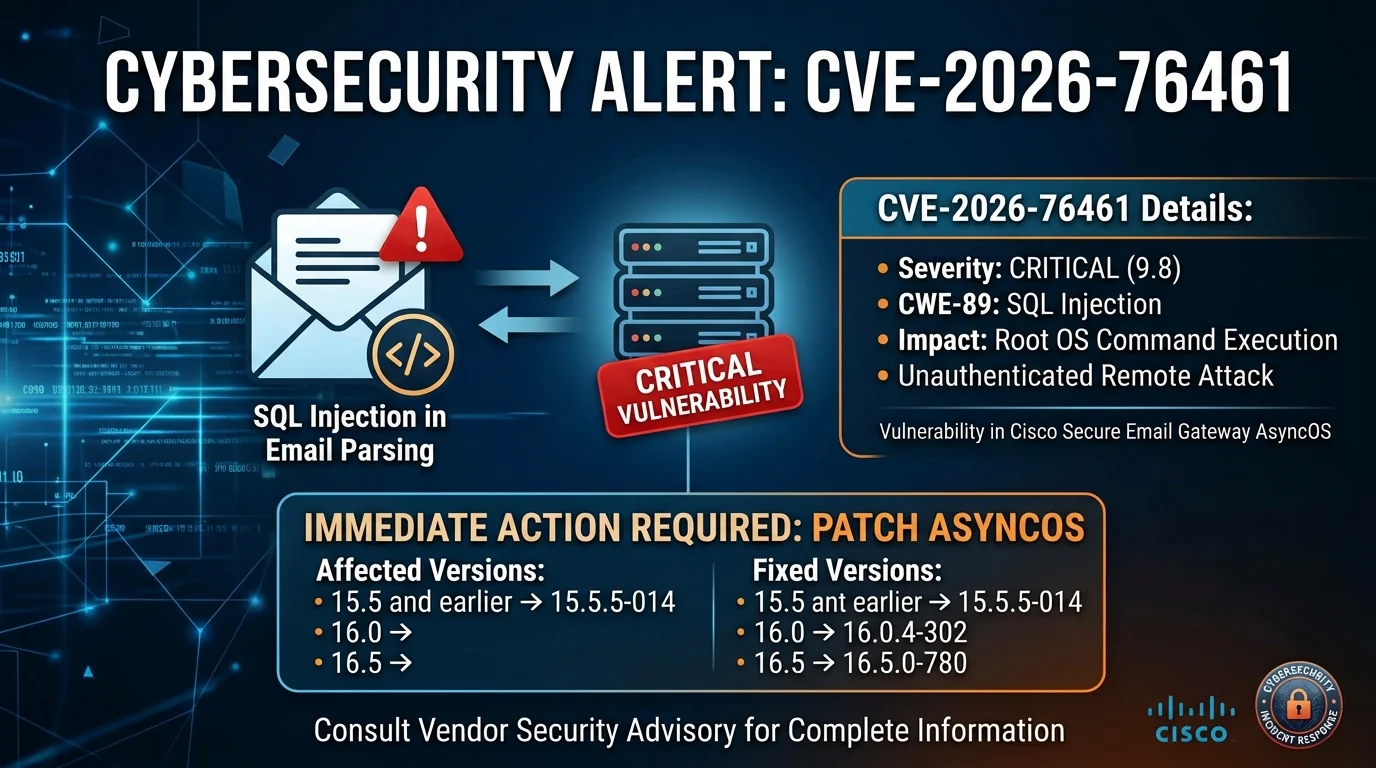 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
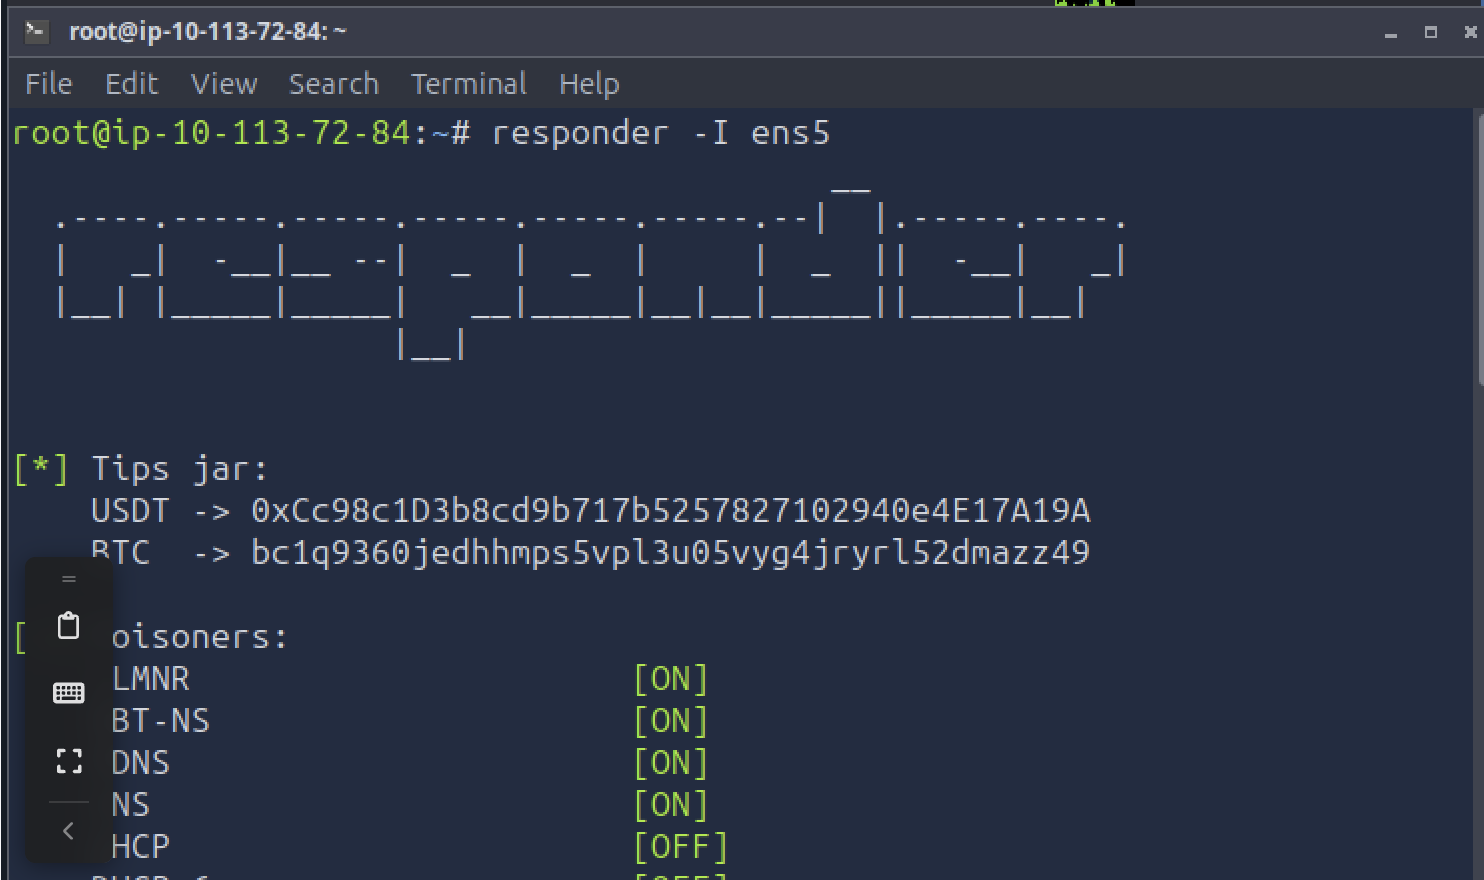 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 george0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form
Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).
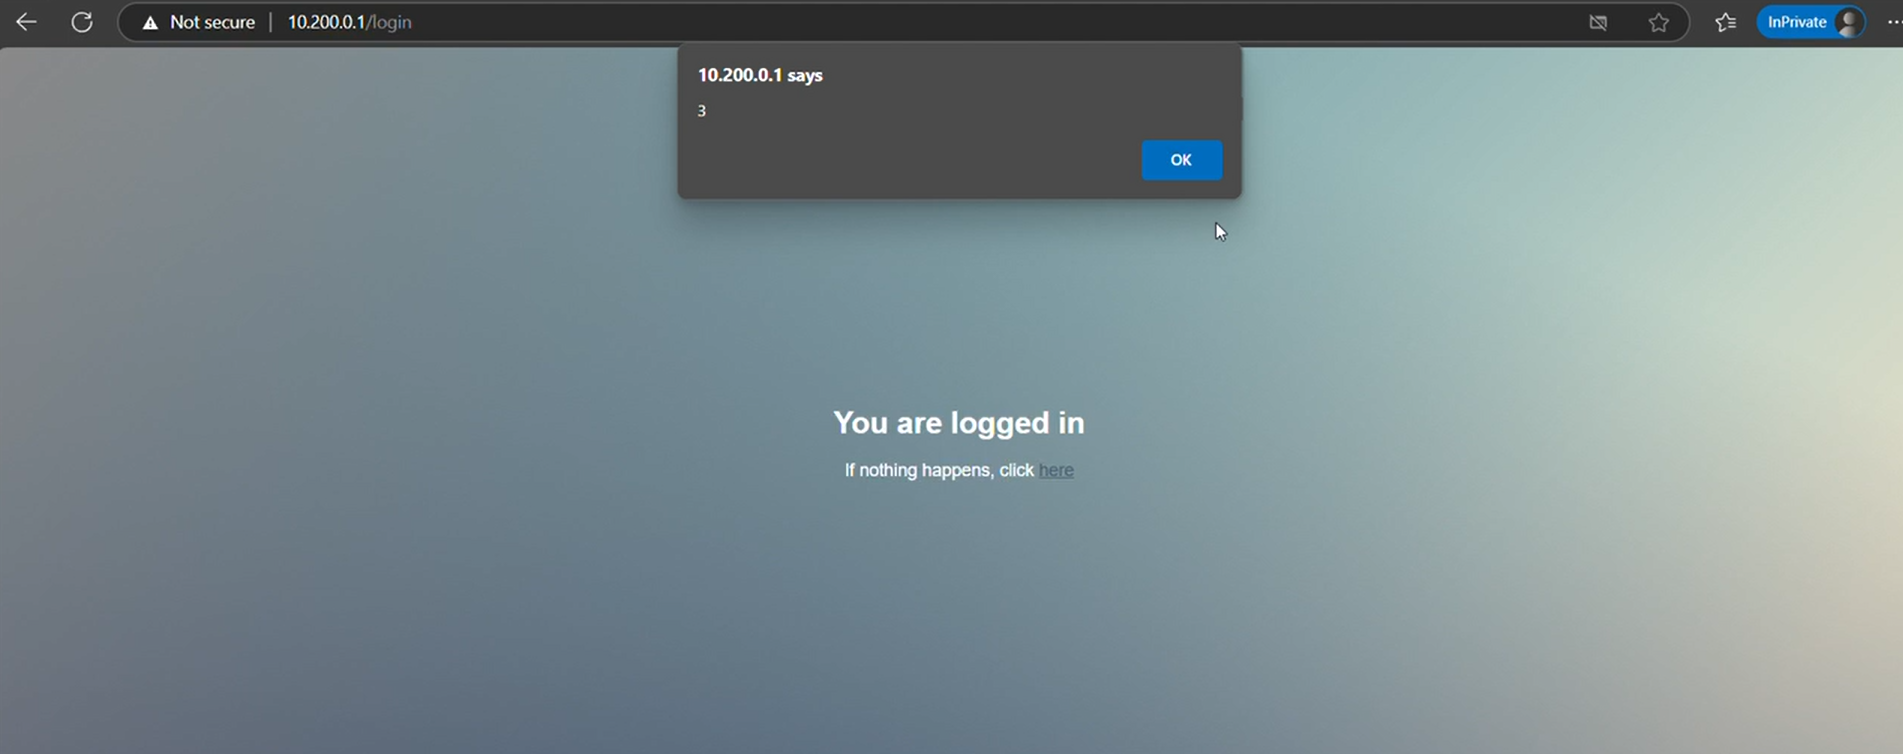 praksokchea/cve-2025-6563
Reflected XSS vulnerability in MikroTik Hotspot login page
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction
 yoguicr/cve-2024-21413-outlook-assessment
Detailed vulnerability assessment and exploitation report for CVE-2024-21413 (Moniker Link) in Microsoft Outlook, including attack path, NetNTLMv2…