Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
sudoinjection — Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell) | Kitploit
Tools/GitHubGitHub/mikivirus0/sudoinjection
Privilege EscalationVulnerability AnalysisExploitationCTFPenetration TestingLearning & EducationBinary ExploitationLabs & Practice
GitHubmikivirus0/sudoinjection

sudoinjection

Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)

View Repository
2351 year agoNot yet reviewed
Share

CVE-2025-32463: Local Privilege Escalation via sudo -R NSS Injection

Summary

This PoC demonstrates local privilege escalation on Linux systems via abuse of the sudo -R option in conjunction with a custom NSS module. It targets the vulnerability CVE-2025-32463, which stems from unsafe handling of the nsswitch.conf and NSS shared libraries under a chroot environment.

This PoC, sudo2root, adapts the original technique by compiling a custom NSS module that leverages the constructor attribute to escalate privileges and drop a setuid root shell in /usr/local/bin/.suidshell.


Vulnerability Details

  • Vulnerability: Improper input validation and unsafe use of the -R chroot flag by sudo.
  • Impact: A local attacker with sudo access can execute arbitrary code as root, breaking container and user isolation.
  • Root Cause:
    • sudo -R changes the root directory but does not drop privileges or sanitize the environment.
    • NSS modules are loaded even from attacker-controlled paths inside this new root.
  • Exploit Strategy:
    1. Create a fake root filesystem with malicious nsswitch.conf and custom libnss_* shared object.
    2. Trick sudo into loading the attacker-controlled NSS library.
    3. The shared object executes code on load (via __attribute__((constructor))), drops a setuid root shell, and escalates privileges.

PoC Overview

Key Components:

  1. sudo2root.c – Malicious NSS module:

    • Uses a constructor function that:
      • Gains root via setreuid(0,0) and setregid(0,0)
      • Writes a small C program for a root shell
      • Compiles it with gcc
      • Sets correct SUID permissions
  2. Bash Exploit Script:

    • Prepares the fake chroot with:
      • etc/nsswitch.conf
      • Custom libnss_/sudo2root1337.so.2 NSS module
    • Launches the exploit via:
      sudo -R sudo2root sudo2root
      
  3. Setuid Shell:

    • Written to: /usr/local/bin/.suidshell
    • Retains root on execution:
      /usr/local/bin/.suidshell id
      

Usage

chmod +x sudoinject.sh
./sudoinject.sh

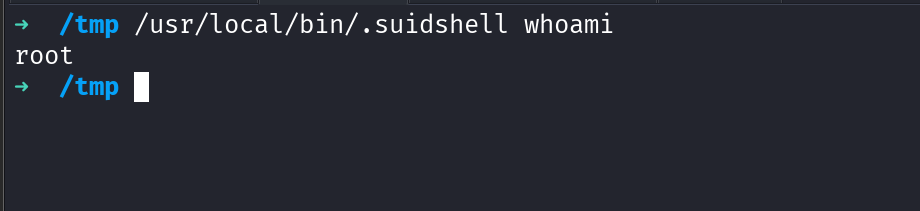
After the exploit completes, run:

/usr/local/bin/.suidshell
whoami  # => root

File Structure

sudoinject.sh                 # Main exploit script
libnss_/sudo2root1337.so.2   # Malicious NSS module (compiled)
sudo2root/etc/nsswitch.conf  # Custom nsswitch pointing to fake module
/usr/local/bin/.suidshell    # Final setuid root shell

Technical Overview:

Exploiting sudo -R:

  • sudo’s -R <dir> flag changes the root directory before executing a command.
  • If this directory has a custom nsswitch.conf with passwd: /libnss_<name>.so, sudo loads it before dropping privileges.
  • This behavior allows arbitrary code execution as root.

NSS Module Execution:

  • Shared object is compiled with:

    gcc -shared -fPIC -Wl,-init,exploit_constructor -o libnss_/sudo2root1337.so.2 sudo2root.c
    
  • Constructor runs before any main() logic.

  • Creates and compiles a suid shell with:

    setreuid(0,0); setregid(0,0); execl("/bin/bash", "bash", NULL);
    
  • Sets permissions via:

    chown 0:0 .suidshell && chmod 4755 .suidshell
    

Screenshot (PoC)

PoC Screenshot PoC Screenshot


Acknowledgments

  • Original PoC Inspiration: pr0v3rbs/CVE-2025-32463_chwoot
  • Exploit adapted and improved by: MikiVirus

📢 Disclaimer

This code is provided for educational purposes only. Unauthorized use of this code on systems you do not own or have explicit permission to test is illegal and unethical. Always get proper authorization before conducting security testing.



Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →