

CVEngine
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
ai-securityemail-securityinformation-gathering+8
372
hevnsnt/cvengineAI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 abraxas/forgejo-openid-discovery-ssrf
Forgejo 16.0.5 - High - Remote - SSRF - OpenID discovery fetches attacker-controlled URLs
 constantinefedorov/review.cve-2023-5612
Proof-of-concept and analysis for CVE-2023-5612, a GitLab CE/EE webhook SSRF. Includes curl PoC steps and custom NSE scripts to verify and…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
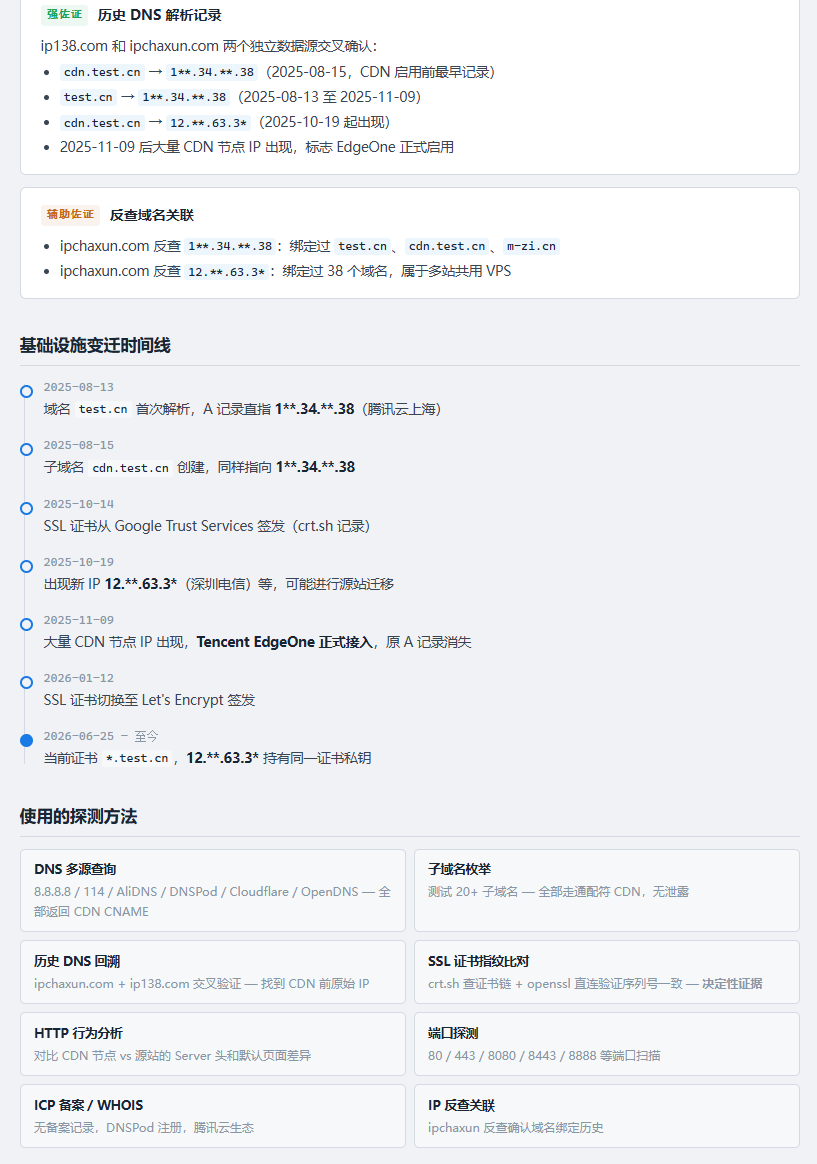 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 dkstar11q/cve-2024-29269
Exploit for CVE-2024-29269 enabling unauthenticated OS command execution on TLR-2005KSH routers, with ZoomEye and Leakix dork queries for target…
 murrez/cve-2026-19658
Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 aerchy/cve-2024-7593
Exploit for CVE-2024-7593, a critical RCE in Pulse Secure VPN management interface, allowing authenticated attackers to execute arbitrary commands.…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
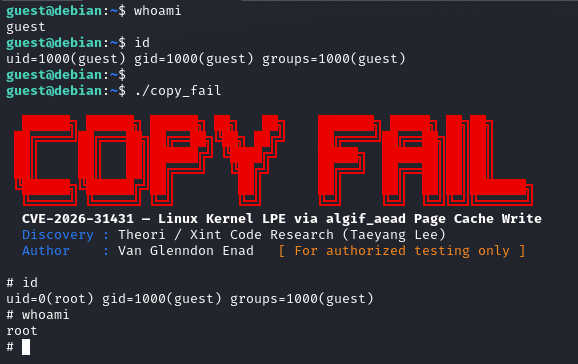 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 lorenzobruno7/cve-2026-26744
Demonstrates user enumeration in FormaLMS via response discrepancy on the /lostpwd endpoint, enabling unauthenticated username discovery for targeted…
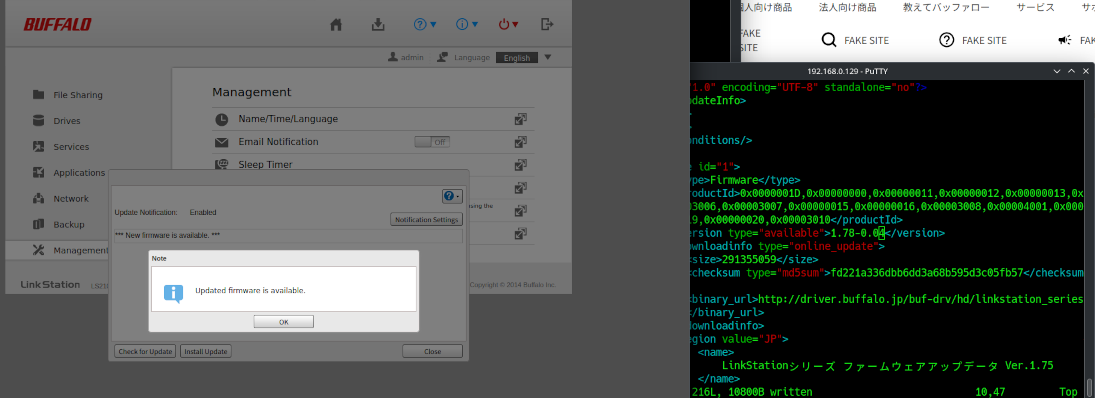 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 null200ok/-nginxui_discover
Nginx UI Discovery Scanner - CVE-2026-27944 Version Detector