
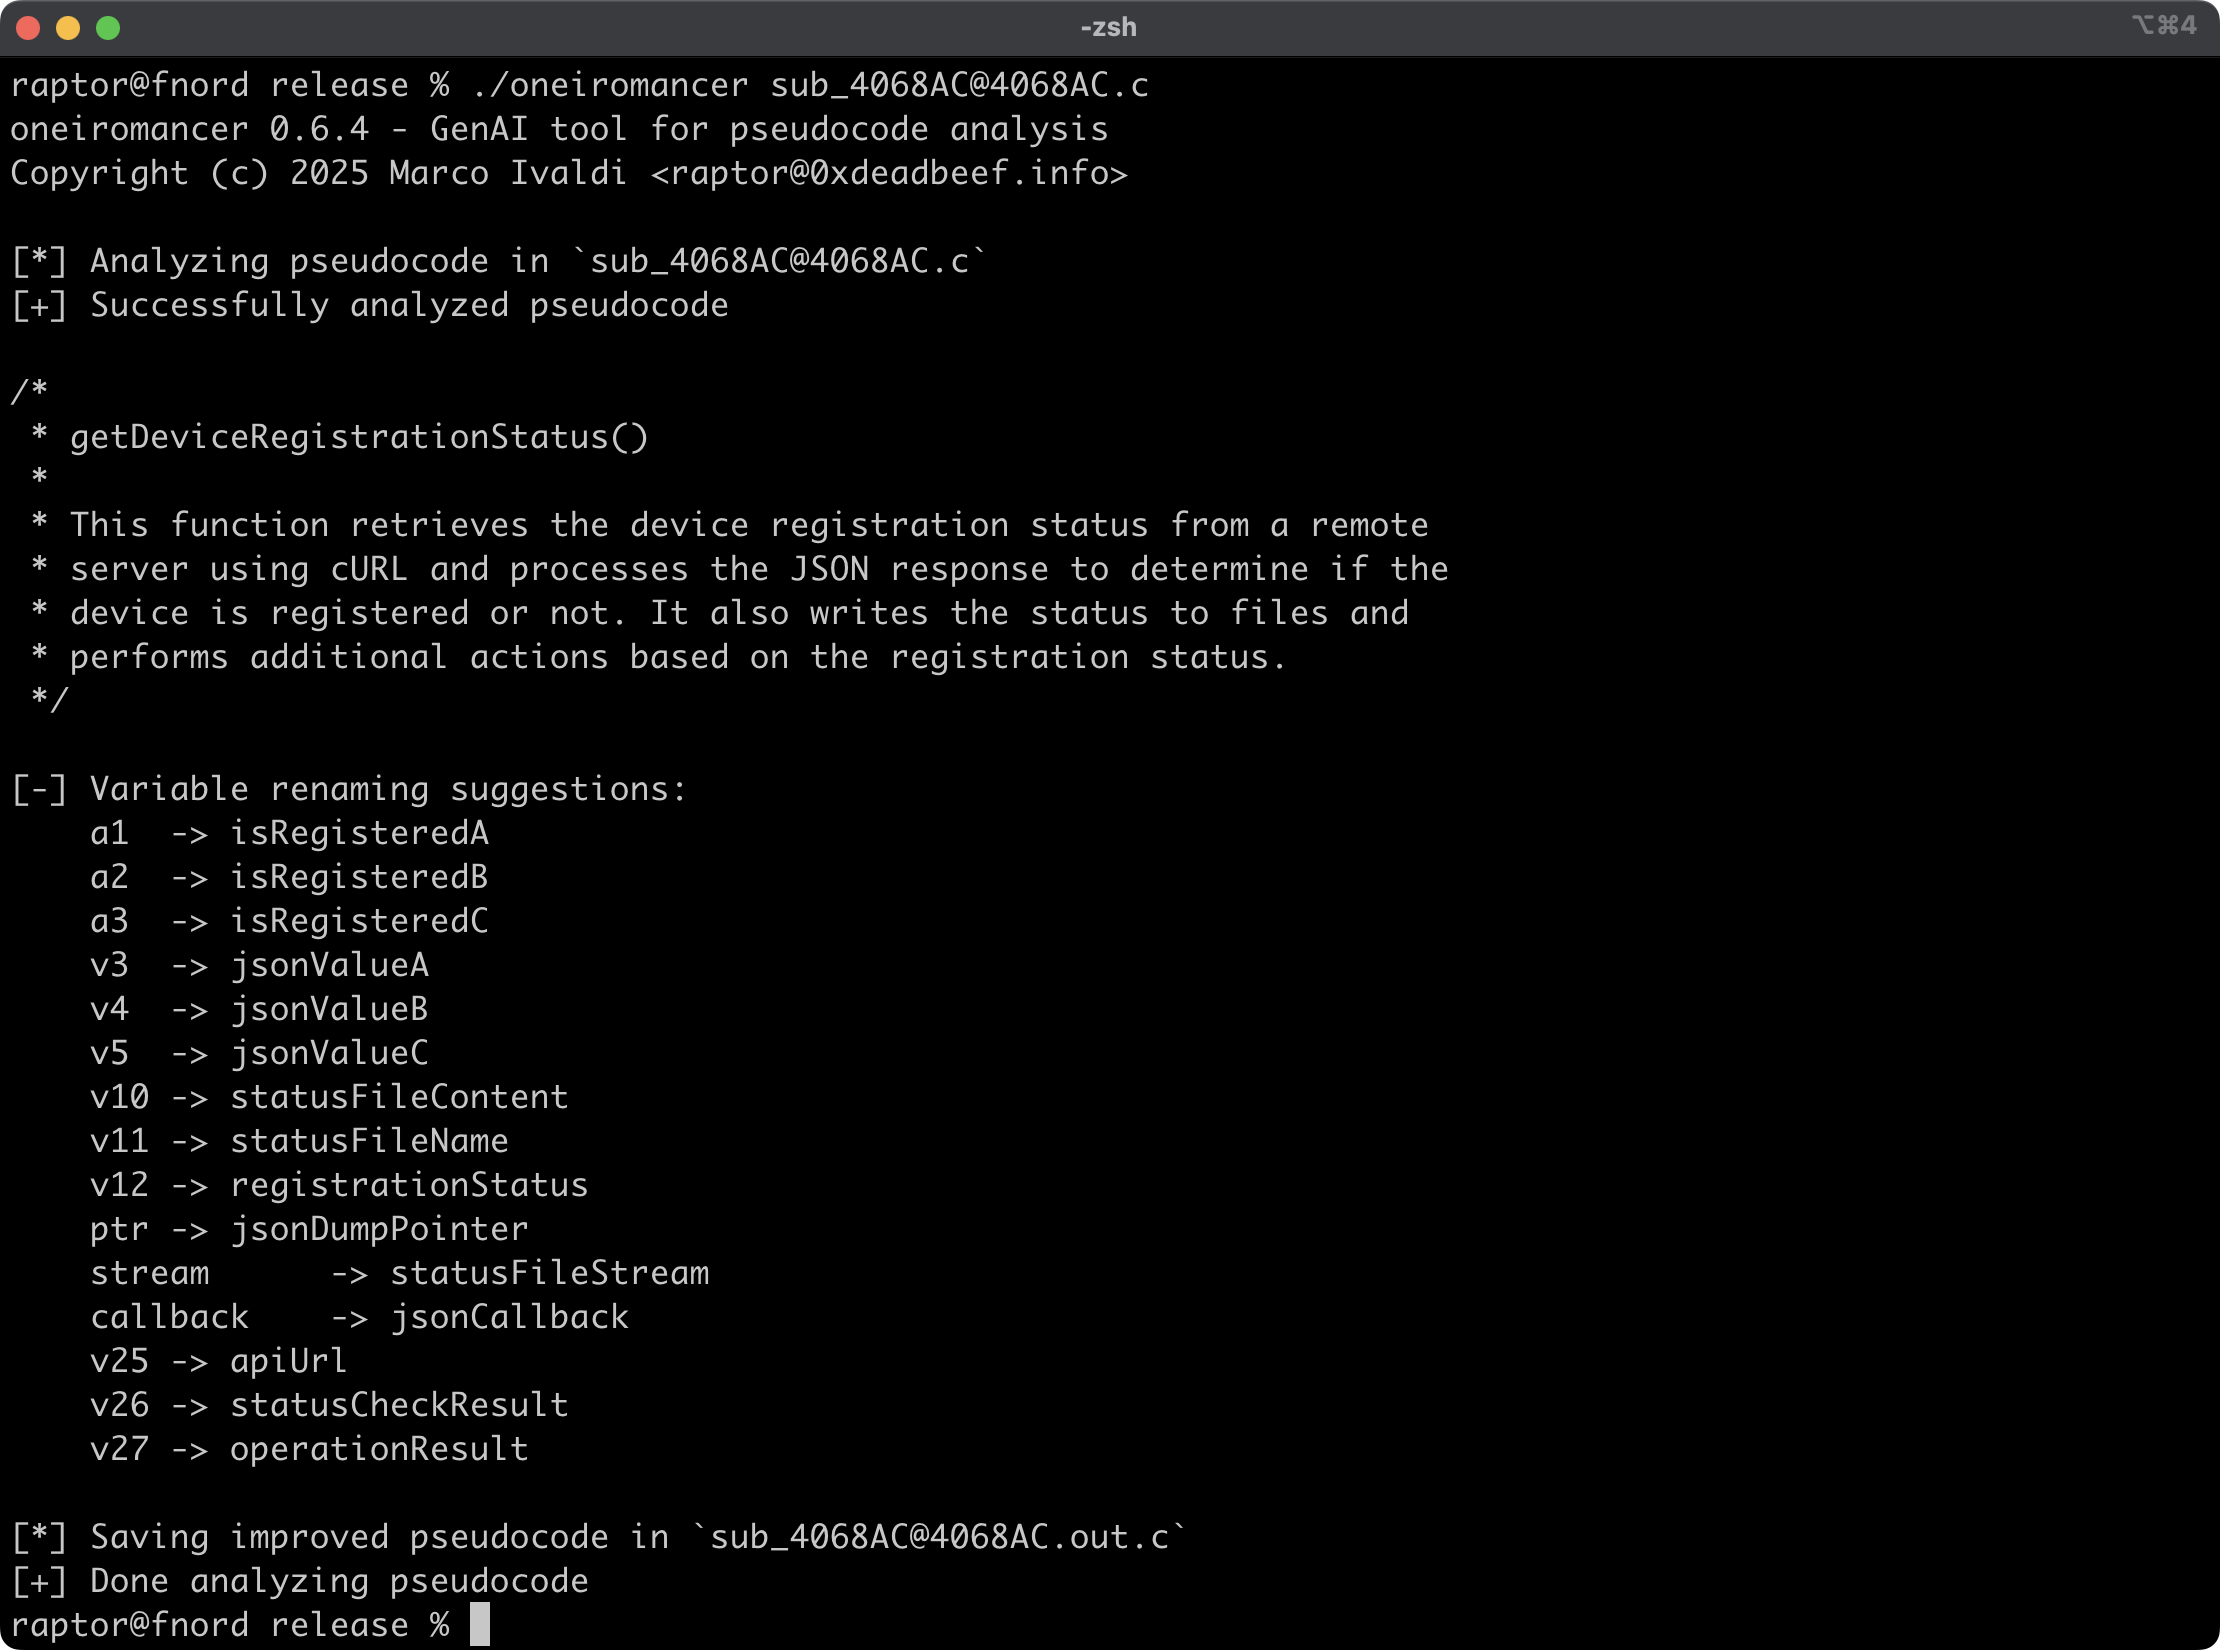
oneiromancer
 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
ai-assisted-reversingcode-analysisreverse-engineering+3
0xdea/oneiromancerReverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
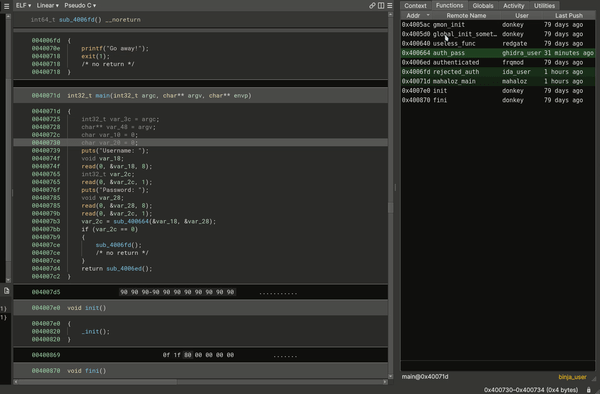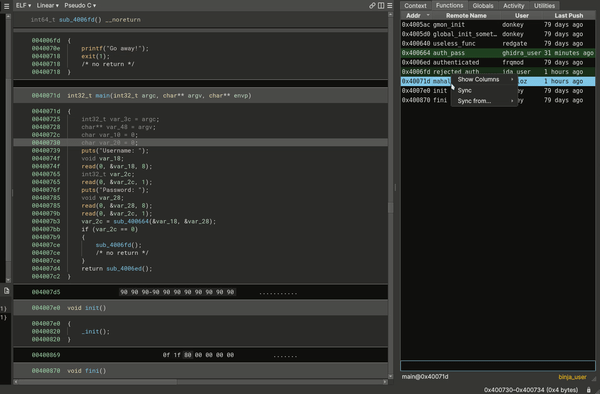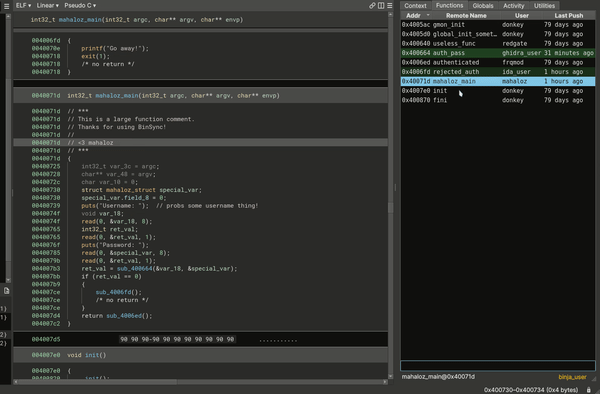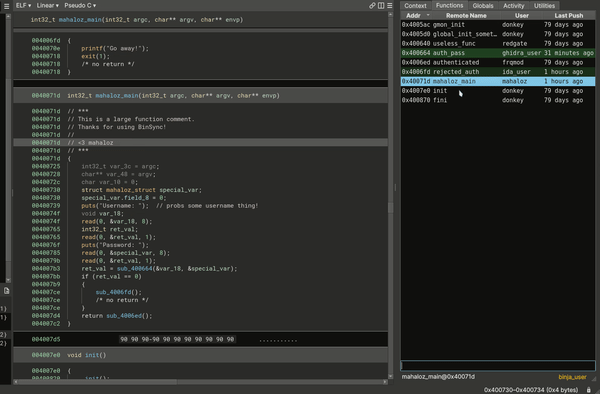 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
 platomav/mcextractor
Intel, AMD, VIA & Freescale Microcode Extraction Tool
 mildsunrise/protobuf-inspector
🕵️ Tool to reverse-engineer Protocol Buffers with unknown definition
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
 quarkslab/quokka
Quokka: A Fast and Accurate Binary Exporter
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
 synacktiv/lumina_server
Local server for IDA Lumina feature
 ricardojoserf/p-invoke.net
Curated collection of P/Invoke definitions from pinvoke.net with Microsoft documentation links, enabling quick Windows API prototyping for security…
 nccgroup/readable-thrift
Human-friendly Thrift encoder/decoder
 p0dalirius/pdbdownload
An utility to download PDB files associated with a Portable Executable (PE).
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
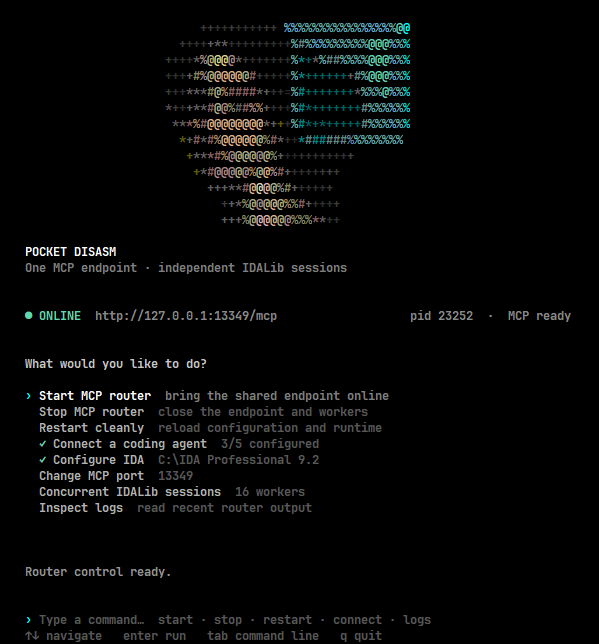 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
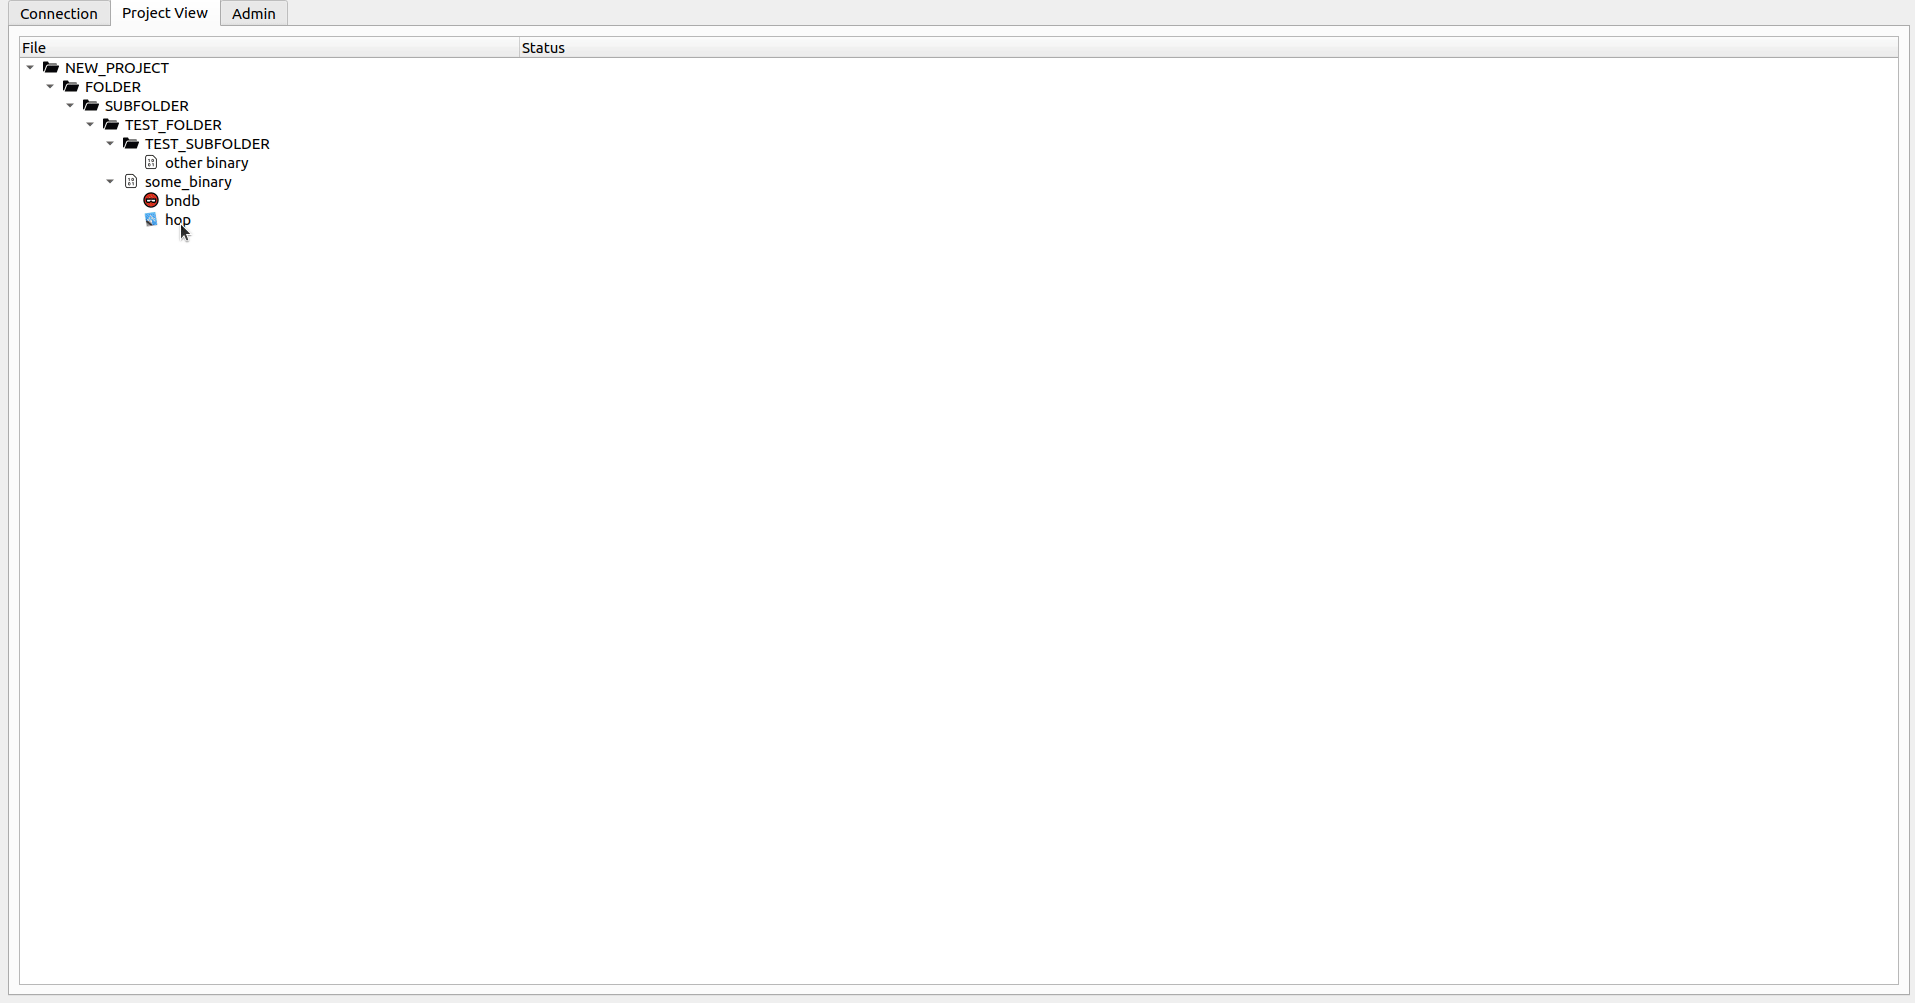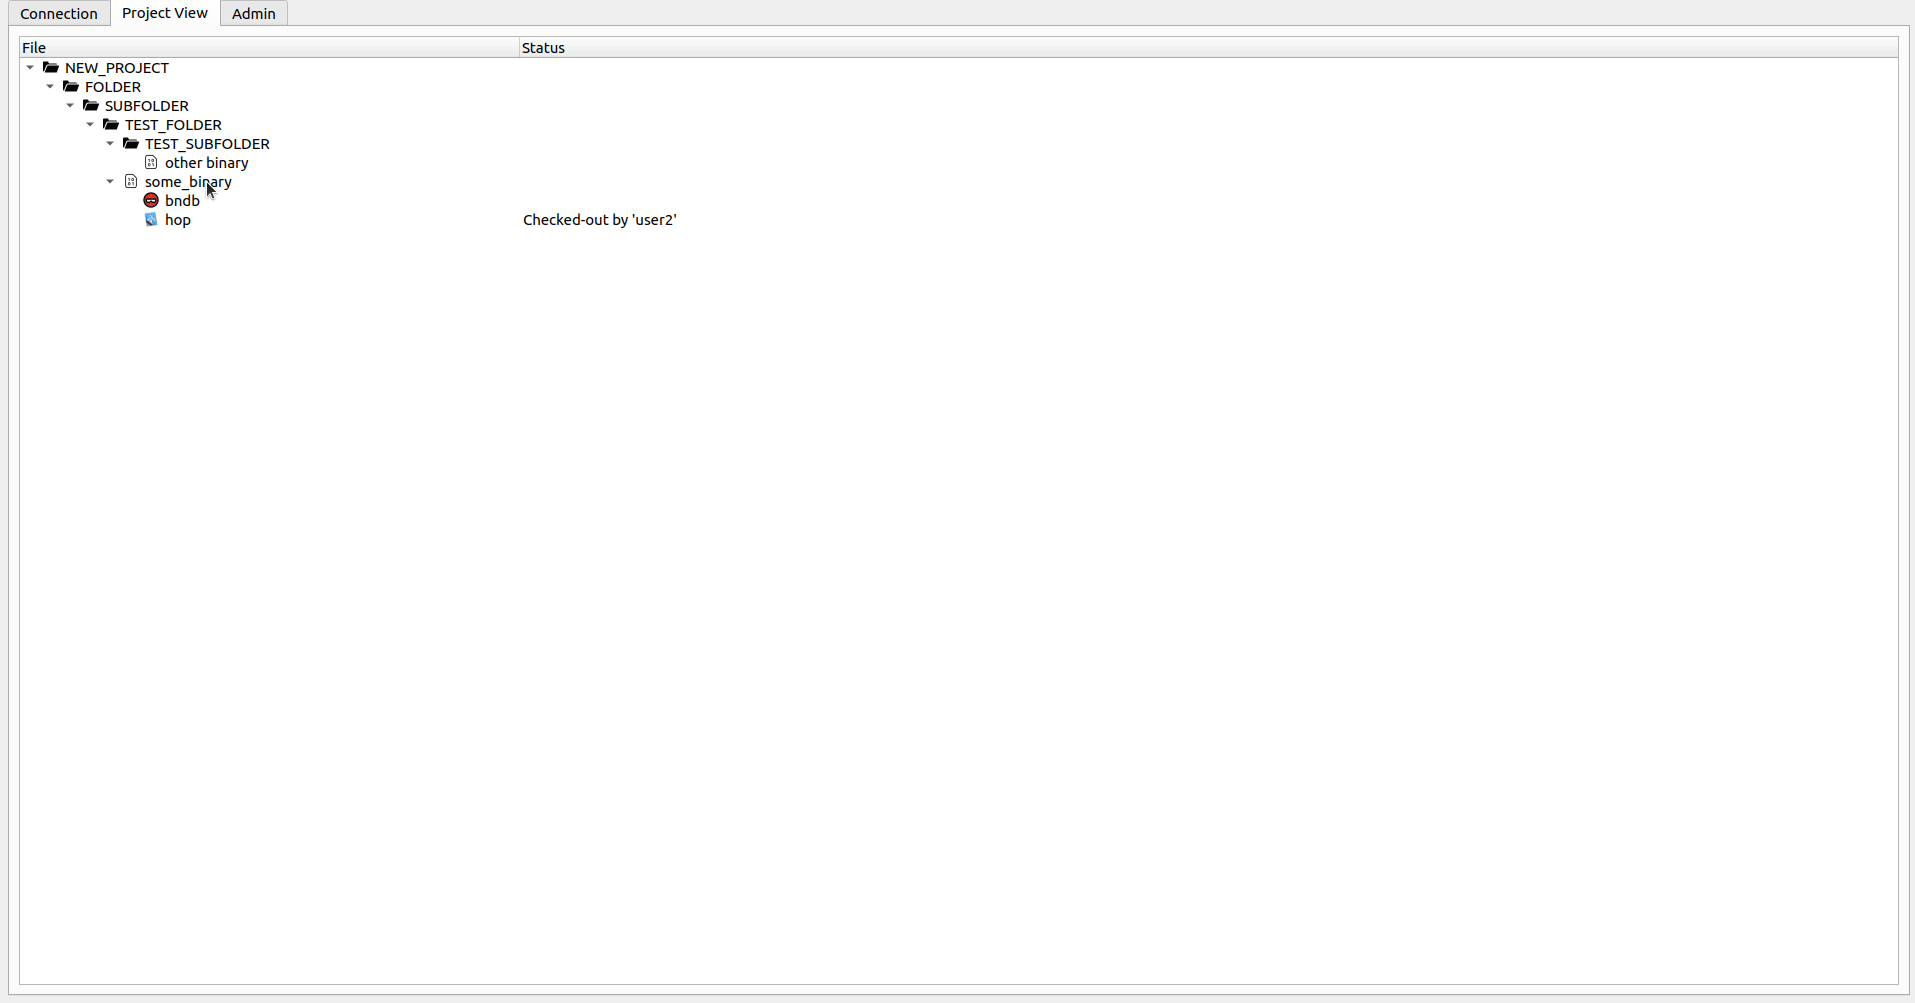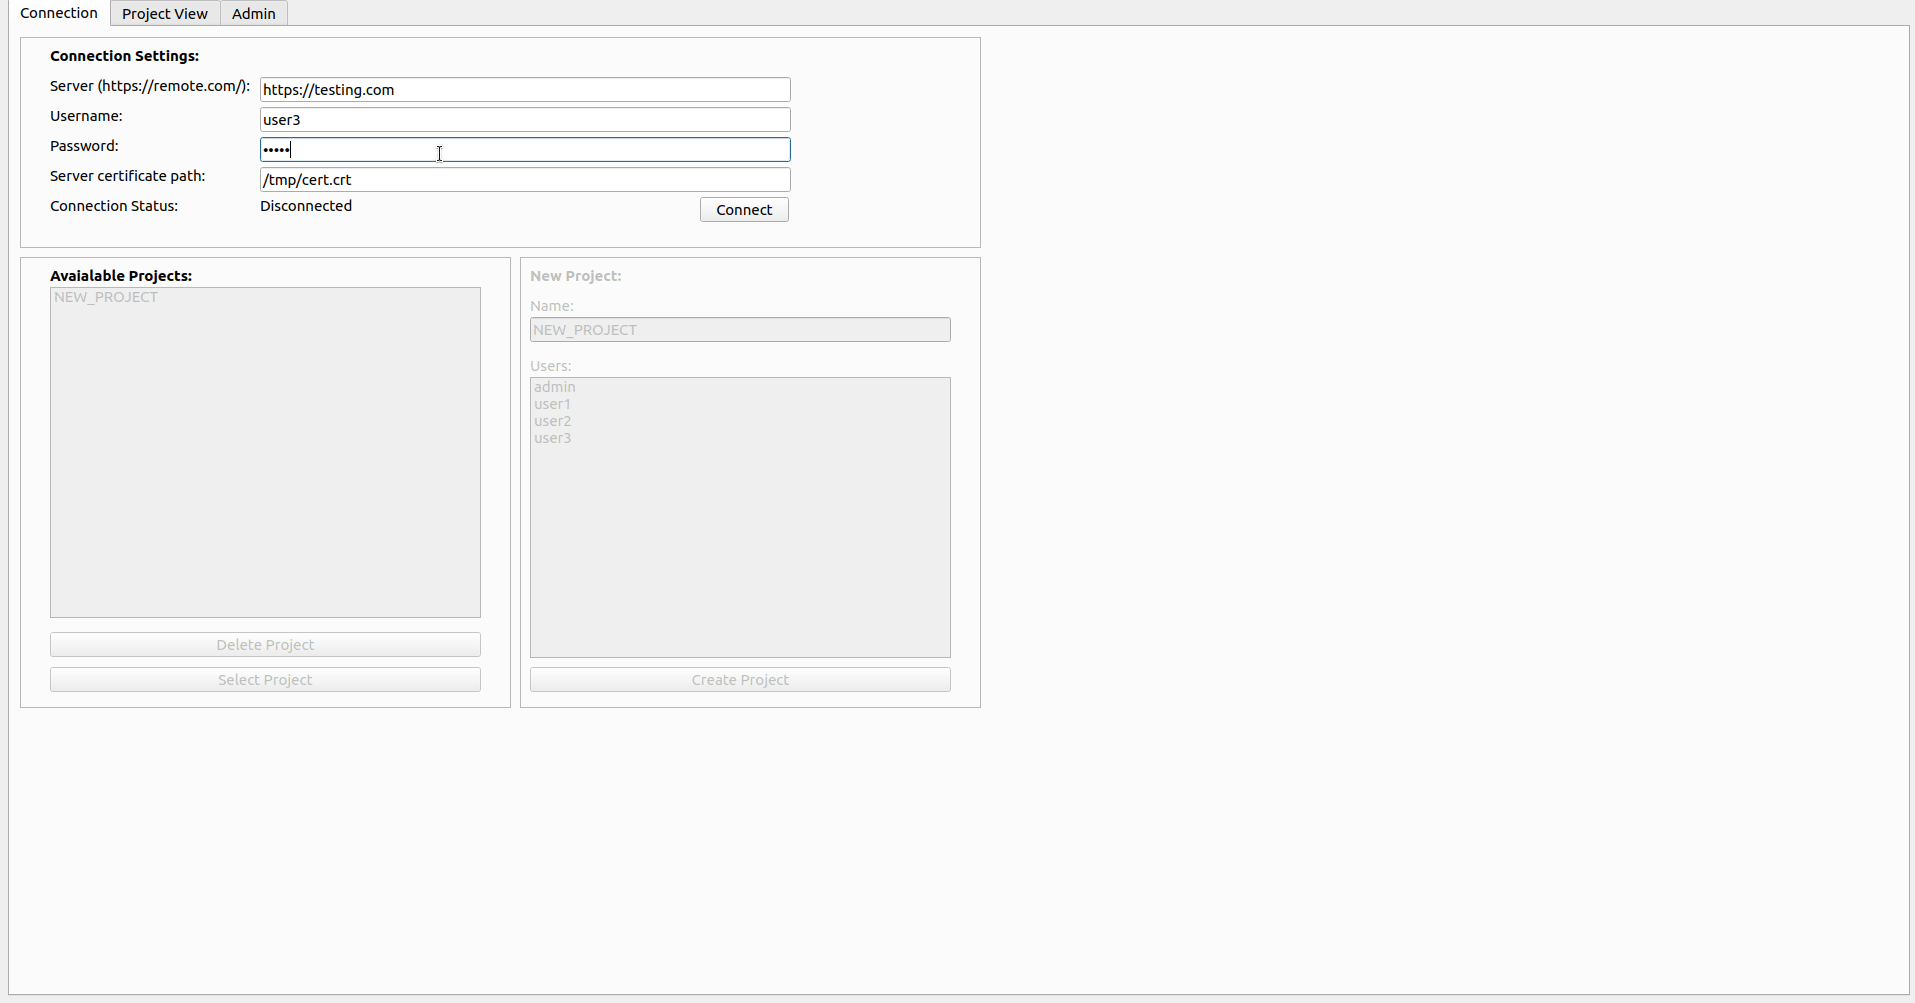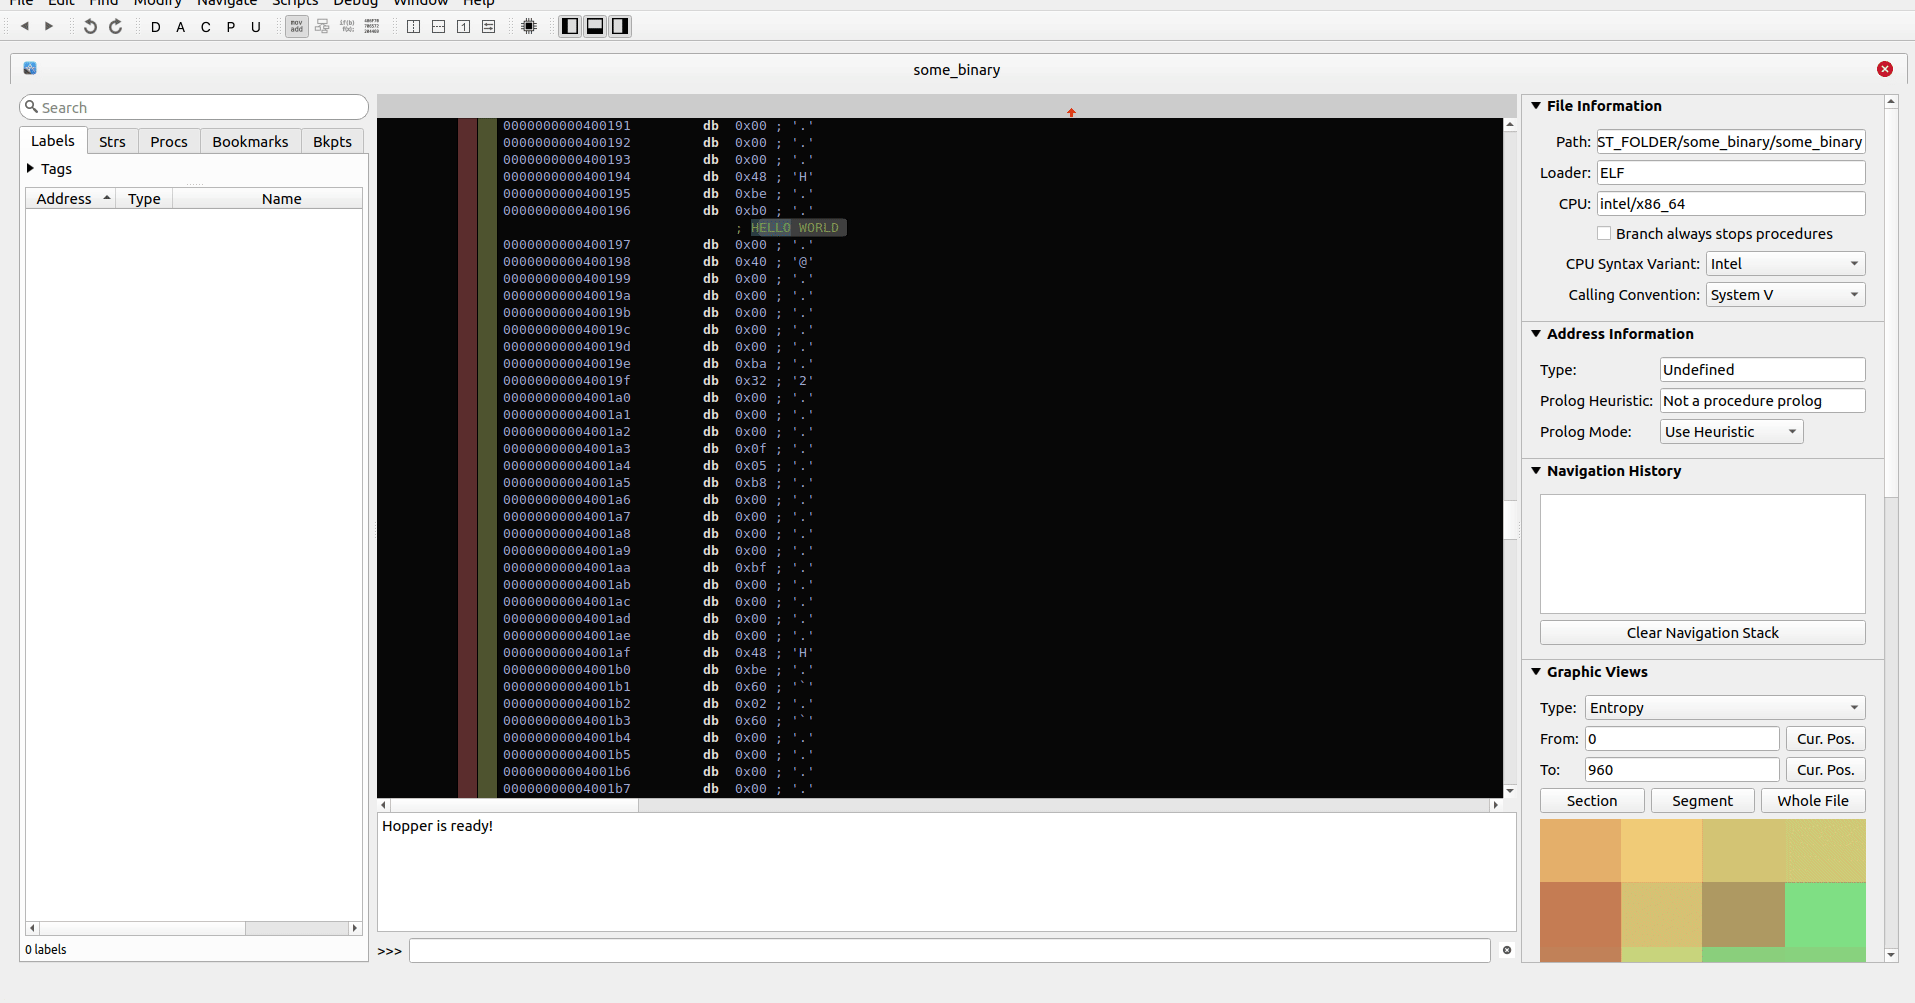 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…