

toolbox
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
api-security-testingcrawlerdynamic-analysis-sandboxing+8
4313h 20m ago
go-appsec/toolboxCollaborative application security testing between humans and agents via CLI and MCP
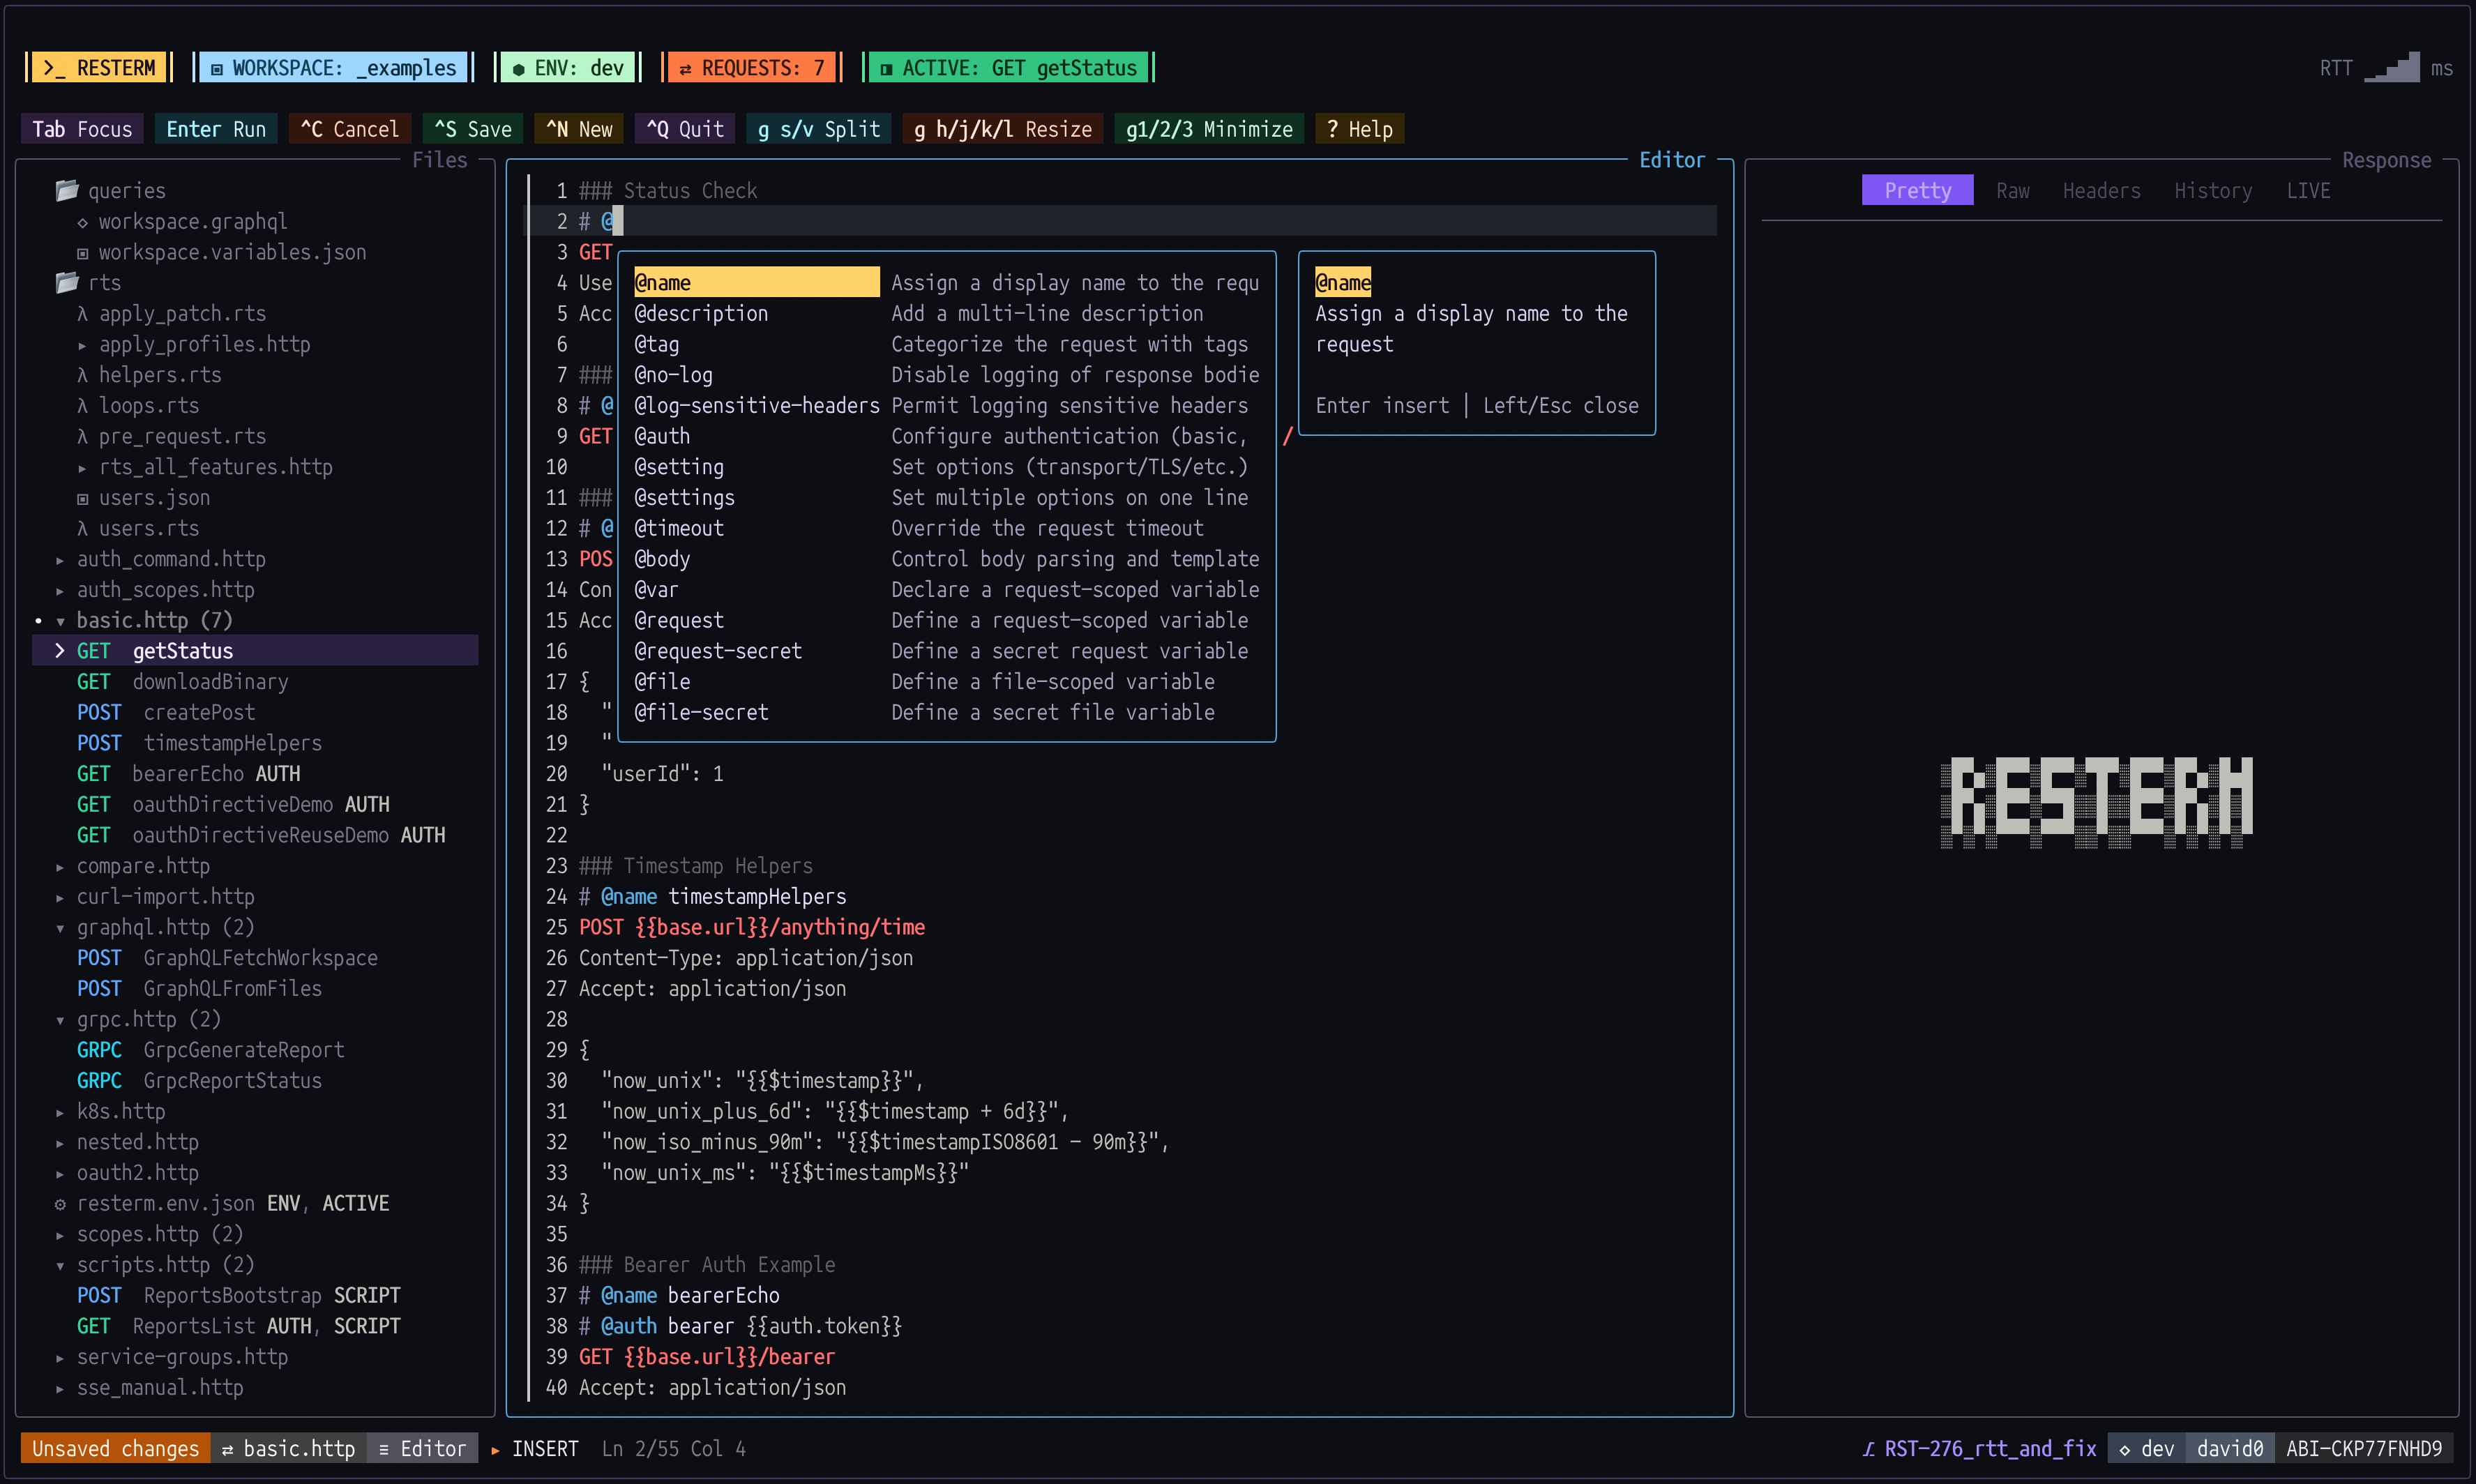 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 owasp/pysap
pysap is an open source Python library that provides modules for crafting and sending packets using SAP's NI, Diag, Enqueue, Router, MS, SNC, IGS,…
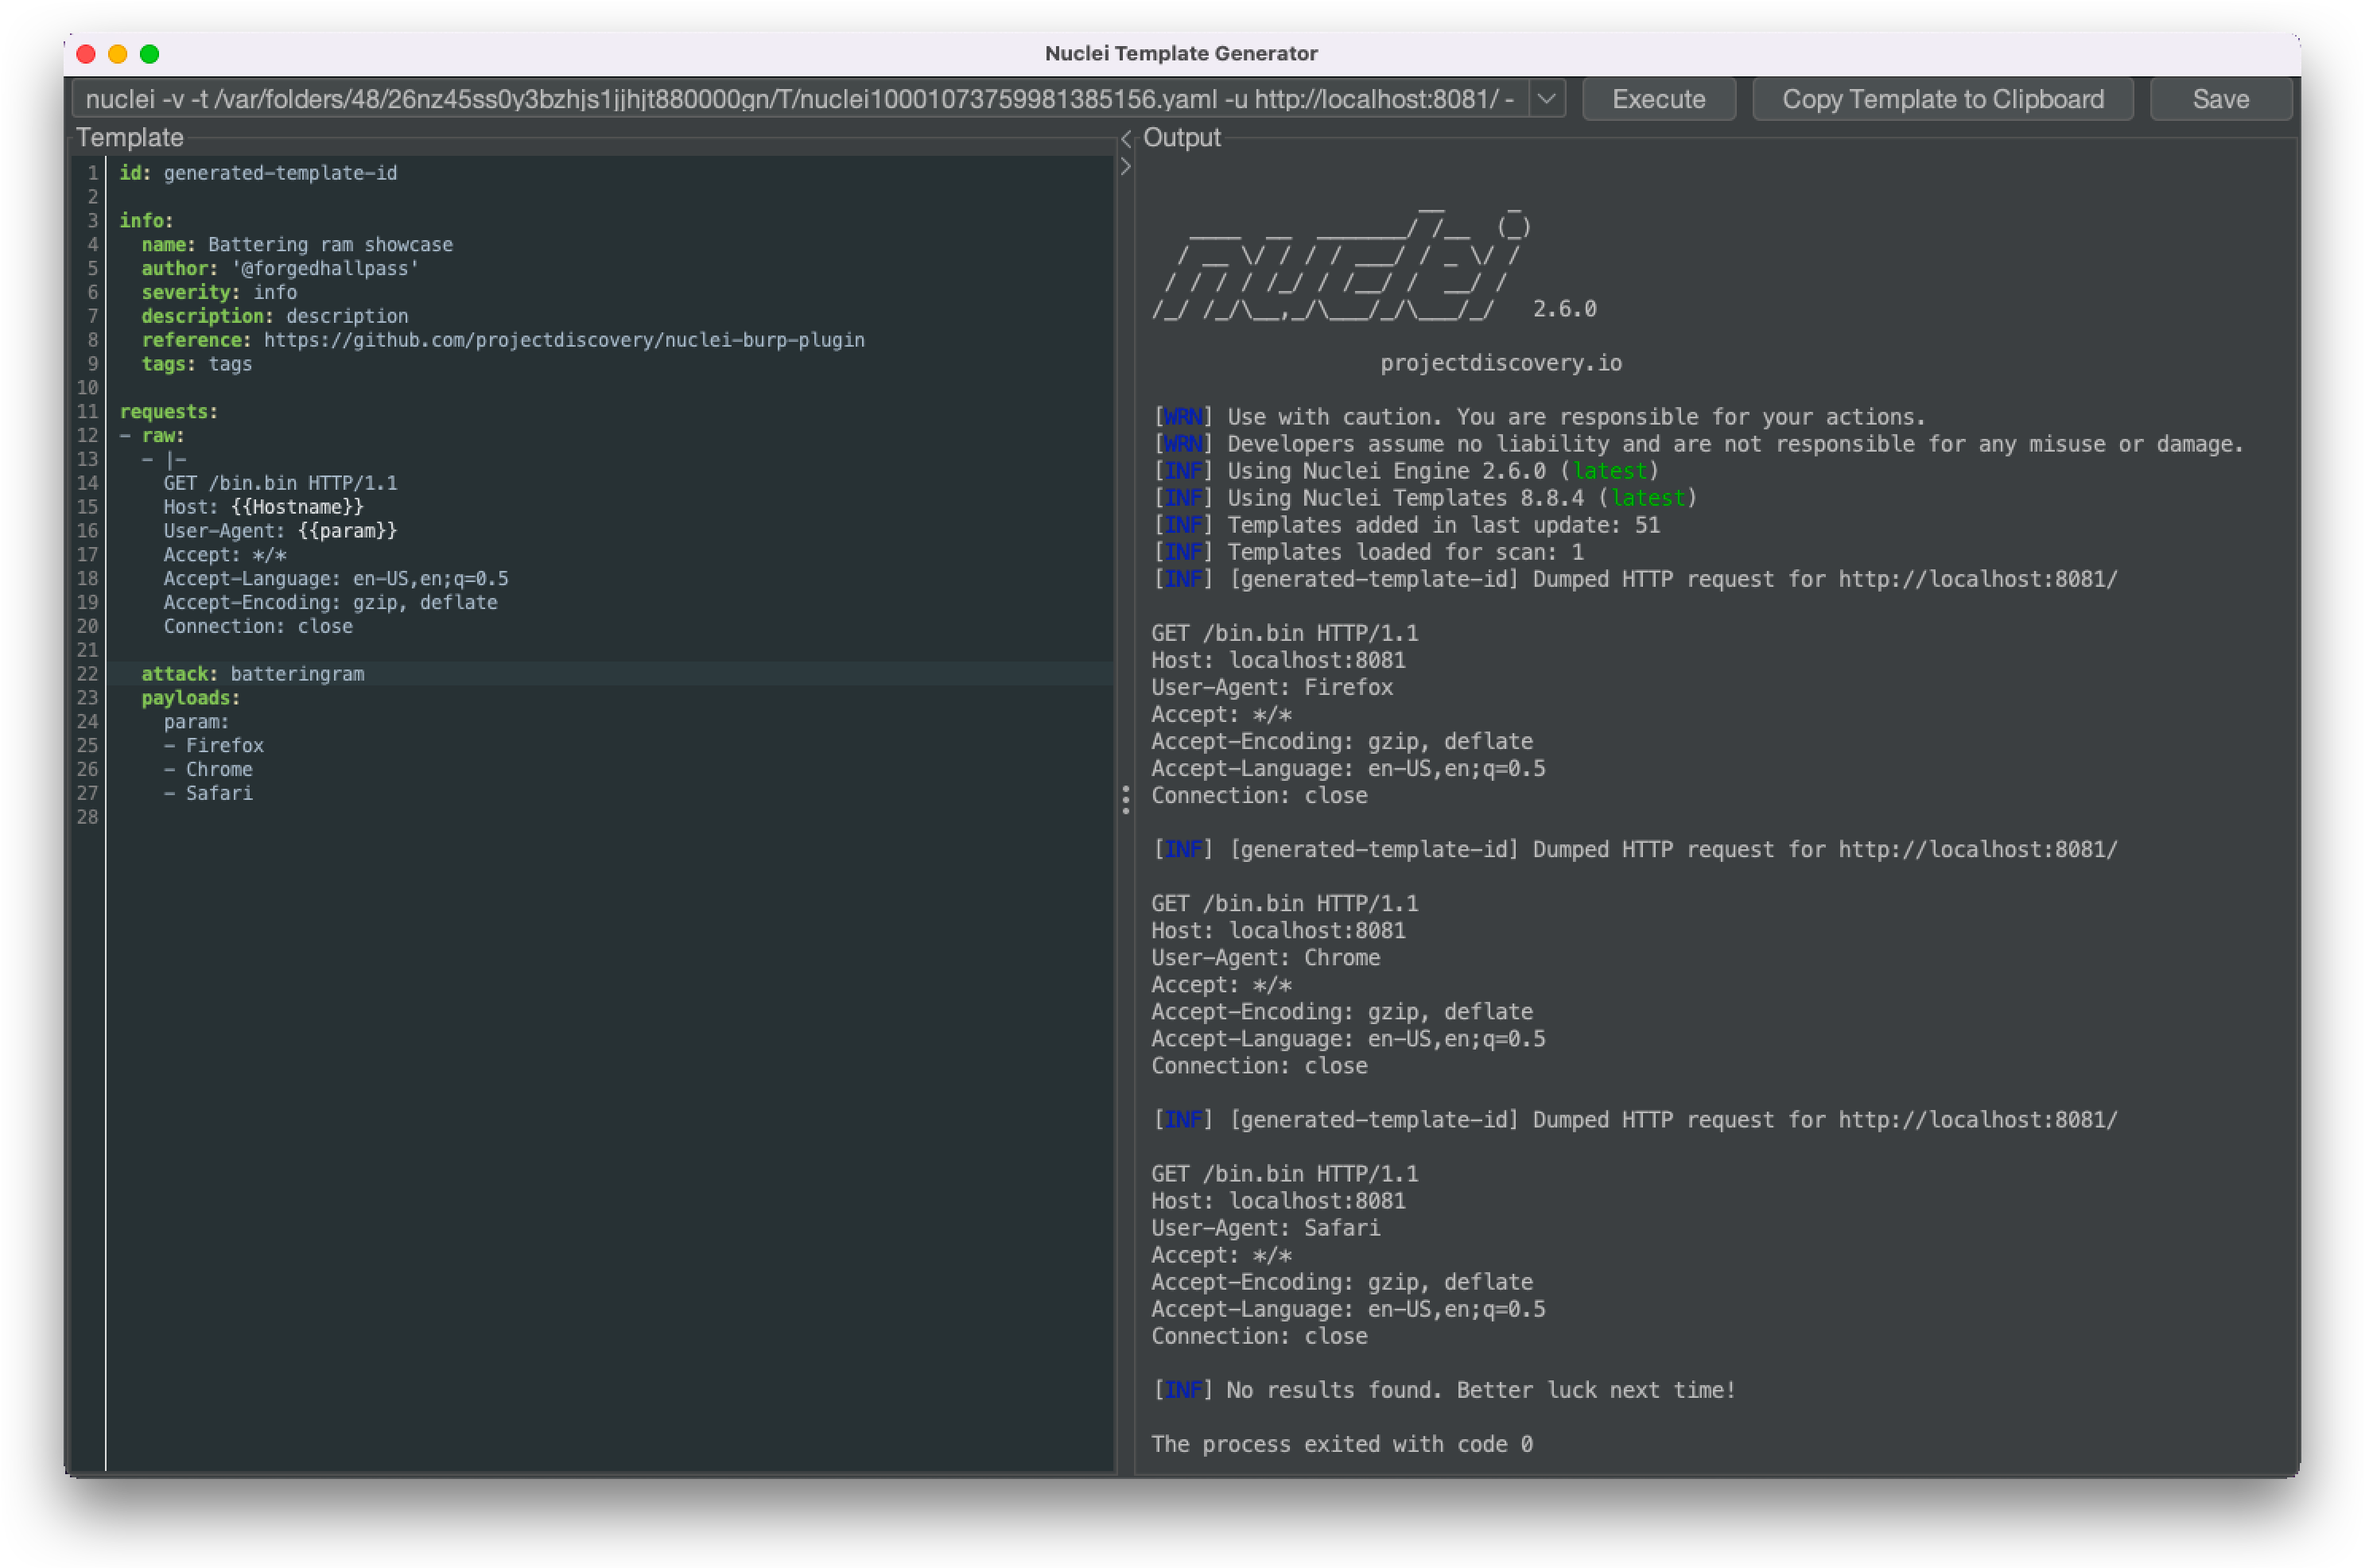 projectdiscovery/nuclei-burp-plugin
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 t0xodile-swig/http3-adapter
Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
 vid4l-07/roxy
Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…
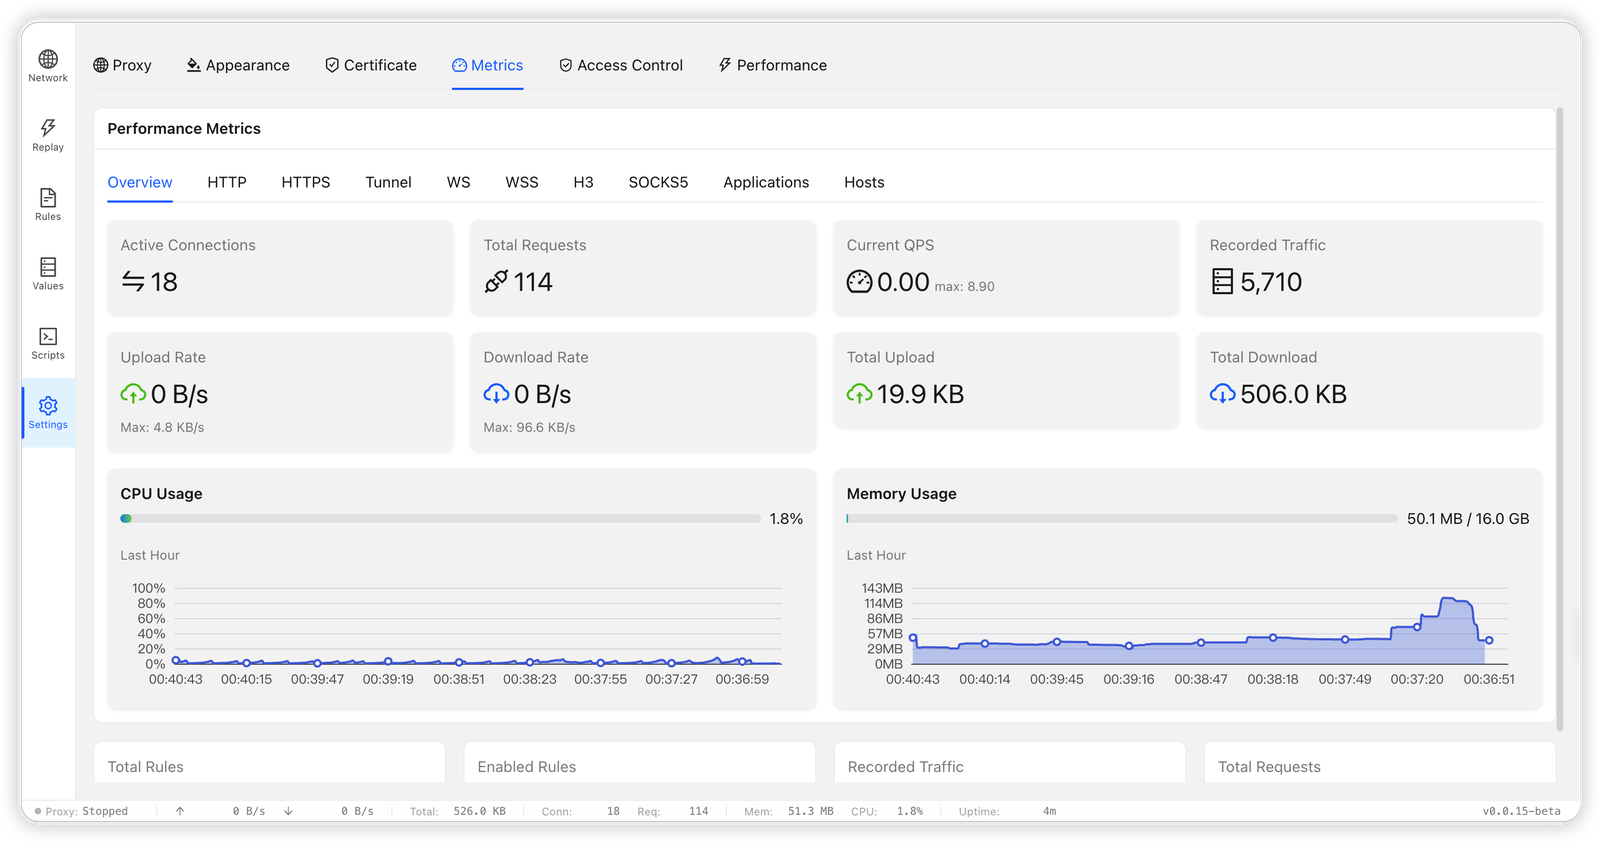 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
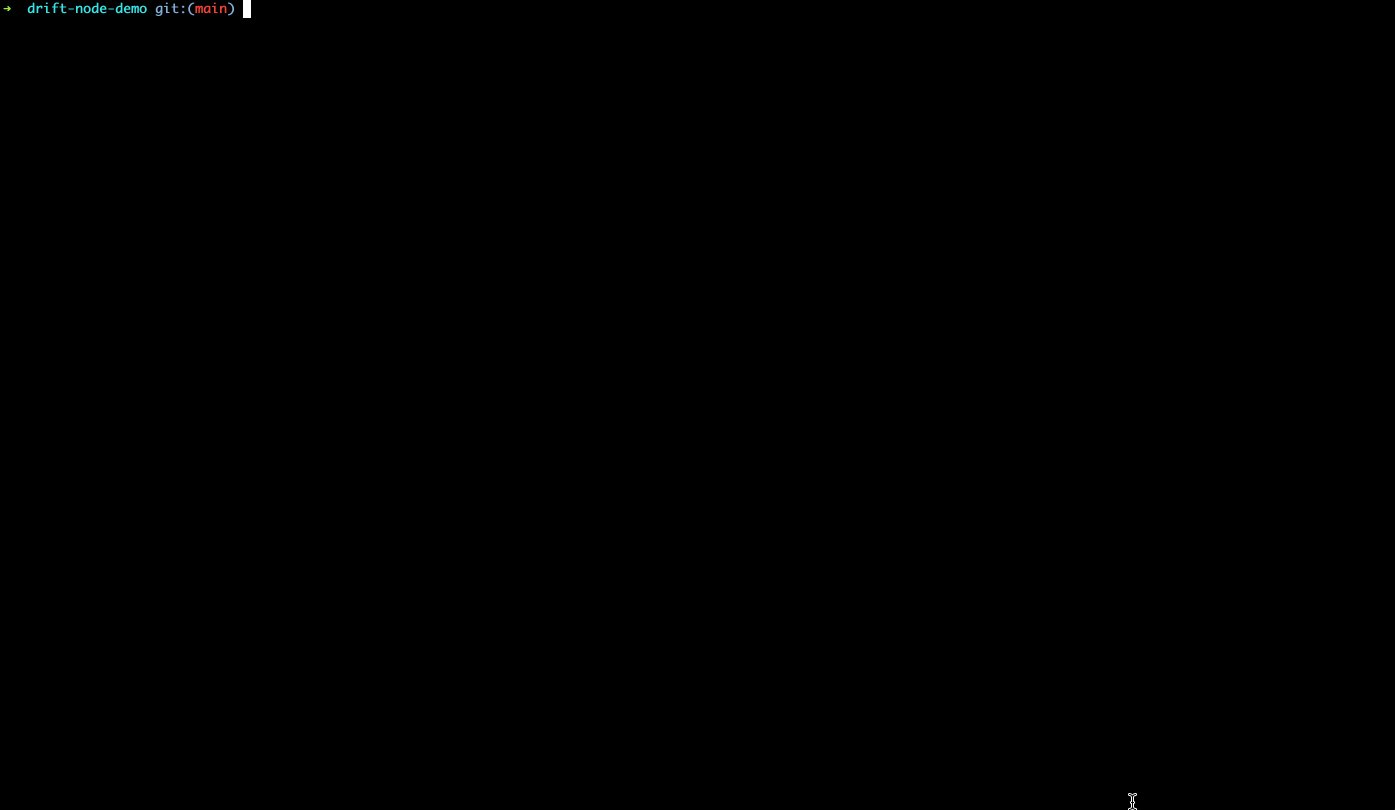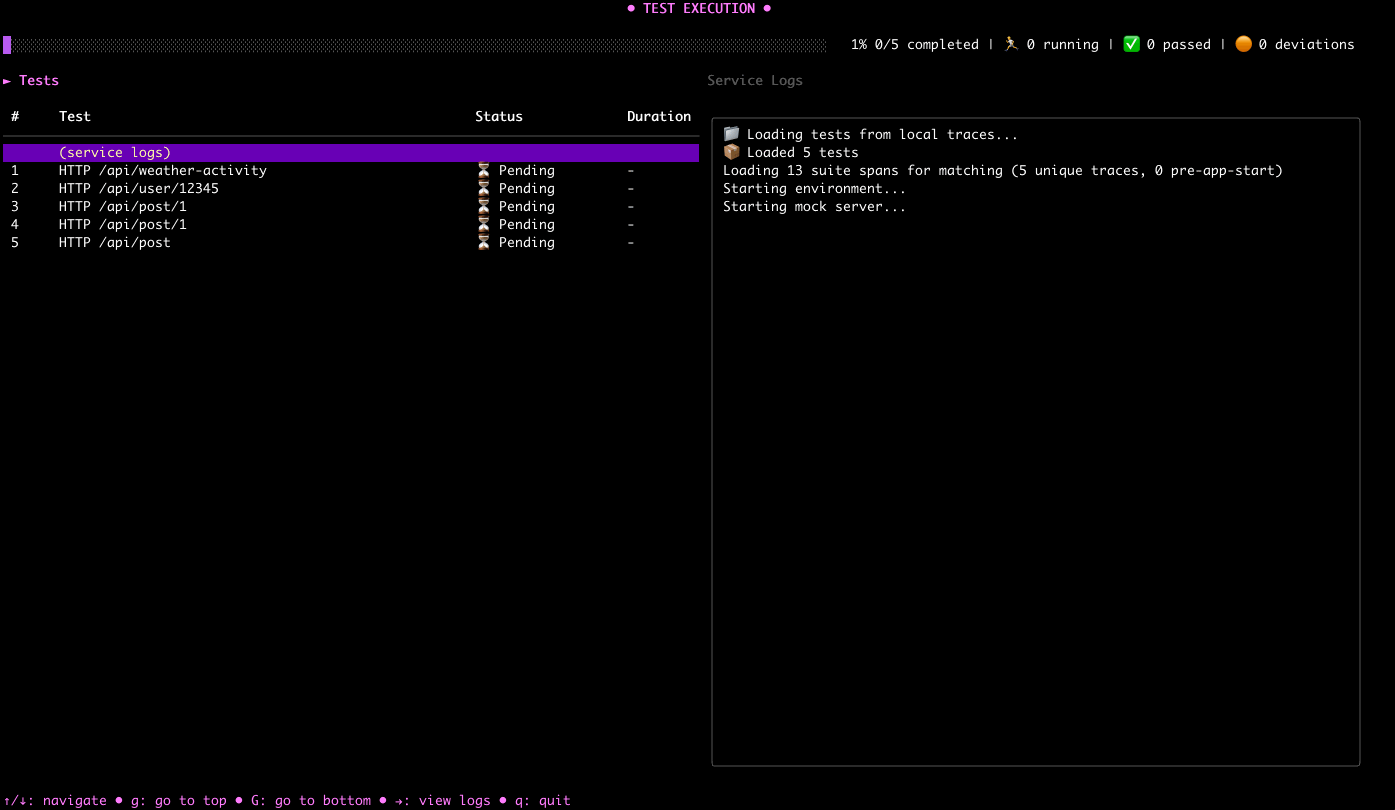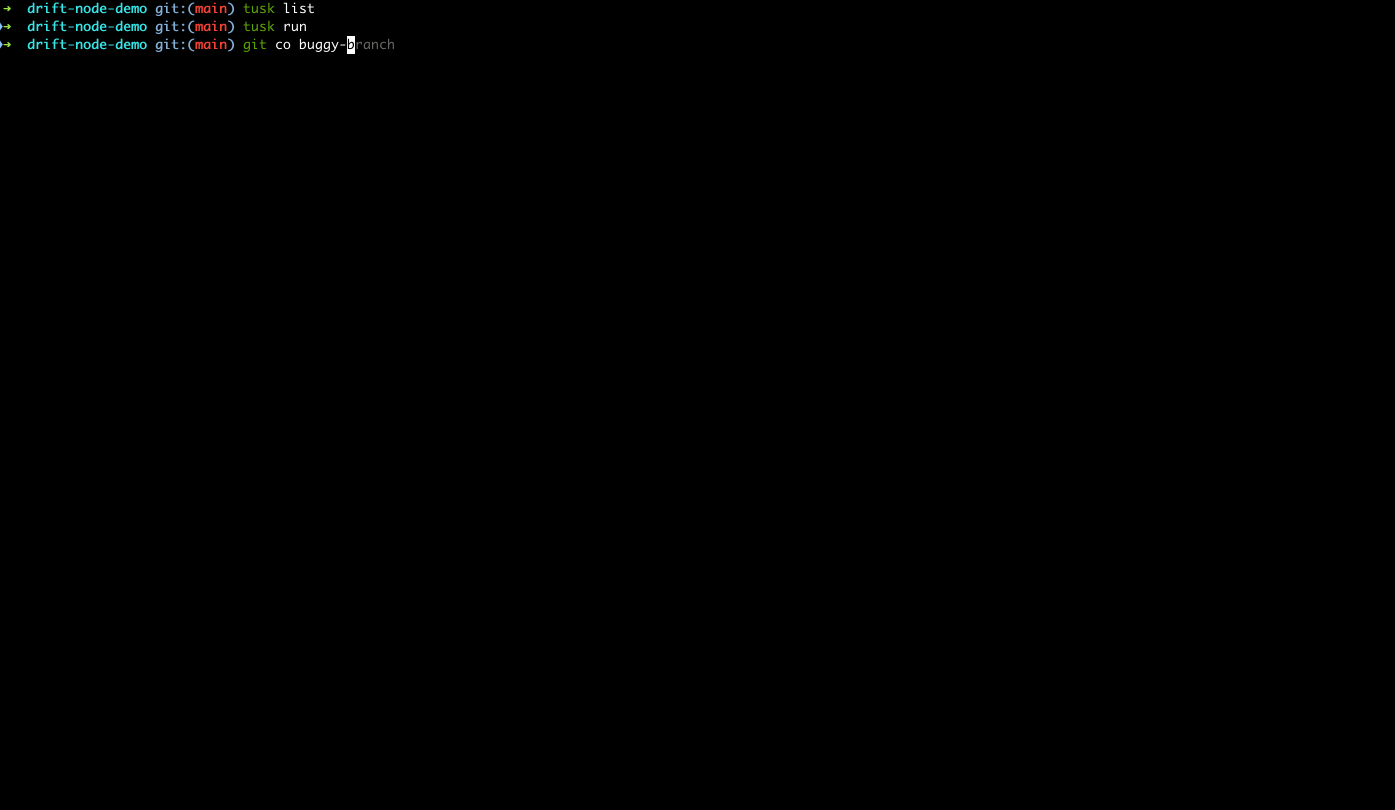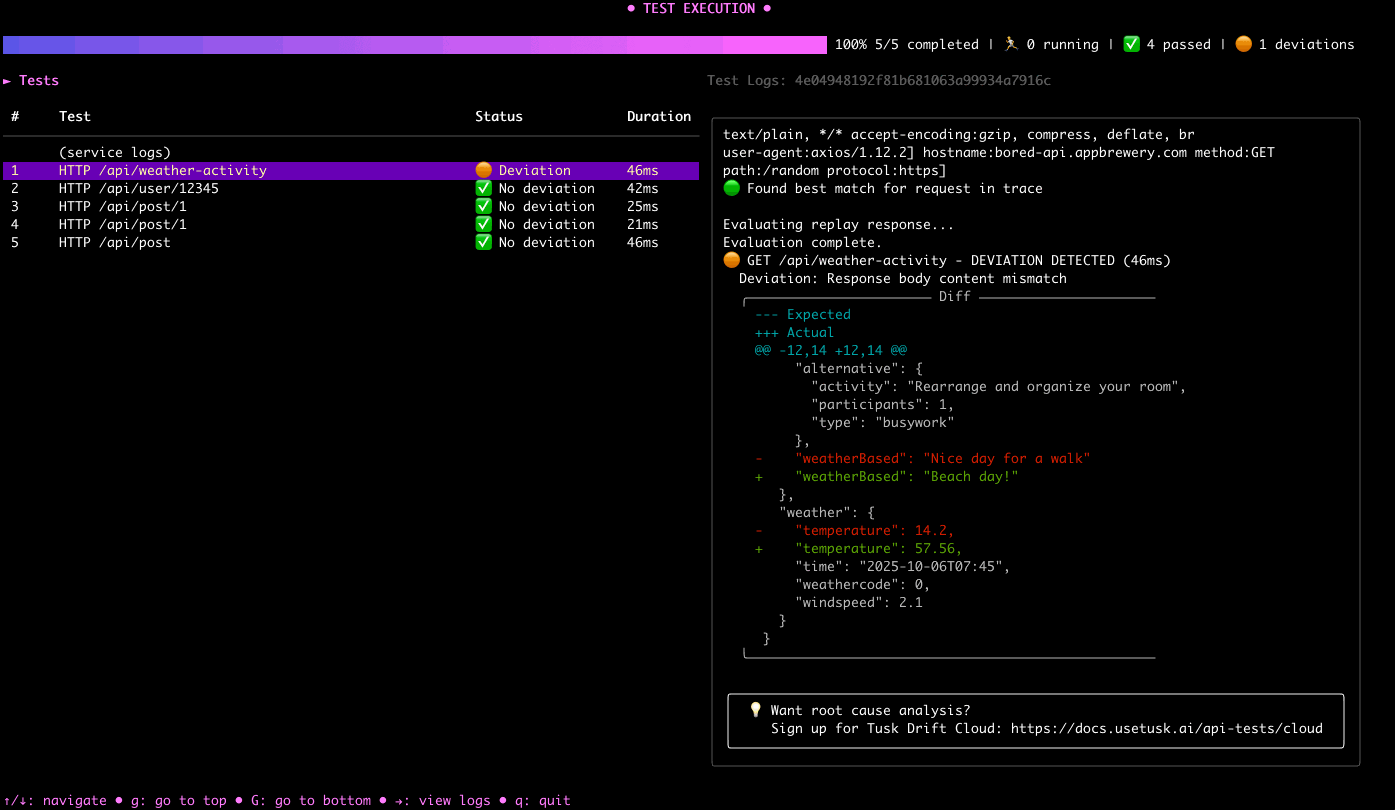
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 use-tusk/drift-node-sdk
Node.js SDK for capturing and replaying API calls made to/from your service
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 owasp/cwe-sdk-javascript
A Common Weakness Enumeration (CWE) Node.js SDK compliant with MITRE / CAPEC
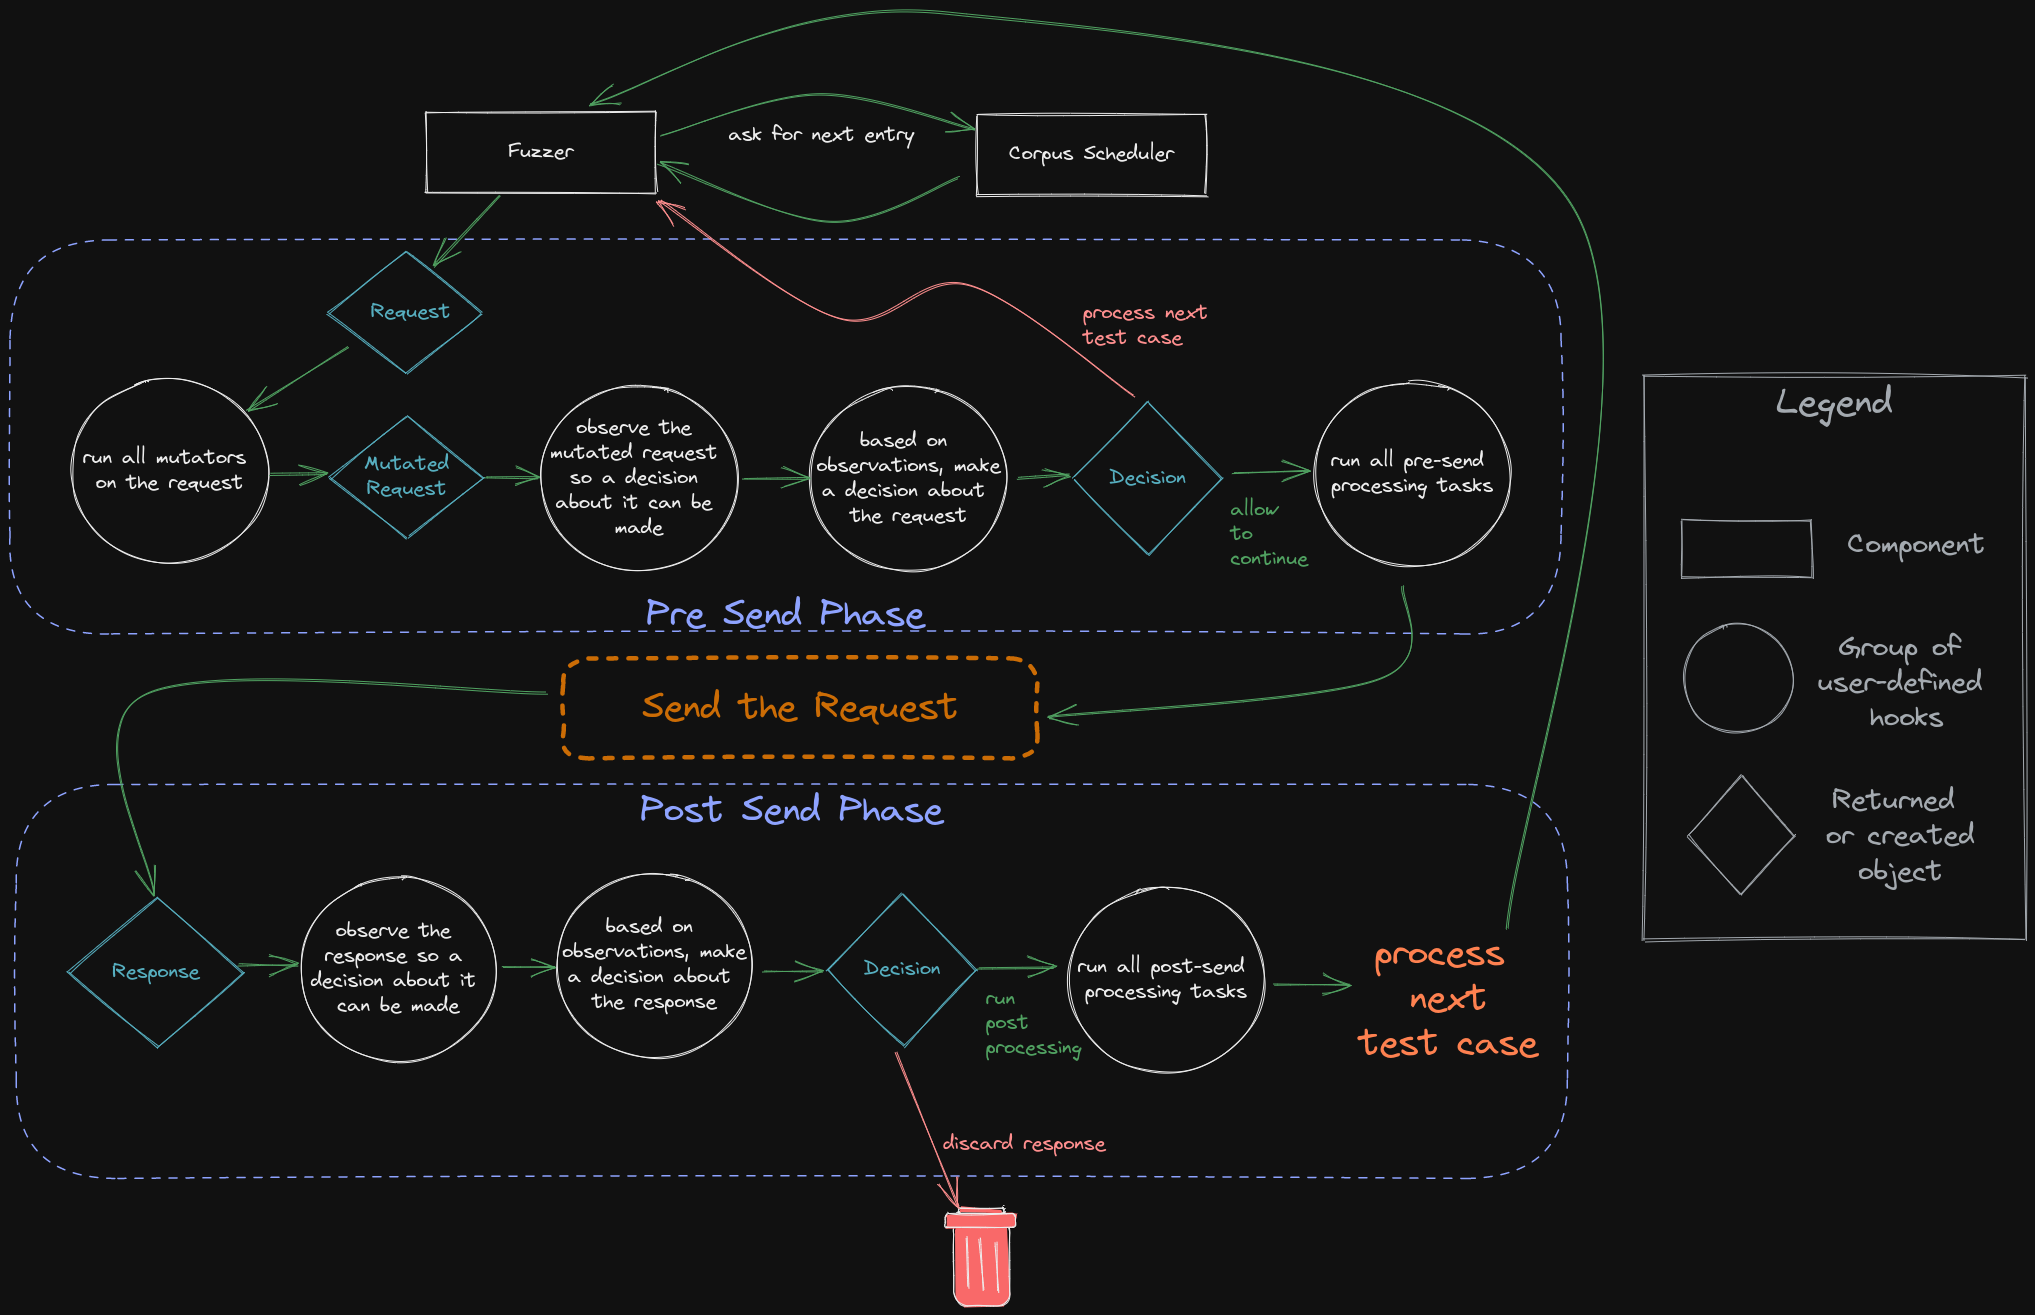 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
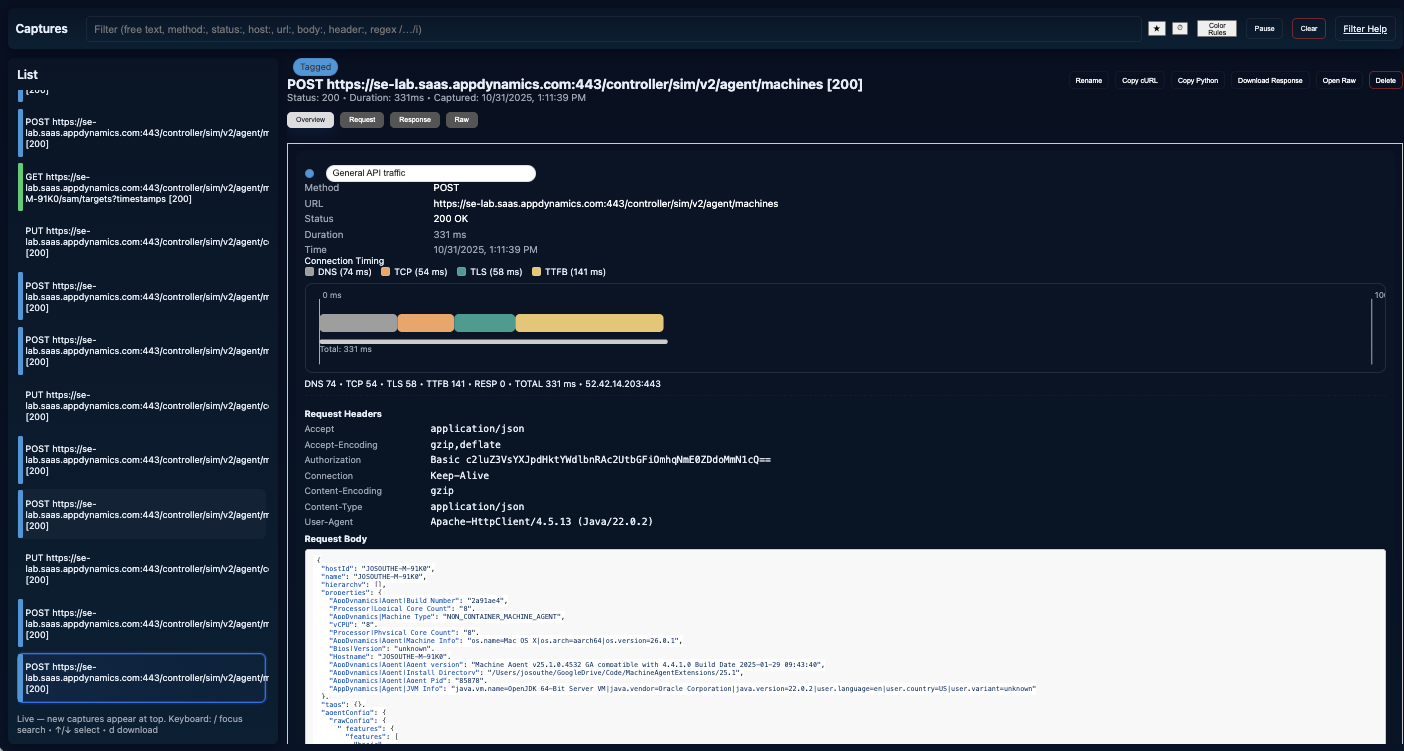 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication