

drakvuf-sandbox
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
dynamic-analysis-sandboxingforensicsmalware-analysis+2
1.3k
cert-polska/drakvuf-sandboxAutomated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 google/security-research
This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
 otrf/ossem
Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…
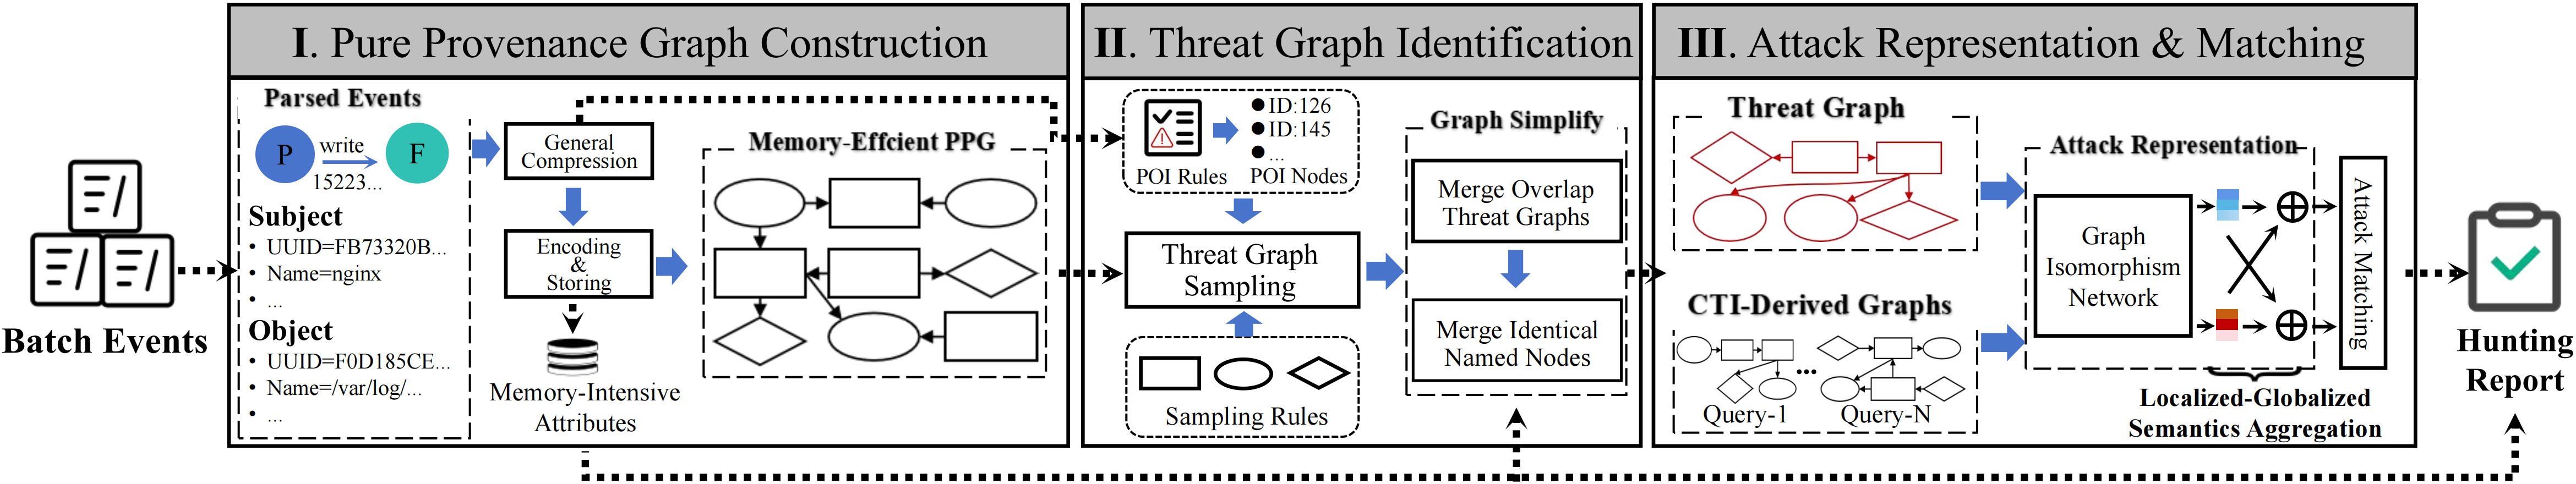 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
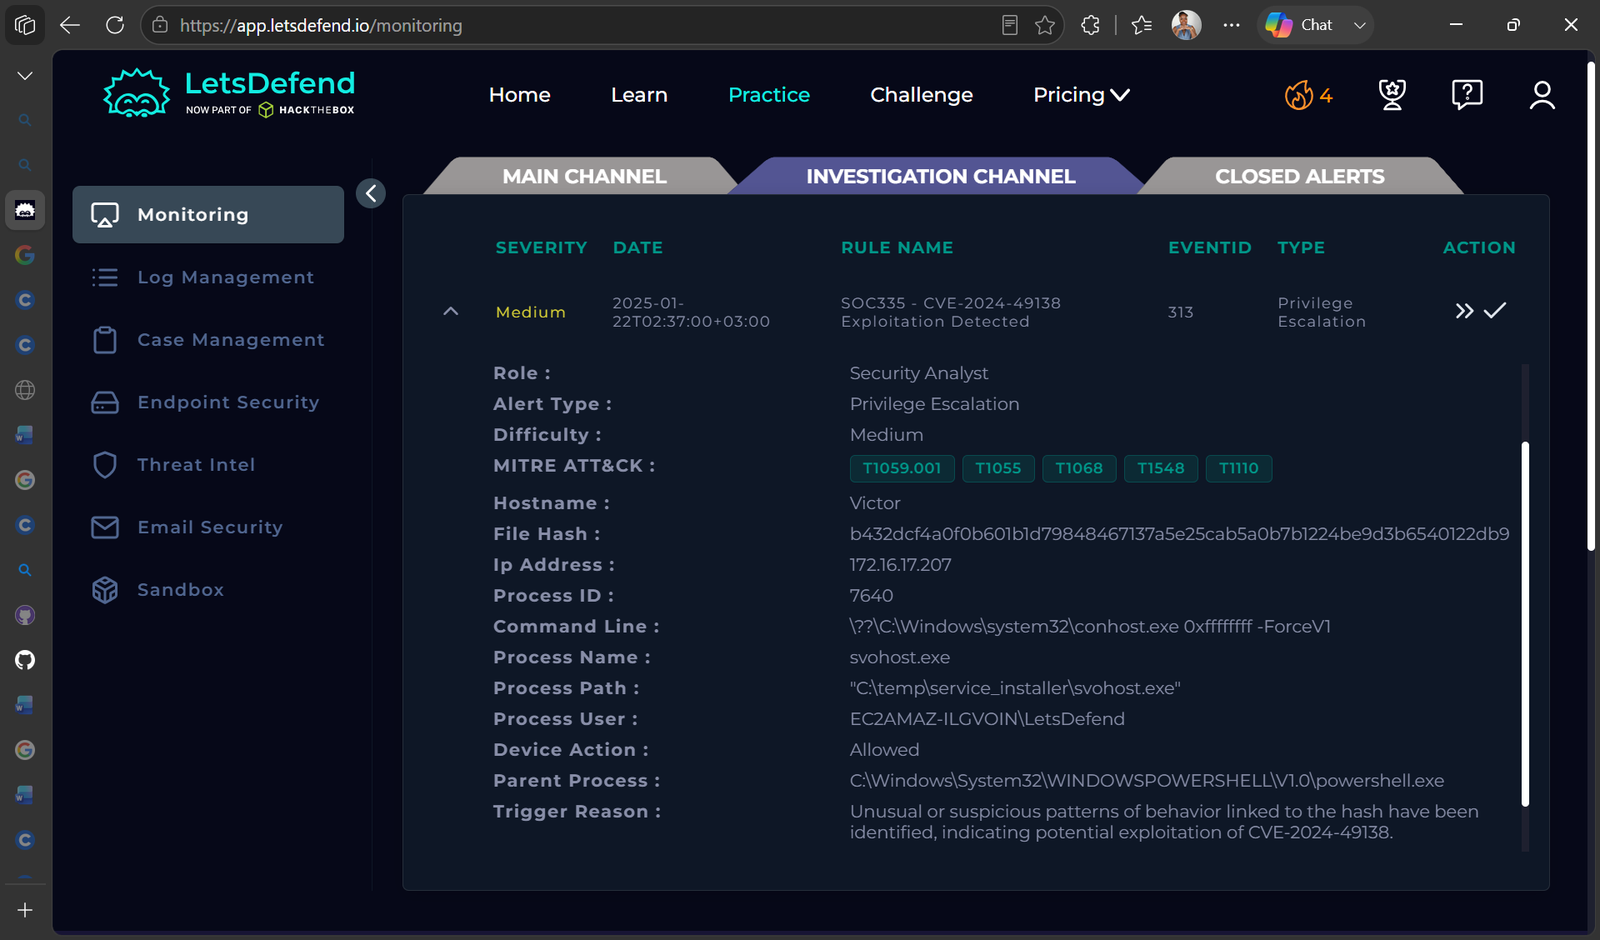 nadineelliottcyber/soc335-cve-2024-49138-investigation
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
 sana-404/cve-2026-8838-mitigation-and-detection
Detection and mitigation scripts for CVE-2026-8838, providing vulnerability scanning, configuration auditing, and incident response guidance to…
 decemberus/bughub
CVEHub of CVE-2023-1498 and CVE-2023-1500
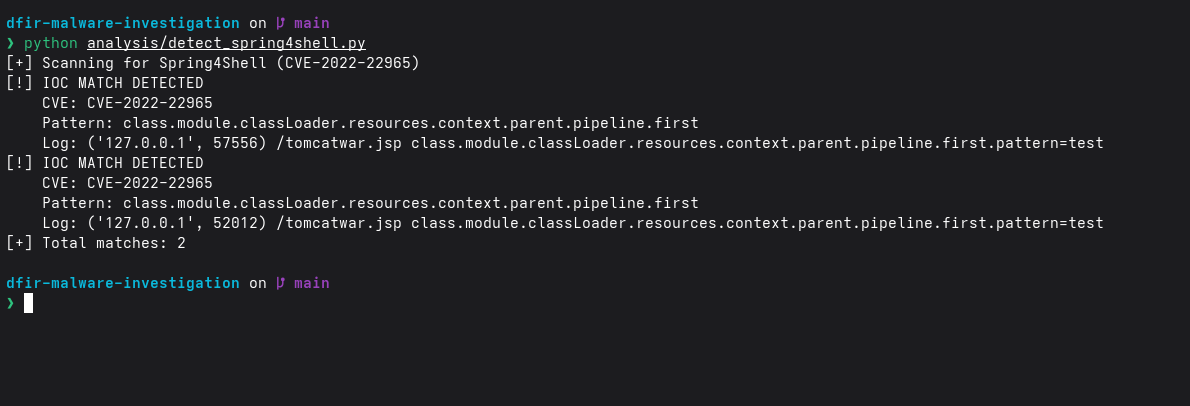 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
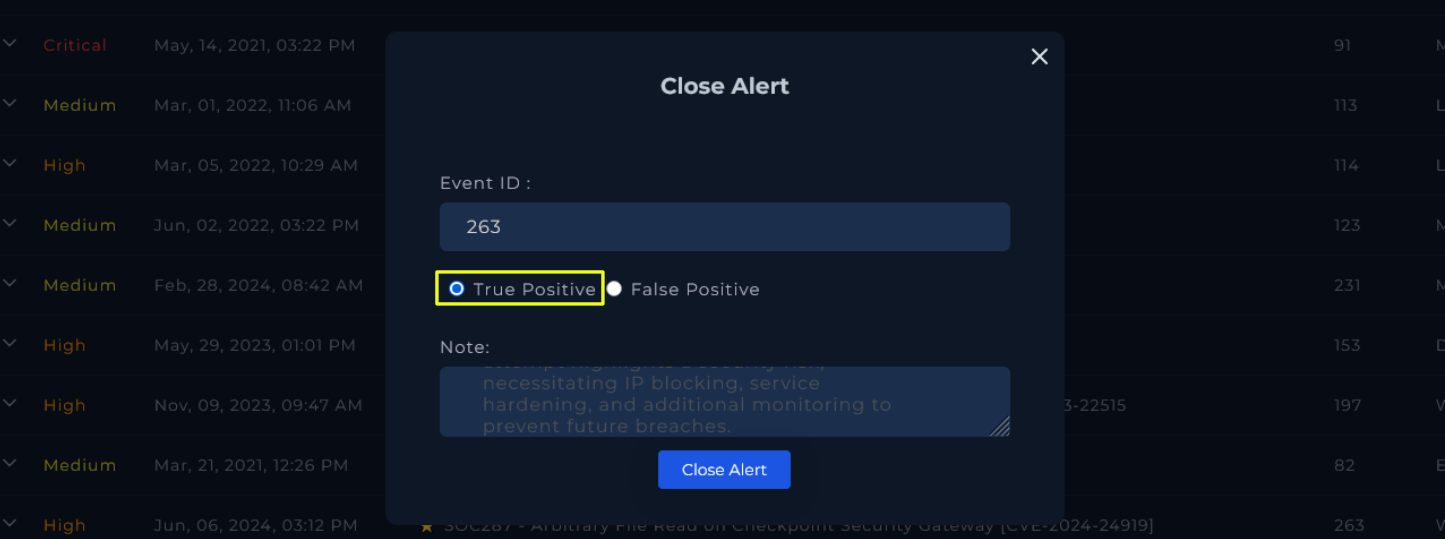 macuchegit/detecting-and-analyzing-cve-2024-24919-exploitation
Step-by-step walkthrough of detecting and analyzing CVE-2024-24919 exploitation using a SIEM platform, including traffic analysis, IOC documentation,…
 bridg3ops/soc335-cve-2024-49138-exploitation-detected
Detailed incident response walkthrough analyzing CVE-2024-49138 exploitation on Windows, covering process tree analysis, IOC identification, and…
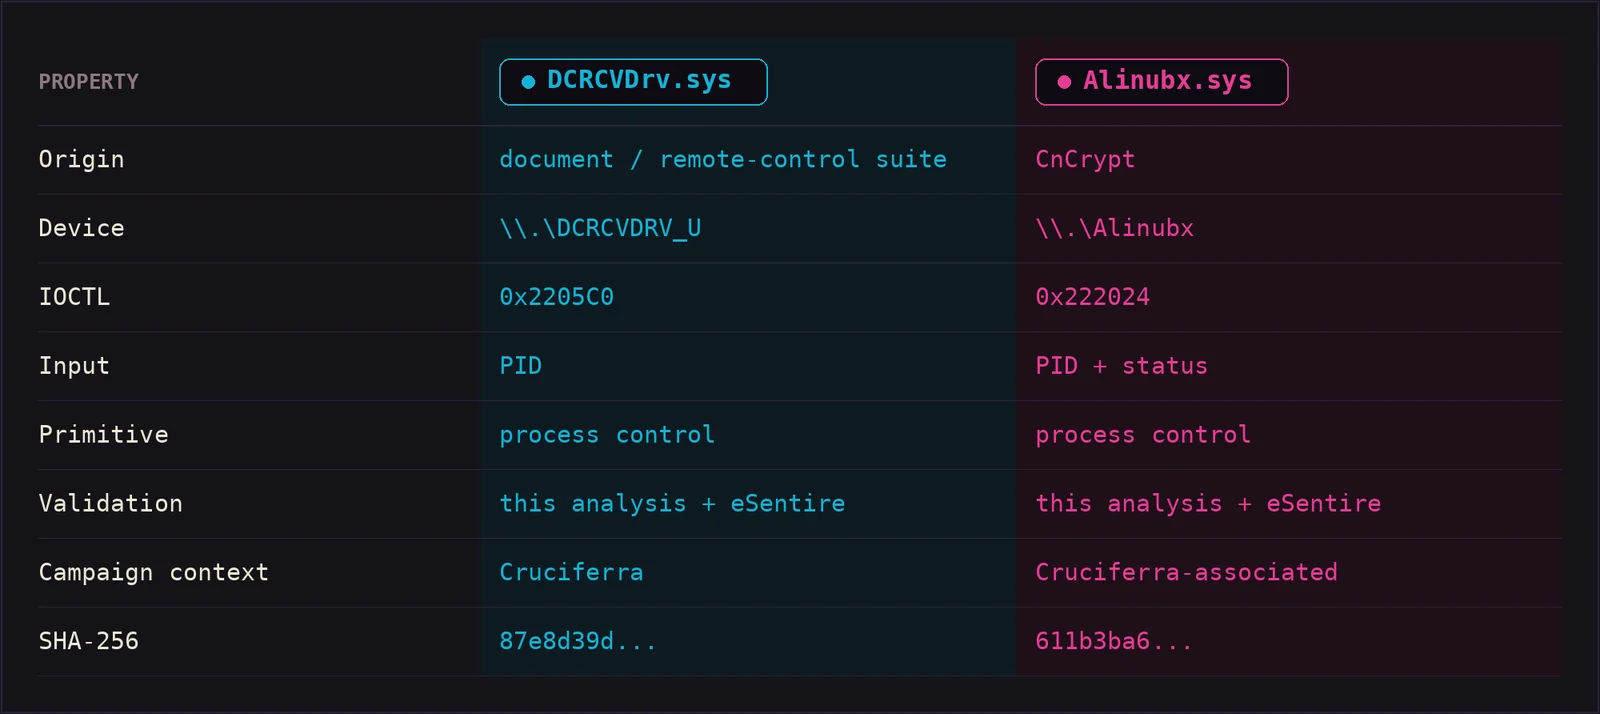 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 ciscocsirt/gosint
The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
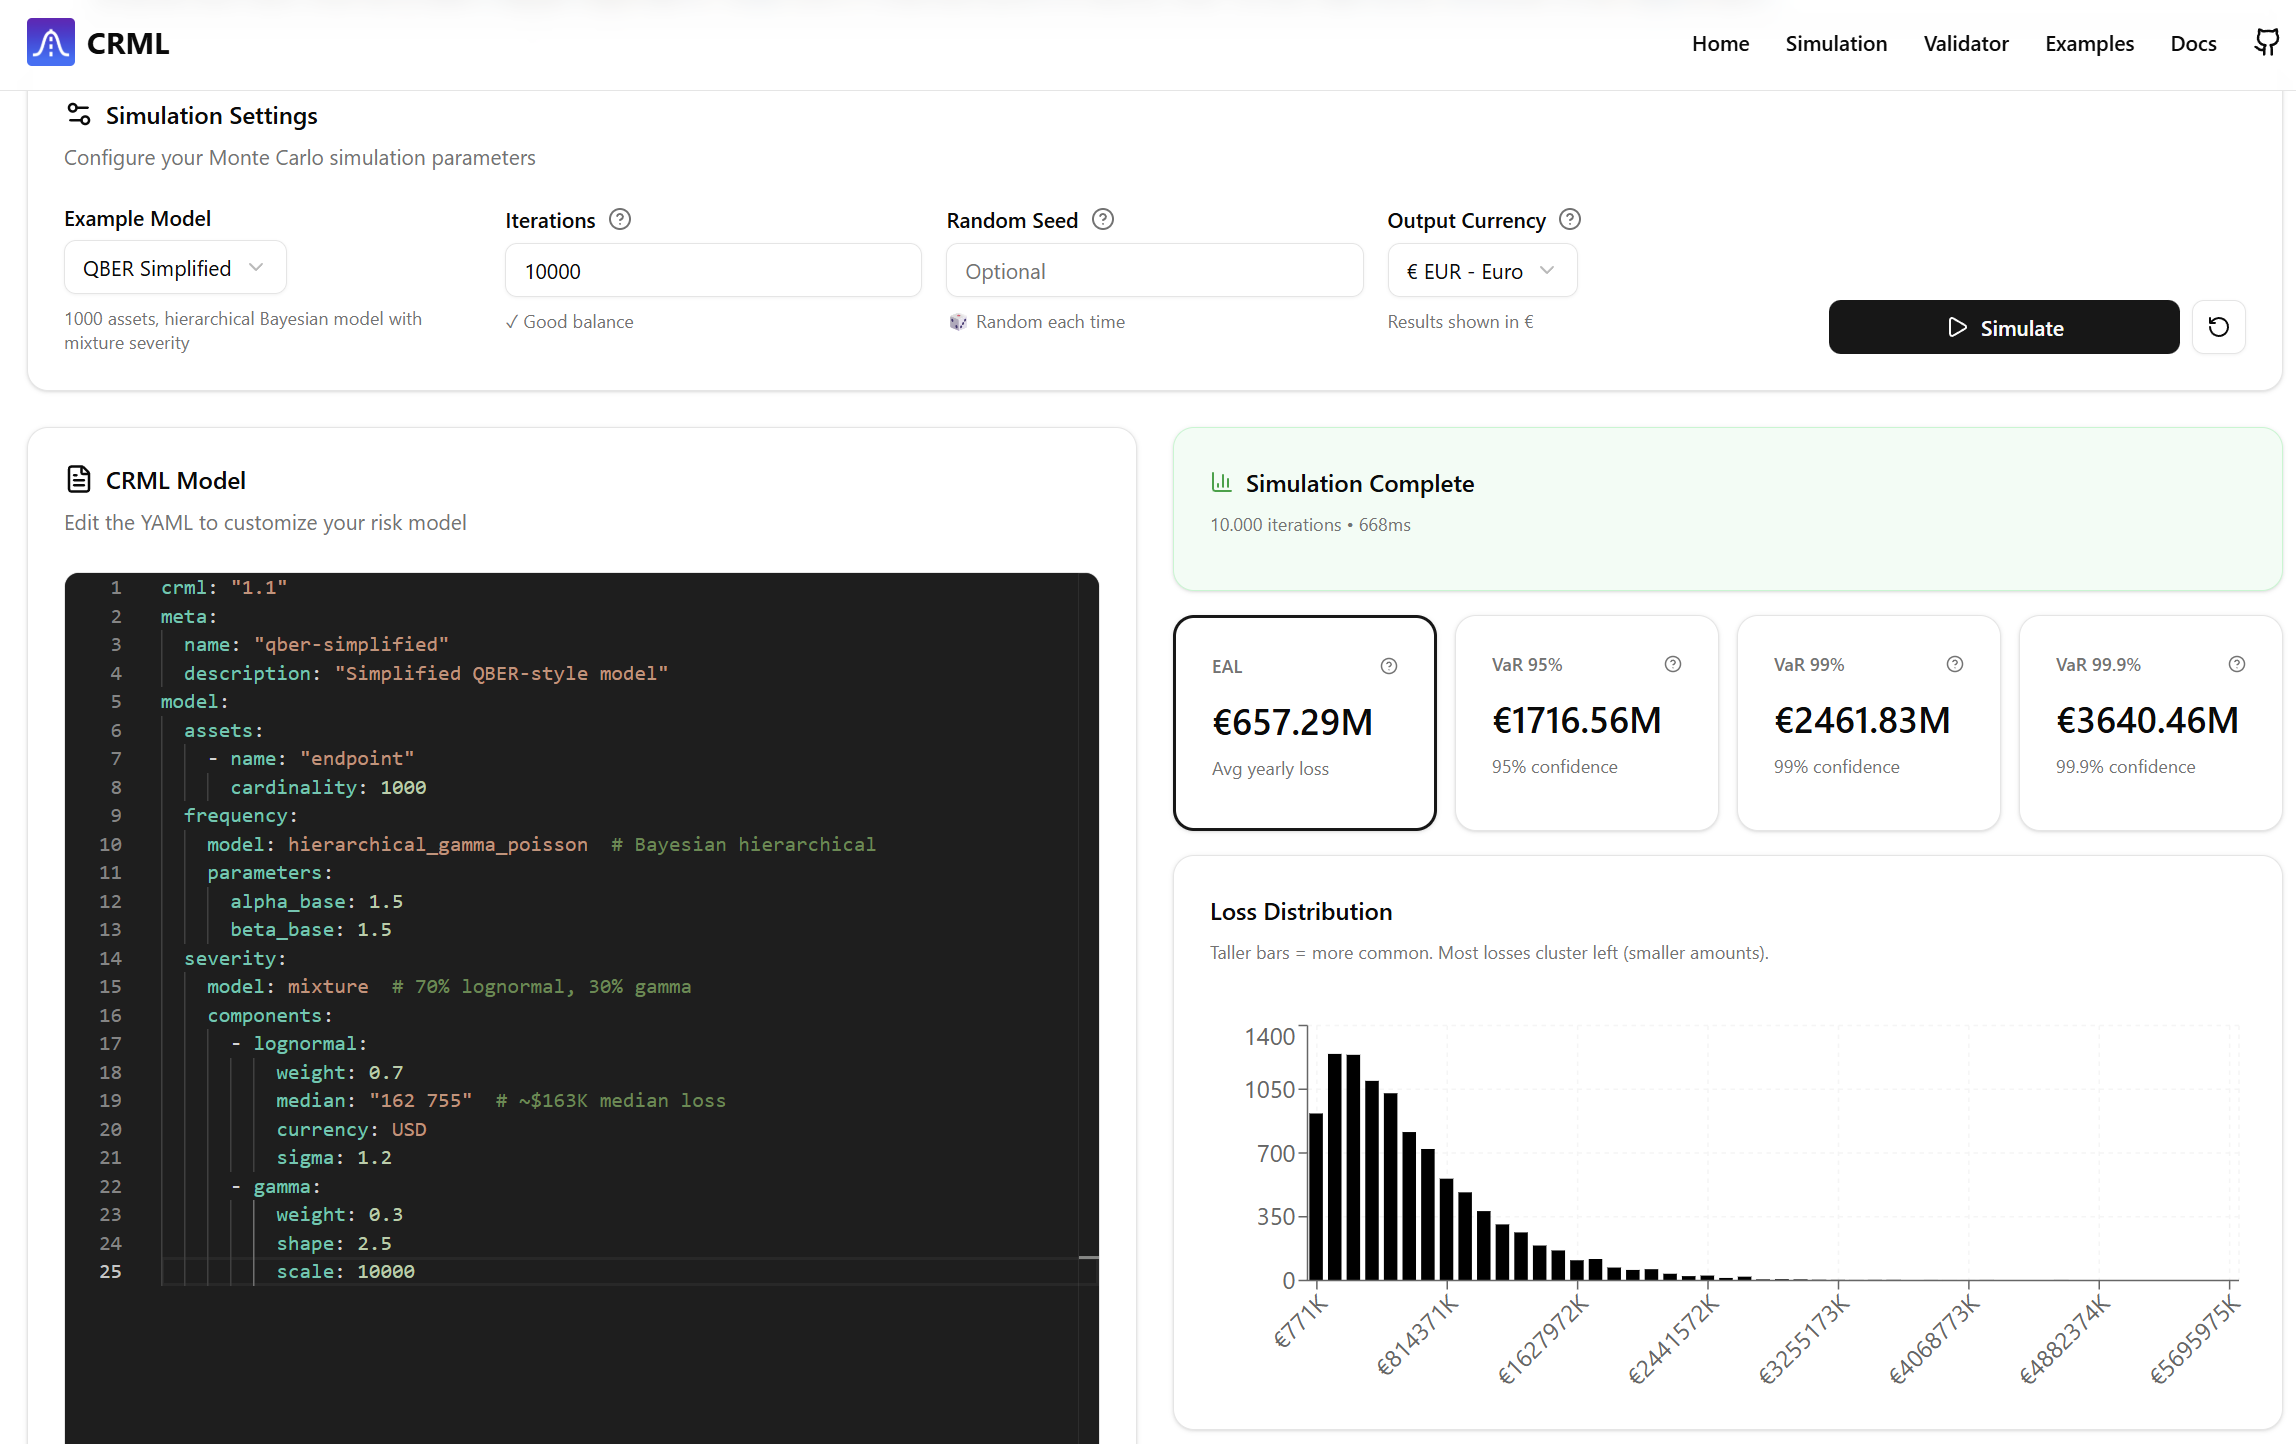 faux16/crml
Open-source declarative language for cyber risk modeling. Build Bayesian risk models like QBER, FAIR Monte Carlo engines, and enterprise risk…