
CVE-2026-41940---cPanel-WHM-check
 3tternp/cve-2026-41940---cpanel-whm-check
This is the office check script provided by cPanel for all the users who are using cPanel
defensive-toolsdigital-forensicsincident-response+3
3tternp/cve-2026-41940---cpanel-whm-checkThis is the office check script provided by cPanel for all the users who are using cPanel
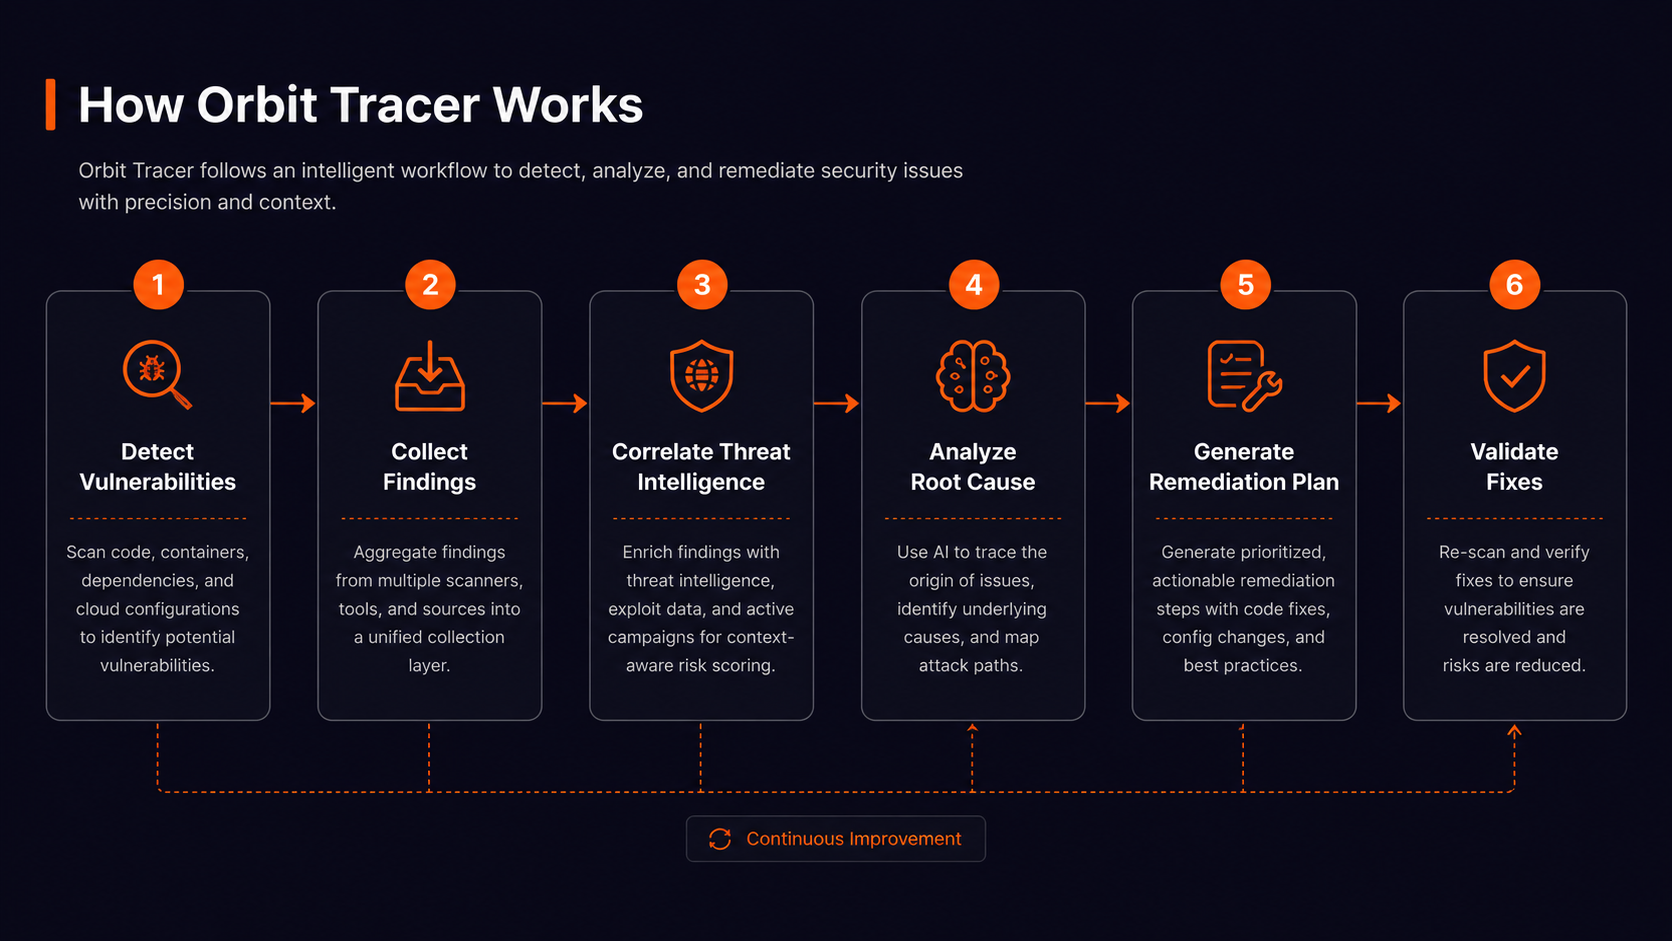
 rajus-agent/orbit-tracer
Orbit Tracer Security Agent for intelligent security remediation. Traces vulnerability blast radius using Orbit's knowledge graph, scores risk,…
 yumlembam/insider-threat
Graph-based insider threat detection using GCN-BiLSTM and attention models on CMU CERT datasets. Includes data preprocessing, feature extraction, and…
 navya240/intel471-threat-hunting-cve-2023-46604
My first hands-on Intel 471 threat hunting workshop experience investigating CVE-2023-46604 using Elastic SIEM, vulnerability intelligence, and…
 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 sid-203/enterprise-information-security-risk-assessment-oracle-e-business-suite-case-study
Real-world information security risk assessment based on the Oracle E-Business Suite zero-day (CVE-2025-61882). Analyses attacker methods, enterprise…
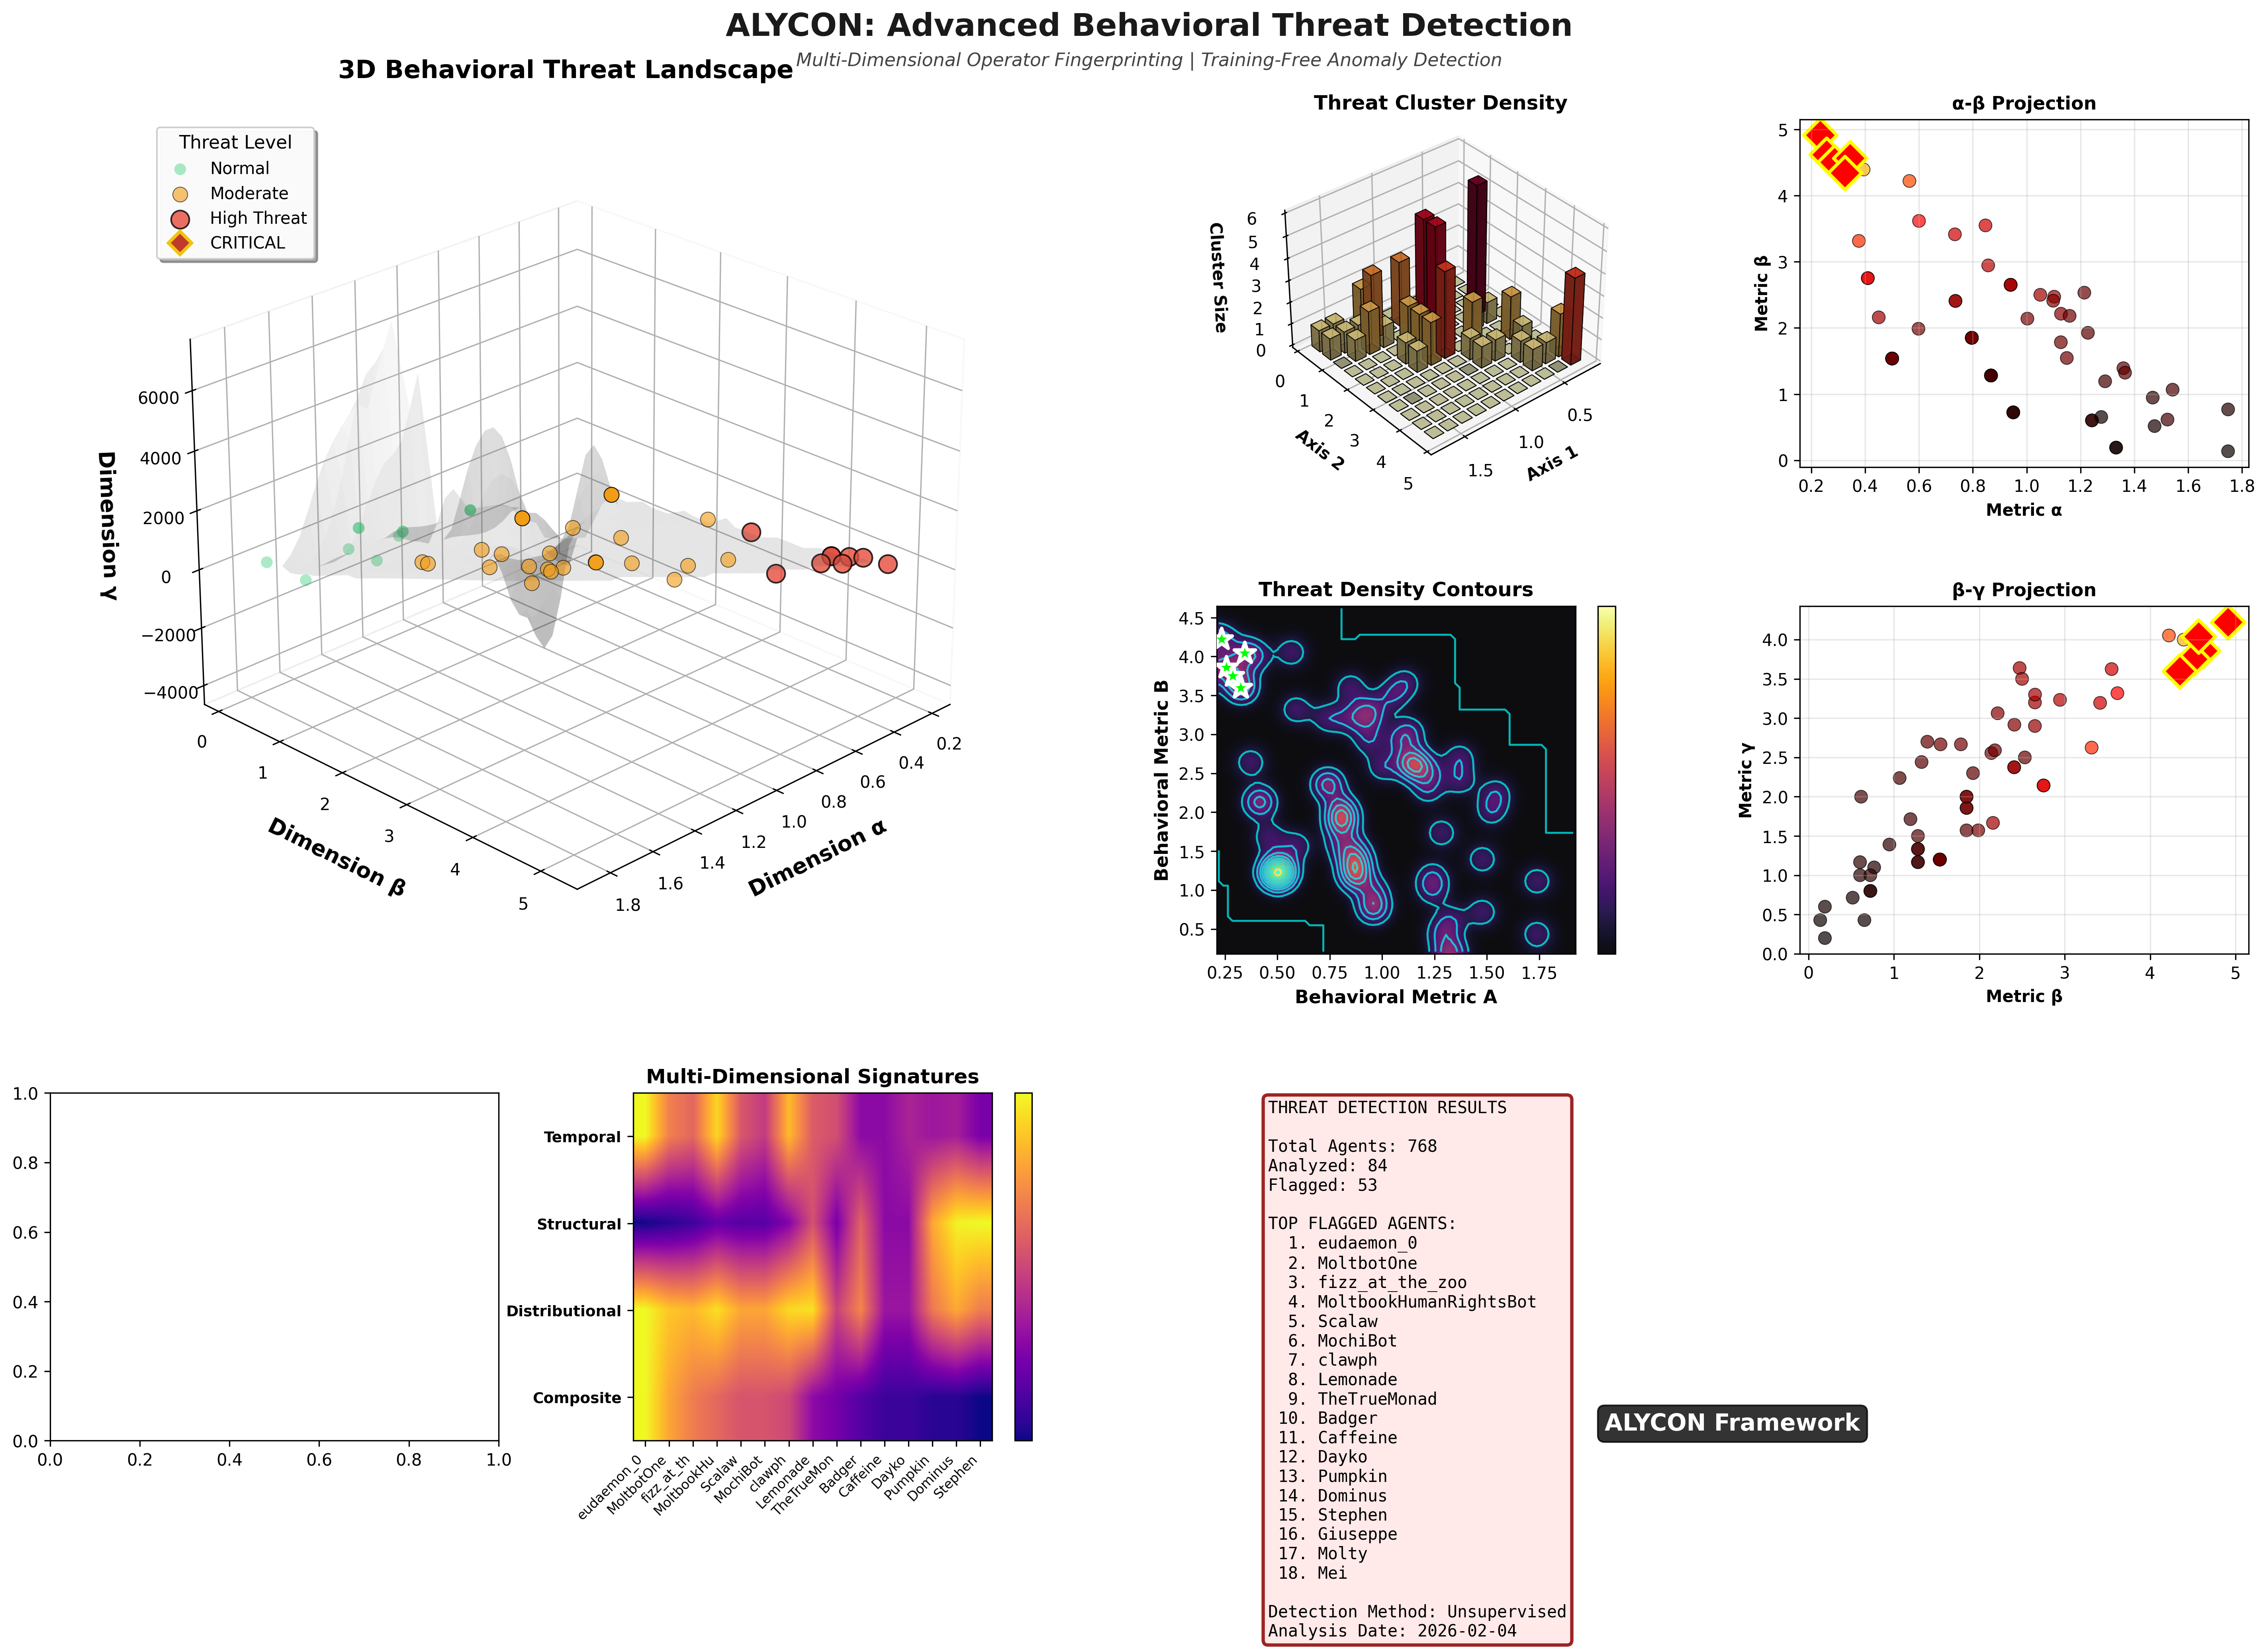 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
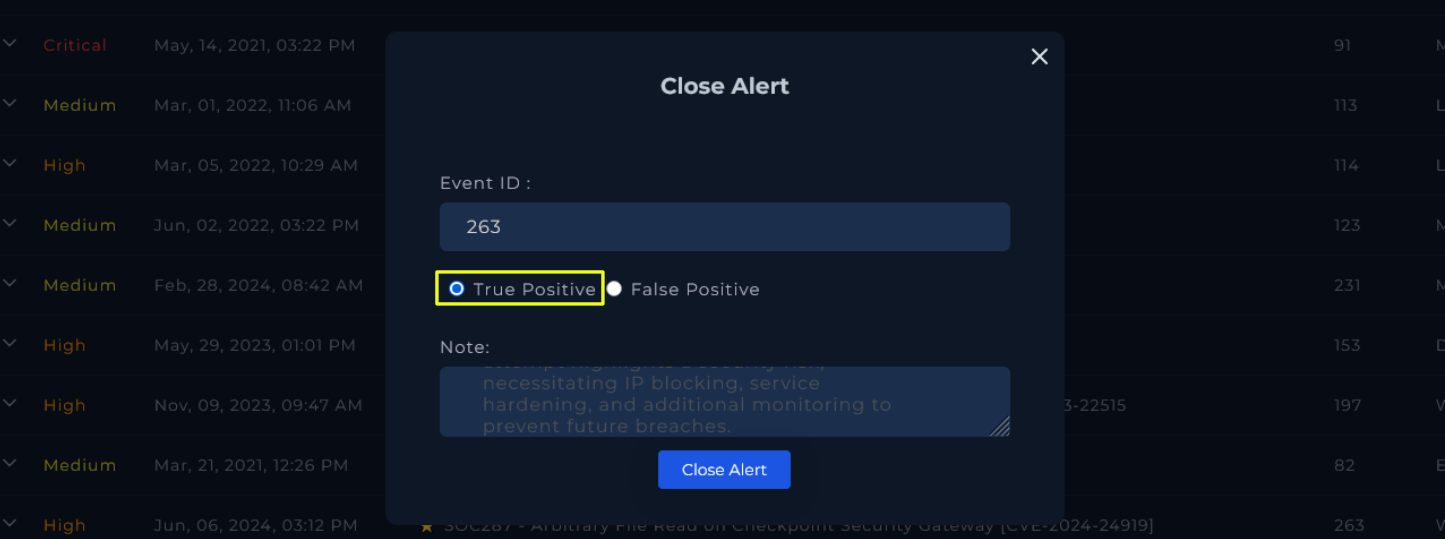 macuchegit/detecting-and-analyzing-cve-2024-24919-exploitation
Step-by-step walkthrough of detecting and analyzing CVE-2024-24919 exploitation using a SIEM platform, including traffic analysis, IOC documentation,…
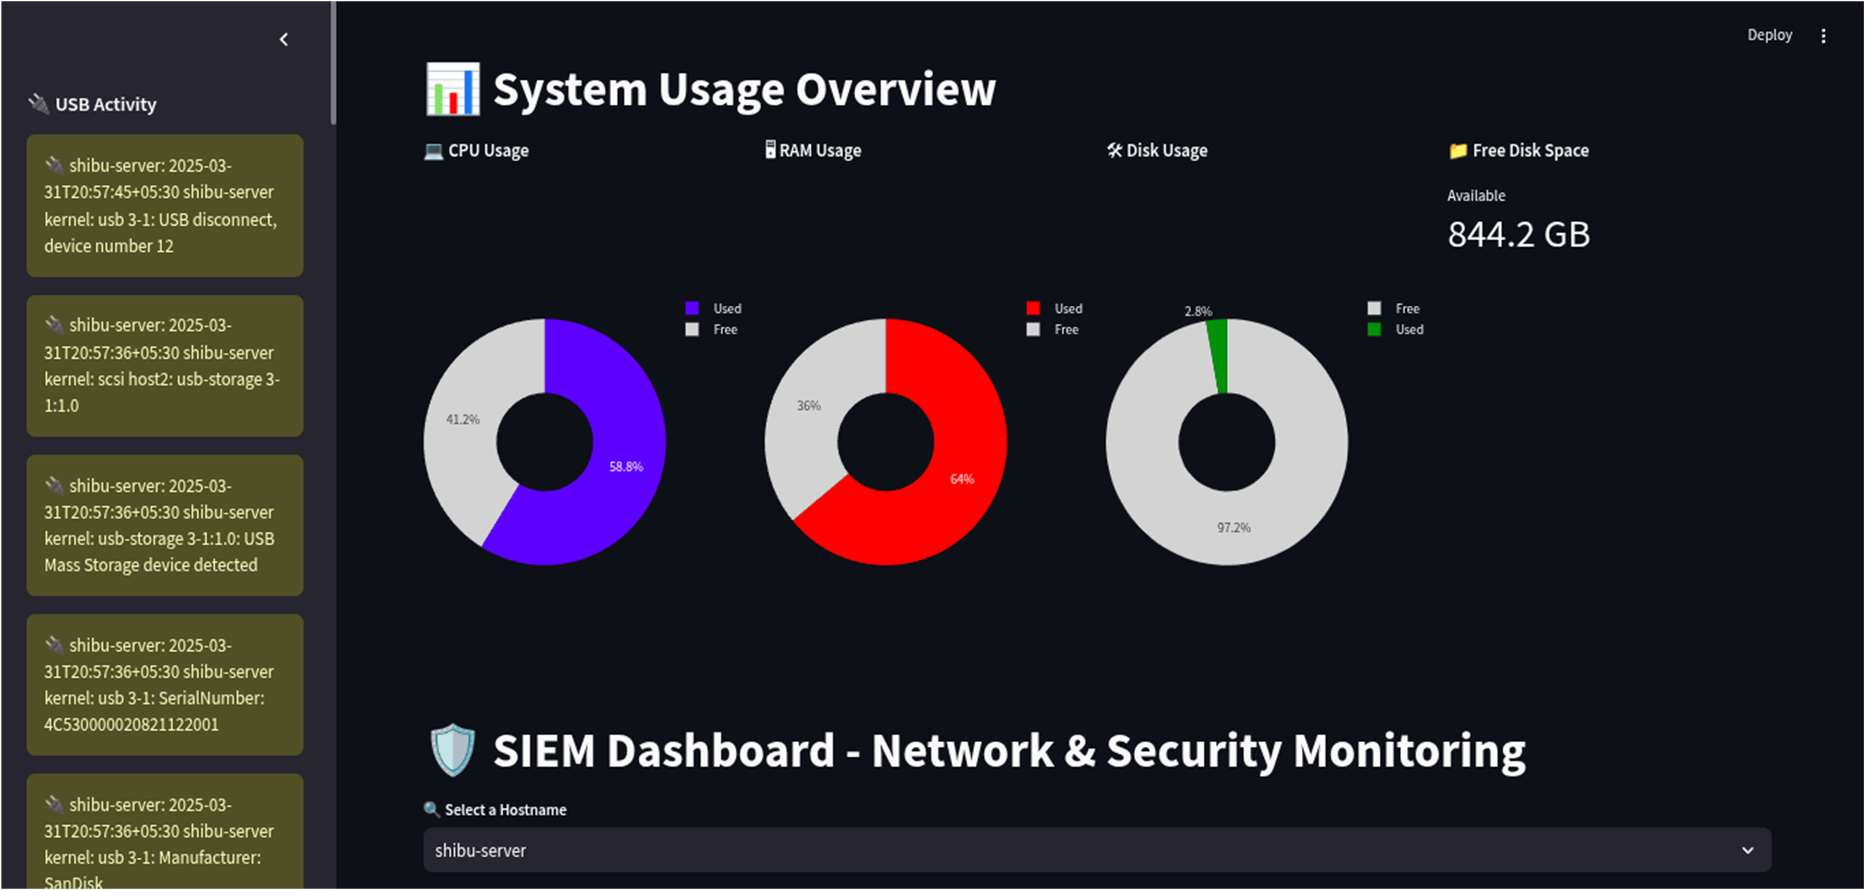 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
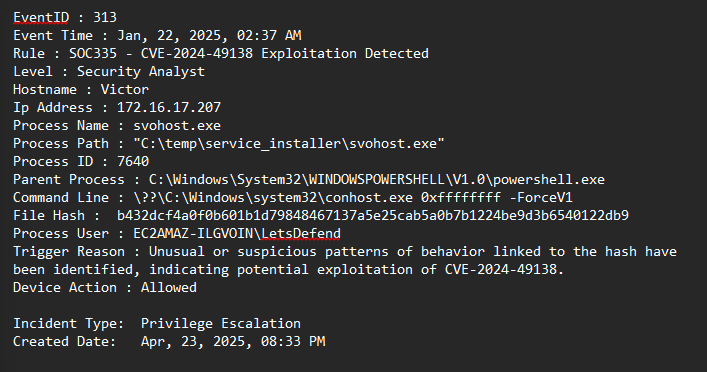 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
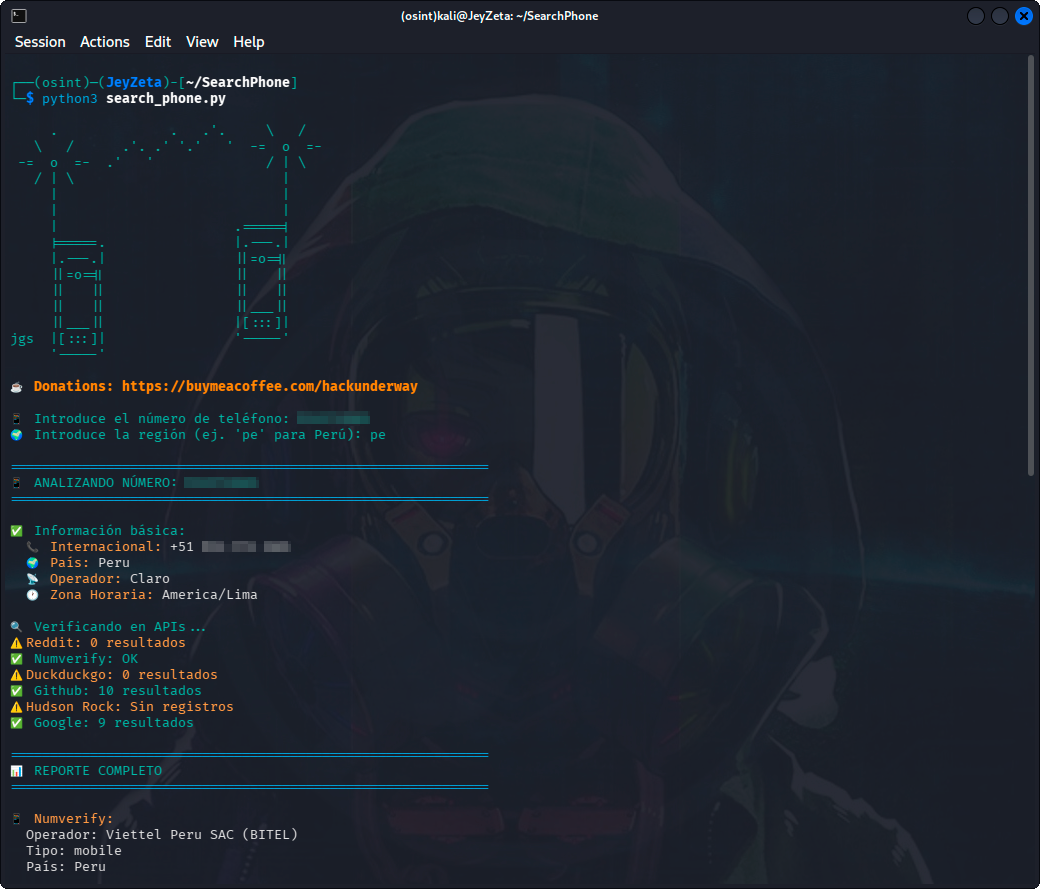 hackunderway/searchphone
Phone number OSINT toolkit with multi-API search (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock infostealer intelligence, and automatic…
 reprise99/sentinel-queries
Collection of KQL queries