
log4j-honeypot-flask
 binarydefense/log4j-honeypot-flask
Internal network honeypot for detecting if an attacker or insider threat scans your network for log4j CVE-2021-44228
defensive-toolsintrusion-detectionnetwork-security+2
binarydefense/log4j-honeypot-flaskInternal network honeypot for detecting if an attacker or insider threat scans your network for log4j CVE-2021-44228
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
 mnemonic-no/grafeo
Open platform for modelling, collection and exchange of knowledge
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 jeet-ganguly/birdy-edwards
Automated AI powered Facebook intelligence tool for target profiling, network analysis and threat reporting. Runs entirely on-device via Ollama.…
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
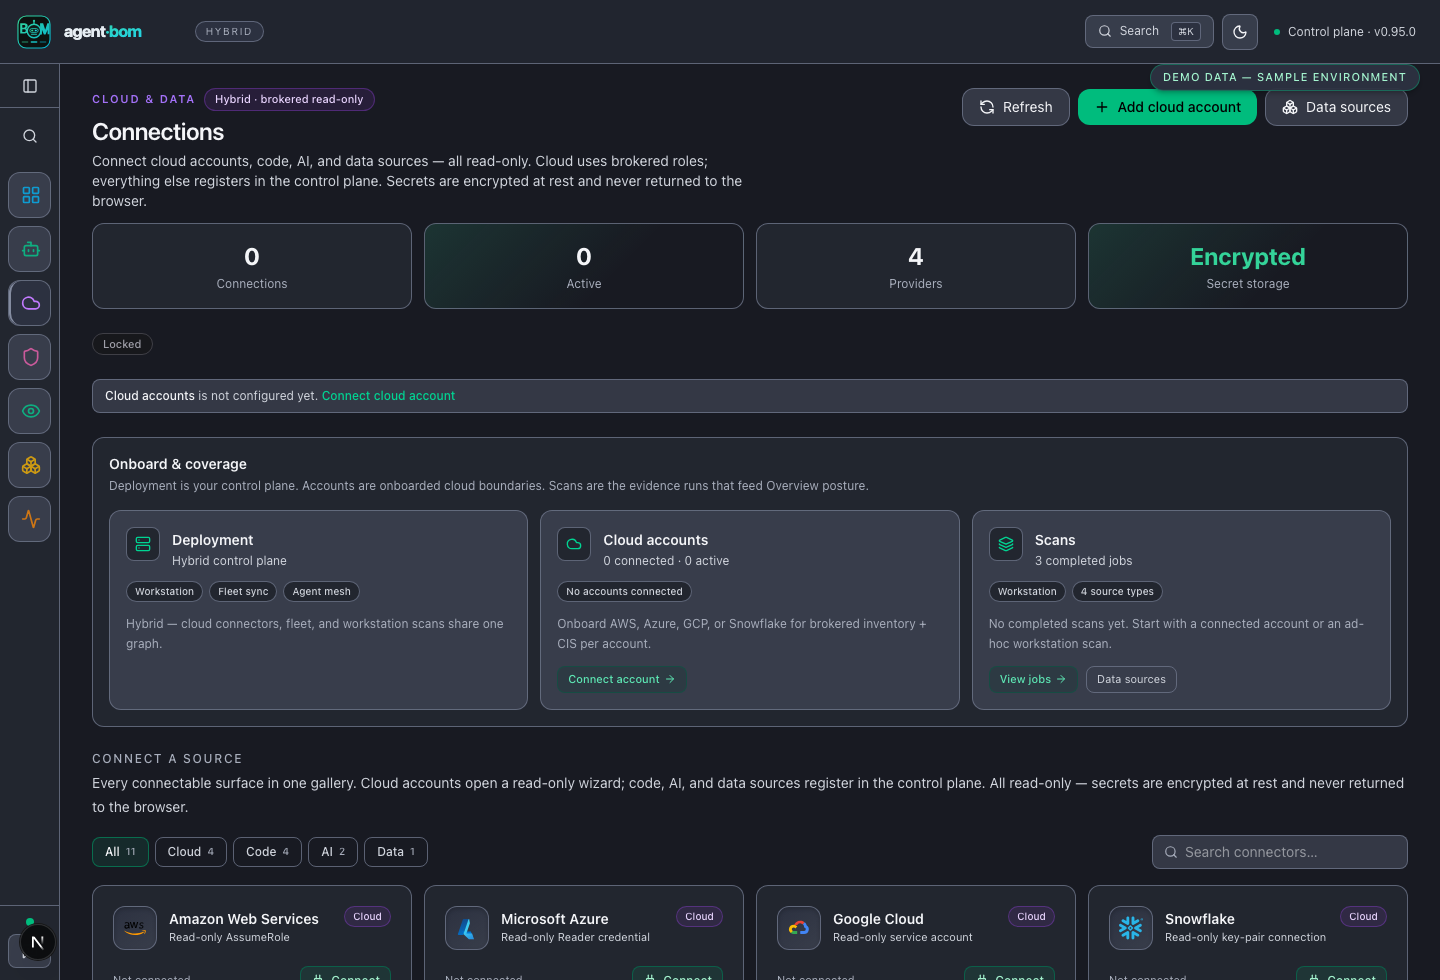 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 kube-tarian/tarian
eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 owasp/odtm
OWASP Ontology-driven Threat Modelling framework