

tenzir
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
incident-responselog-analysisnetwork-security+1
762
tenzir/tenzirCollect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
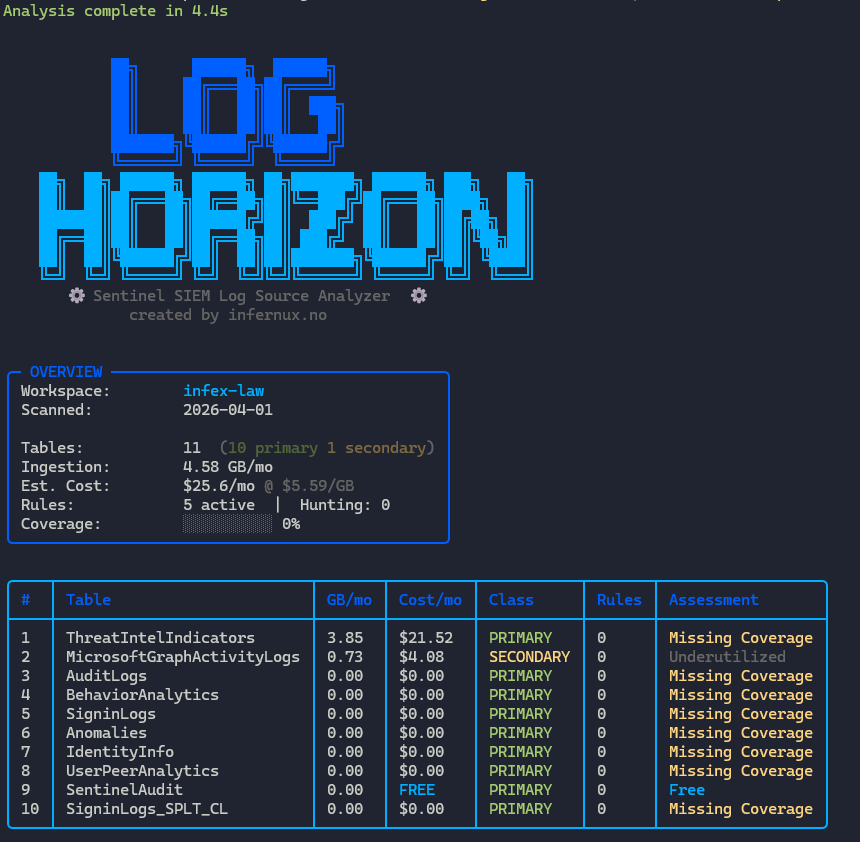 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

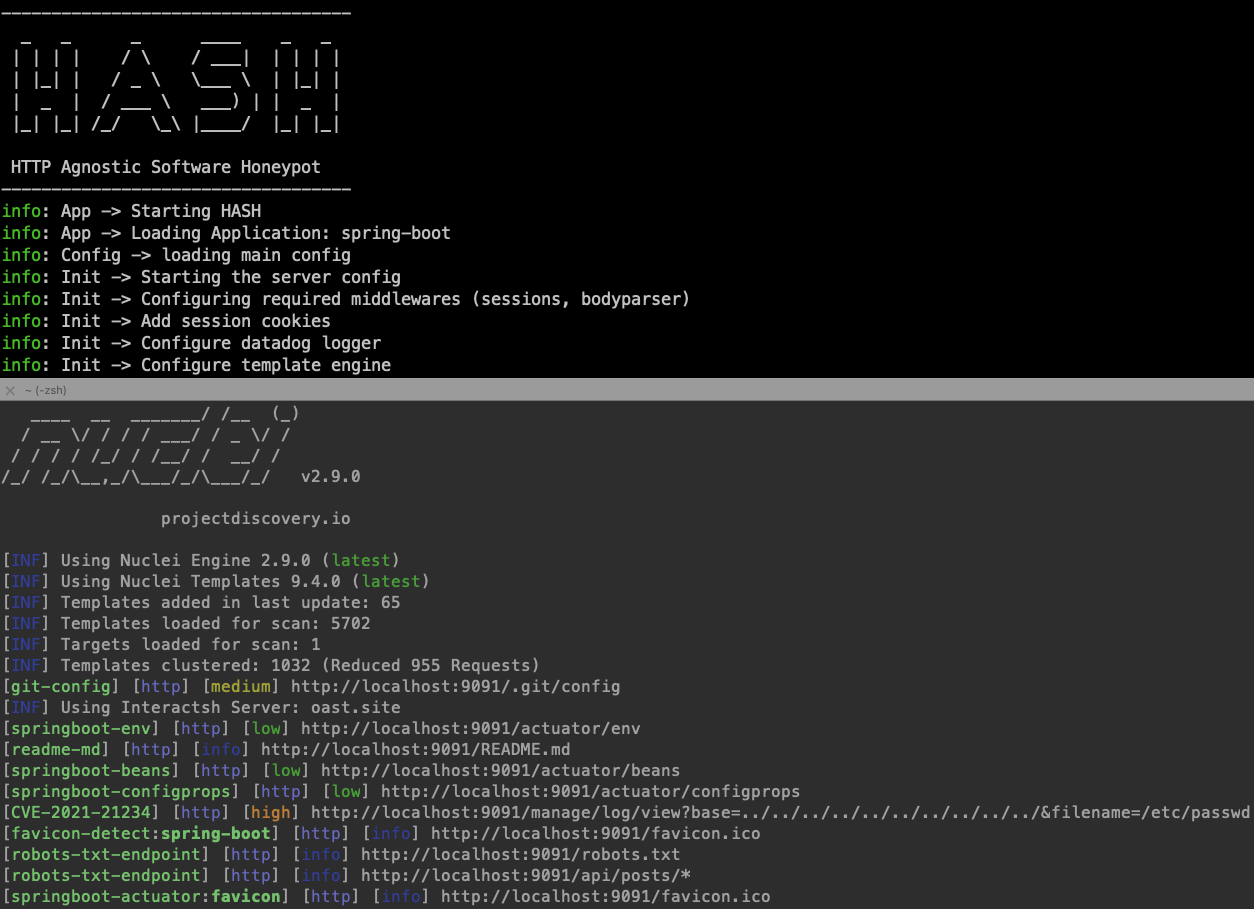 datadog/hash
YAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 corelight/ecs-mapping
Mapping Corelight or Zeek data to Elastic Common Schema fields
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
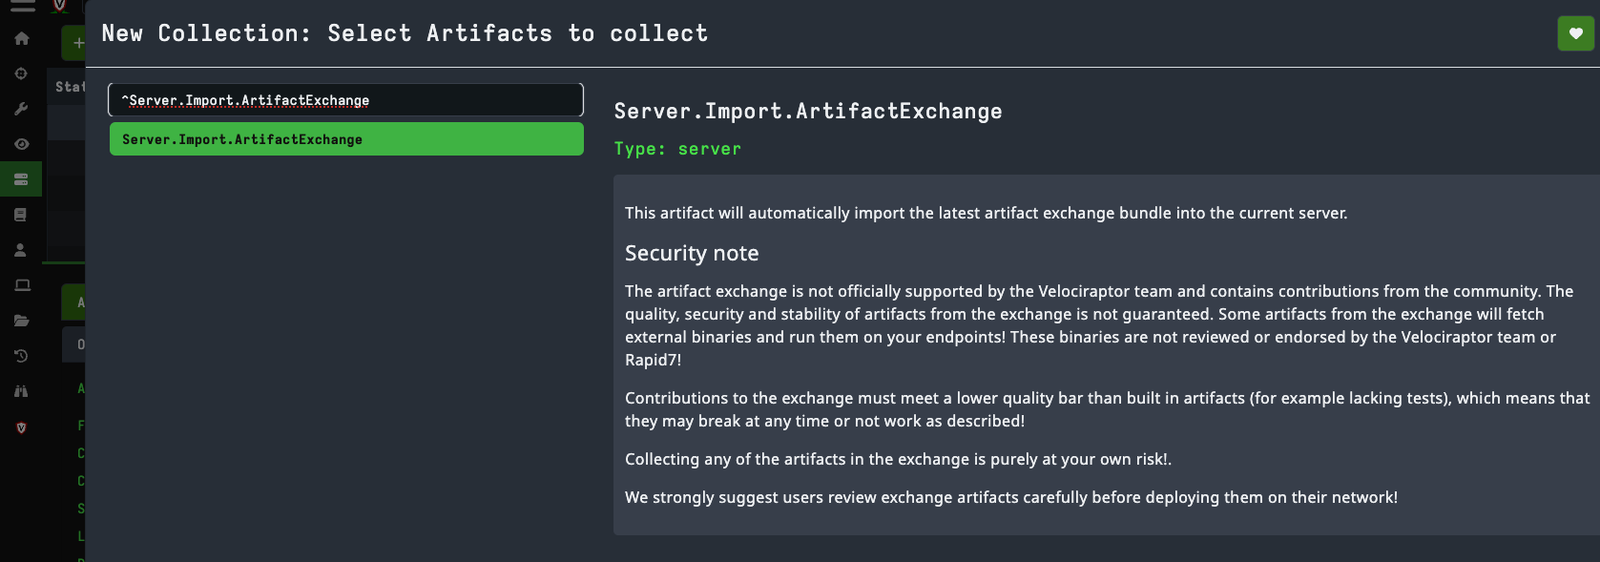 mgreen27/detectraptor
A repository to share publicly available Velociraptor detection content
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
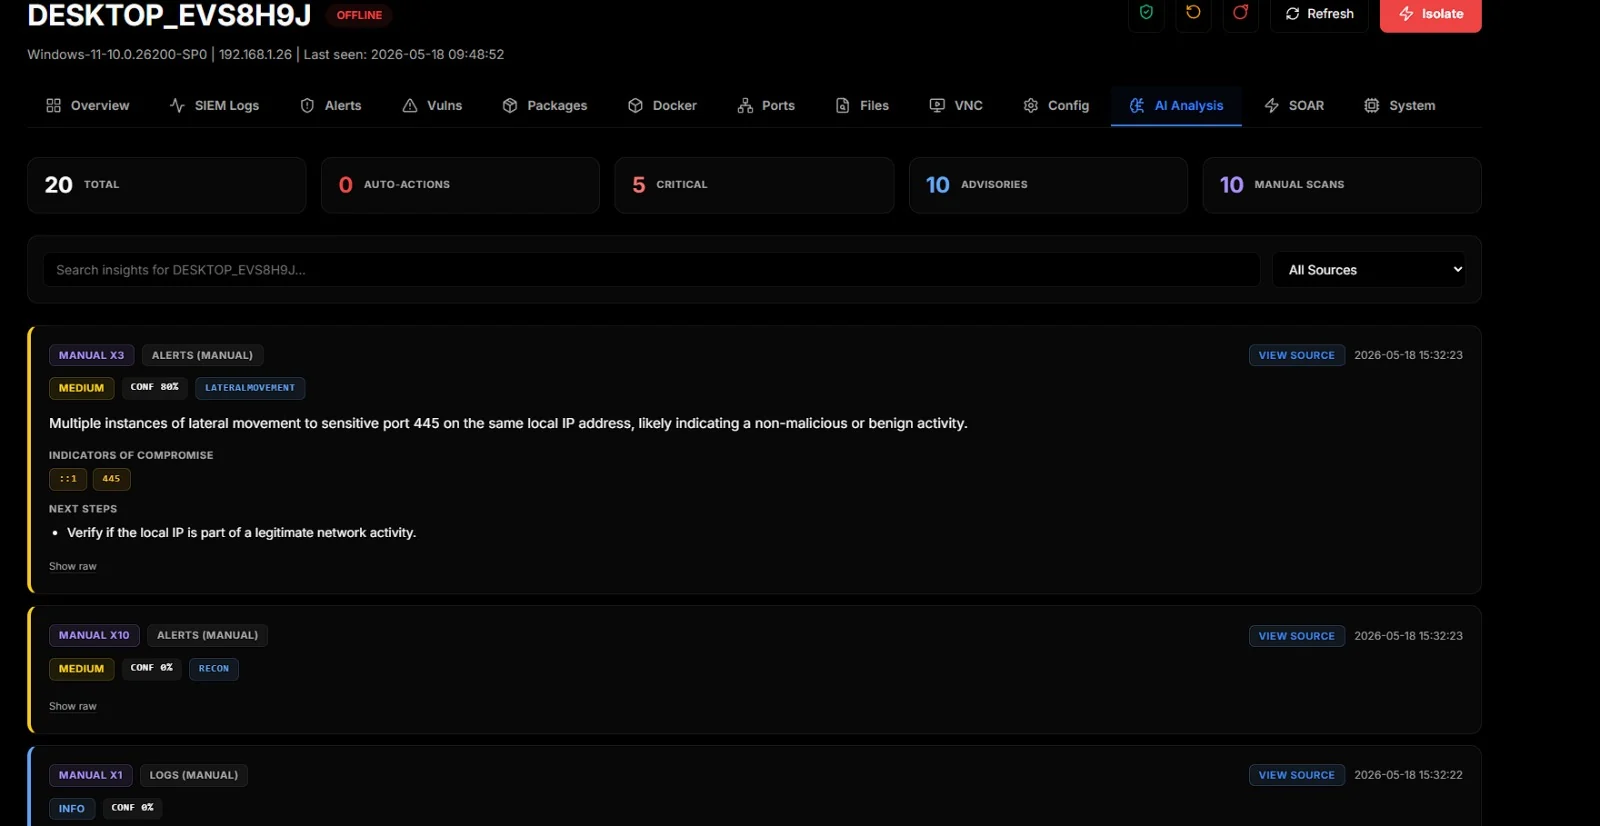 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.