maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
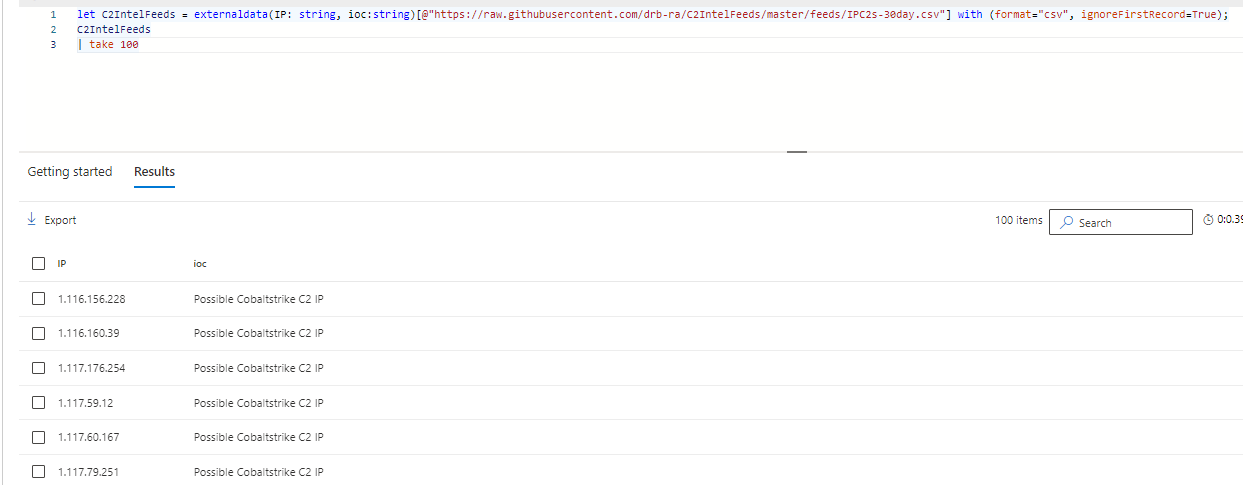 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
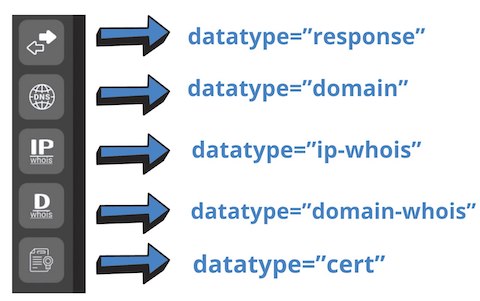 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 t-beckett/h-osint
Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 awesom3alex/osint-menace
Passive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
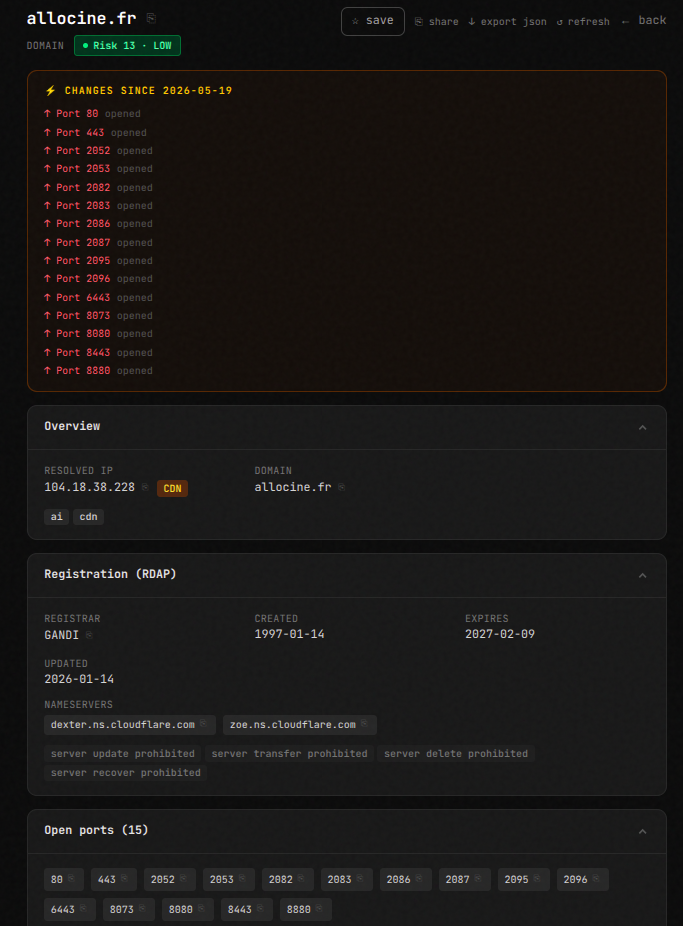 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
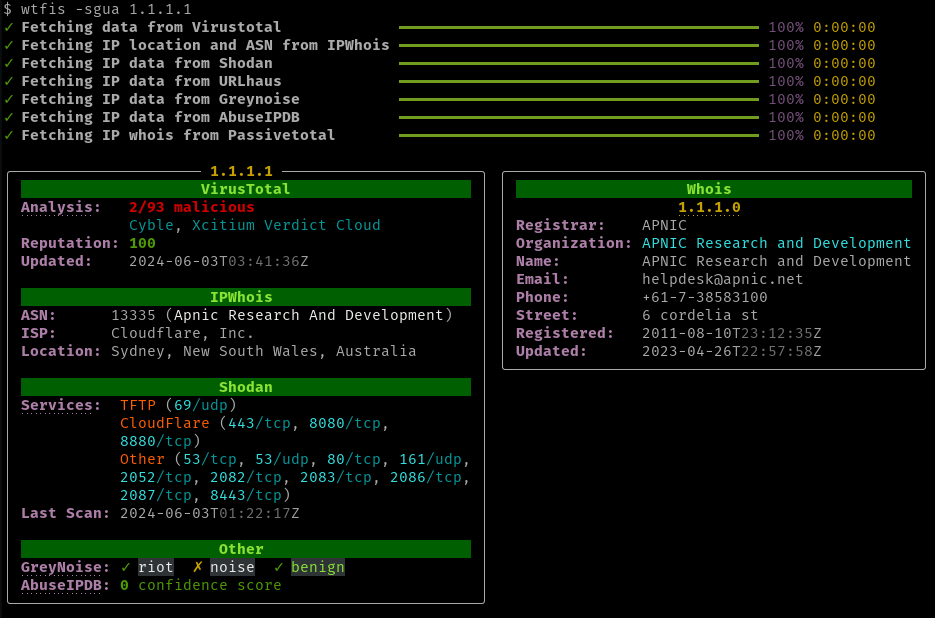 pirxthepilot/wtfis
Passive hostname, domain and IP lookup tool for non-robots
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
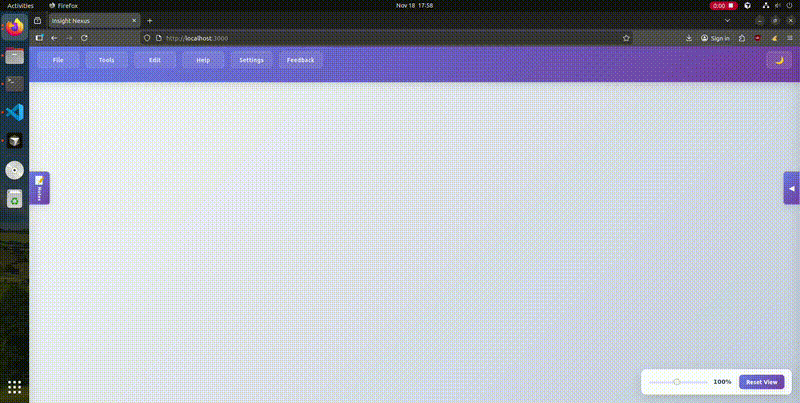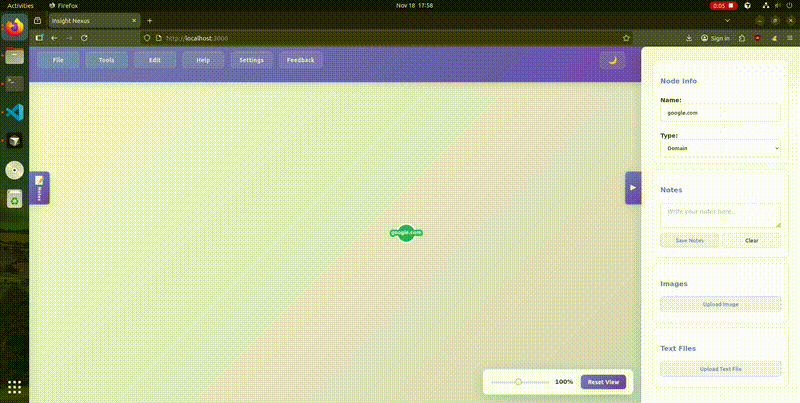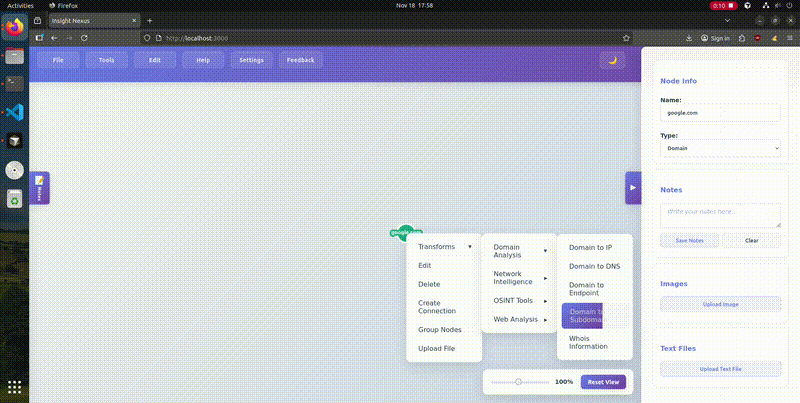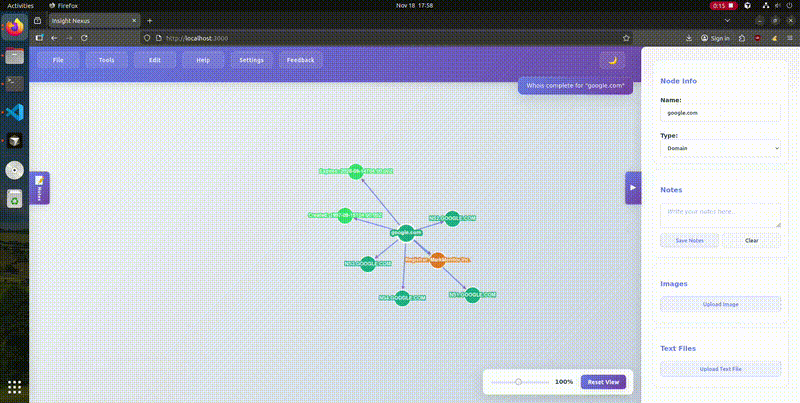 cyberintel-labs/insightsnexus
OSINT Graph Investigation Application
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 mouna23/osint-with-llm
It’s an OSINT reconnaissance poc powered by Local LLMs (Ollama). You can feed it an email, domain, or IP, and it automatically performs multiple…