Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
Weekly-Breach-Investigation--006 preview

Weekly-Breach-Investigation--006

GitHubjamal-soc21/weekly-breach-investigation--006

Repository documenting the Copy Fail (CVE-2026-31431) Linux kernel vulnerability, a local privilege escalation flaw enabling root access and mapped…

curated-resourceseducationexploitation+3

1
4 months ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.4k2 months ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
121 month ago
memOptix preview

memOptix

GitHubblueteam0ps/memoptix

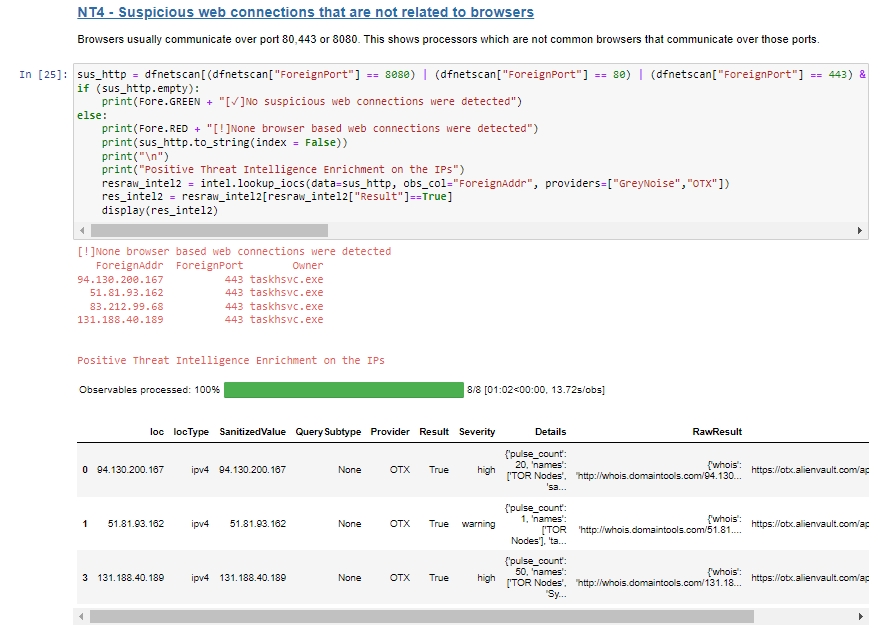
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.

digital-forensicsforensicsincident-response+2
983 years ago
Reports preview

Reports

GitHubj4ck3lsyn-gen2/reports

Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…

binary-exploitationcurated-resourcesexploitation+8
22 months ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

anomaly-detectiondigital-forensicsincident-response+5
73727 days ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

binary-analysiscommand-and-controleducation+6
52 months ago
Cisco-IOS-Exploitation-JAGUAR_TOOTH-CVE-2017-6742-Reconstruction preview

Cisco-IOS-Exploitation-JAGUAR_TOOTH-CVE-2017-6742-Reconstruction

GitHubsastraadiwiguna-purpleeliteteaming/cisco-ios-exploitation-jaguar_tooth-cve-2017-6742-reconstruction

Comprehensive 100% Unrestricted Technical Analysis of JAGUAR_TOOTH Malware (APT28). High-precision reconstruction of Cisco IOS SNMP exploitation, ROP…

binary-exploitationeducationexploitation+7
8 months ago
letsdefend-cve-2024-49138-investigation preview

letsdefend-cve-2024-49138-investigation

GitHubcyprianatsyor/letsdefend-cve-2024-49138-investigation

Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.

binary-exploitationdigital-forensicseducation+7
1 year ago
Kernel-Chaos-Weaponizing-CVE-2025-62215-for-SYSTEM-Privilege-Escalation preview

Kernel-Chaos-Weaponizing-CVE-2025-62215-for-SYSTEM-Privilege-Escalation

GitHubmrk336/kernel-chaos-weaponizing-cve-2025-62215-for-system-privilege-escalation

Hands‑on analysis of CVE‑2025‑62215, a Windows Kernel race condition exploited in the wild. Demonstrates privilege escalation to SYSTEM, detection…

binary-exploitationeducationexploitation+4
310 months ago
CVE-2023-38831 preview

CVE-2023-38831

GitHubmishra0230/cve-2023-38831

CVE-2023-38831 - WinRAR

binary-exploitationeducationexploitation+8
8 months ago
DIRTY-FRAG-Detection-with-Wazuh-4.14.4 preview

DIRTY-FRAG-Detection-with-Wazuh-4.14.4

GitHubmym0us3r/dirty-frag-detection-with-wazuh-4.14.4

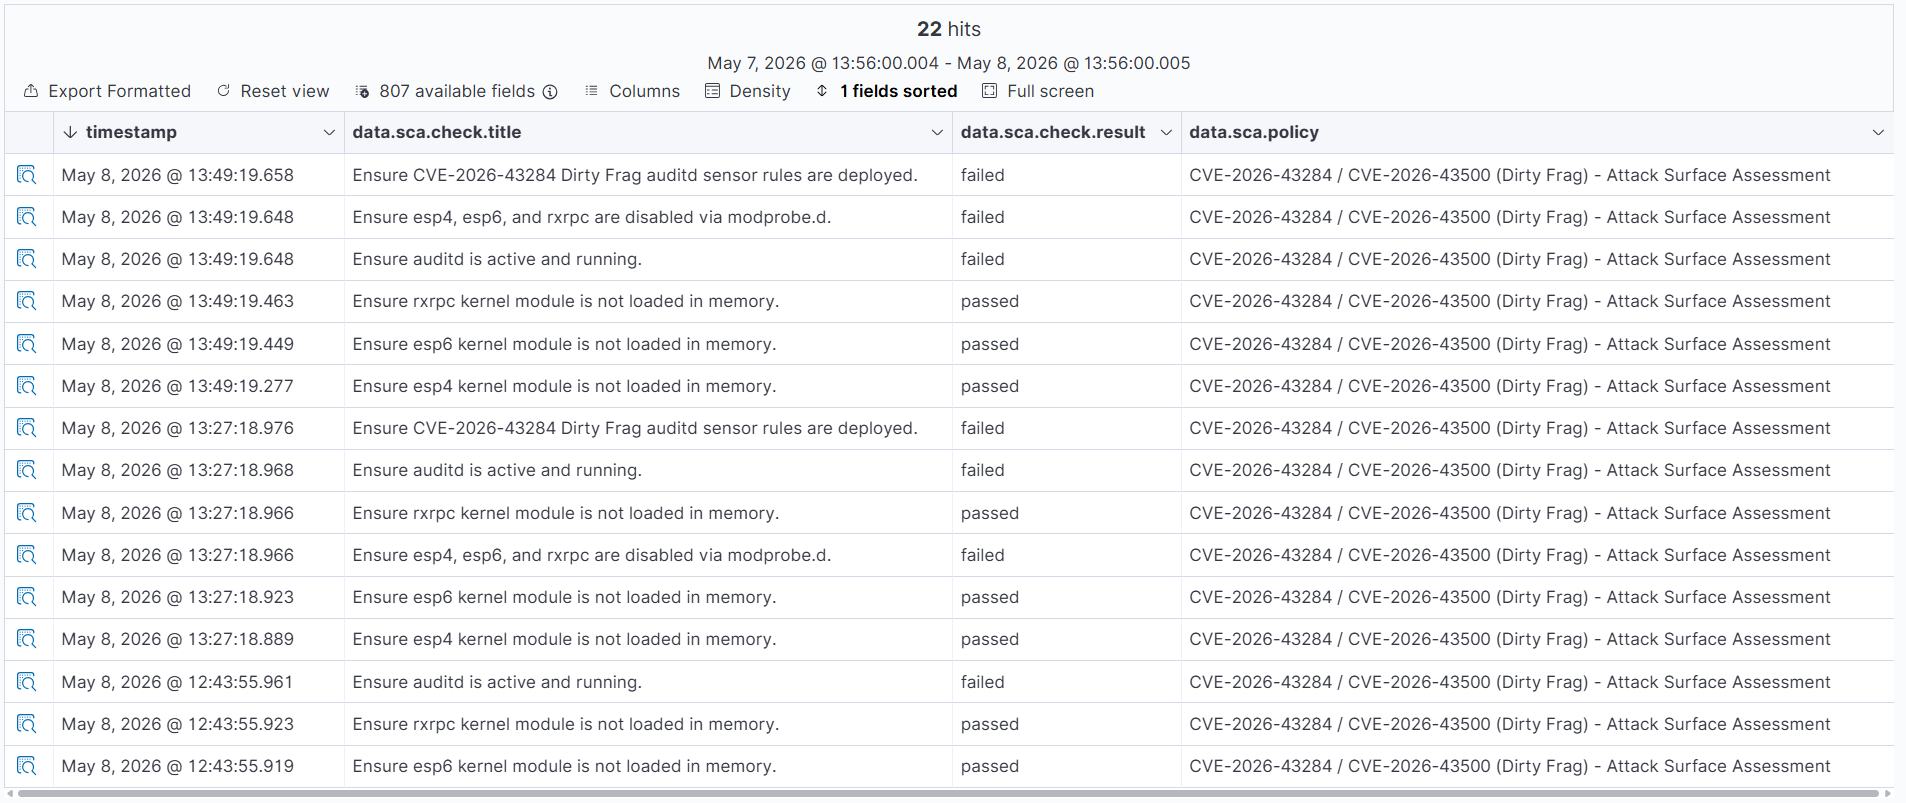
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write

binary-exploitationeducationexploitation+6
34 months ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

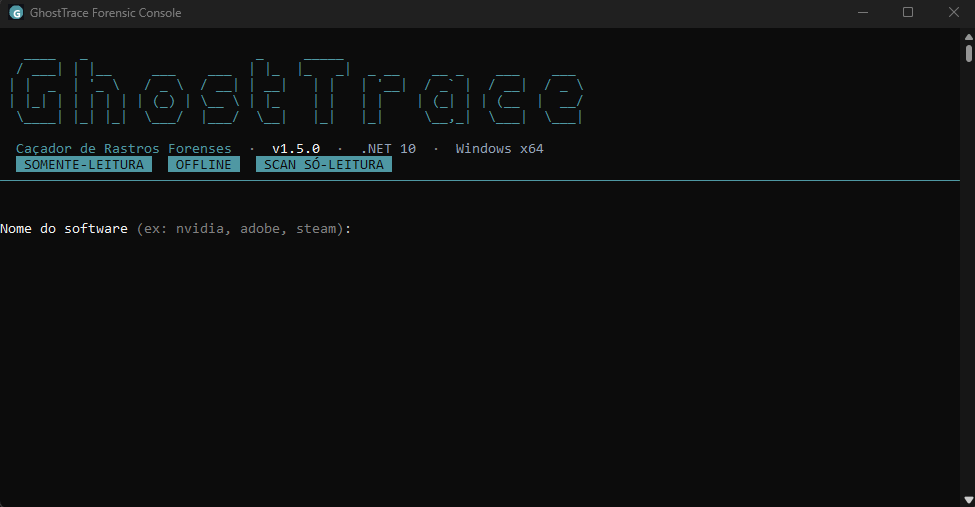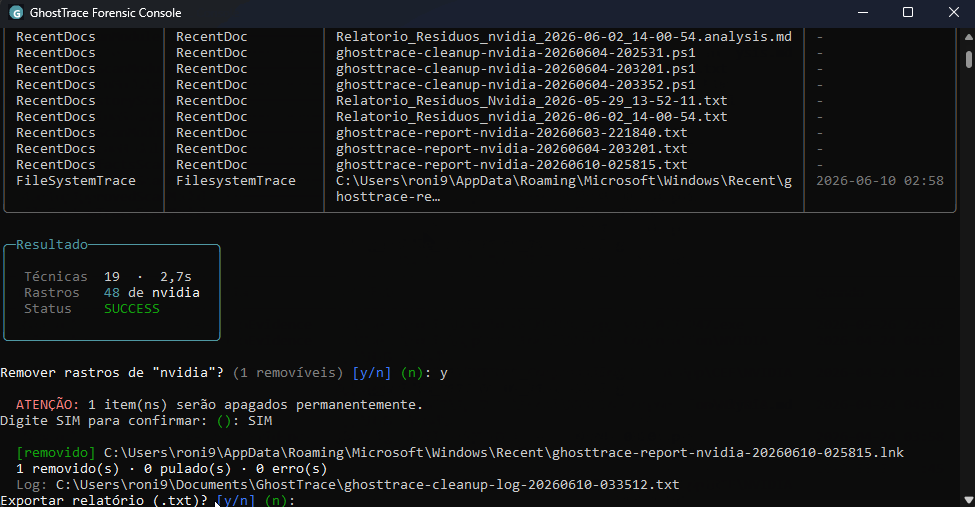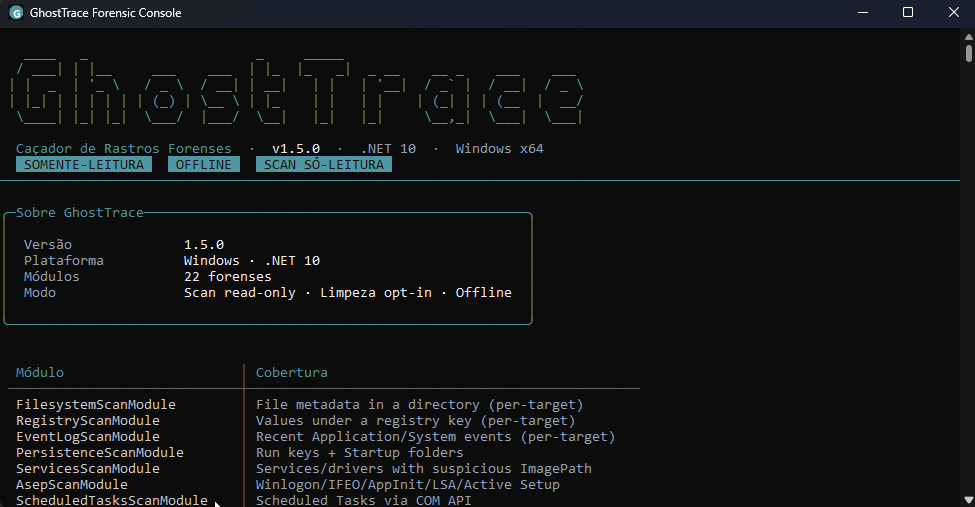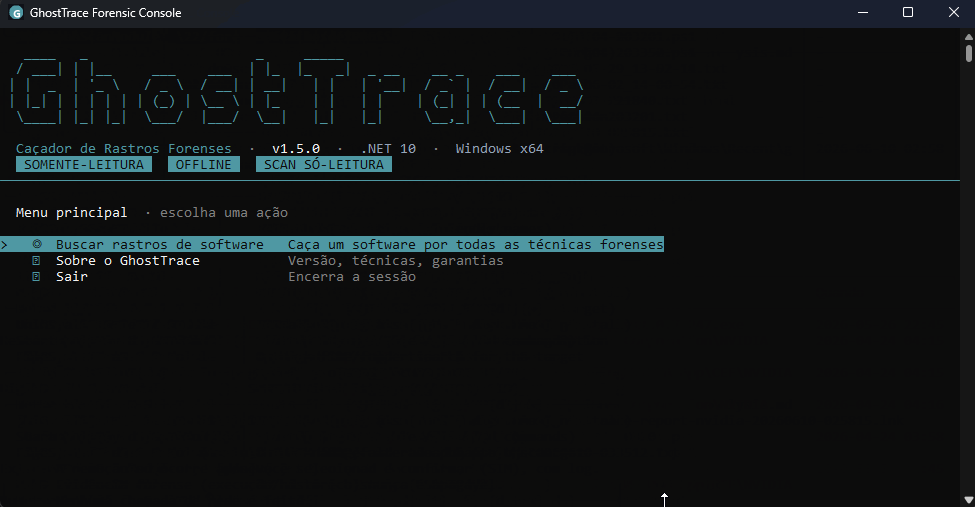
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

digital-forensicsforensicsincident-response+3
2 months ago
Fragnesia-CVE-2026-46300 preview

Fragnesia-CVE-2026-46300

GitHubmaxime288/fragnesia-cve-2026-46300

Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…

binary-exploitationcurated-resourceseducation+5
4 months ago
ghost preview

ghost

GitHubpandaadir05/ghost

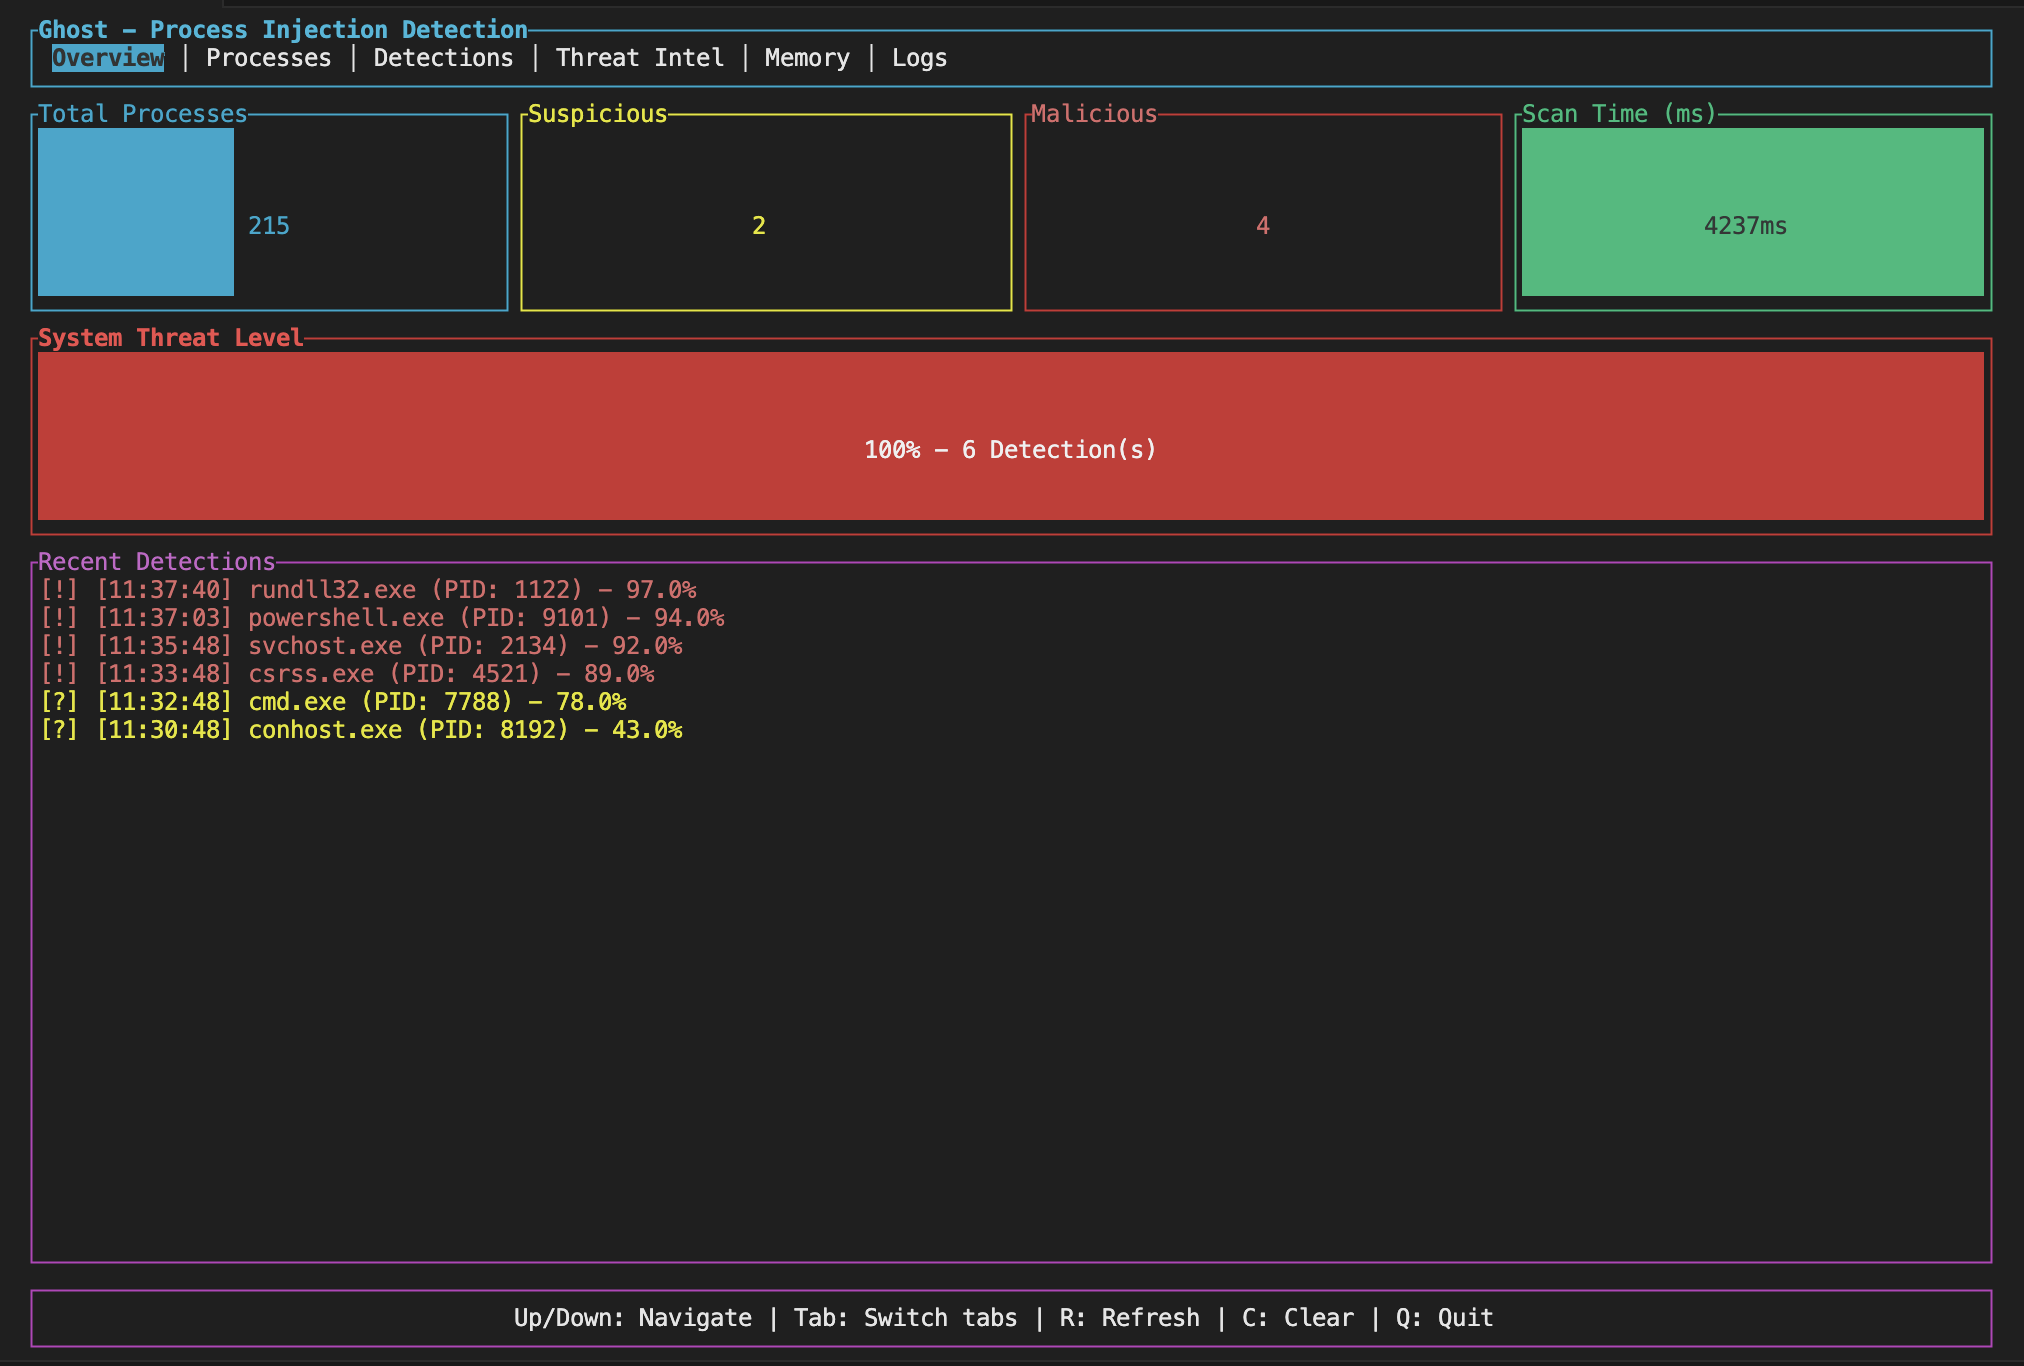
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

binary-analysisdefensive-toolsforensics+6
3911 month ago
CVE-2017-4878-Samples preview

CVE-2017-4878-Samples

GitHubbrianwrf/cve-2017-4878-samples

CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html

binary-exploitationexploitationmalware-analysis+3
178 years ago
CVE-2026-43284-dirtyfrag-detection preview

CVE-2026-43284-dirtyfrag-detection

GitHubg0thamrabb1t/cve-2026-43284-dirtyfrag-detection

Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…

binary-exploitationeducationforensics+7
3 months ago
openclaw-security-monitor preview

openclaw-security-monitor

GitHubadibirzu/openclaw-security-monitor

Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.

defensive-toolseducationforensics+9
488 days ago
Previous12Next