

quipu
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
code-analysisdefensive-toolsdigital-forensics+6
corelight/quipuA desktop workbench for writing, validating, compiling, and testing YARA rules.
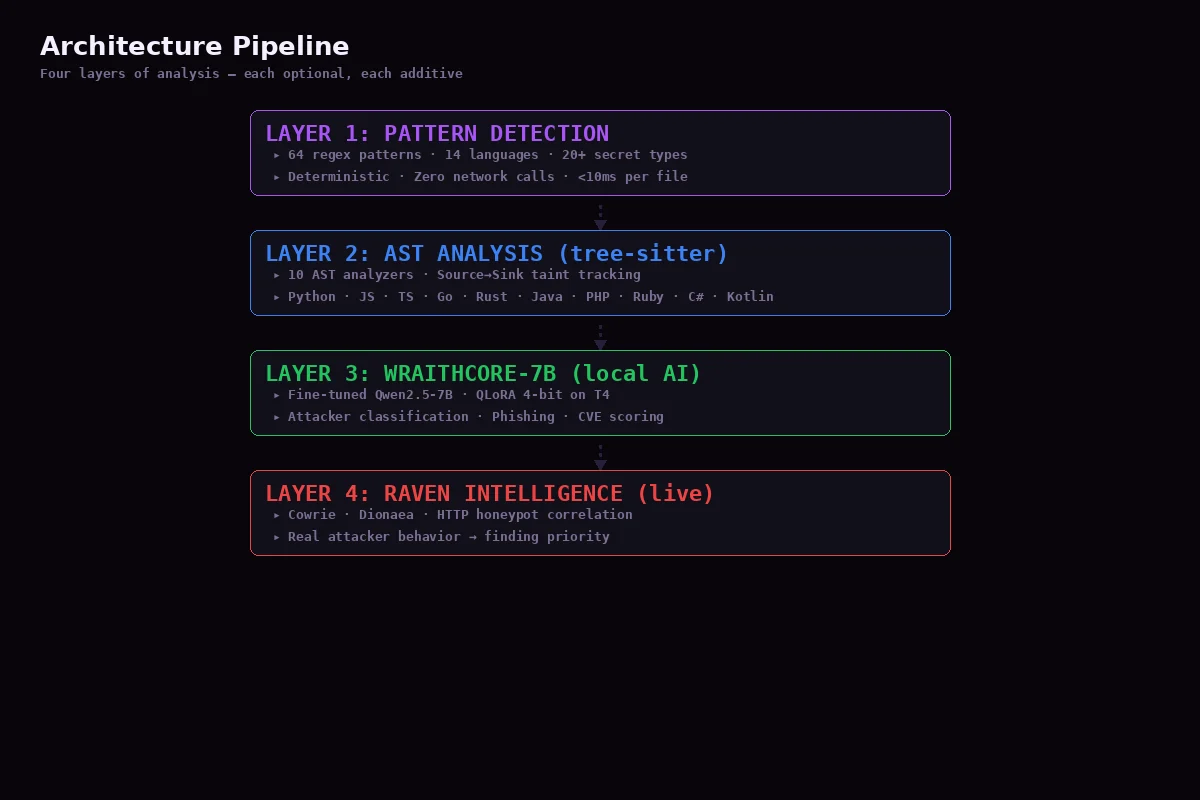 niffyhunt/codeguard-copilot
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 foxirain/linux-kernel-codex-harness-v2
Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
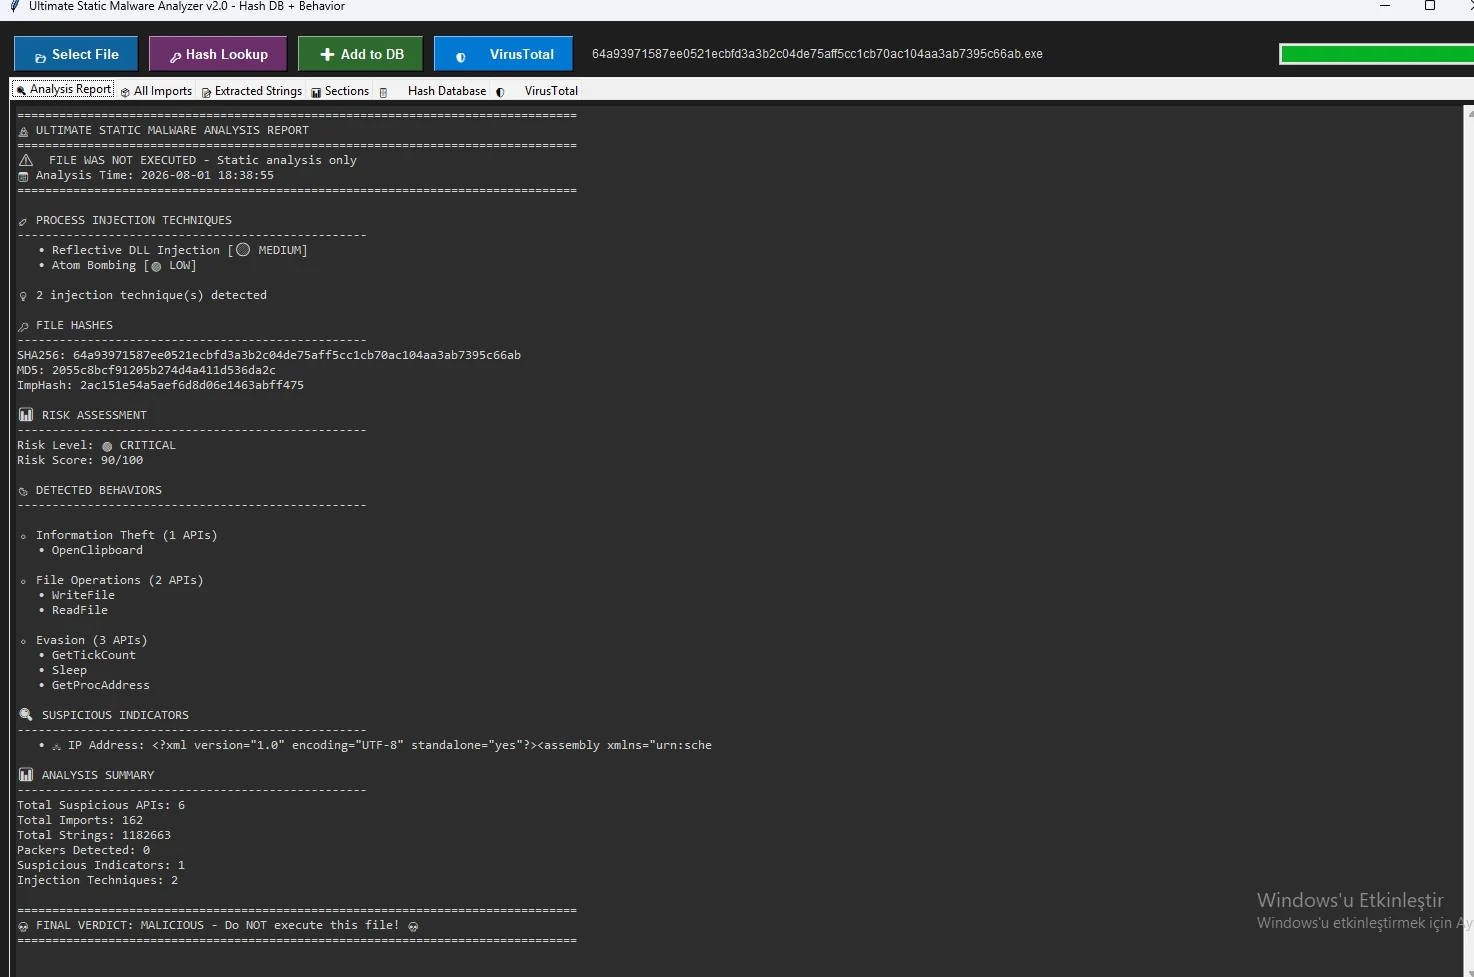 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 codextf2/cobaltstrike-sleepmask-yara
Just a git repo for the sleepmask detection rule i found in https://codex-7.gitbook.io/codexs-terminal-window/blue-team/detecting-cobalt-strike/sleep-…
 embee-research/asyncrat-venom-dcrat-config-extractor
Config Extractor for Asyncrat/Dcrat/VenomRat
 embee-research/icedid-file-decryptor
Static Decryptor for IcedID Malware
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 rmottanet/unauthscout
UnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)