
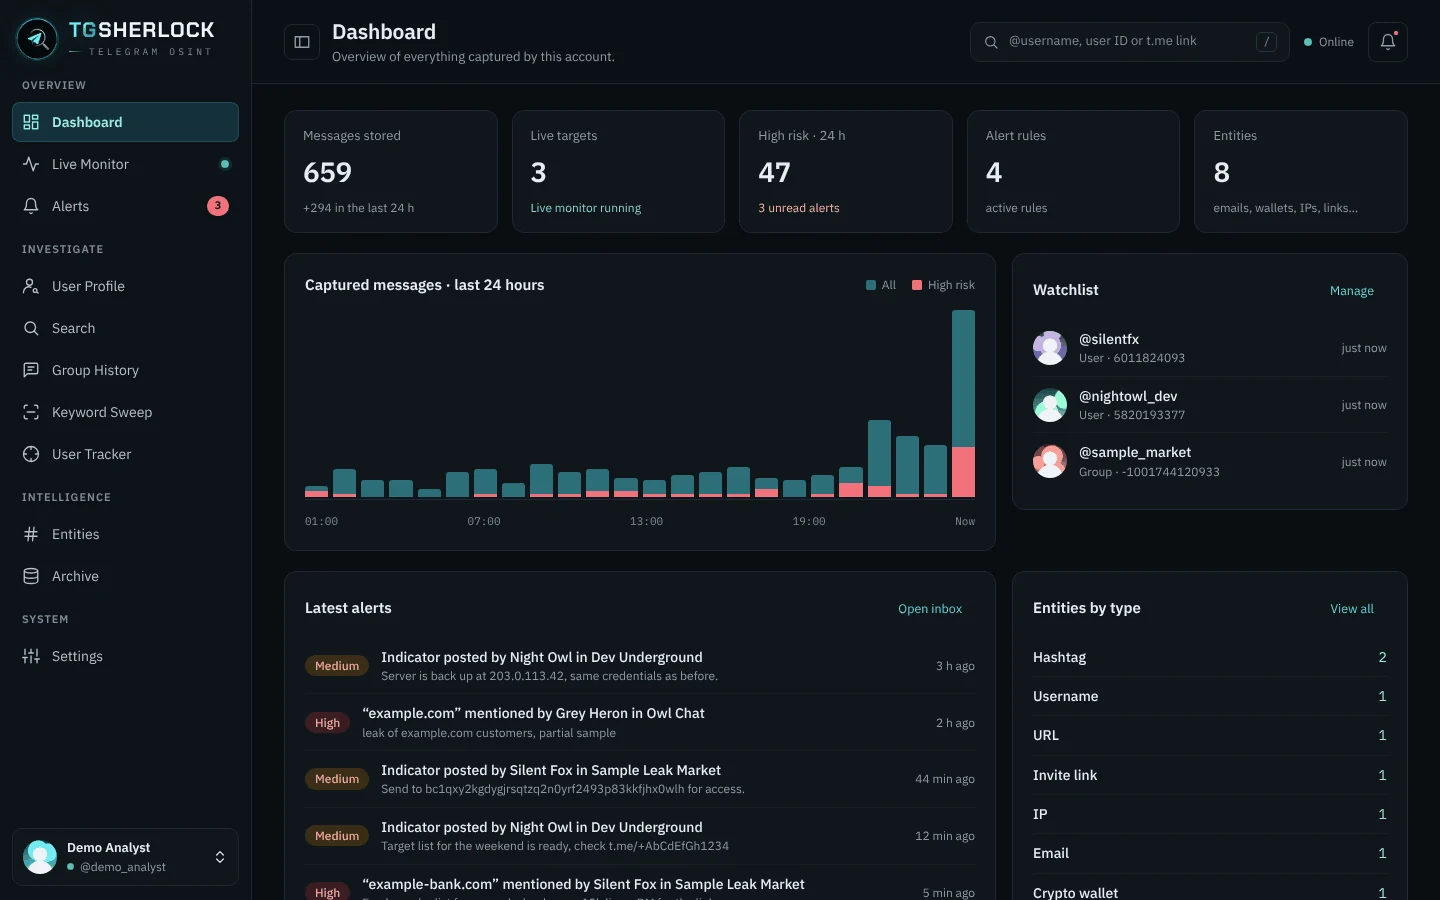
tgsherlock
 emrekybs/tgsherlock
Telegram OSINT tool for user, group and message investigation
data-exfiltrationinformation-gatheringlog-analysis+6
emrekybs/tgsherlockTelegram OSINT tool for user, group and message investigation
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 suominen/diagspill
Patch-status tracker for the Linux kernel SCTP sock_diag heap overflow (CVE-2026-74469), recording which distributions have shipped a fix.
 suominen/cve-2025-39964
Patch-status tracker for CVE-2025-39964, a Linux AF_ALG race condition enabling local privilege escalation, recording per-distribution fix…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 thrandomv/cve-2026-31431-detection
Defensive detection package for CVE-2026-31431 (Linux kernel AF_ALG LPE). Sigma, Falco, auditd, KQL, and EQL rules mapped to MITRE ATT&CK…
 offseq/threat-finder
Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 cisco-talos/deceive
DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
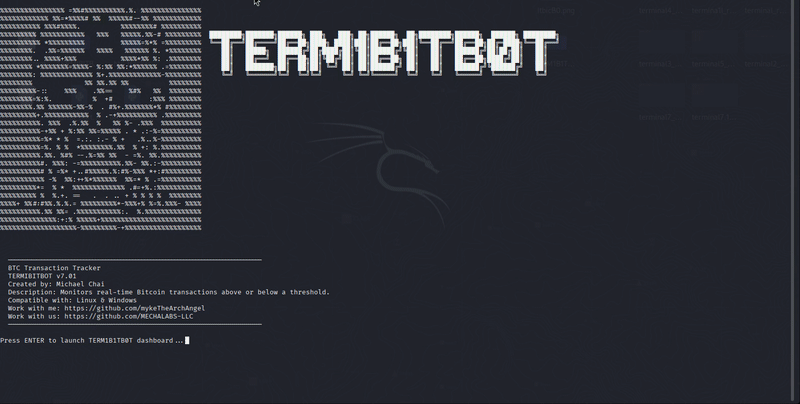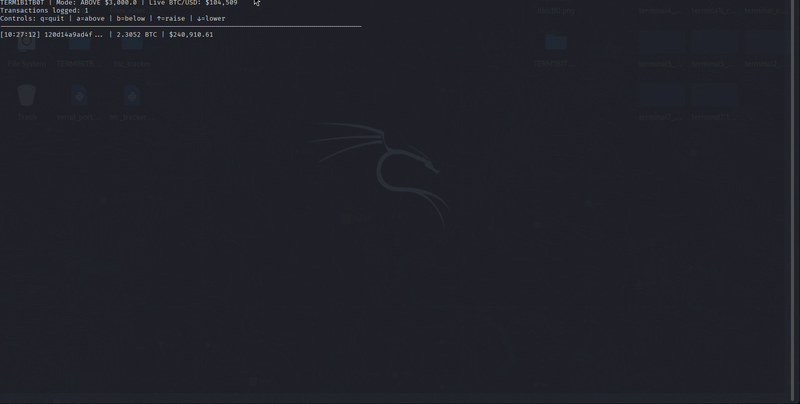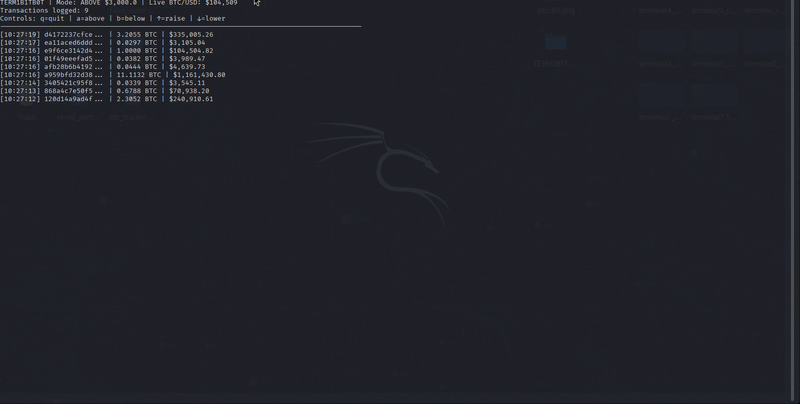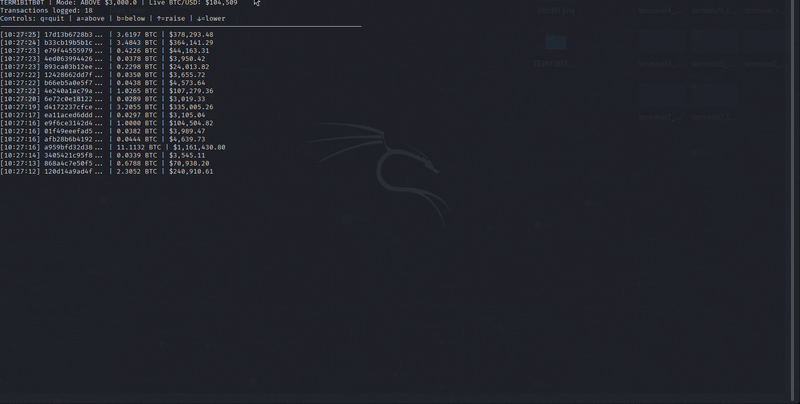 mykethearchangel/term1b1tb0t
A terminal based tool that monitors real-time Bitcoin transactions above or below a specified threshold.
 criann/check-cve-2026-23111
Script to check if system are vulnable to cve-2026-23111
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…