
chainsaw
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k
withsecureopensource/chainsawRapidly Search and Hunt through Windows Forensic Artefacts
 withsecurelabs/remotepspy
Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 zhoucc-cpu/cve-2023-23397-detection-lab
Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.
 neo23x0/raccine
A Simple Ransomware Vaccine
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 jonny-jhnson/msrpc-to-attack
A repository that maps commonly used attacks using MSRPC protocols to ATT&CK
 malwaremorghulis/sunburst
Detection for SUNBURST C2 Stage-1 using Shannon Entropy
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
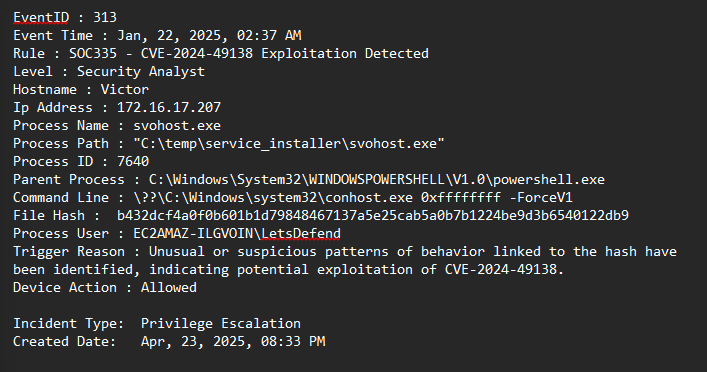 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
 navya240/intel471-threat-hunting-cve-2023-46604
My first hands-on Intel 471 threat hunting workshop experience investigating CVE-2023-46604 using Elastic SIEM, vulnerability intelligence, and…
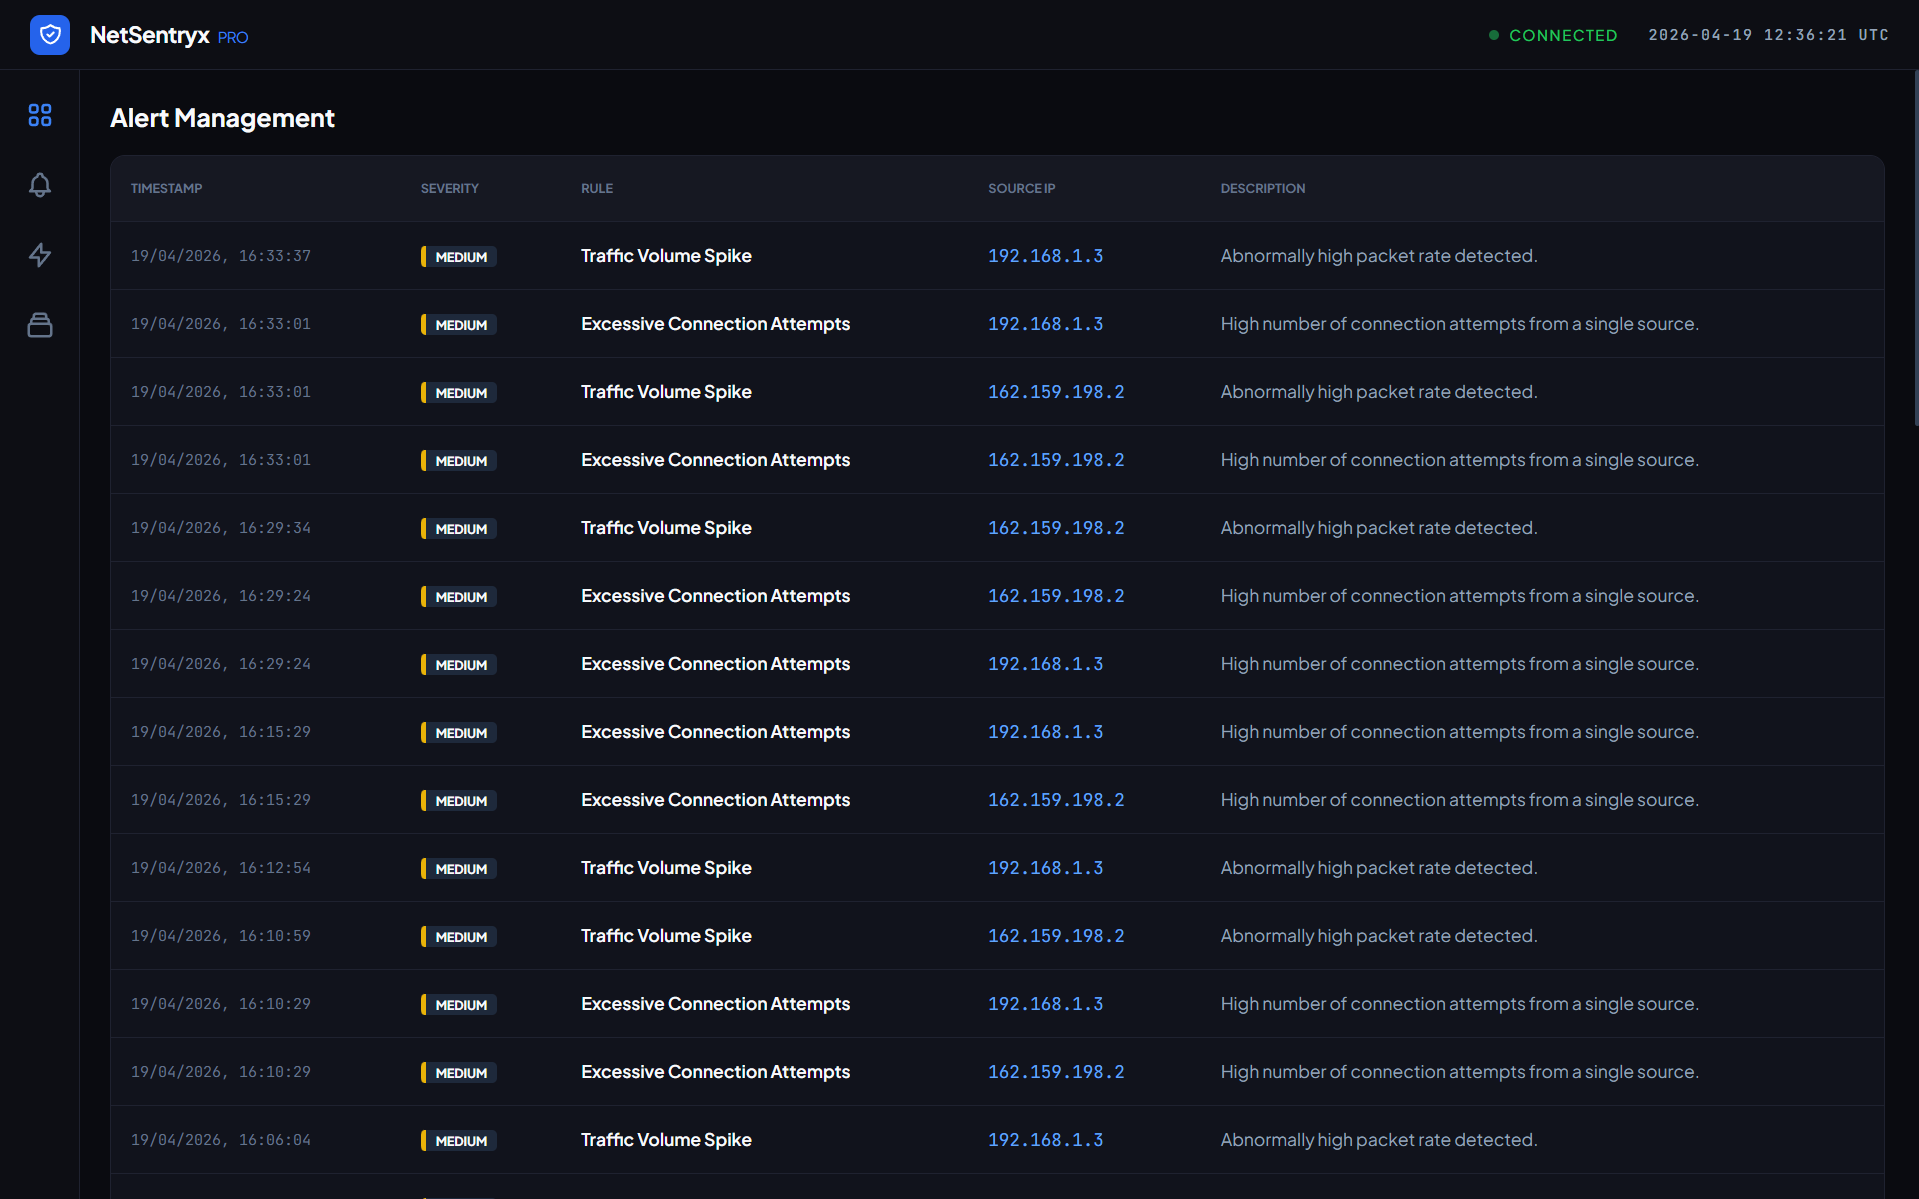 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
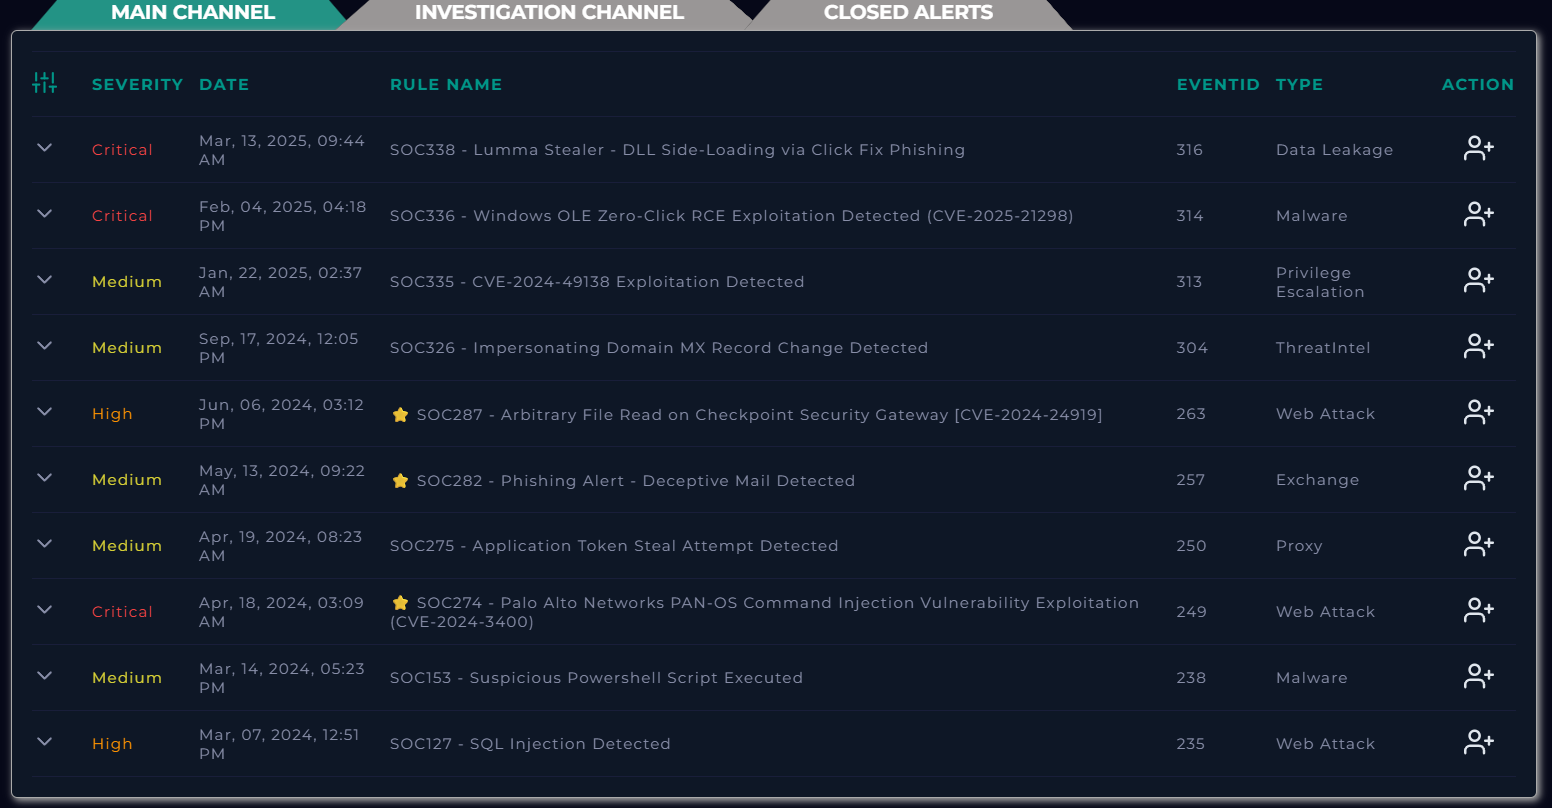 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 qjawls2003/blacklotus-detection
Public repo for anything CVE-2022-21894
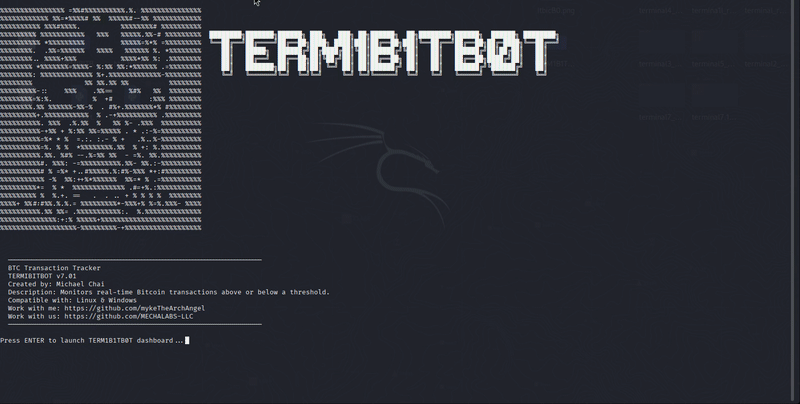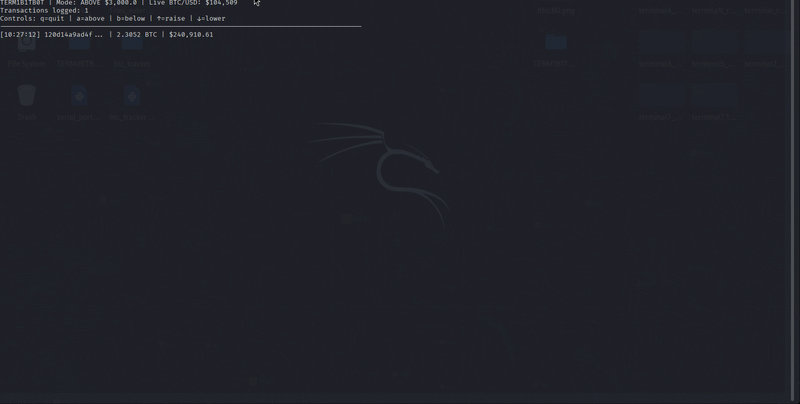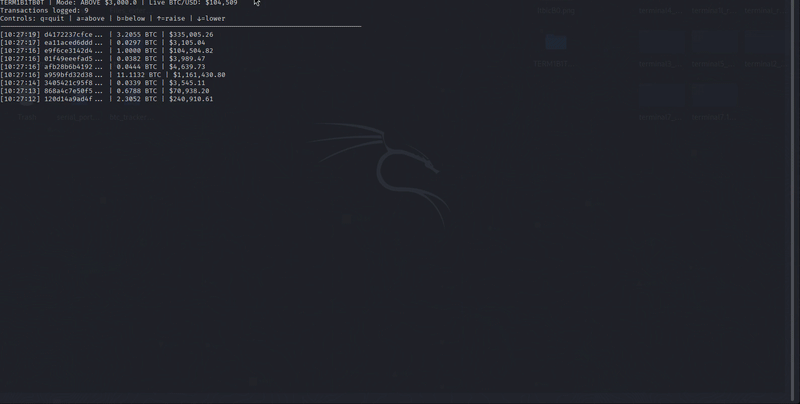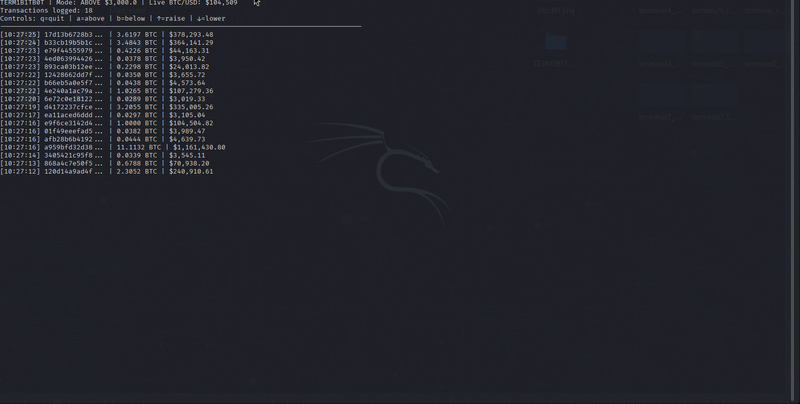 mykethearchangel/term1b1tb0t
A terminal based tool that monitors real-time Bitcoin transactions above or below a specified threshold.
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 iiamit/cyberqrm
An implementation of the FAIR CRQ Framework