

EntraTrace
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
authenticationcloud-securitydefensive-tools+5
54
bert-janp/entratraceDefensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 unkl4b/gitminer3
Tool for advanced mining for content on Github
 sw33ber/nuclei-cve-analyzer
CVE intelligence pipeline that compares public CVEs against Nuclei templates to identify missing vulnerability coverage, classify types, and rank…
 withsecurelabs/remotepspy
Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
 jeet-ganguly/birdy-edwards
Automated AI powered Facebook intelligence tool for target profiling, network analysis and threat reporting. Runs entirely on-device via Ollama.…
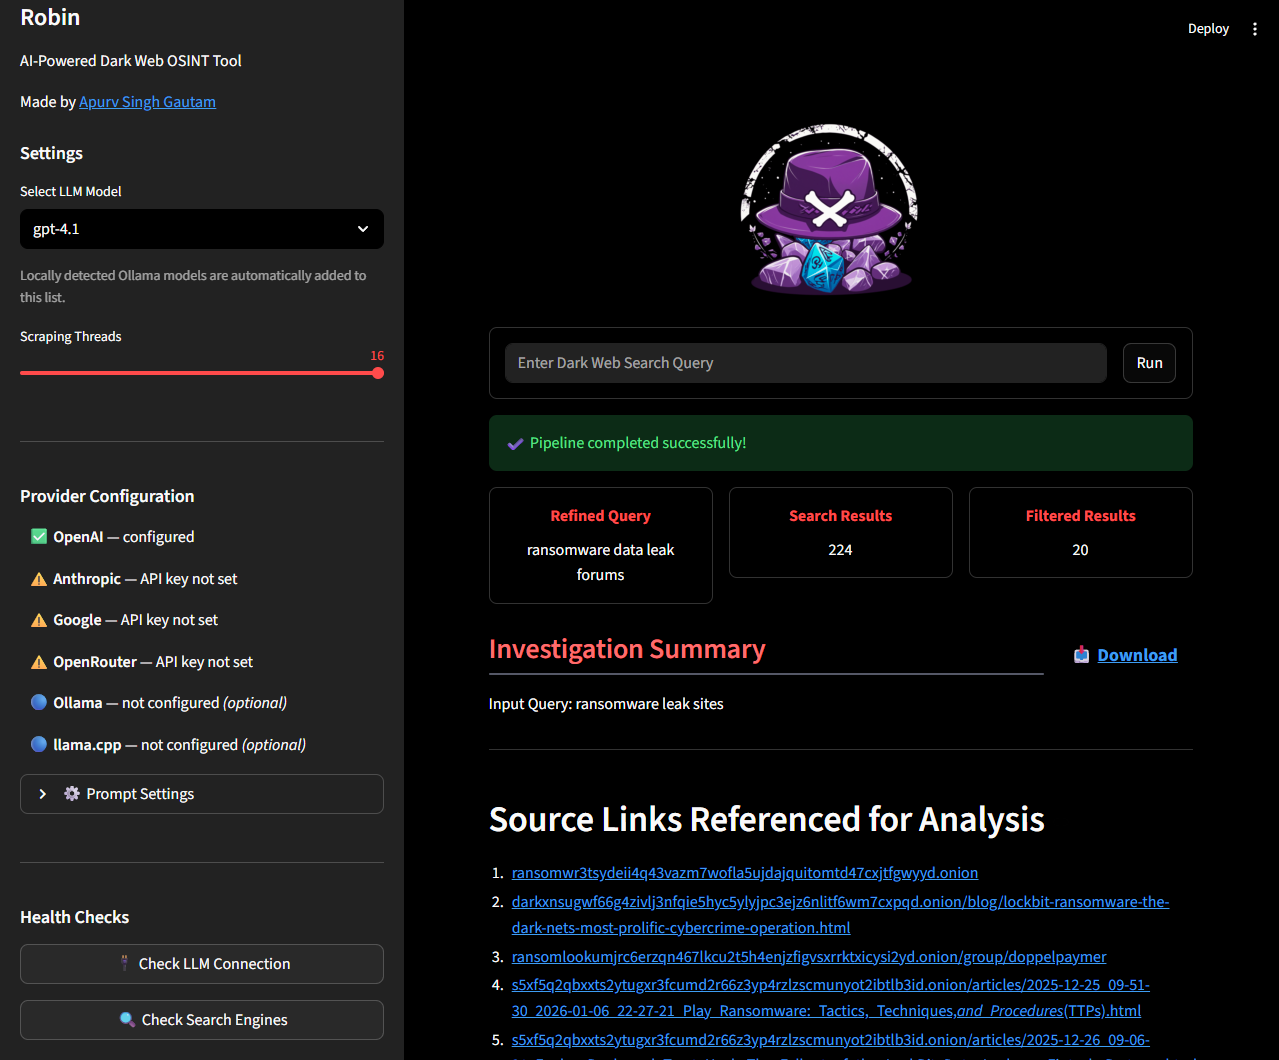 apurvsinghgautam/robin
AI-powered dark web OSINT tool that uses LLMs to refine queries, filter search results, and generate investigation summaries with a web UI and Docker…
 foxirain/linux-kernel-codex-harness-v2
Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075
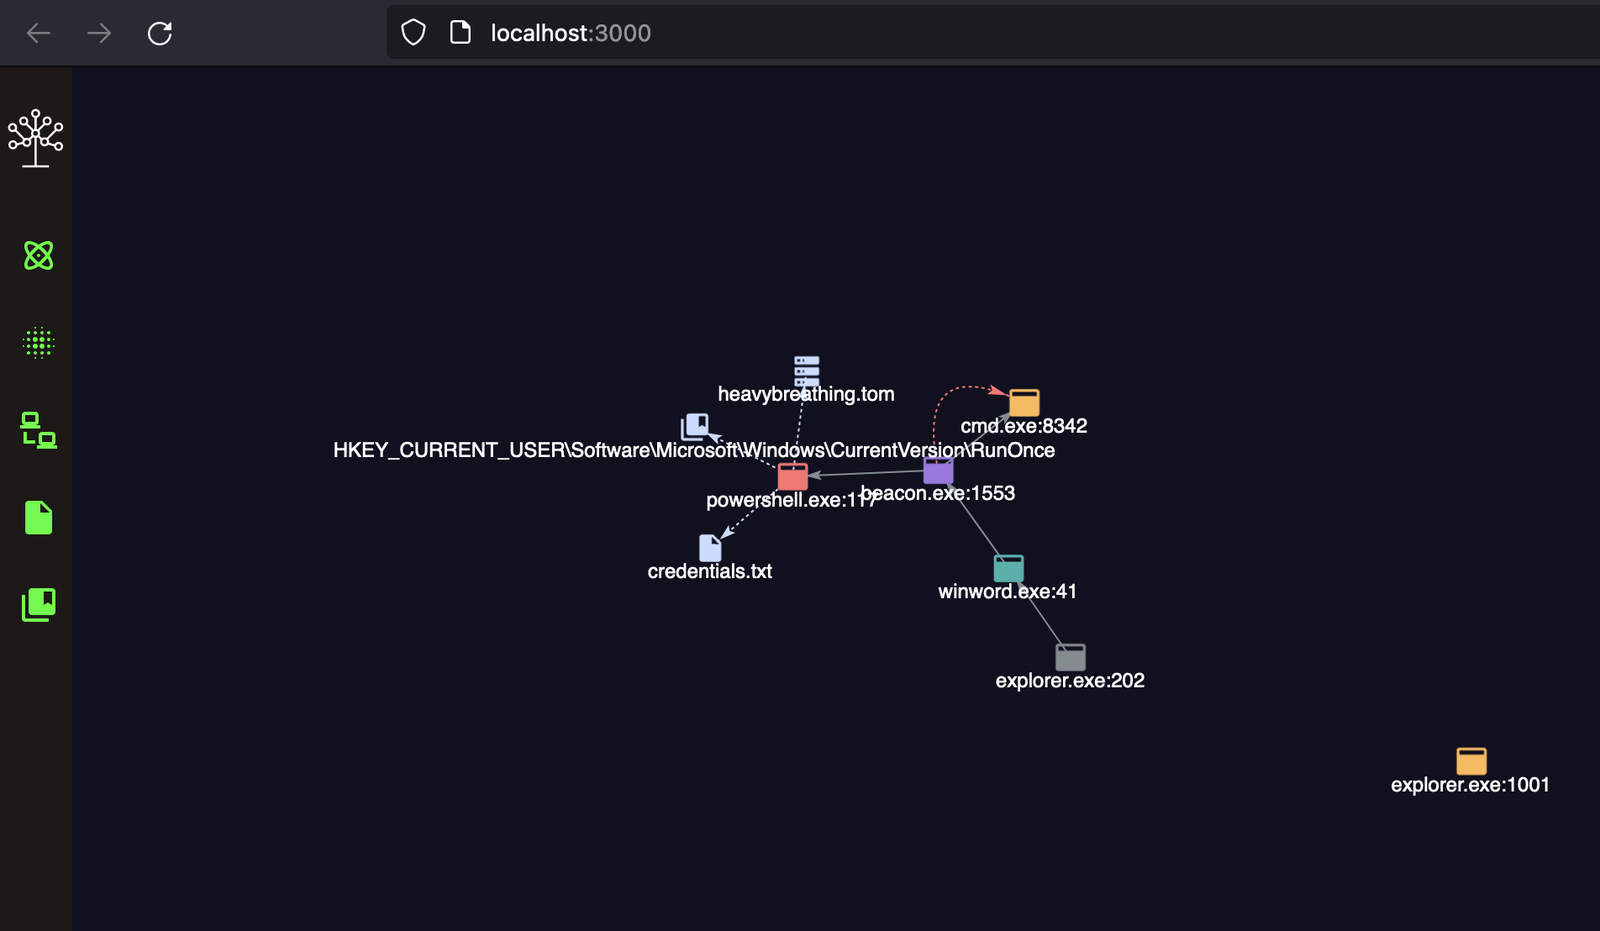 withsecurelabs/detectree
Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
 juanlunaia/aegis-latent-core
AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
 cyberdudebivash/cyberdudebivash-modular-ds-cve-2026-23550-detector
authorized CYBERDUDEBIVASH ECOSYSTEM tool for detecting CVE-2026-23550 in WordPress Modular DS plugin
 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
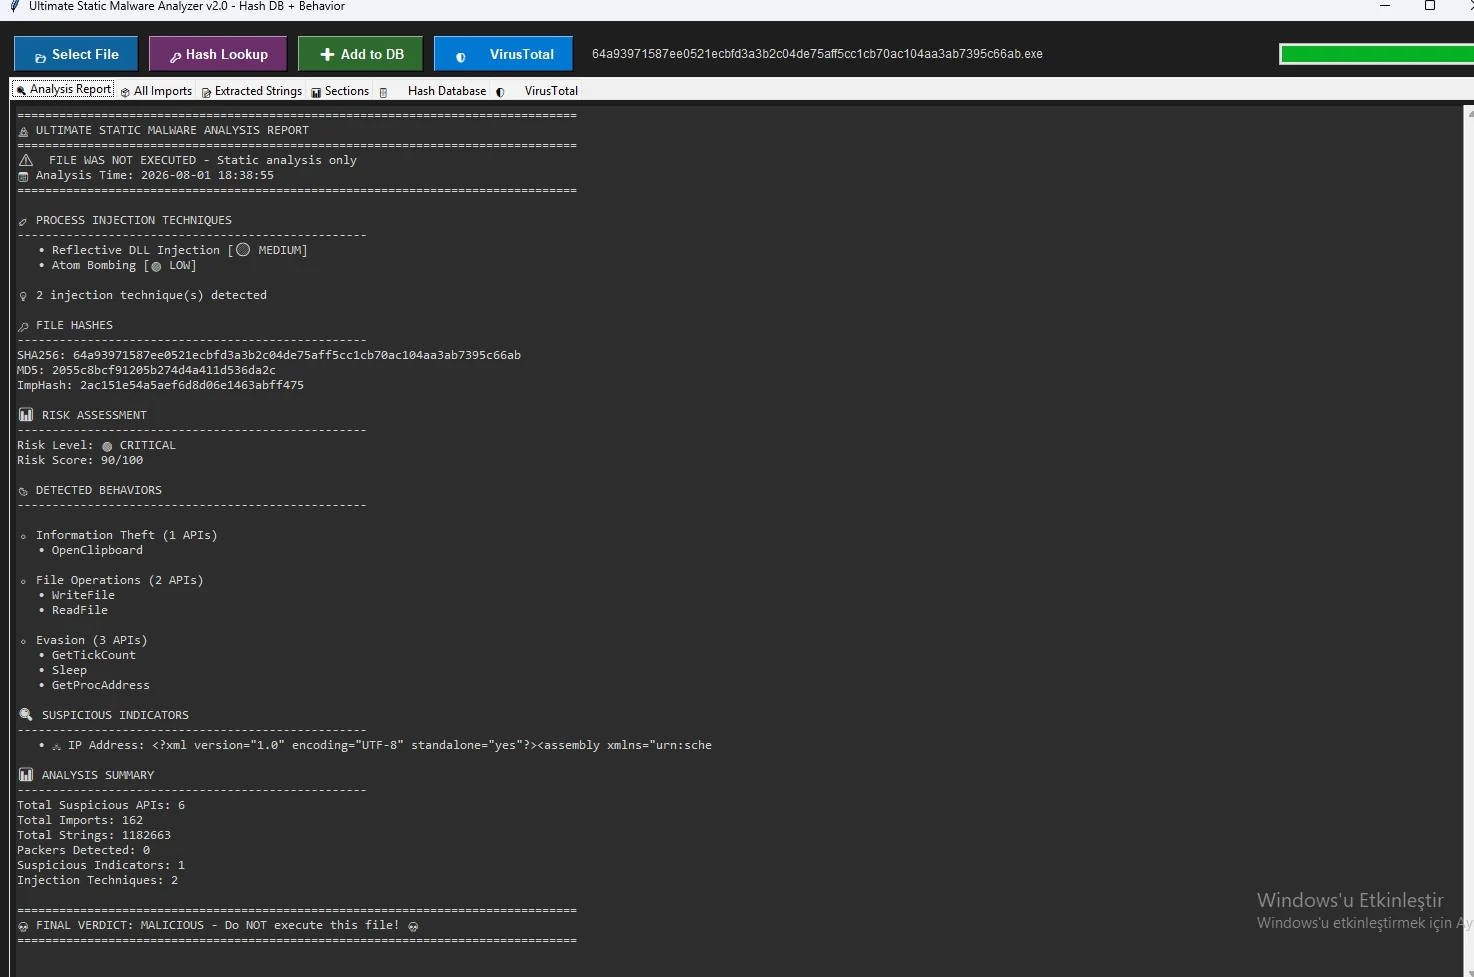 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
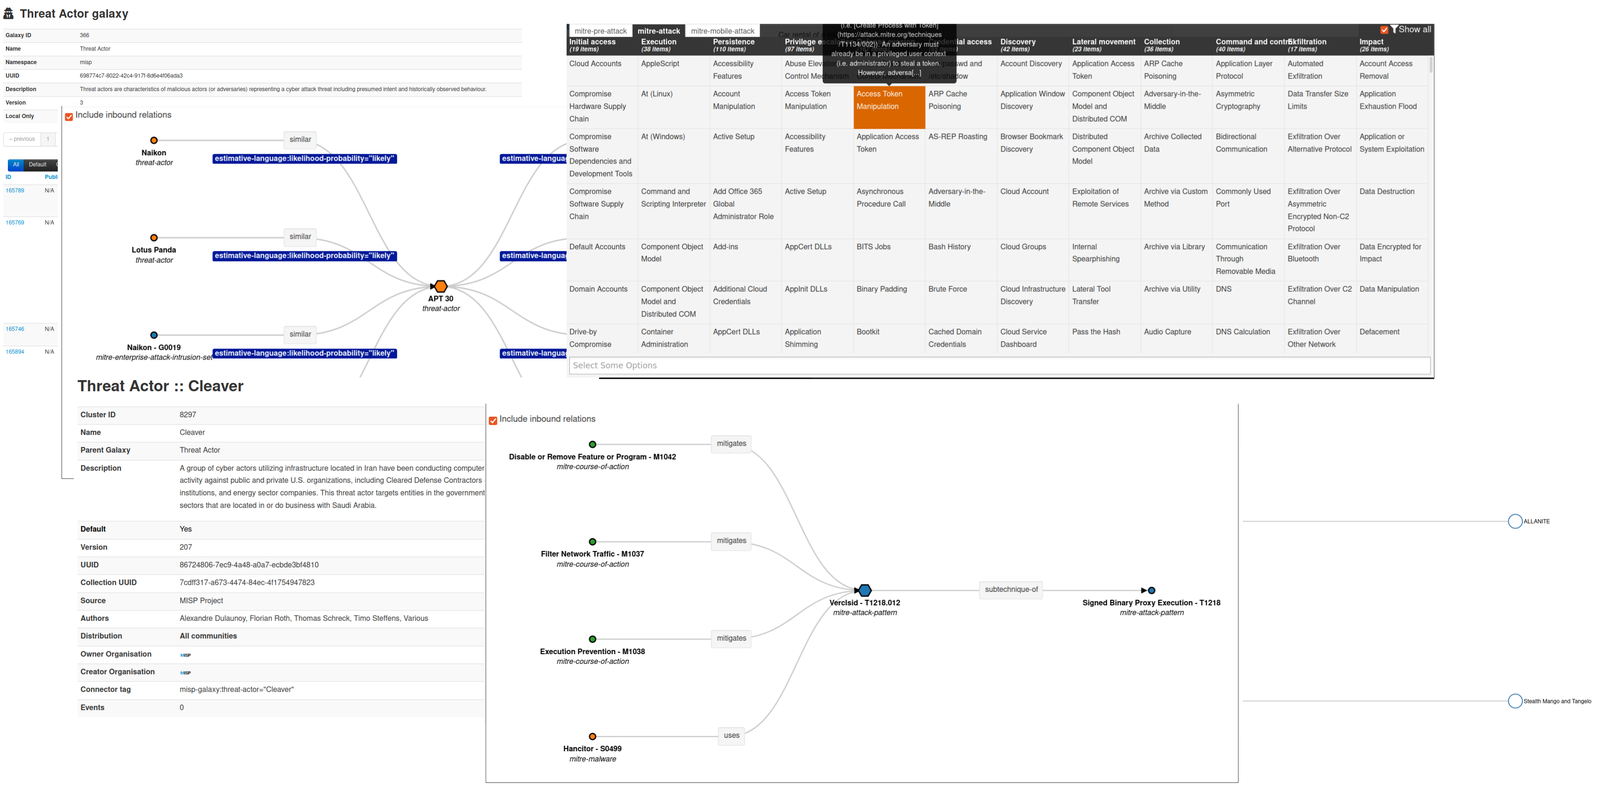 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.