

malware-research
 eset/malware-research
Code written as part of our various malware investigations
digital-forensicsdynamic-code-analysismalware-analysis+4
417
eset/malware-researchCode written as part of our various malware investigations
 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 rshipp/awesome-malware-analysis
Defund the Police.
 elastic/agent-skills
Official Elastic Skills
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 hurricanelabs/machinae
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…
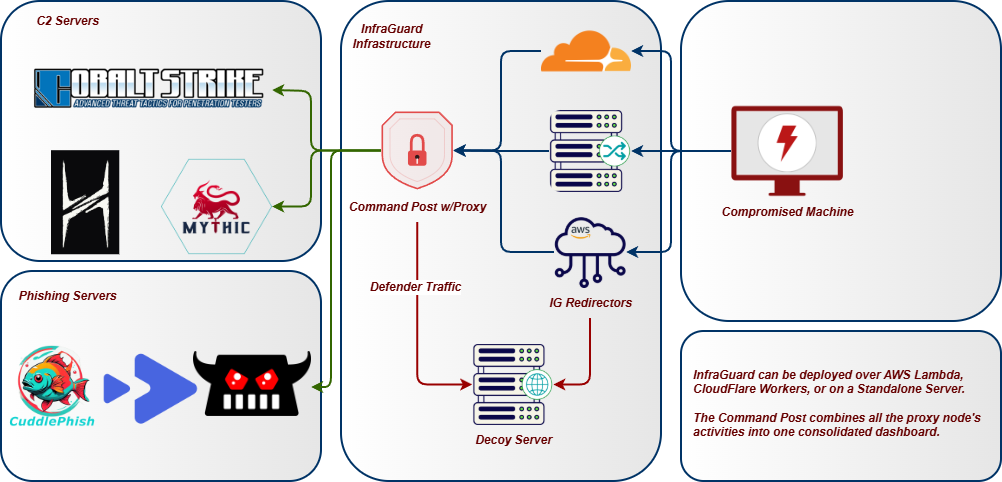 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
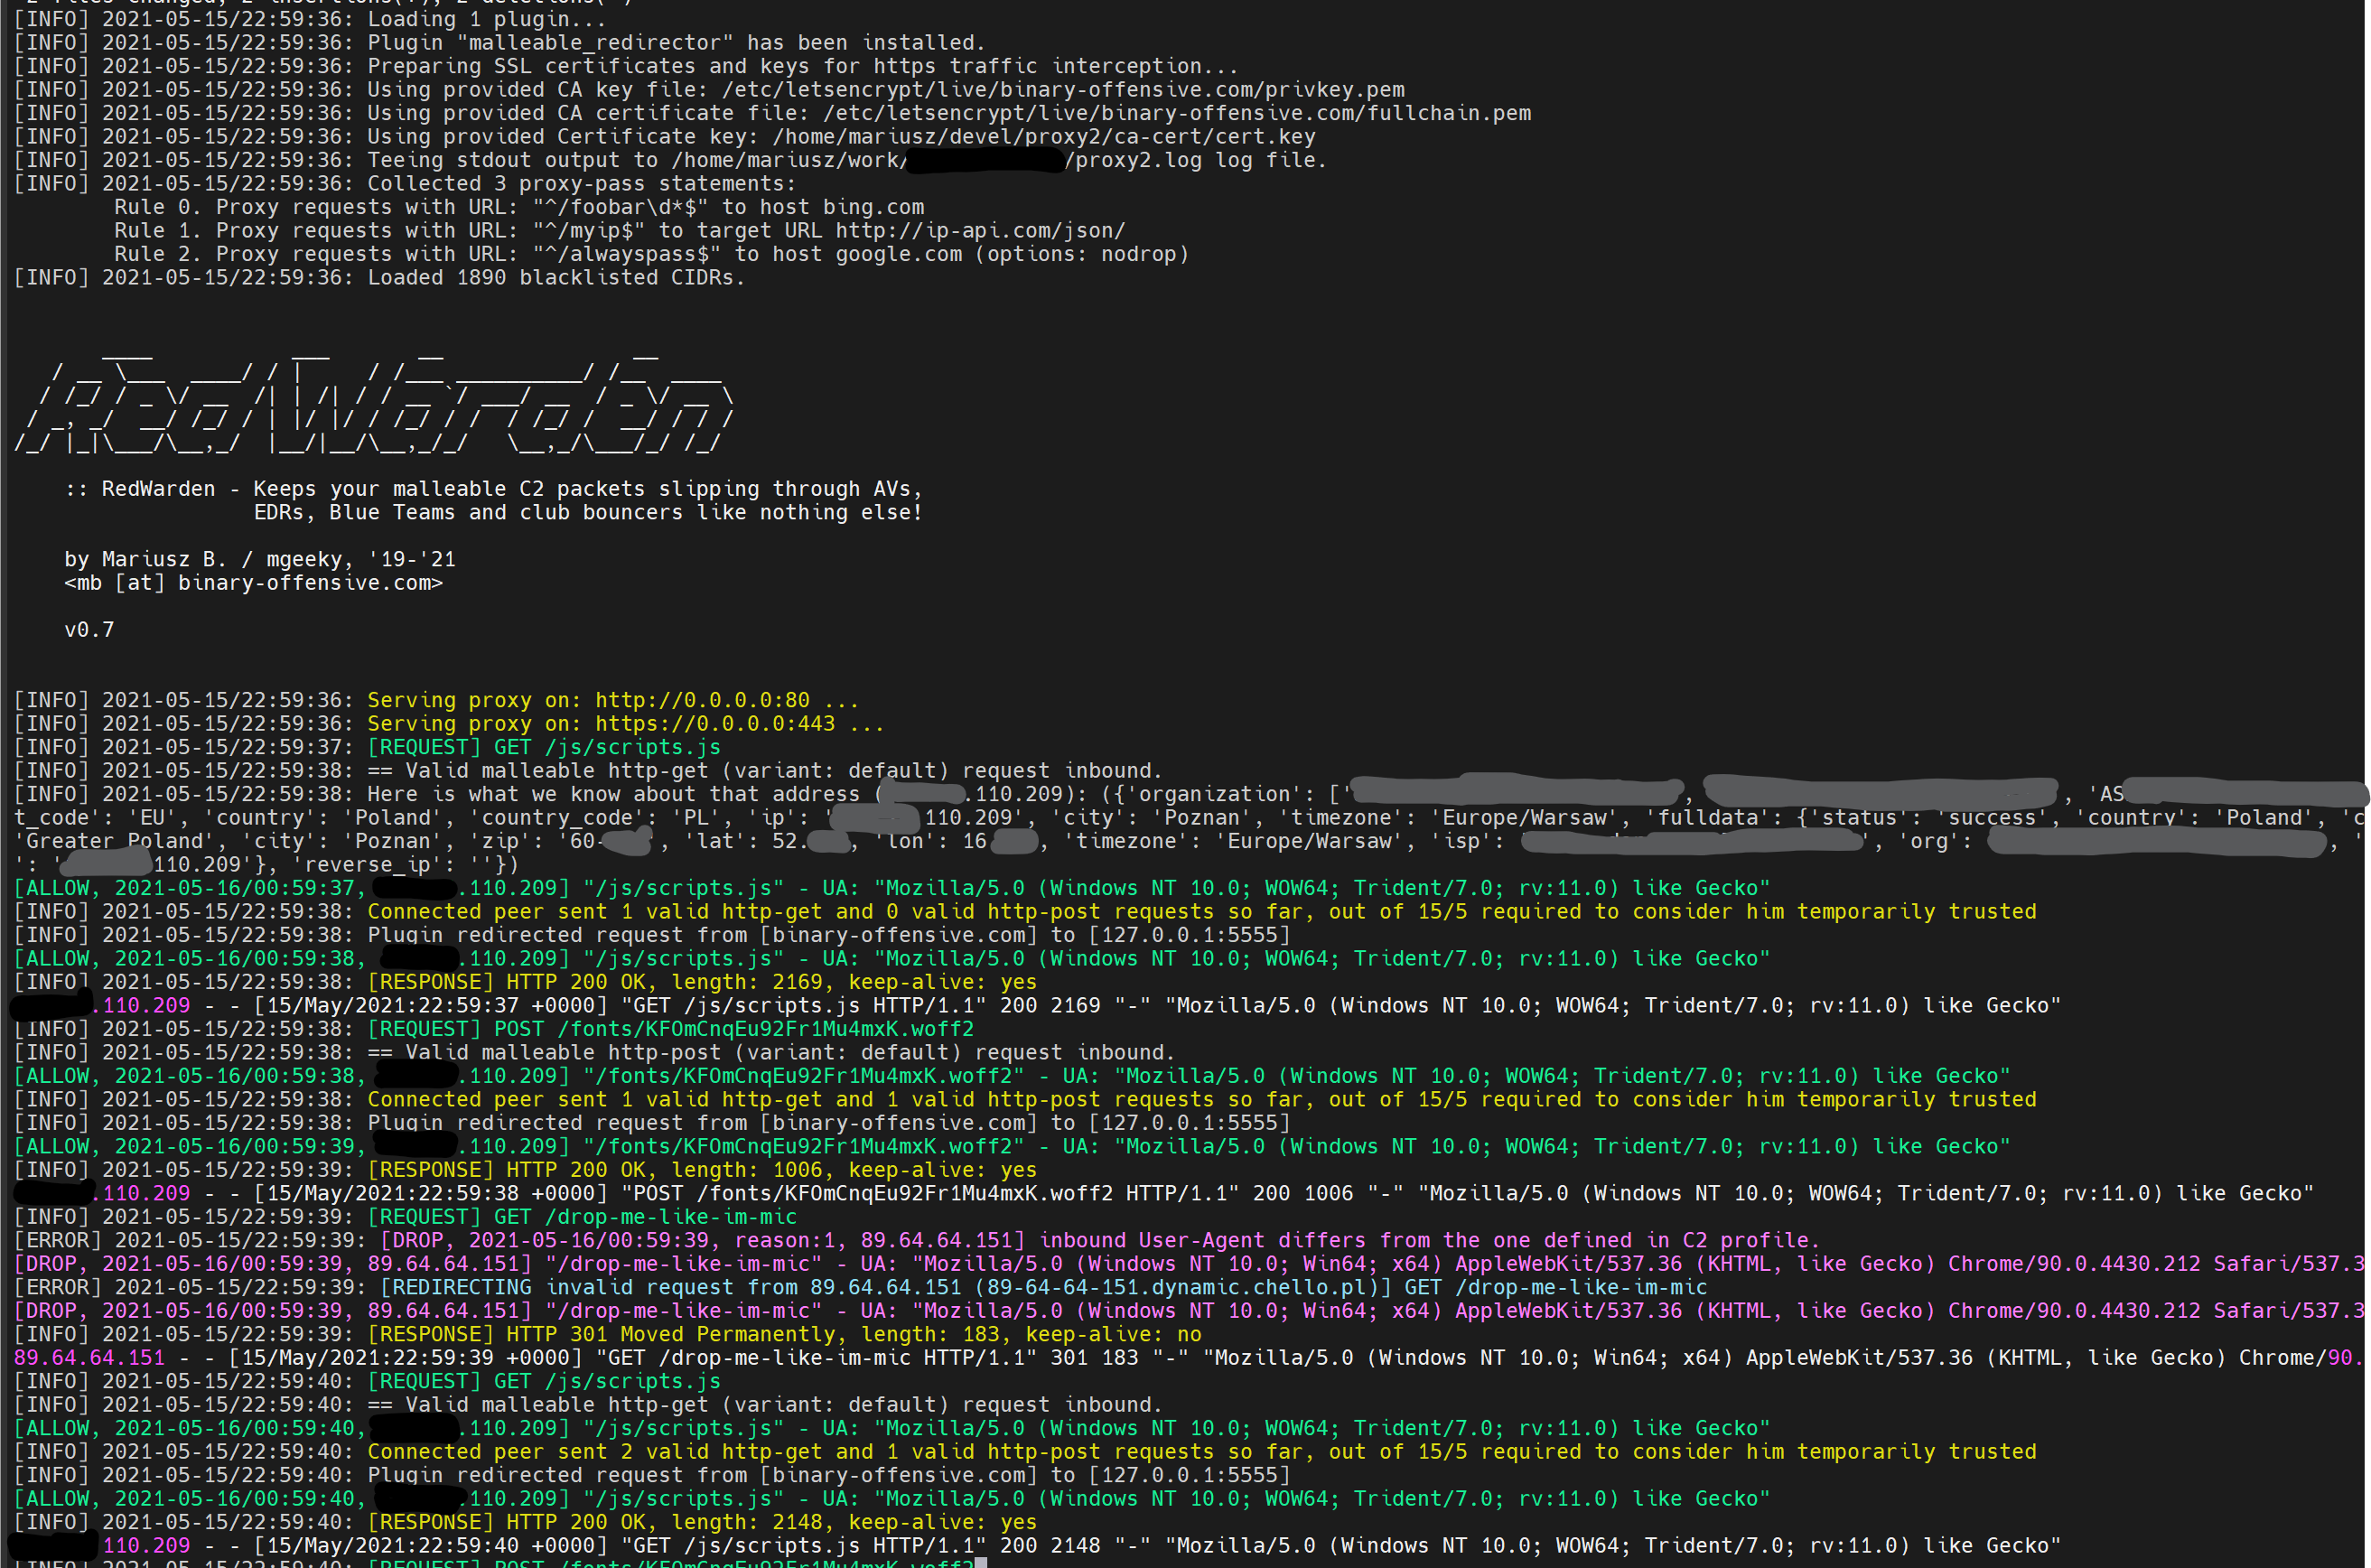 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 c0oki3s/veilgate
Asymmetric defense against adversarial AI agents. VeilGate evaluates each incoming request, redirects suspected agents into a per-IP-consistent…
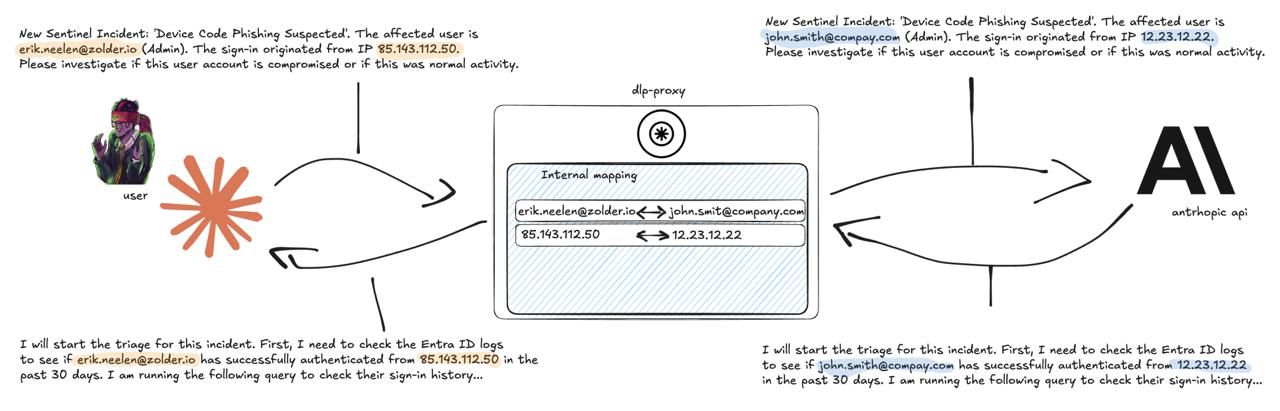 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
 mthbernardes/ipchecker
Check if a IP is from tor or is a malicious proxy
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails