Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
openclaw-security-monitor preview

openclaw-security-monitor

GitHubadibirzu/openclaw-security-monitor

Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.

defensive-toolseducationforensics+9
48
8 days ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.4k2 months ago
CVE-2017-4878-Samples preview

CVE-2017-4878-Samples

GitHubbrianwrf/cve-2017-4878-samples

CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html
binary-exploitationexploitationmalware-analysis+3
178 years ago
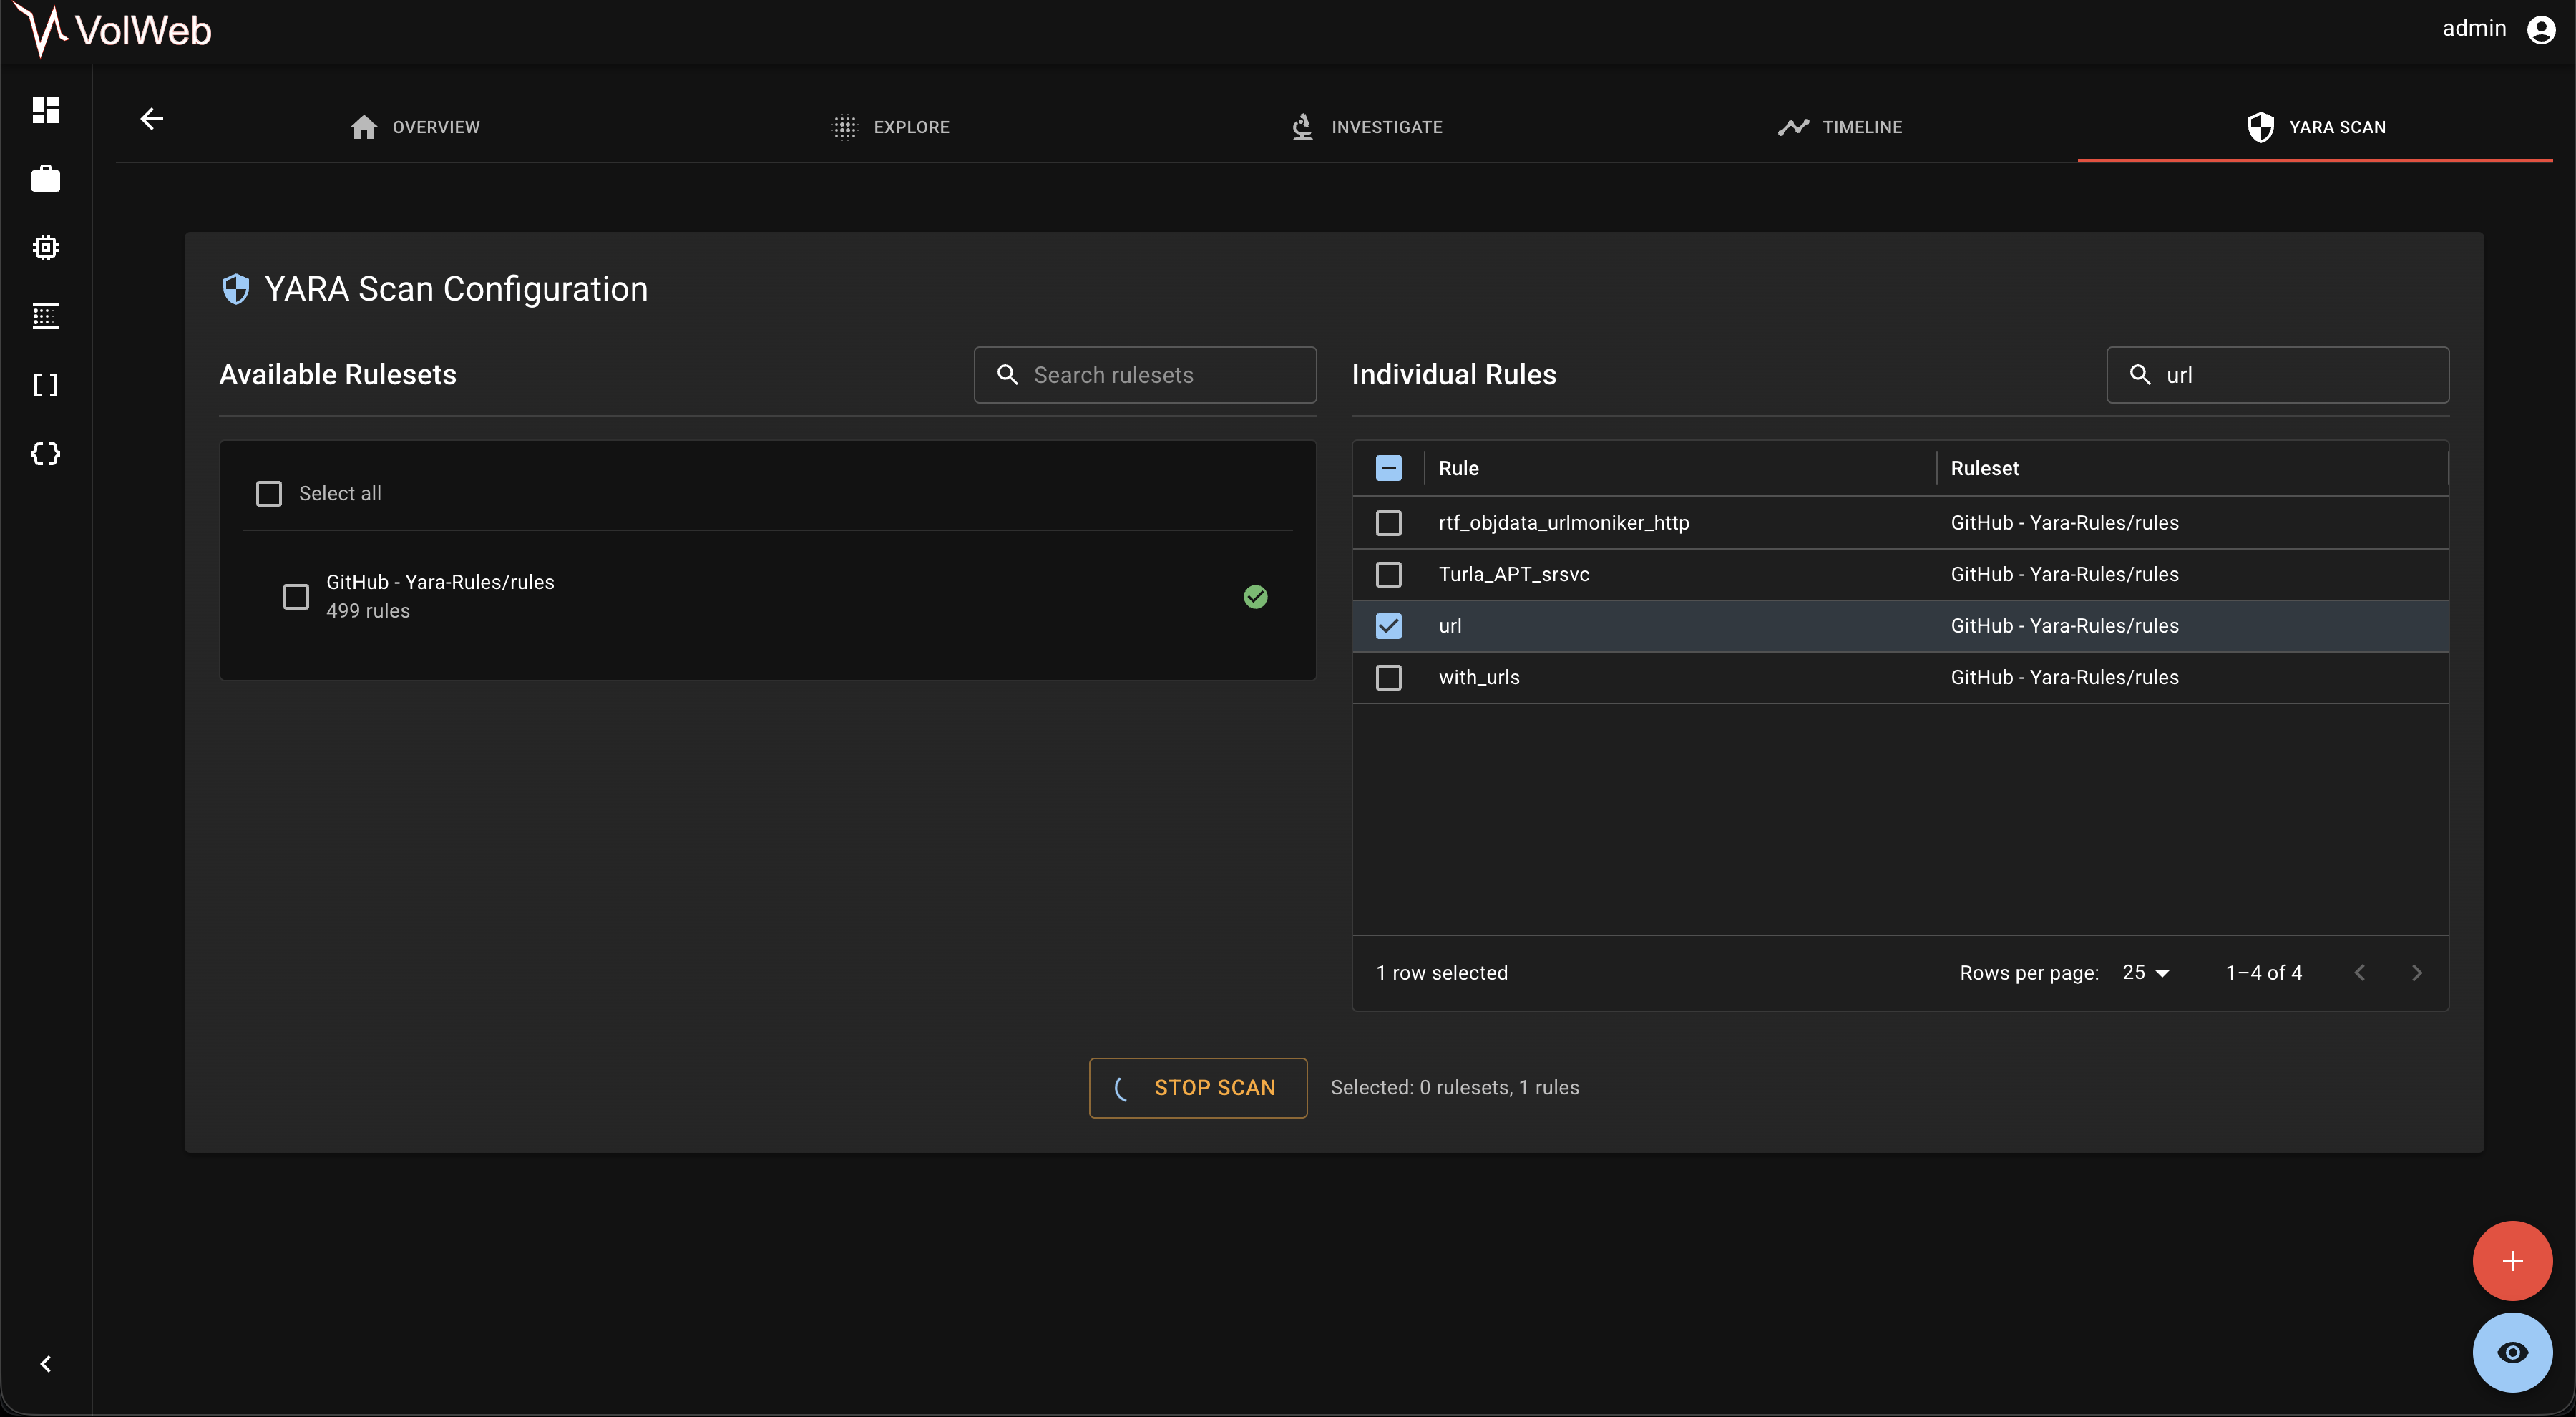
VolWeb preview

VolWeb

GitHubk1nd0ne/volweb

A centralized and enhanced memory analysis platform
digital-forensicseducationforensics+5
5382 months ago
CVE-2023-38831 preview

CVE-2023-38831

GitHubmishra0230/cve-2023-38831

CVE-2023-38831 - WinRAR
binary-exploitationeducationexploitation+8
8 months ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
binary-analysisdigital-forensicseducation+8
18521 days ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
binary-analysiscontainer-escapedata-recovery+7
121 month ago
Fragnesia-CVE-2026-46300 preview

Fragnesia-CVE-2026-46300

GitHubmaxime288/fragnesia-cve-2026-46300

Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
binary-exploitationcurated-resourceseducation+5
4 months ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

binary-analysiscommand-and-controleducation+6
52 months ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
3232 years ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
binary-analysisdebuggersdigital-forensics+9
442 years ago
awesome-reverse-engineering-and-malware-analysis preview

awesome-reverse-engineering-and-malware-analysis

GitHubzx41r/awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
binary-analysisbinary-exploitationctf+8
901 day ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

anomaly-detectiondigital-forensicsincident-response+5
73727 days ago
linux-explorer preview
Archived

linux-explorer

GitHubintezer/linux-explorer

Easy-to-use live forensics toolbox for Linux endpoints
digital-forensicsforensicsincident-response+7
4042 years ago
BeaconEye preview

BeaconEye

GitHubccob/beaconeye

Hunts out CobaltStrike beacons and logs operator command output
command-and-controldigital-forensicsmalware-analysis+2
9602 years ago
Reports preview

Reports

GitHubj4ck3lsyn-gen2/reports

Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
binary-exploitationcurated-resourcesexploitation+8
22 months ago
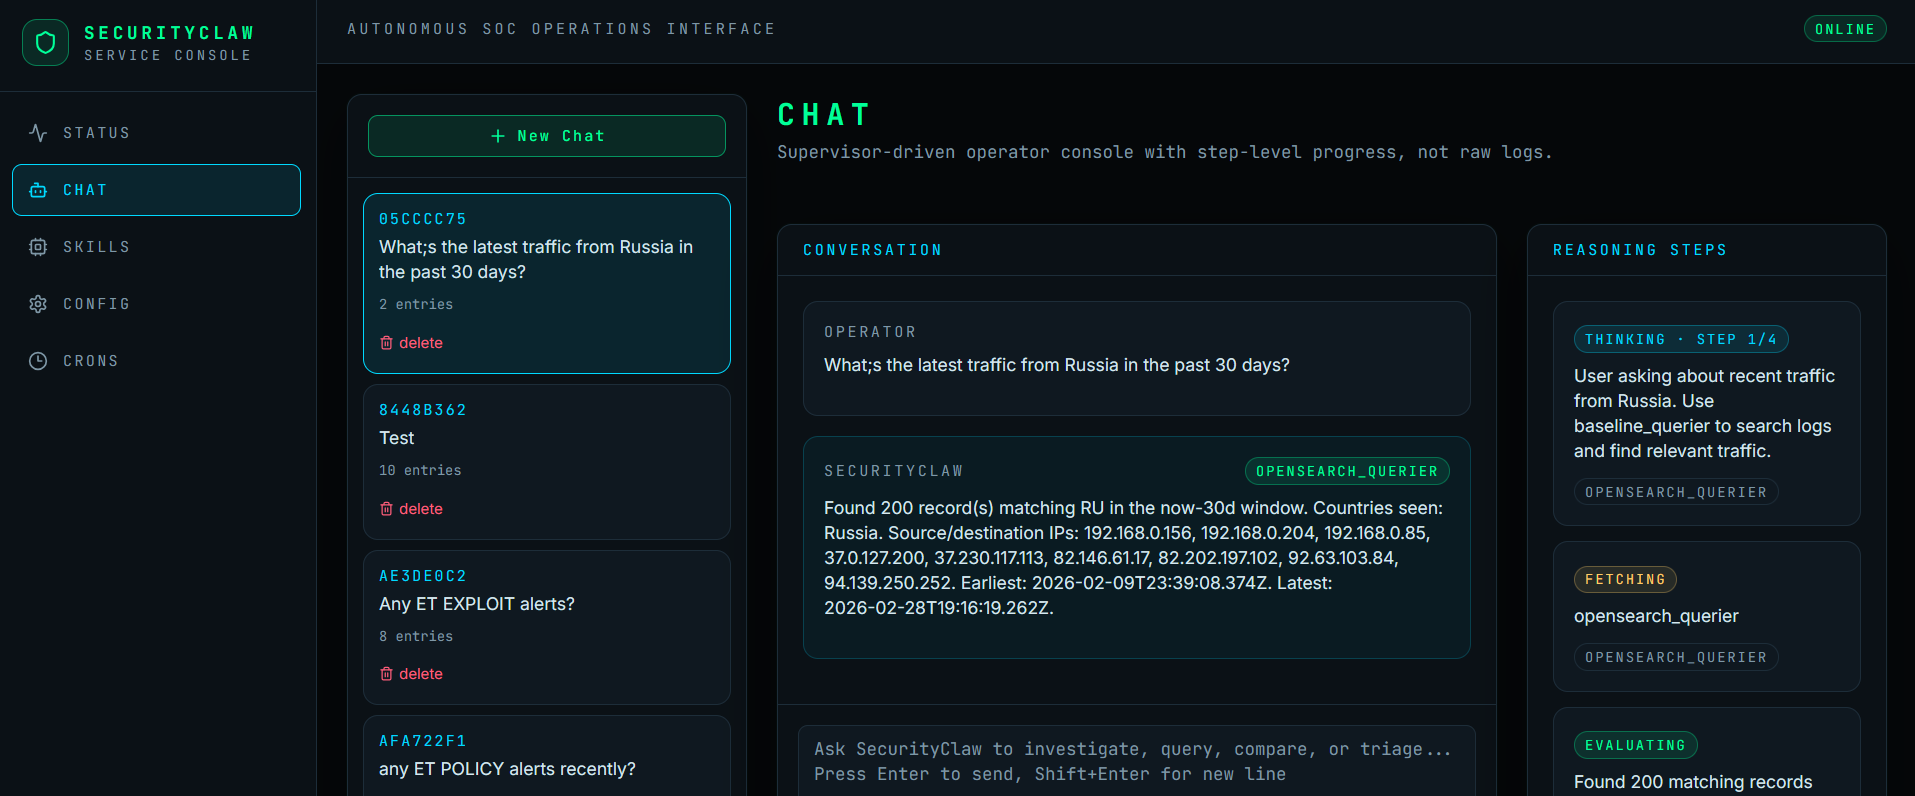
SecurityClaw preview

SecurityClaw

GitHubsecurityclaw/securityclaw

A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
ai-securityanomaly-detectionforensics+8
2722 months ago
YourMemory preview

YourMemory

GitHubsachitrafa/yourmemory

Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.

ai-securityauthentication-authorizationforensics+5
2702 months ago
Previous12Next