

NetAlertX
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
configuration-auditingdevsecopsincident-response+6
7.3k
netalertx/netalertxCentralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 eset/malware-research
Code written as part of our various malware investigations
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
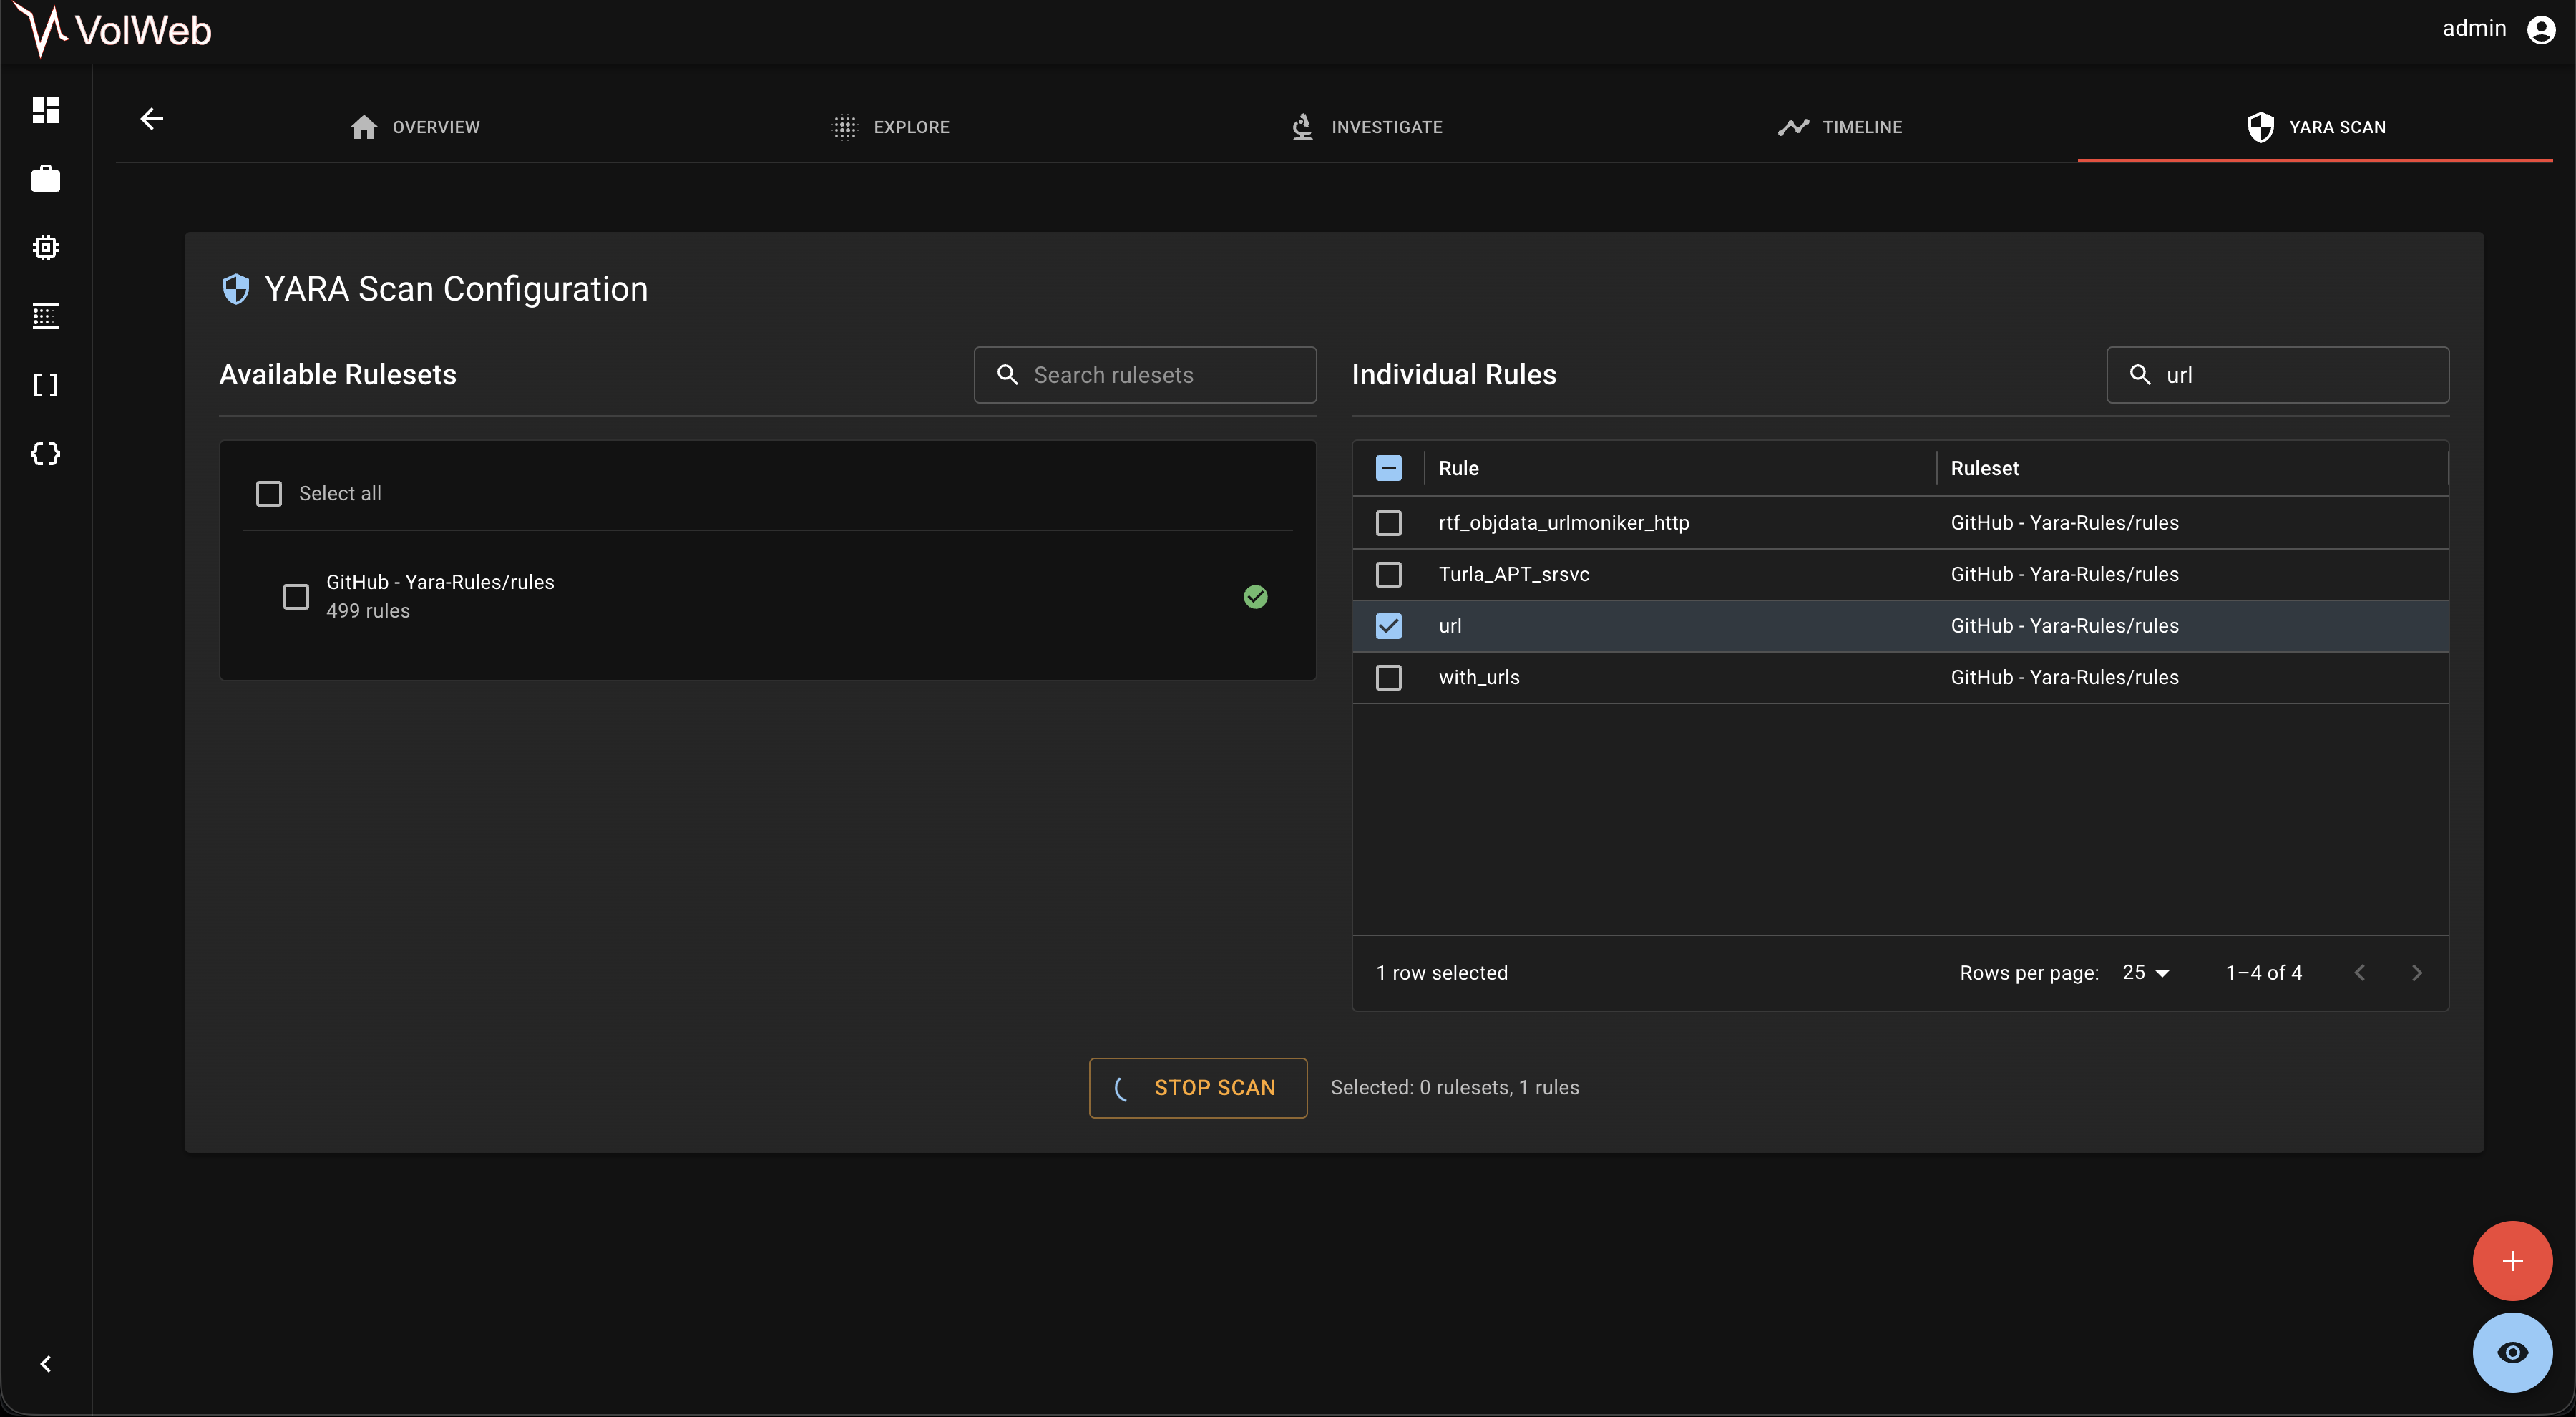 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 mrwadams/stride-gpt
An AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
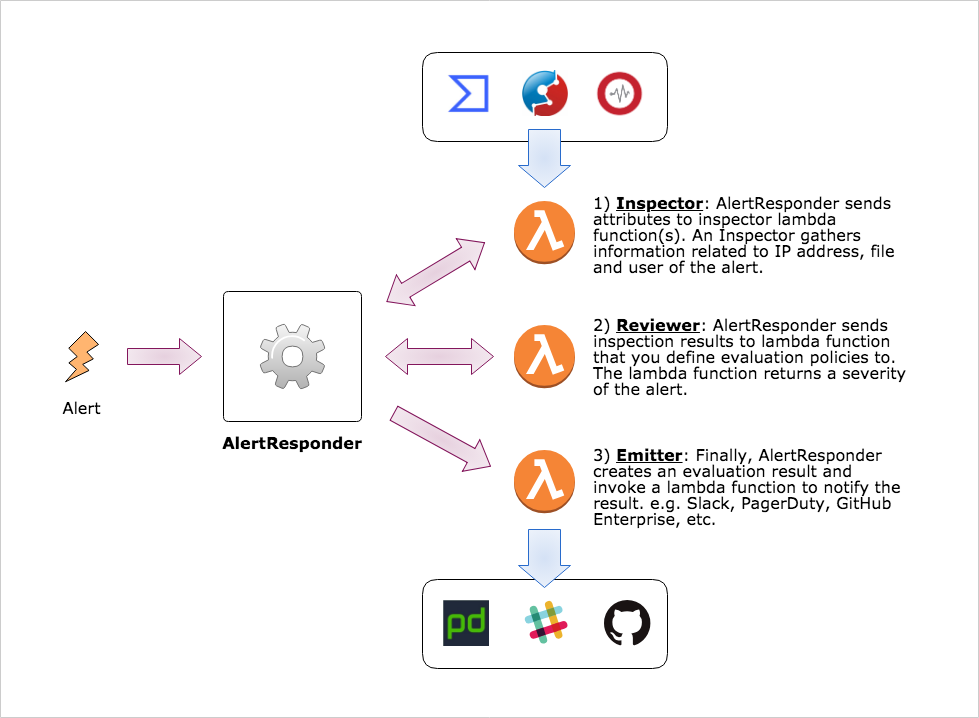 m-mizutani/alertresponder
Automatic security alert response framework by AWS Serverless Application Model
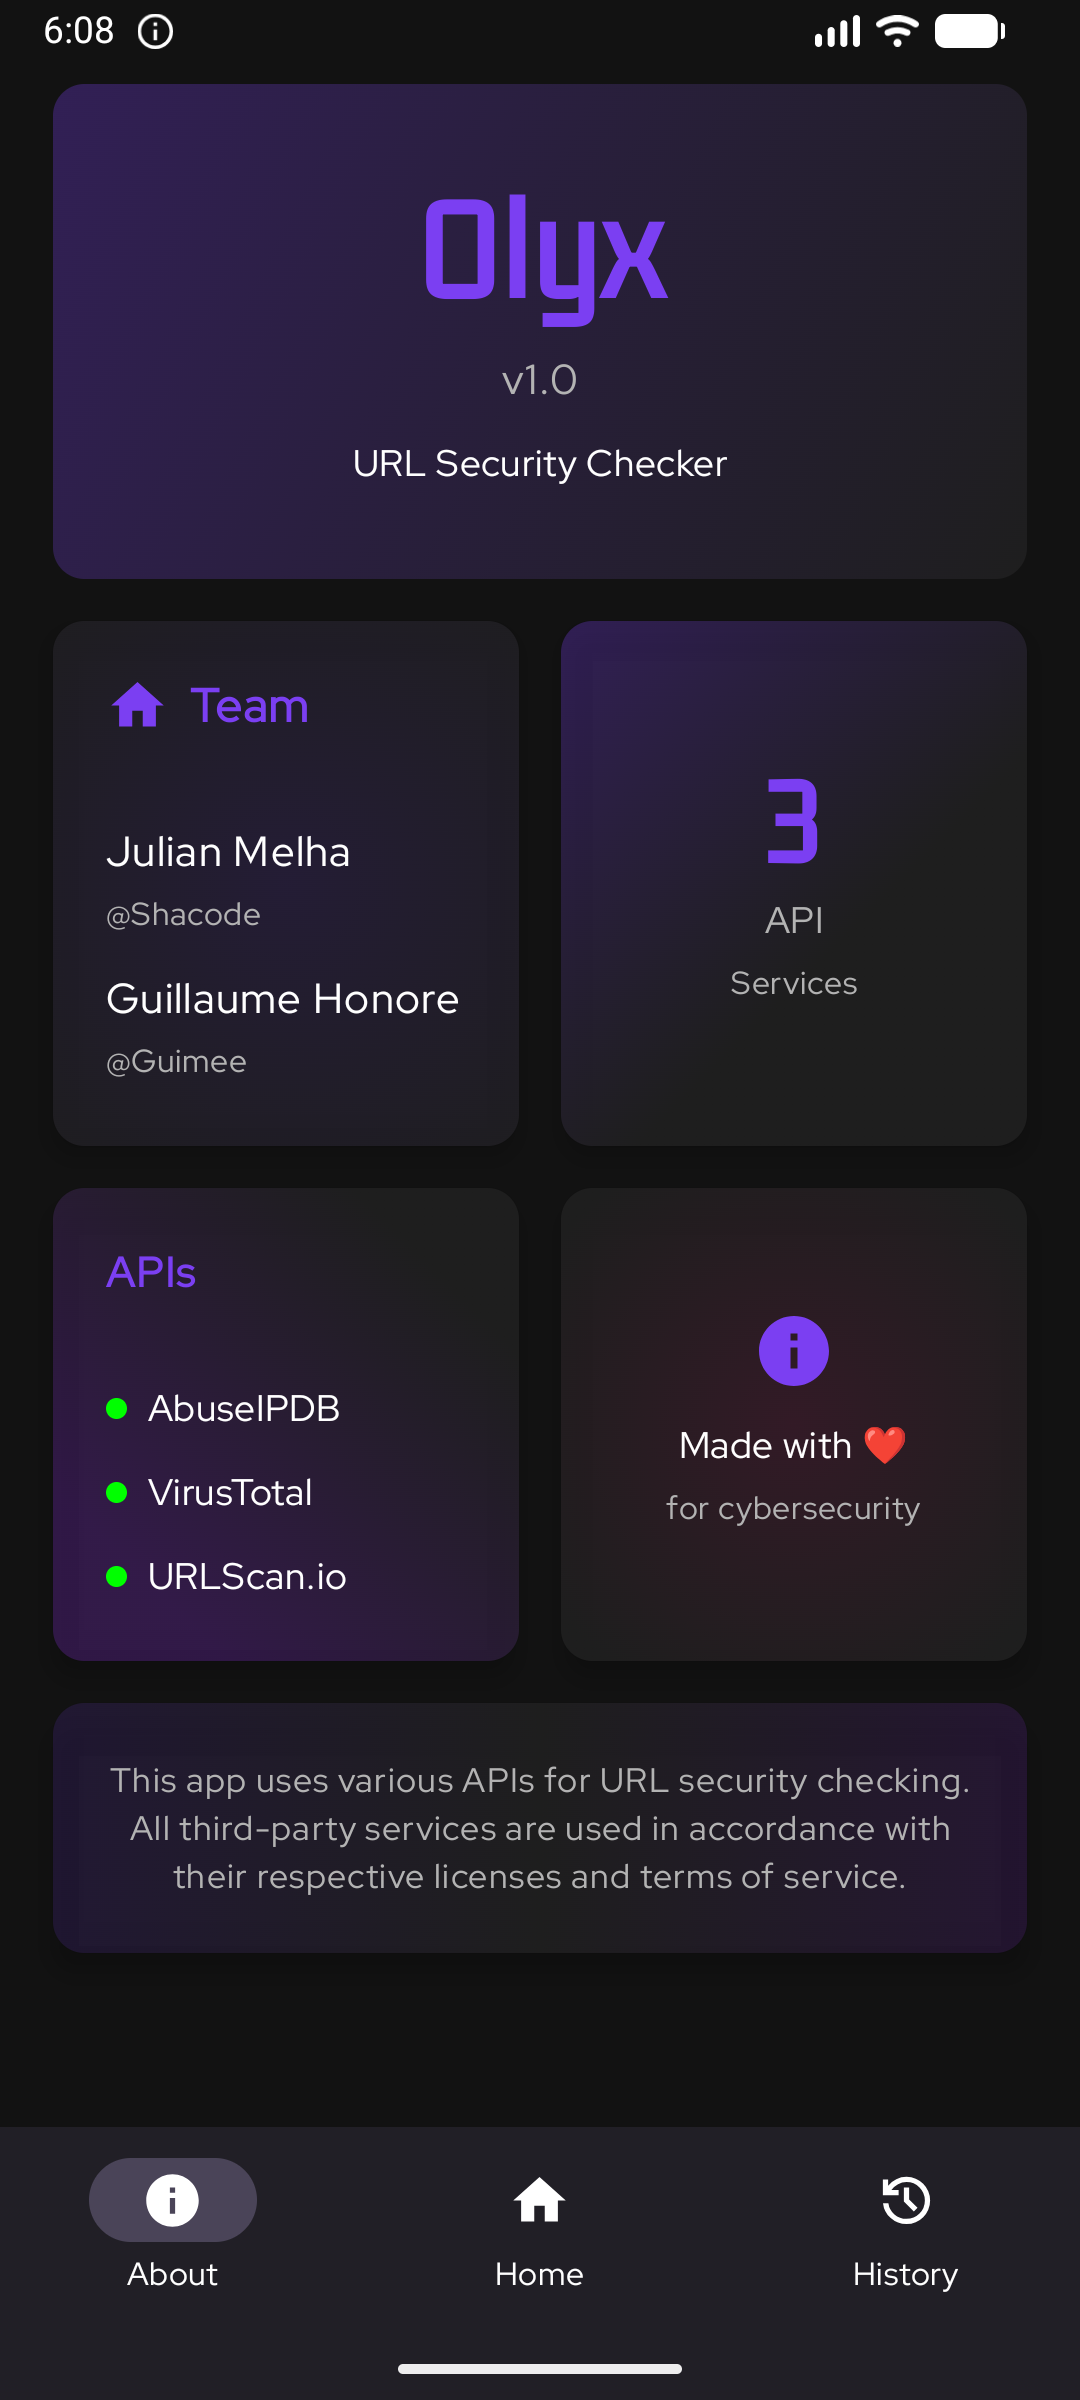 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 0xblackash/cve-2026-72898
CVE-2026-72898
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.