

trufflehog
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
cloud-securitycode-analysisdevsecops+6
28.0k
trufflesecurity/trufflehogFind, verify, and analyze leaked credentials
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 zdhenard42/soc-multitool
A powerful and user-friendly browser extension that streamlines investigations for security professionals.
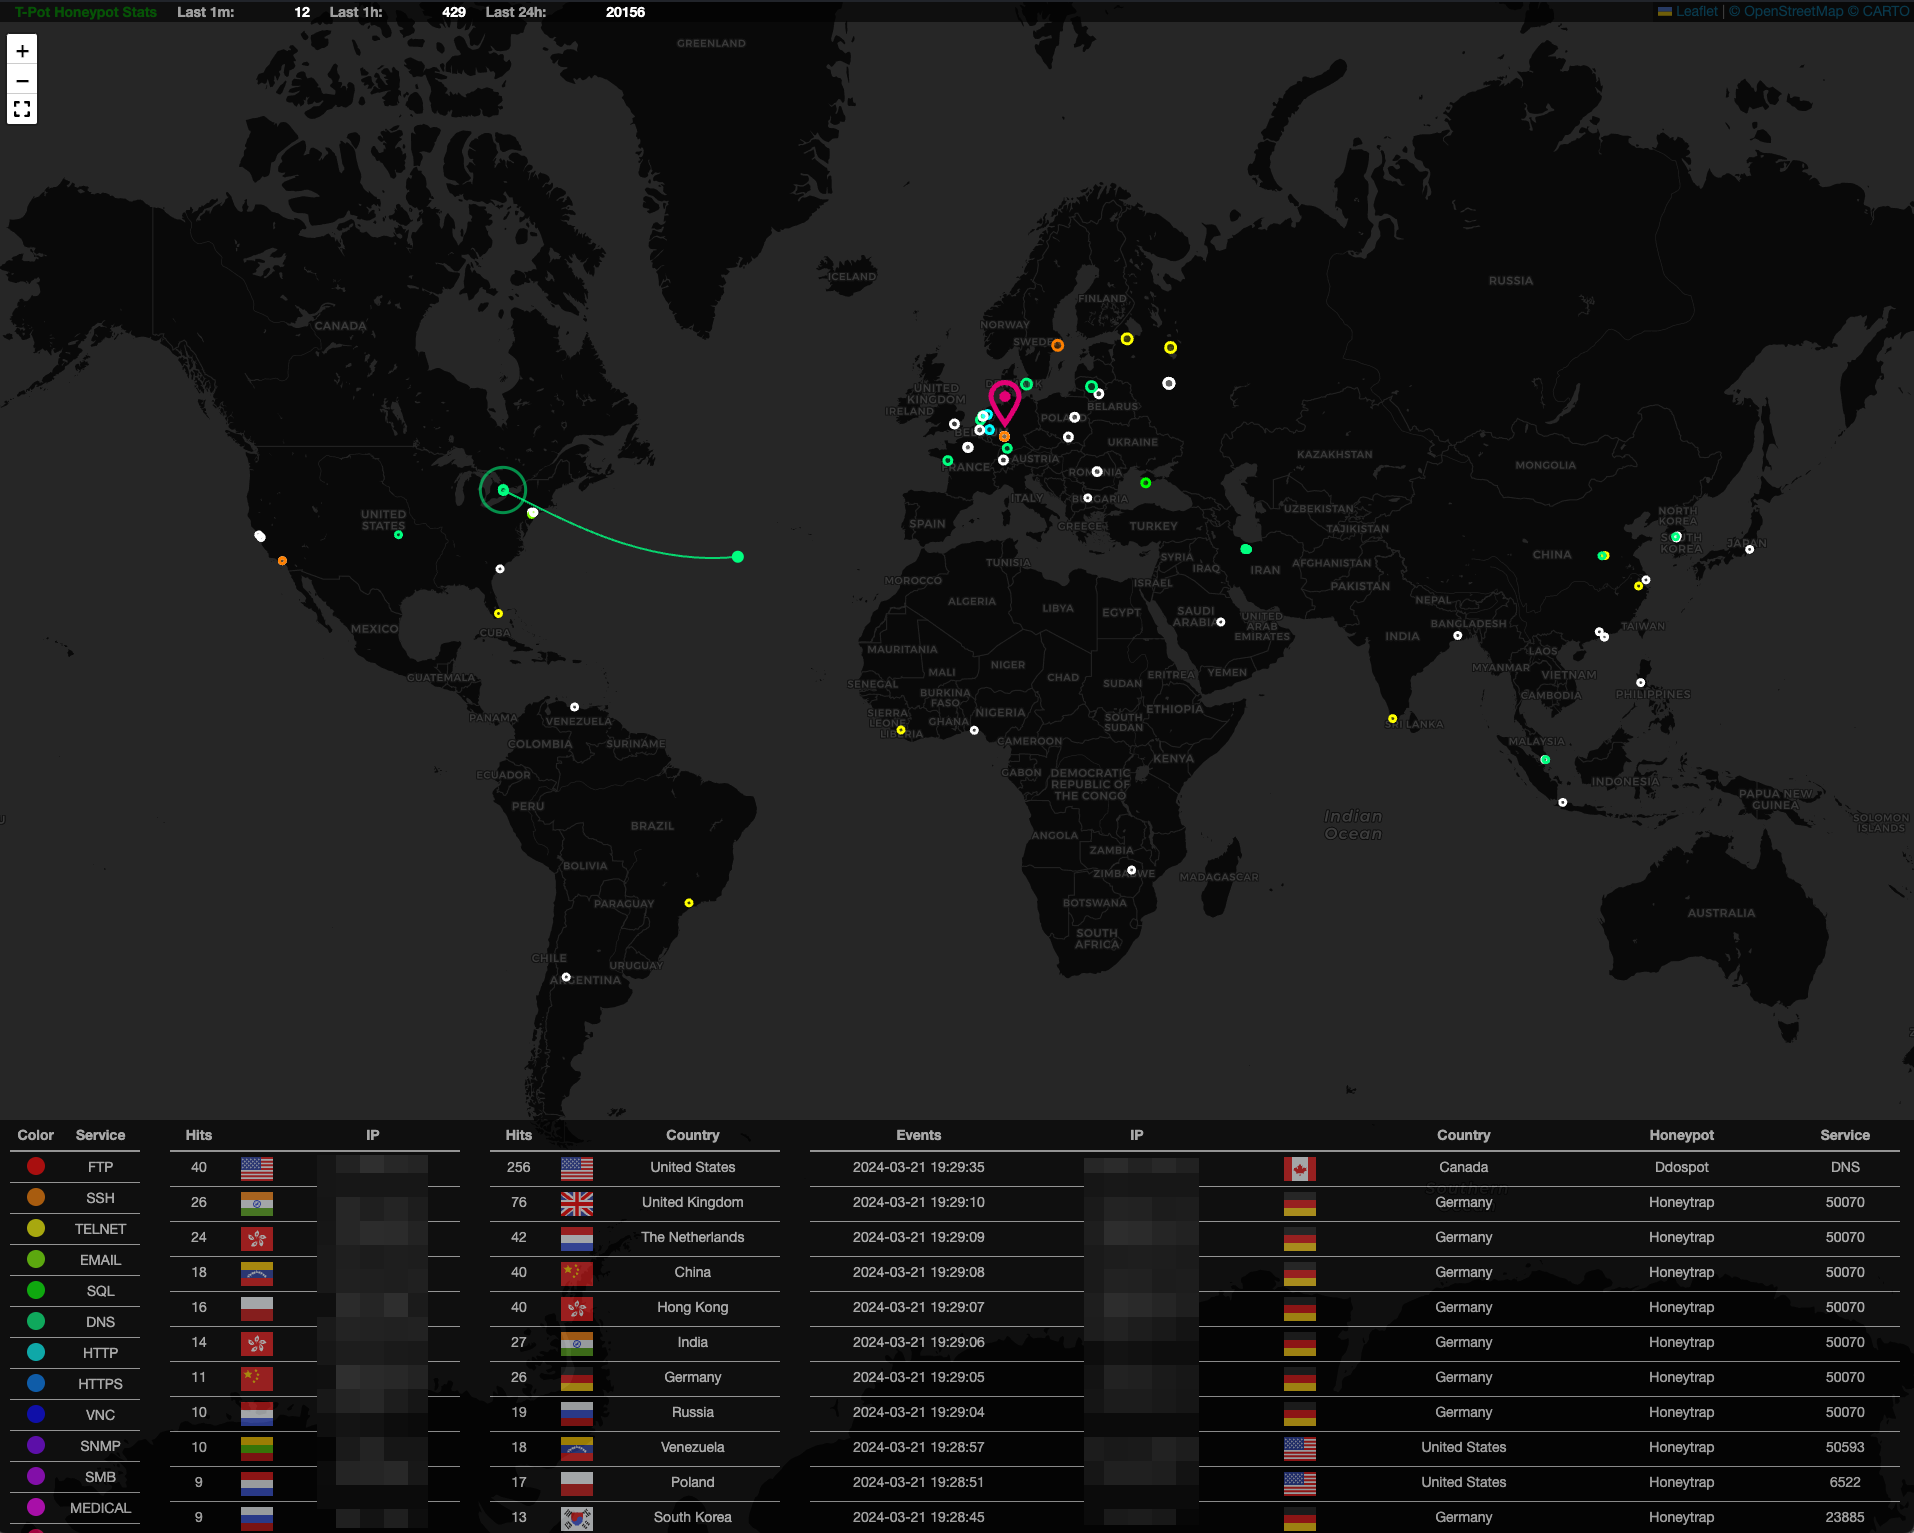 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 ares-sys/uefi_bootkit_softlanding
First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…
 michaelsanford/log4shell-honeypot
Dockerized honeypot for CVE-2021-44228.

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
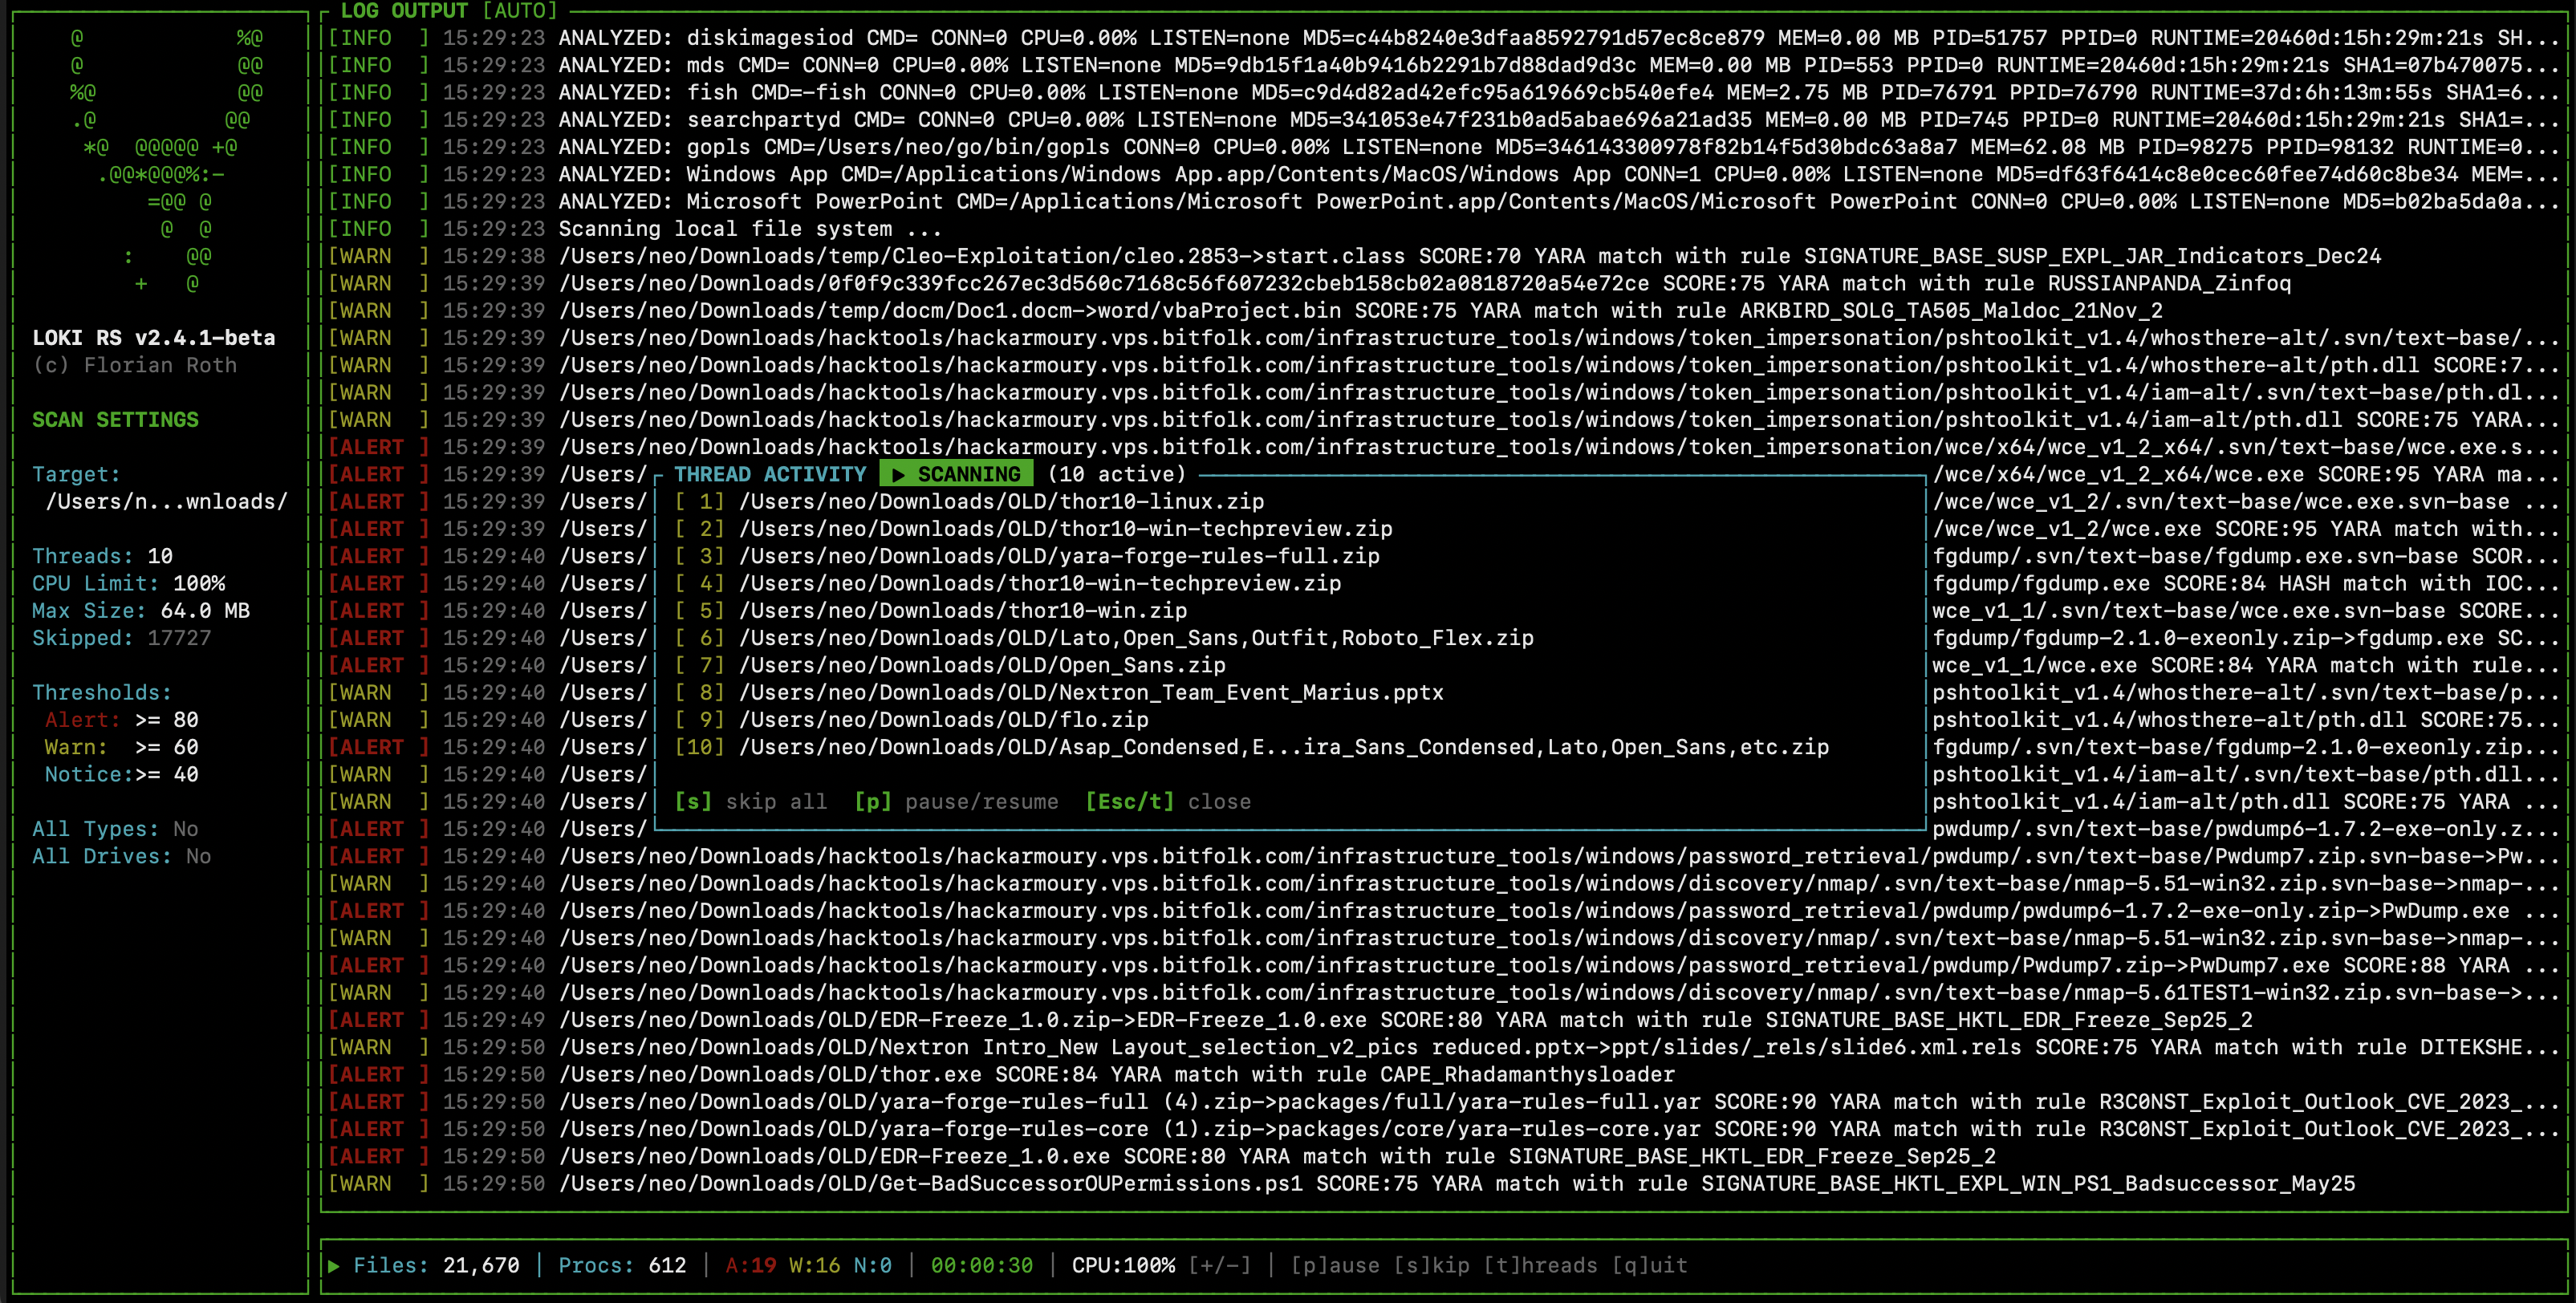 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 alsatianconsulting/skyprofile
A lightweight aviation intelligence tool that queries ADSB-Exchange flight data using tail numbers or ICAO identifiers to quickly profile aircraft…