Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

VulnCheck's official command line tool

Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA

Defund the Police.

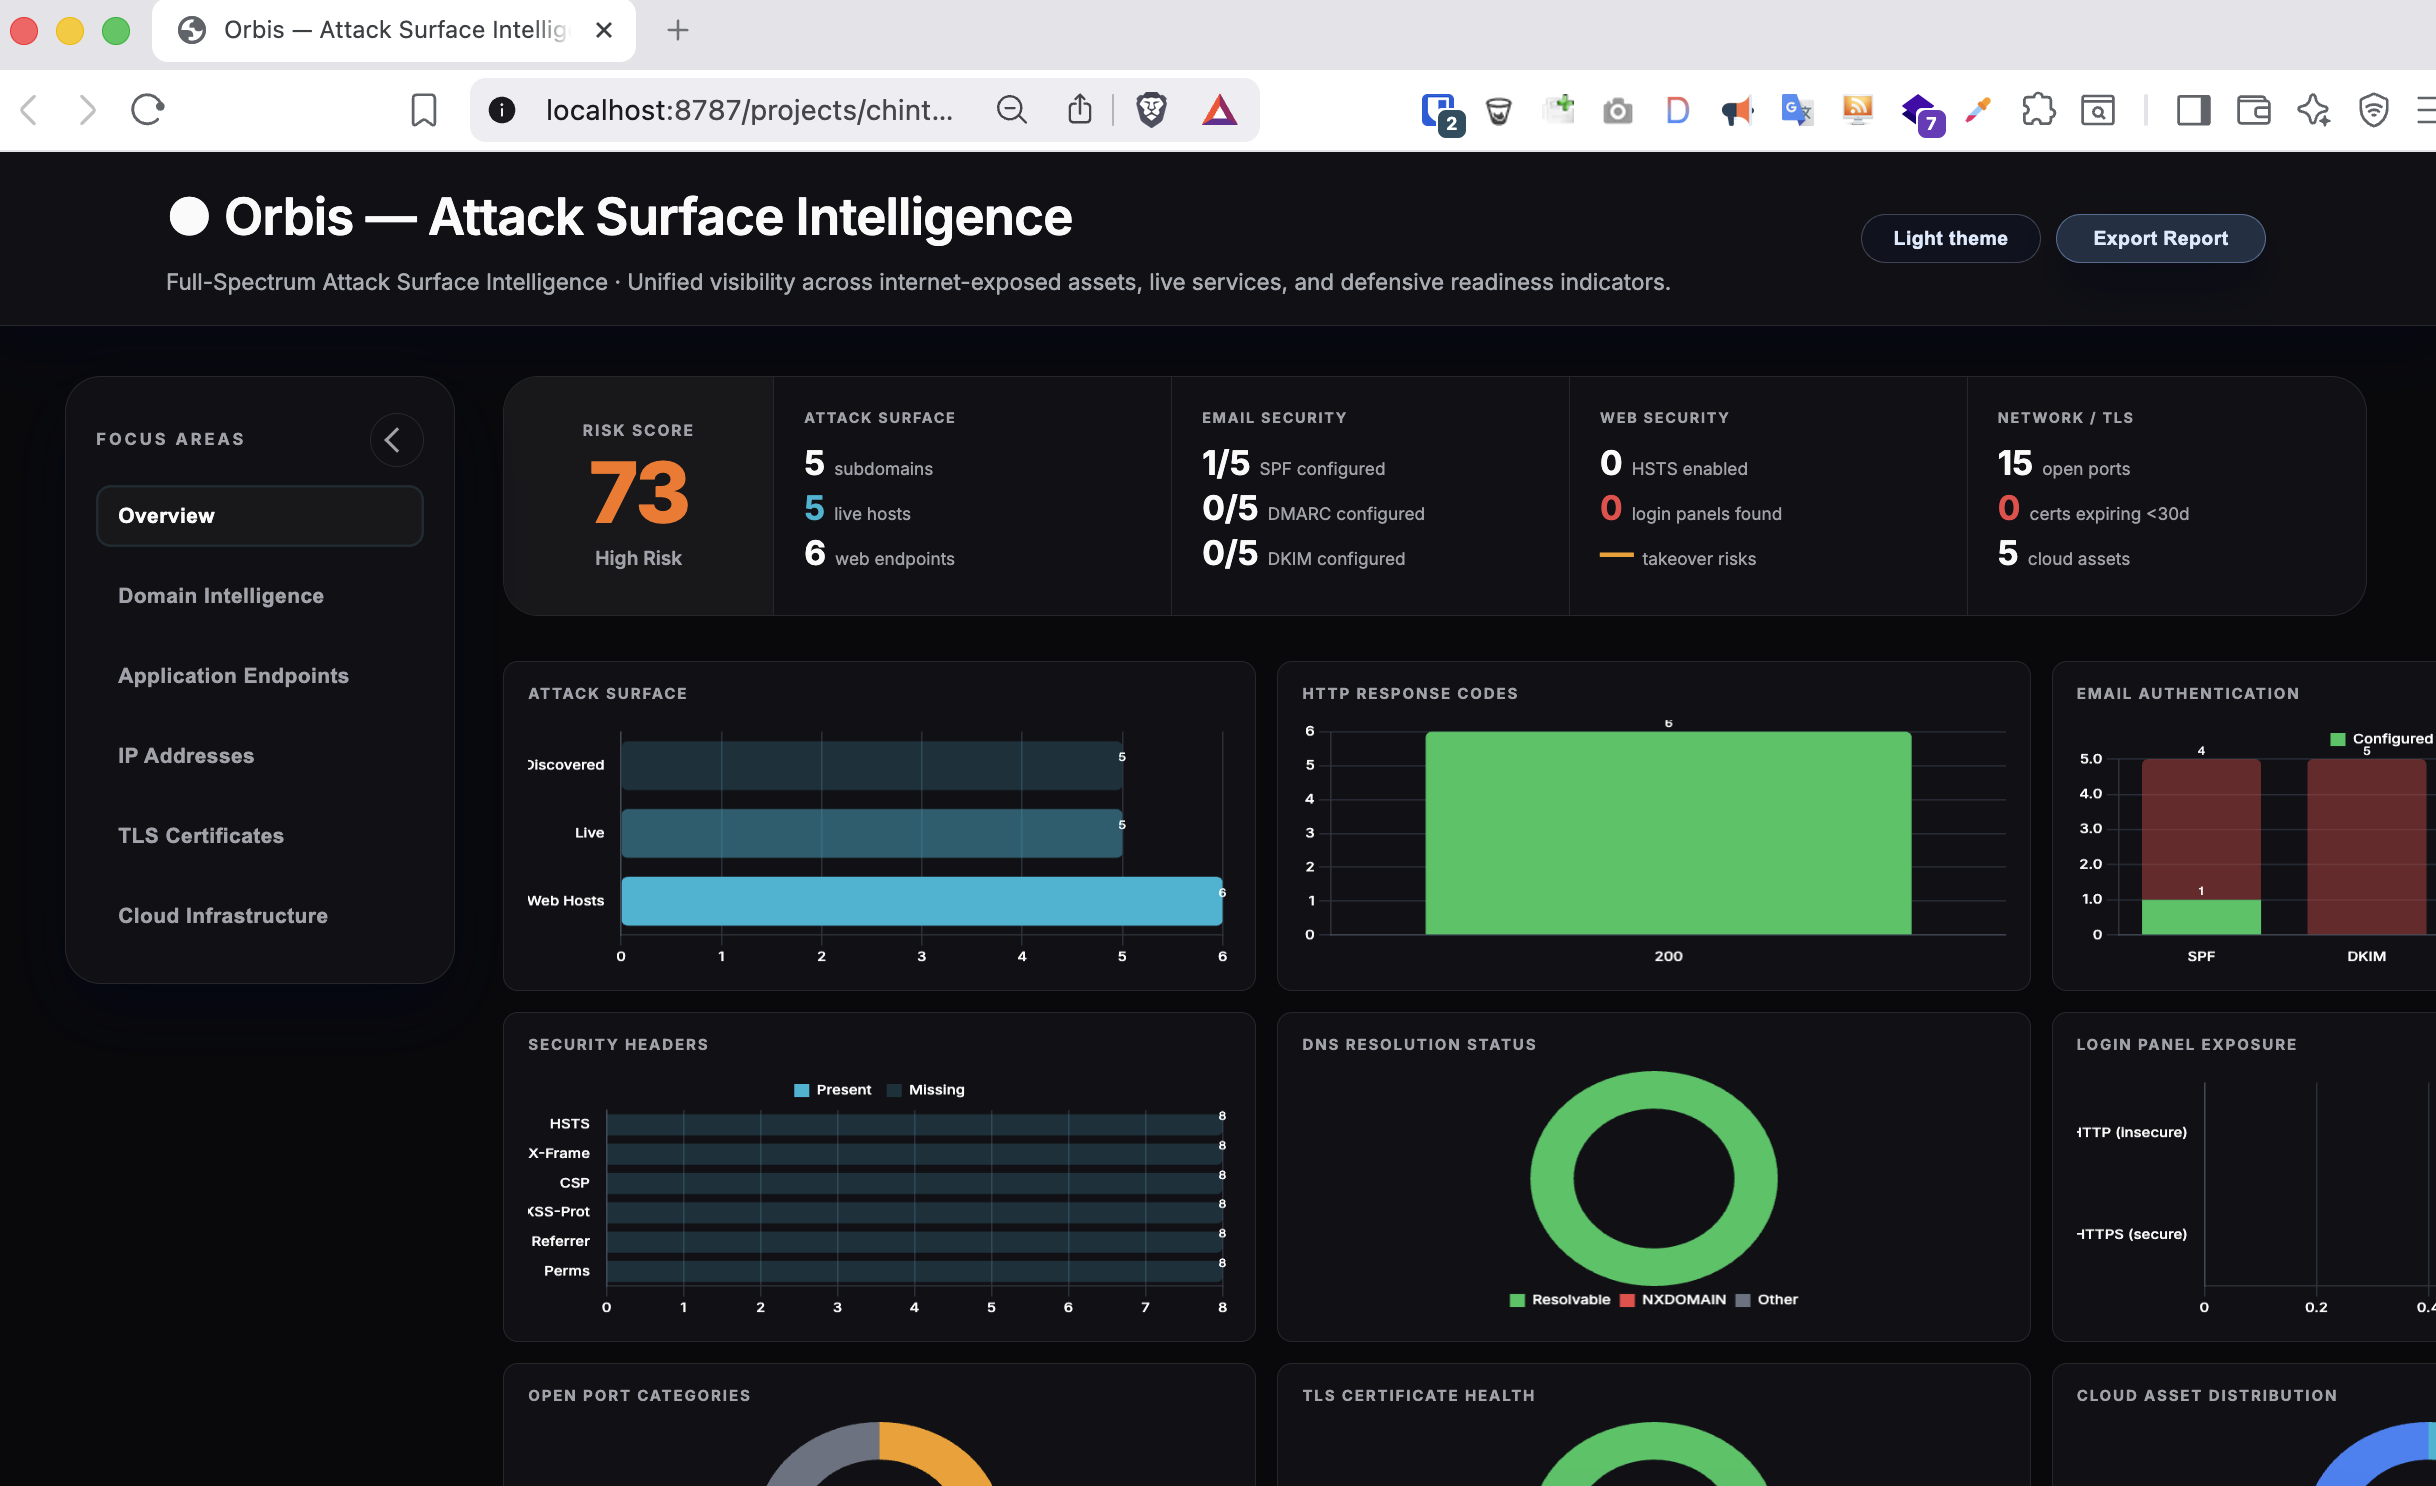
Orbis is an full spectrum automated external attack surface intelligent toolkit.

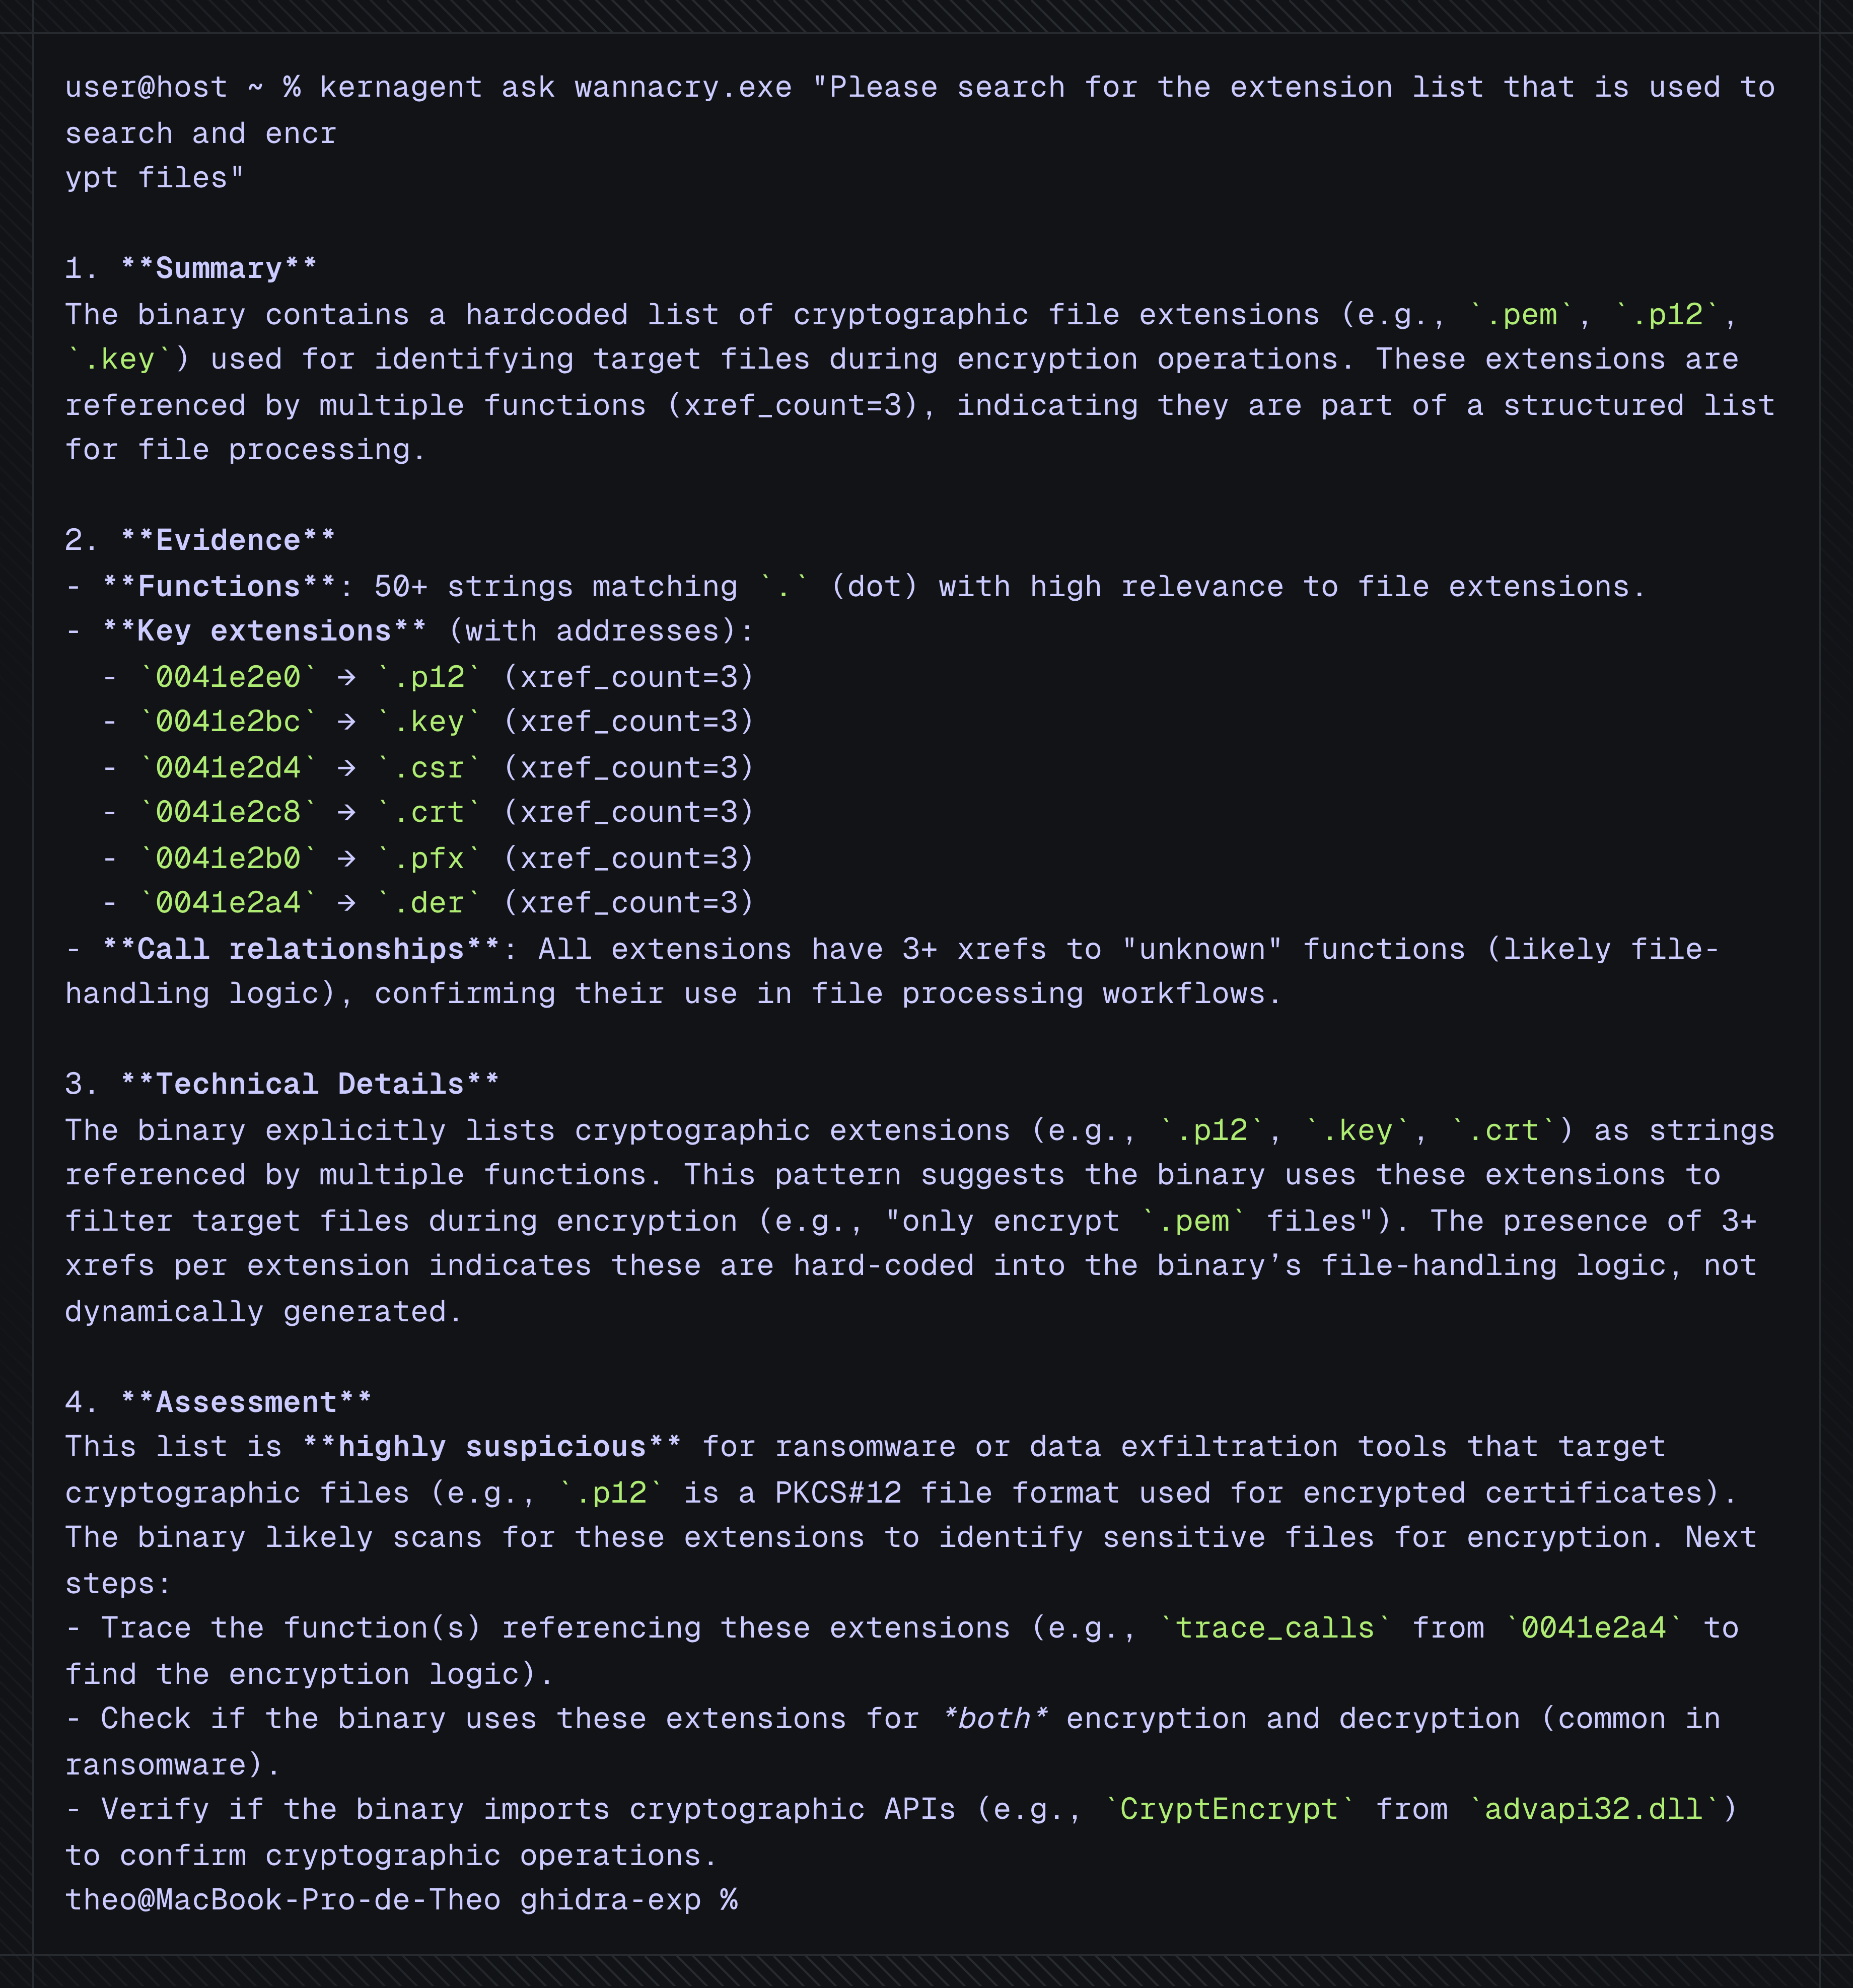
Headless AI agent for deterministic reverse engineering.

A process monitoring tool that tries to detect exploitation

Tracking interesting Linux (and UNIX) malware. Send PRs

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.

Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075

Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…

a guard that blocks catastrophic agent actions

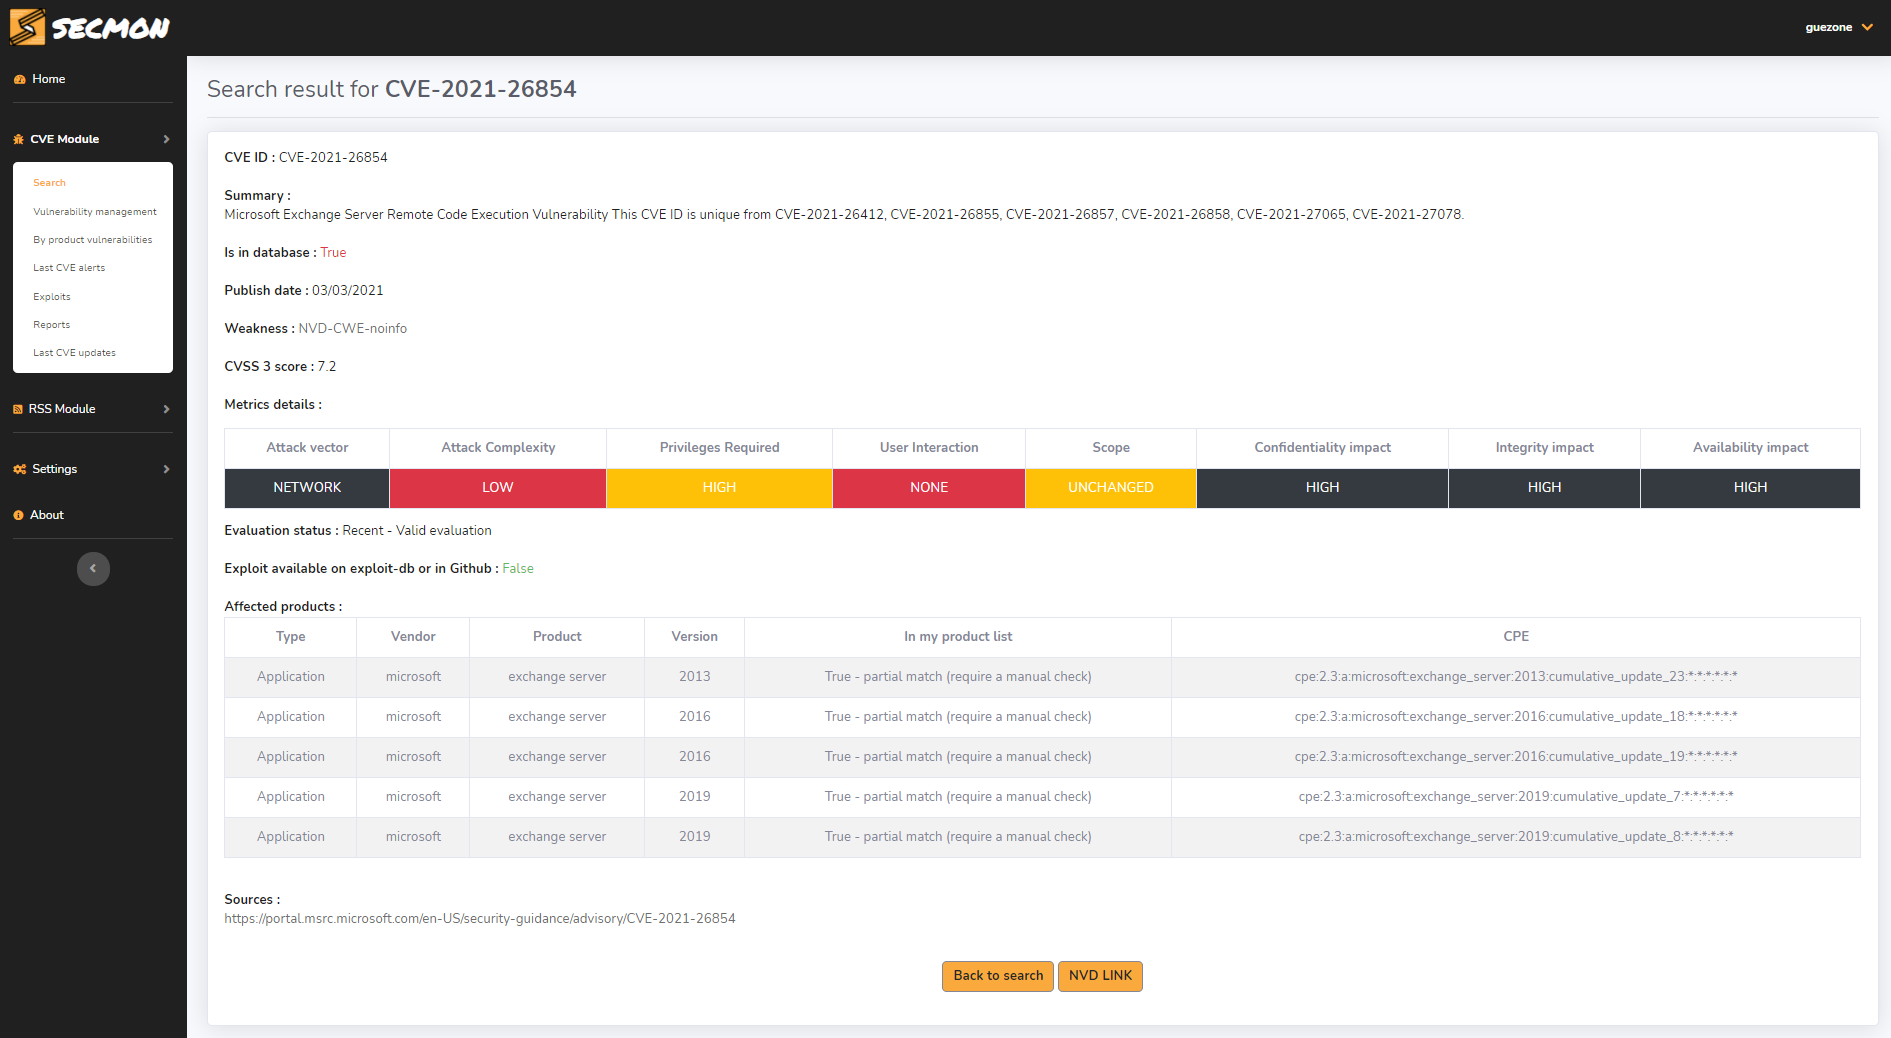
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.