

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
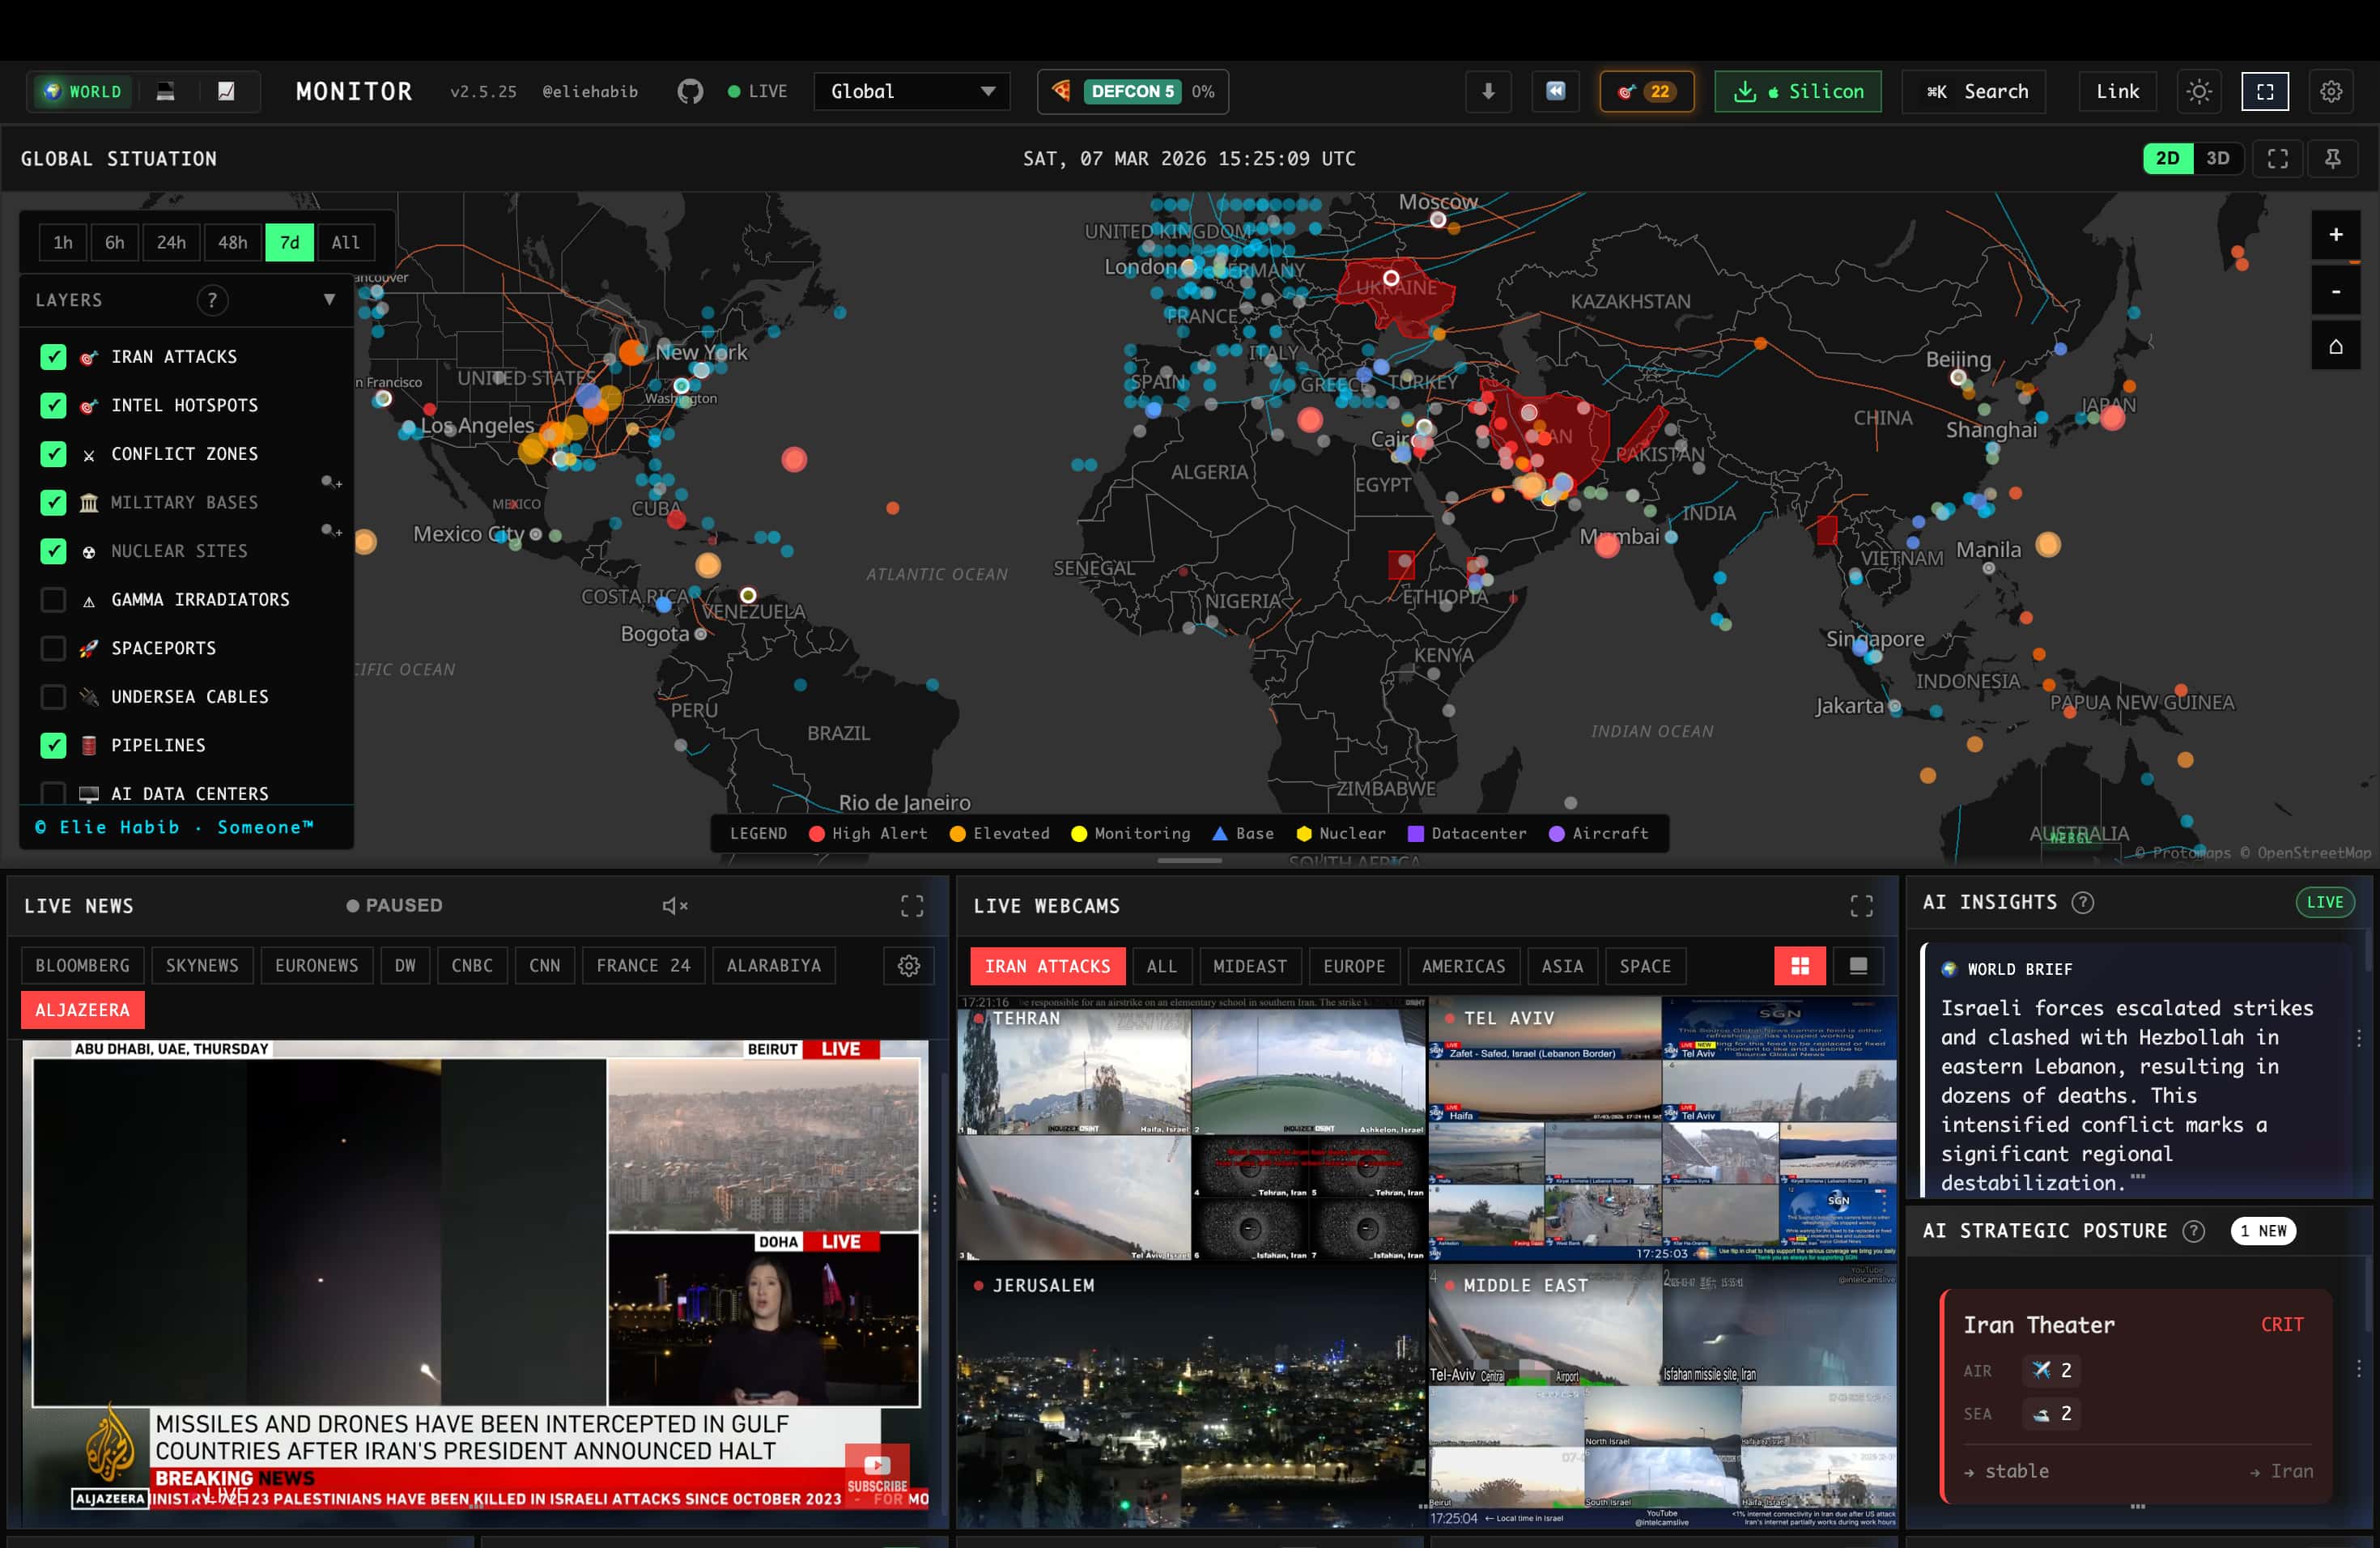 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…

 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 eclecticiq/opentaxii
TAXII server implementation in Python from EclecticIQ
 jangeisbauer/gundog
gundog - guided hunting in Microsoft Defender
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
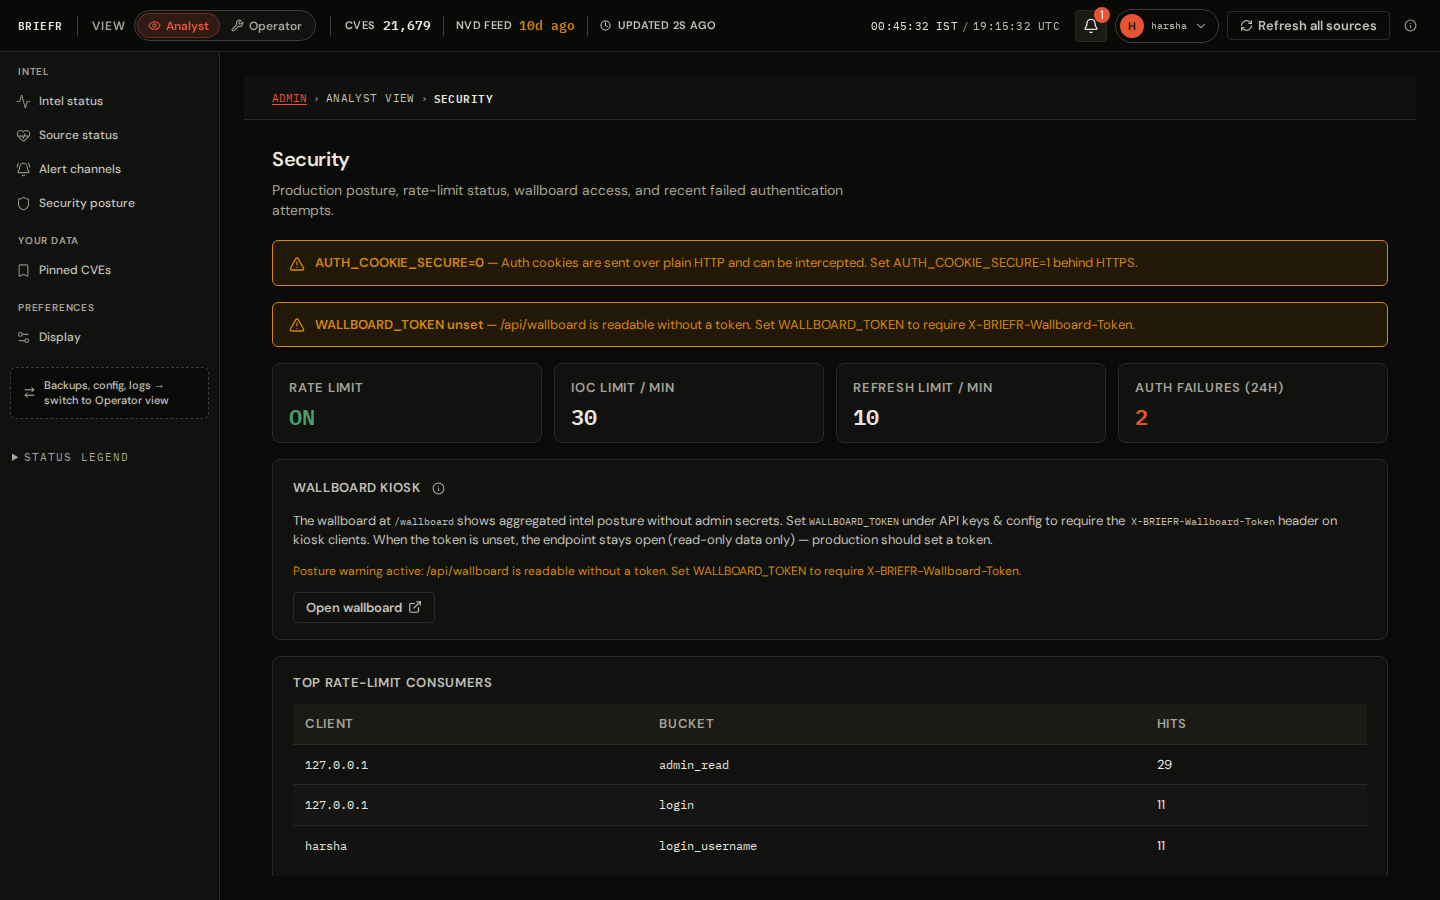 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 knqyf263/vuln-list-backup
Collects vulnerability and advisory data from multiple public security feeds and stores it in a parsable, structured format for downstream security…
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker

 phishdestroy/destroylist
Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats