 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and Flare.
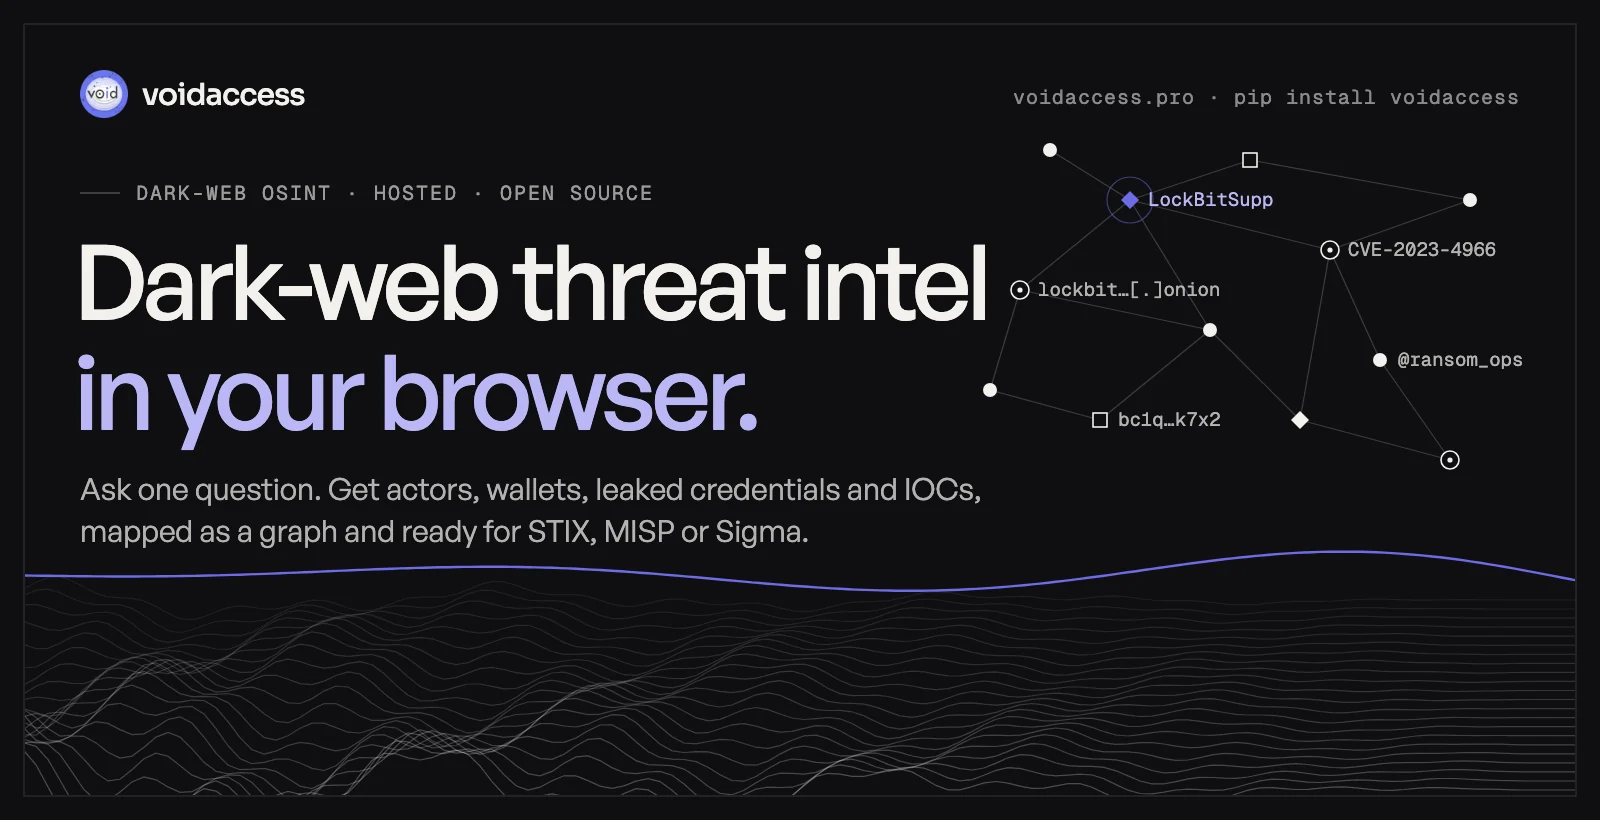


Ask one question. Get a sourced report, a graph you can search, and IOCs you can load.
For security researchers, threat-intel teams, MSSPs and authorized investigators.
Use it hosted → voidaccess.pro
·
Run it yourself → pip install voidaccess
The hosted version runs this engine for you. Searches and page fetches go out from our servers through Tor, so your research doesn't start from your laptop or office network. A live view shows every link found, kept or discarded (duplicates, 404s, timeouts, the safety filter), then the results open as a graph with every value searchable by category.
Start free at voidaccess.pro →
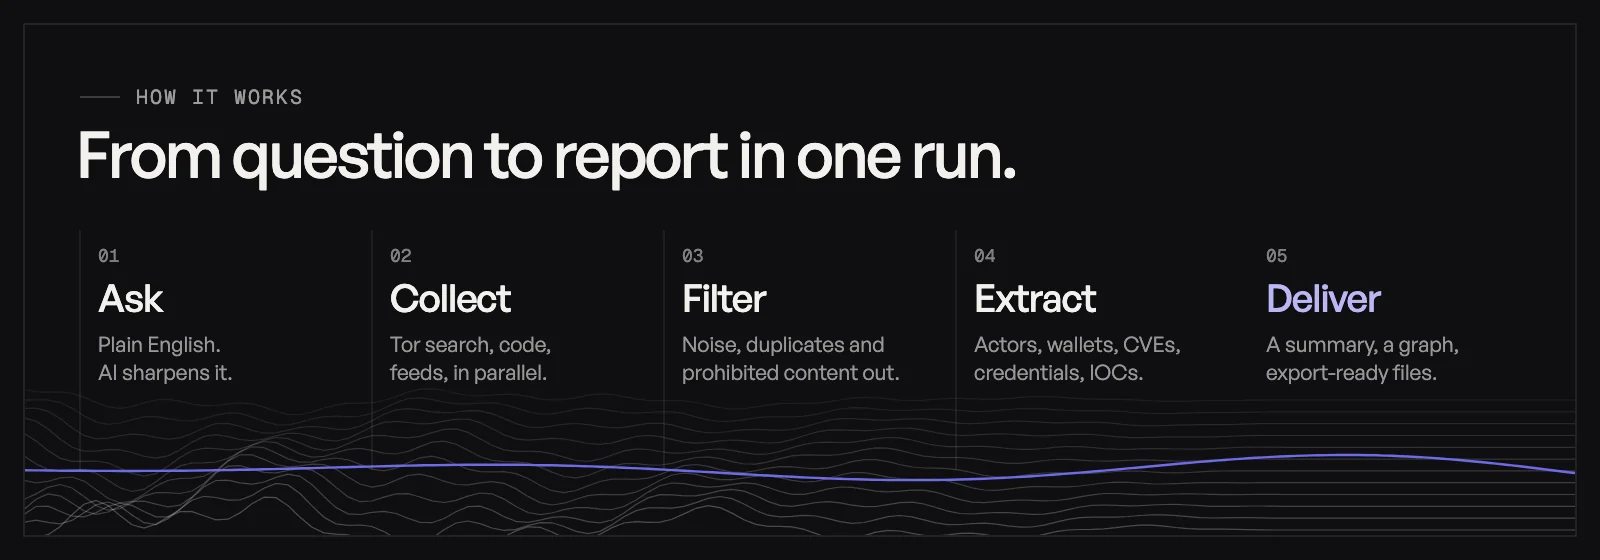
One query fans out in parallel to 12+ Tor search engines, code hosts, security feeds and curated .onion seeds, then follows new .onion links as it finds them. Prohibited queries, URLs and content are dropped at mandatory safety gates. The full pipeline, with timeouts and recovery, is in Architecture.
| Category | Examples |
|---|---|
| Threat actors | Actor handles, ransomware groups, malware families, MITRE ATT&CK techniques |
| Infrastructure | IPv4/IPv6, domains, URLs, .onion addresses, file hashes |
| Crypto wallets | Bitcoin, Ethereum, Monero, Litecoin, Zcash, Solana, Tron and more |
| Credentials | Cloud keys, tokens, JWTs, API keys, stealer-log and combo-list entries (masked) |
| Messaging | Telegram, Discord, XMPP, Tox, Session, Matrix, Wire, ICQ, Wickr |
| Vulnerabilities | CVEs, Exploit-DB IDs |
Entities are linked into a relationship graph with communities and infrastructure clusters, and cross-referenced against earlier findings.
pip install voidaccess
voidaccess configure                      # LLM provider, enrichment keys, Tor
voidaccess investigate "LockBit ransomware"
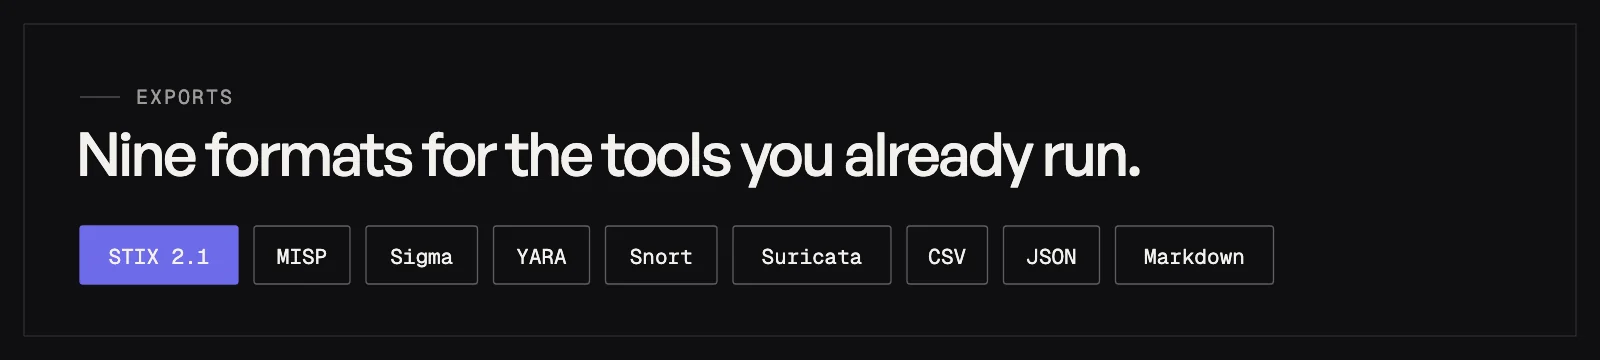
voidaccess export <id> --format stix     # stix, misp, sigma, yara, snort, suricata, package, csv, md, json
No Tor or LLM key yet? voidaccess investigate "LockBit ransomware" --no-llm --no-tor --depth shallow runs a clearnet-only pass. For the full stack (PostgreSQL, Tor, API and web UI) with Docker Compose, see the self-hosting guide. Python 3.10+.
| Command | Description |
|---|---|
voidaccess investigate "QUERY" | Run an investigation |
voidaccess show | Open the interactive entity browser |
voidaccess export ID --format FORMAT | Export as STIX, MISP, Sigma, YARA, Snort, Suricata, package, CSV, Markdown or JSON |
voidaccess package ID | Build an IOC package ZIP |
voidaccess enrich ID | Re-enrich a saved investigation |
voidaccess list | List saved investigations |
voidaccess status | Show configuration, Tor, cache, engine and seed status |
voidaccess actors | List persistent actor profiles |
voidaccess actor HANDLE [--timeline] [--note "TEXT"] | Show an actor, its timeline, or add a note |
voidaccess configure [llm | keys | tor] | Run the setup wizard, or one part of it |
voidaccess version | Print the installed version |
Optional clearnet requests can use ScrapingAnt with --use-scraping-api or --use-proxies; Tor, .onion, GitHub and GitLab traffic are unaffected.
| Layer | Sources |
|---|---|
| Dark-web search | 12+ Tor search engines and curated .onion seeds |
| Open-web collection | Paste sites, GitHub, GitLab and curated RSS feeds |
| Threat feeds | AlienVault OTX, abuse.ch (MalwareBazaar, ThreatFox, URLhaus), CISA KEV |
| IP and domain context | Shodan InternetDB, GreyNoise, AbuseIPDB, Feodo Tracker, crt.sh, URLScan.io, Wayback Machine, CIRCL PDNS, RDAP |
| File and identity context | VirusTotal, Hybrid Analysis, Have I Been Pwned, EmailRep |
| Blockchain | BlockCypher and Etherscan |
Sources that need an API key are skipped cleanly without one. The hosted version uses a subset whose terms allow it. Full configuration: Architecture. For full sentence-transformer embeddings, pip install "voidaccess[nlp]"; without it, a deterministic fallback encoder is used.








