

cli
 vulncheck-oss/cli
VulnCheck's official command line tool
api-securitydns-analysisinformation-gathering+8
vulncheck-oss/cliVulnCheck's official command line tool
 m4nbat/100_days_of_kql_2026
A repo to hold KQL queries as part of my 100 days of KQL effort.
 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 paloaltonetworks/unit42-timely-threat-intel
A collection of files with indicators supporting social media posts from Palo Alto Network's Unit 42 team to disseminate timely threat intelligence.
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
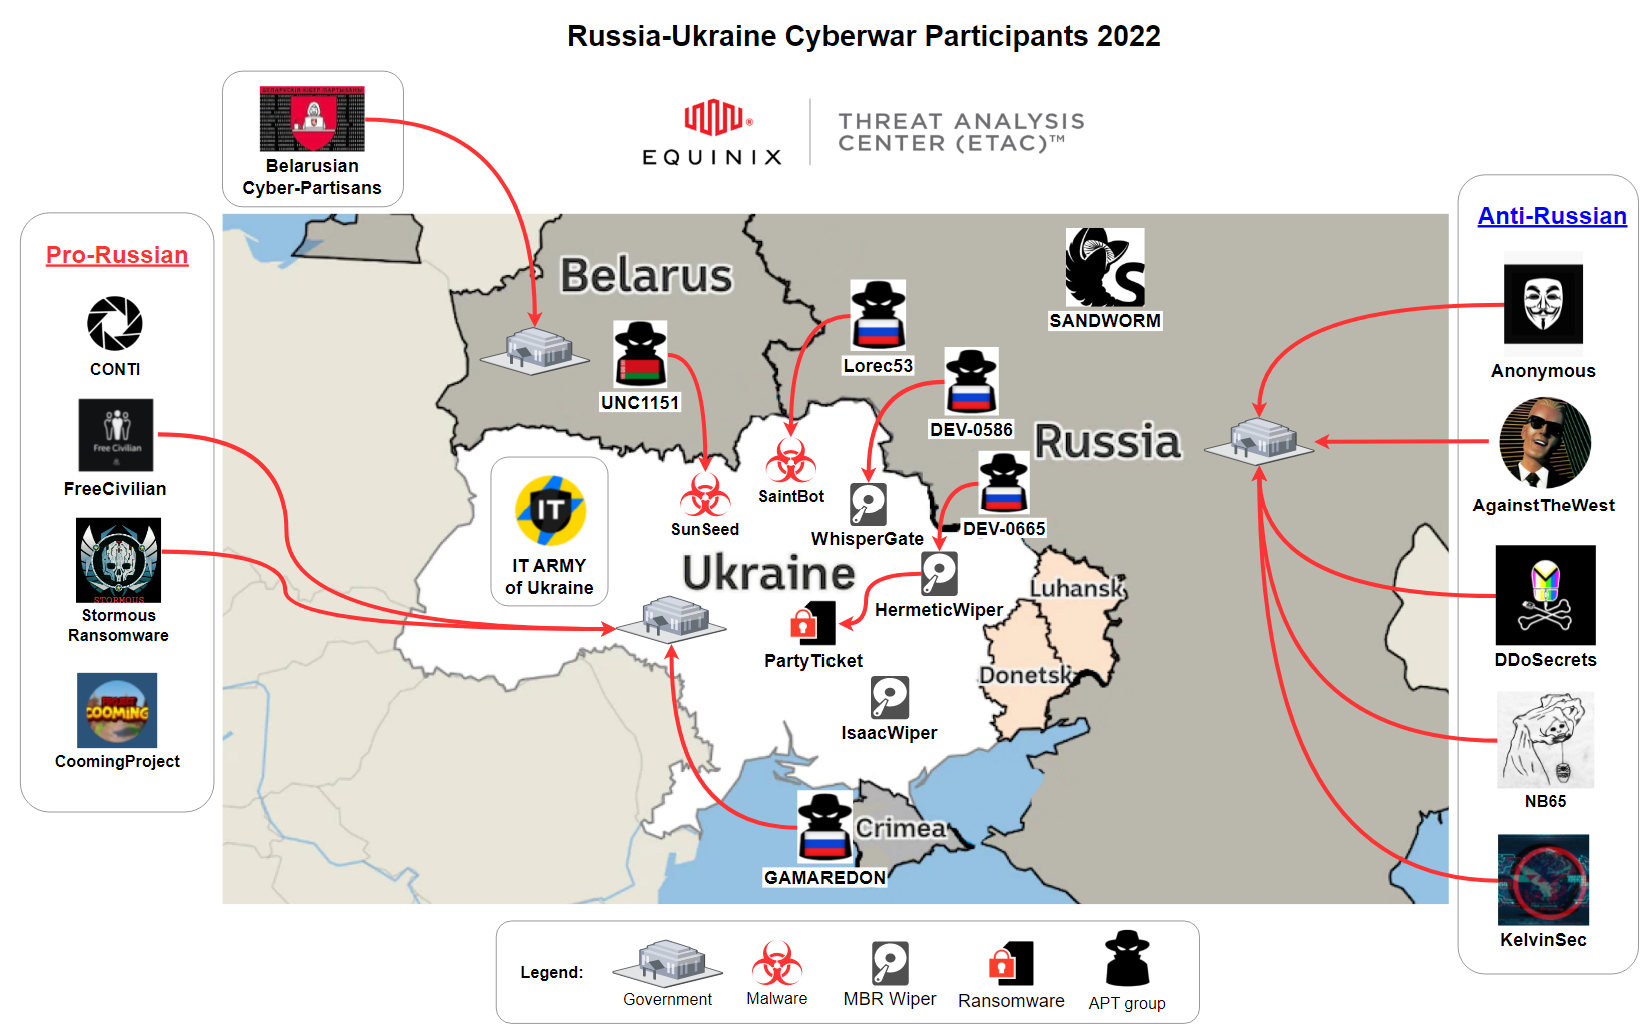 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 olafhartong/threathunting
A Splunk app mapped to MITRE ATT&CK to guide your threat hunts
 olafhartong/attackdatamap
A datasource assessment on an event level to show potential coverage or the MITRE ATT&CK framework