


 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
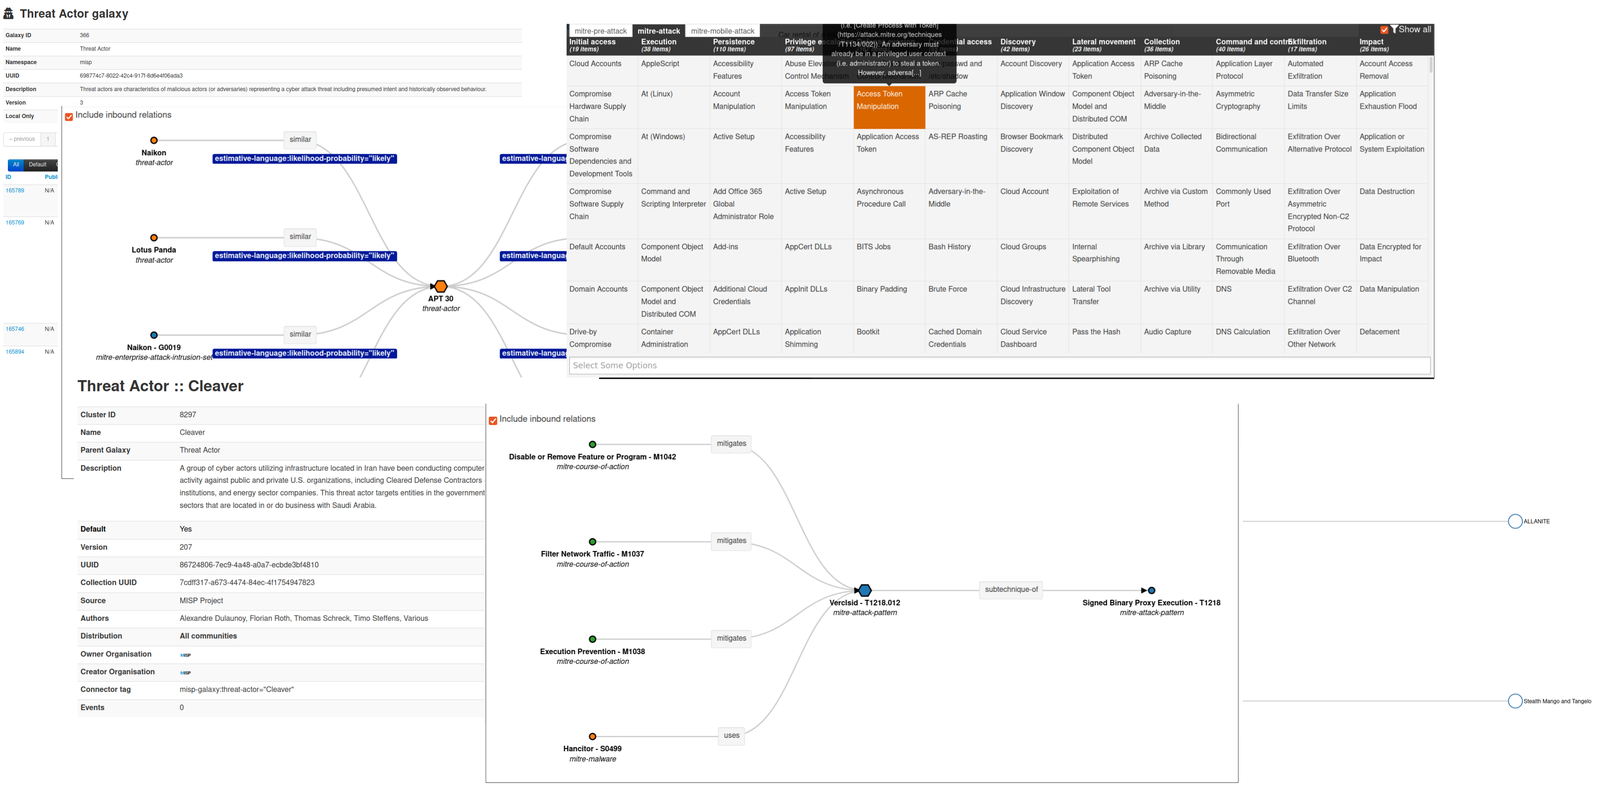 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 gendigitalinc/ioc
Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 ninoseki/mihari
A query aggregator for OSINT based threat hunting
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
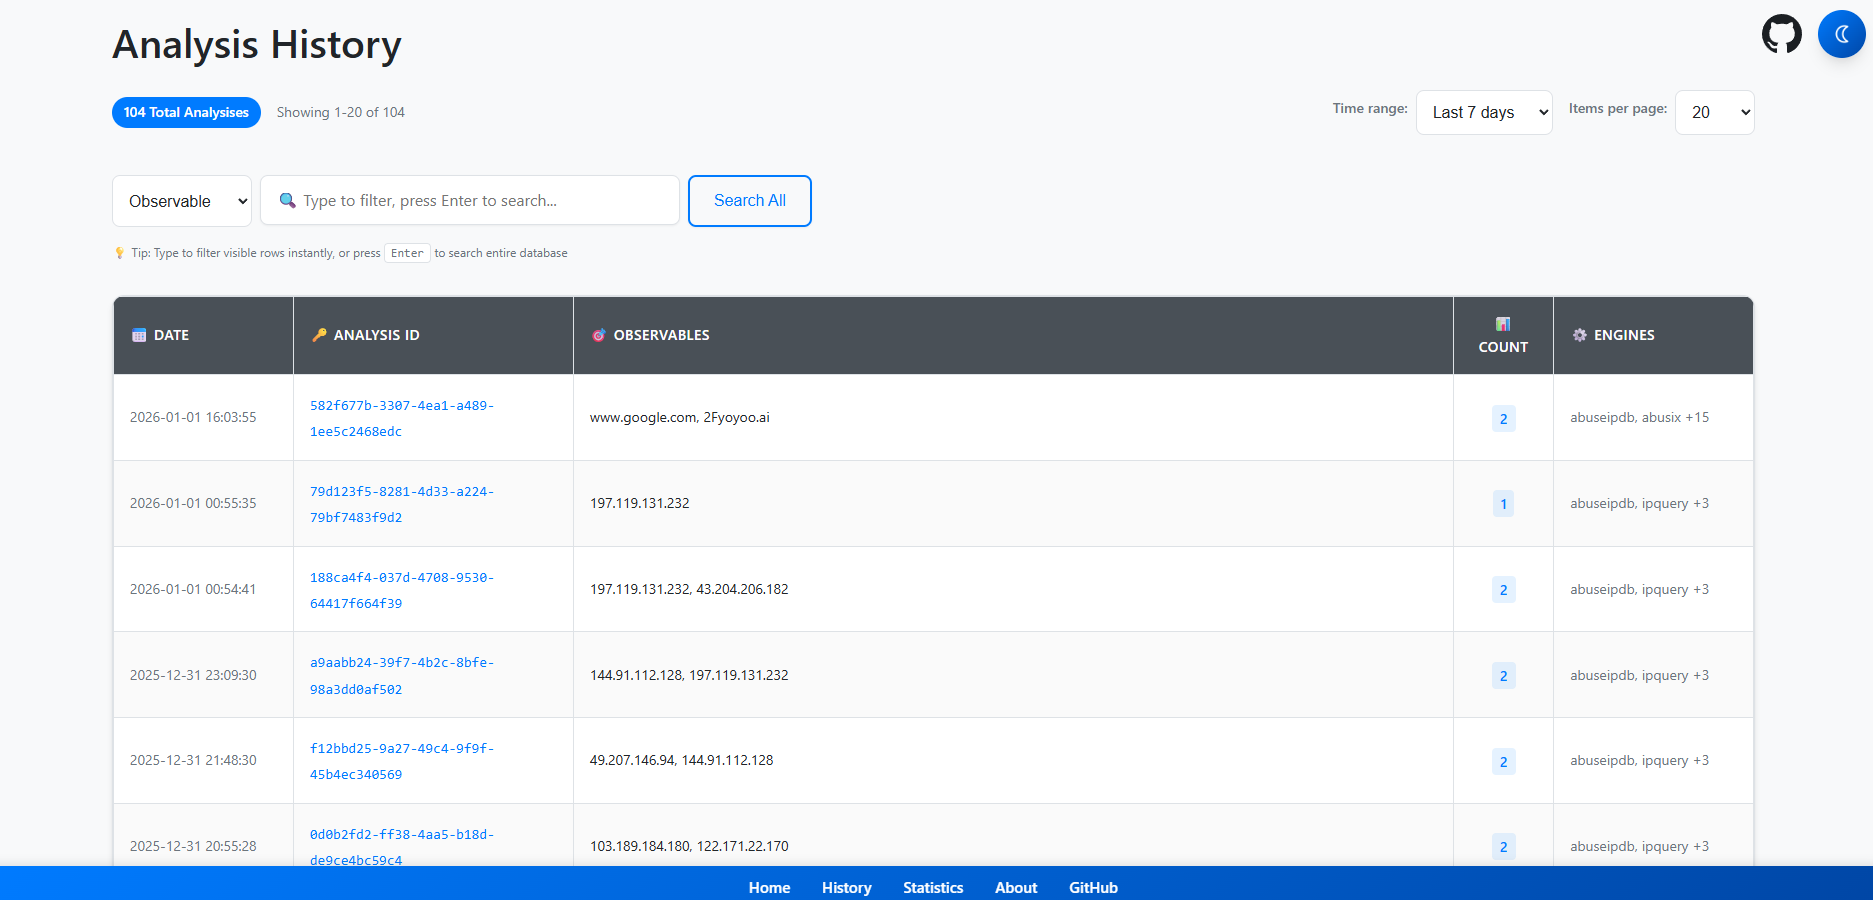 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
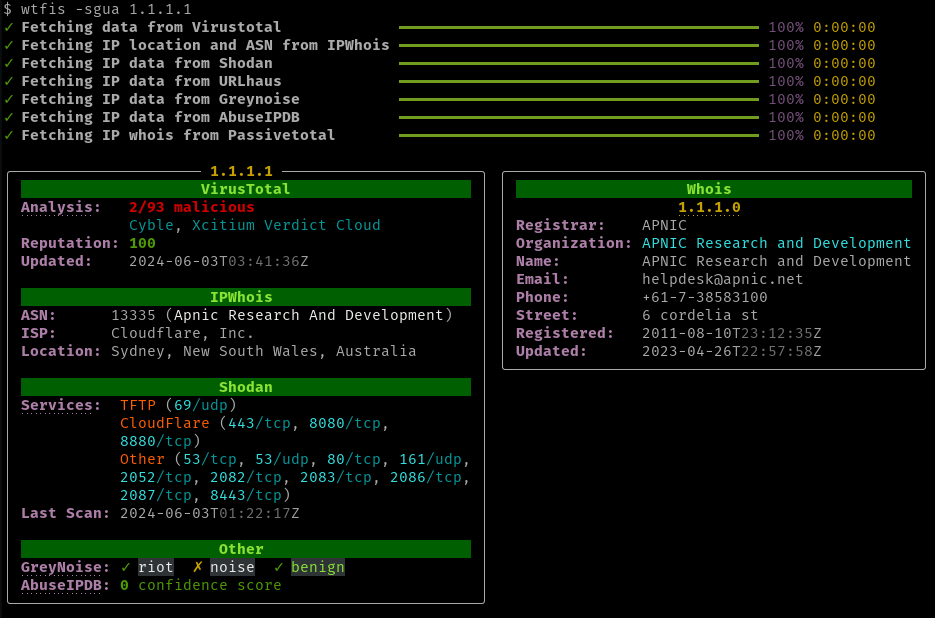 pirxthepilot/wtfis
Passive hostname, domain and IP lookup tool for non-robots
 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 stamusnetworks/scirius
Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 toborrm9/malicious_extension_sentry
Malicious Extension Database