
worldmonitor
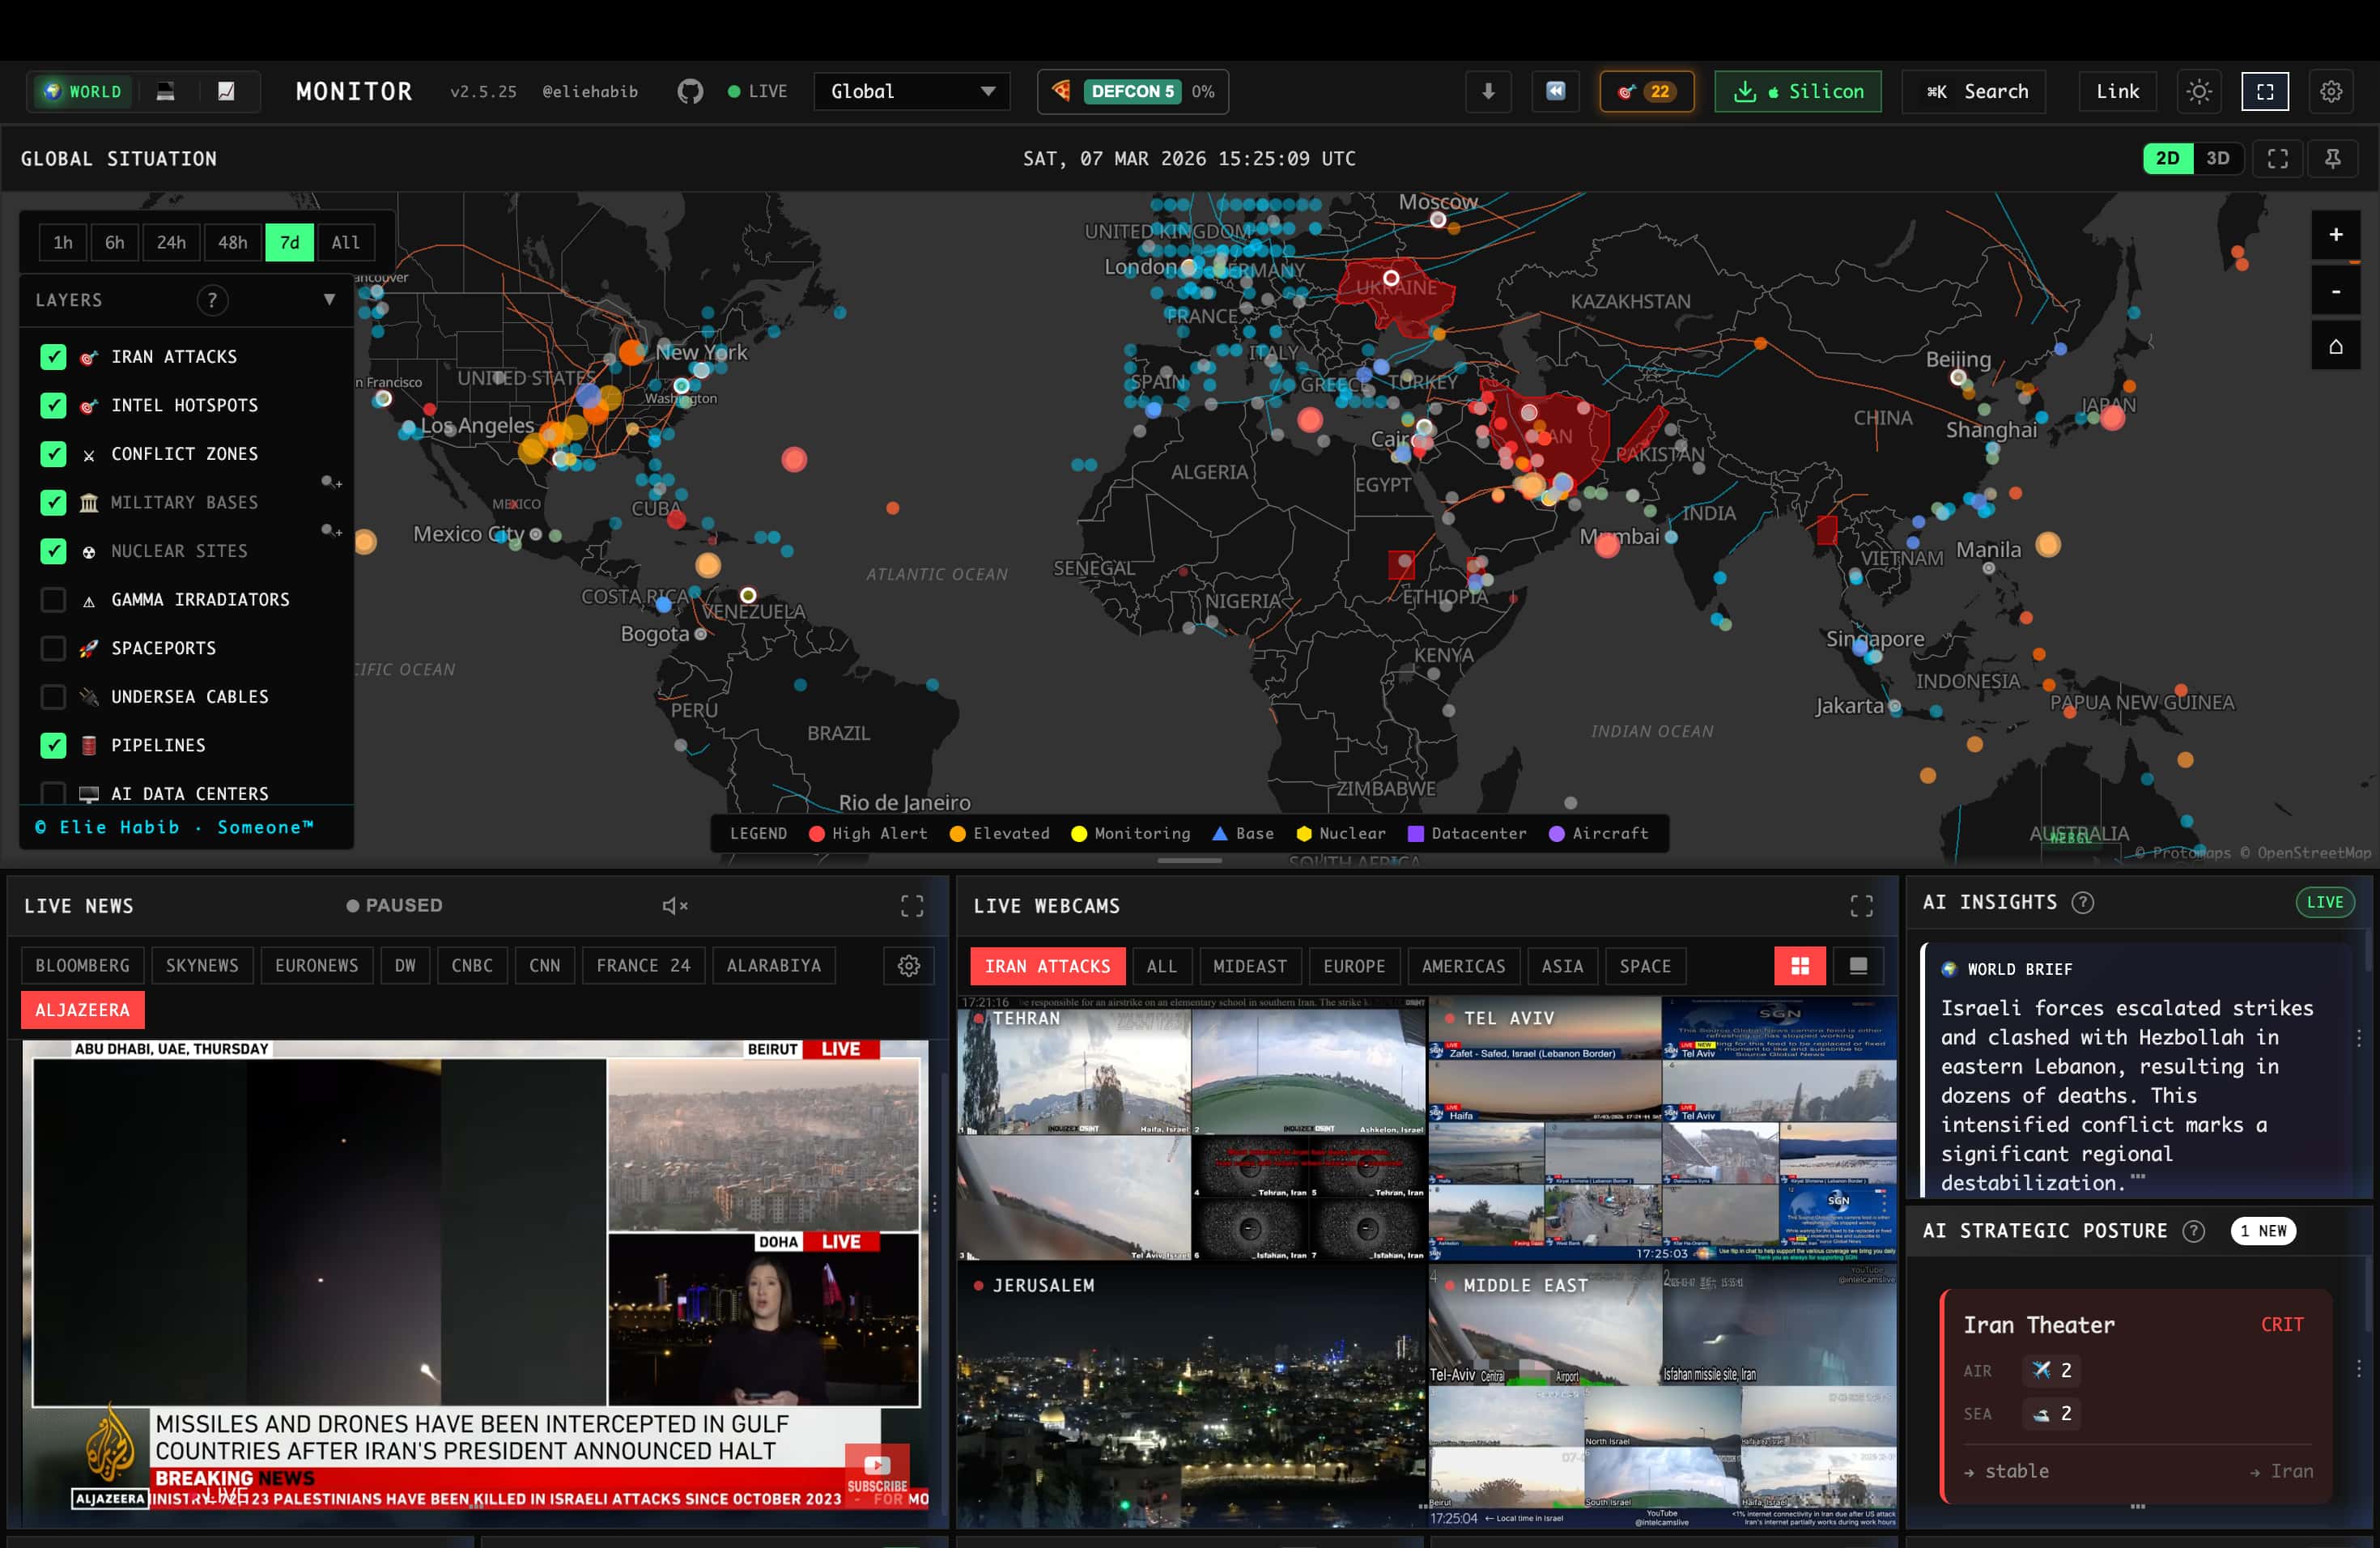
 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
ai-securitycrawlerdns-analysis+7
89.2k
koala73/worldmonitorReal-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 vulncheck-oss/cli
VulnCheck's official command line tool
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
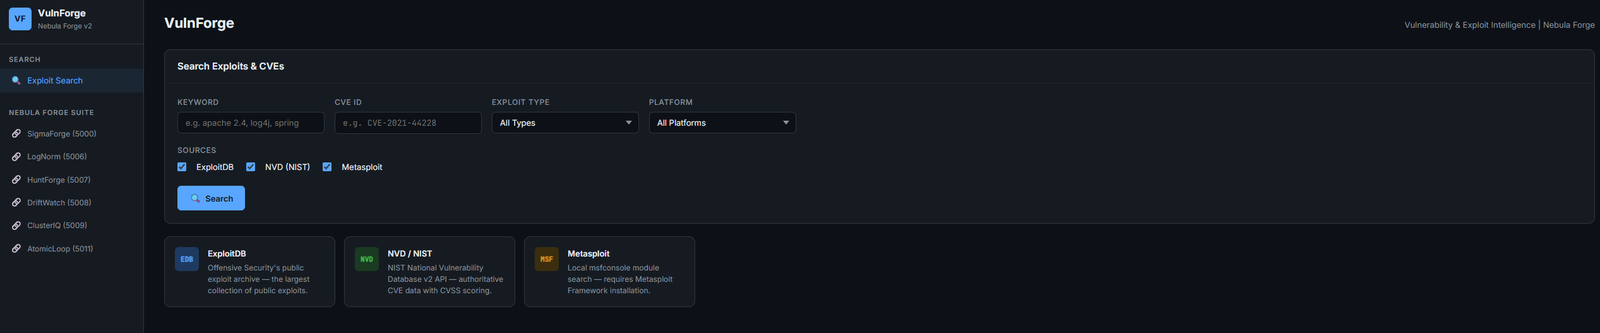 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…