
ifuncd-up
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
binary-analysisdynamic-code-analysiseducation+5
robertdfrench/ifuncd-upGNU IFUNC is the real culprit behind CVE-2024-3094
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 gouldnicholas/cve-2026-7669-poc
PoC for CVE-2026-7669: SGLang silent trust_remote_code override -> RCE
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 doyensec/malicious-devfile-registry
CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 zerbaliy3v/cve-2018-6574-exploit
CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…
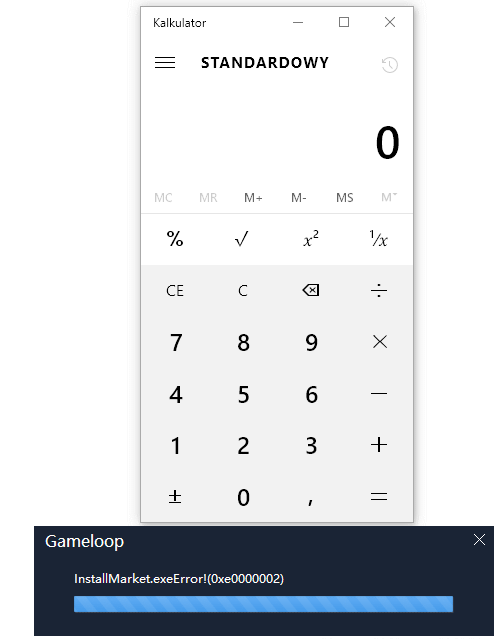 mmiszczyk/cve-2021-33879
GameLoop update MITM
 bfengj/cve-2024-32002-exploit
Proof-of-concept exploit for CVE-2024-32002, a Git submodule vulnerability enabling arbitrary code execution via crafted repositories and symlinks.
 theth1nk3r/cve-2020-27955
cve-2020-27955
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.

 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…
 astaruf/cve-2026-44590
Proof-of-concept exploit for CVE-2026-44590, a command injection in Sherlock's GitHub Actions workflow enabling RCE and GITHUB_TOKEN exfiltration via…
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…