
Log4JShell-Bytecode-Detector
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
binary-analysiscode-analysisincident-response+3
49
codeshield-security/log4jshell-bytecode-detectorLocal Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
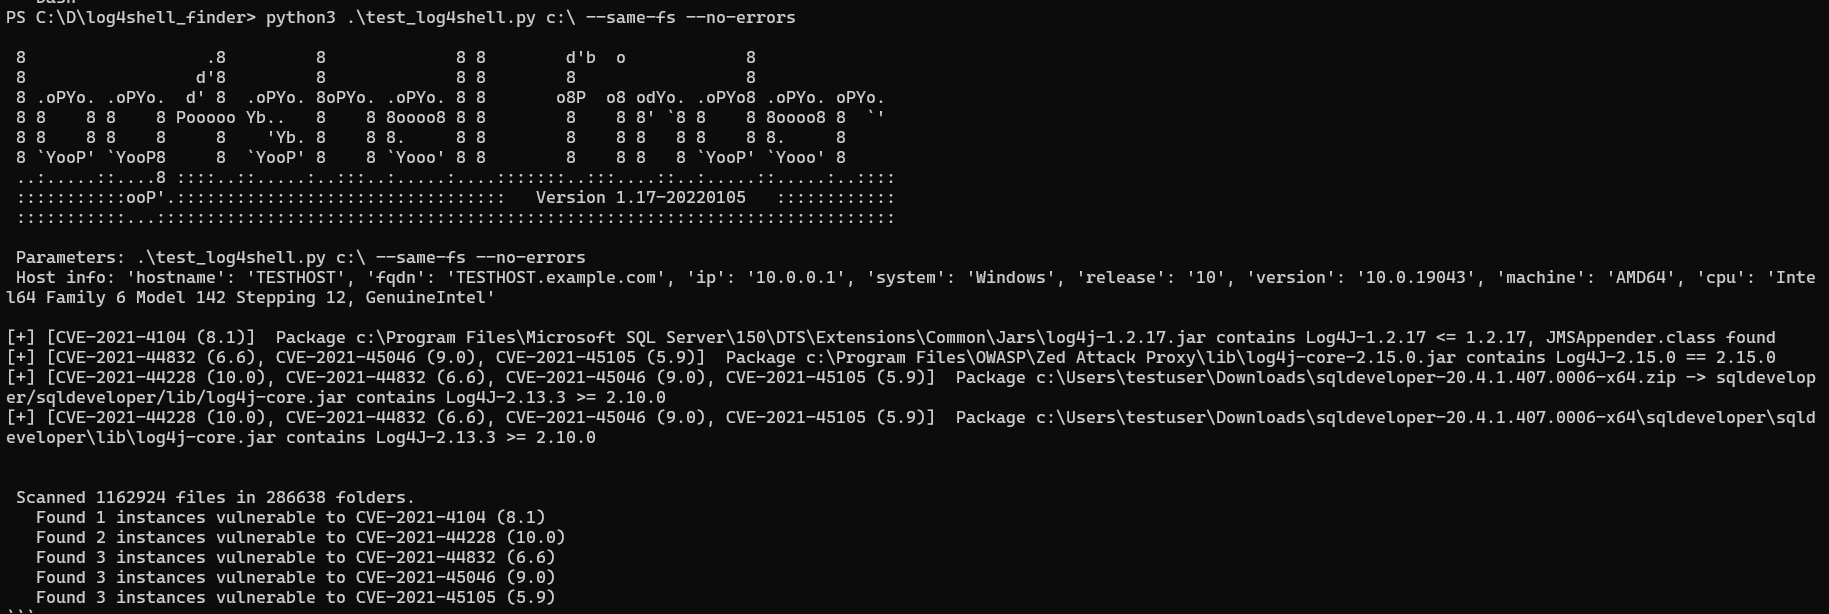 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 mhaggis/package-inferno
A Public Package Scanner for The Community
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 anchore/grype
A vulnerability scanner for container images and filesystems
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 snyk/agent-scan
Security scanner for AI agents, MCP servers and agent skills.
 cisco-ai-defense/skill-scanner
Security Scanner for Agent Skills
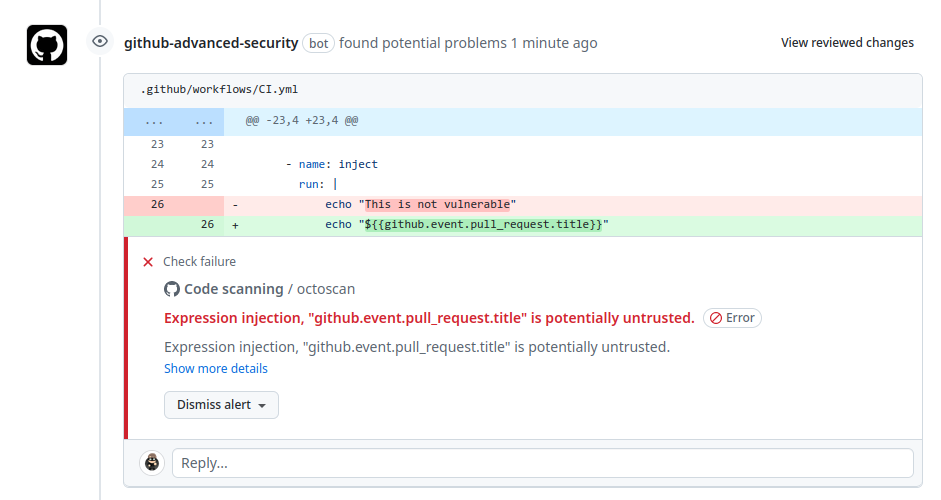 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
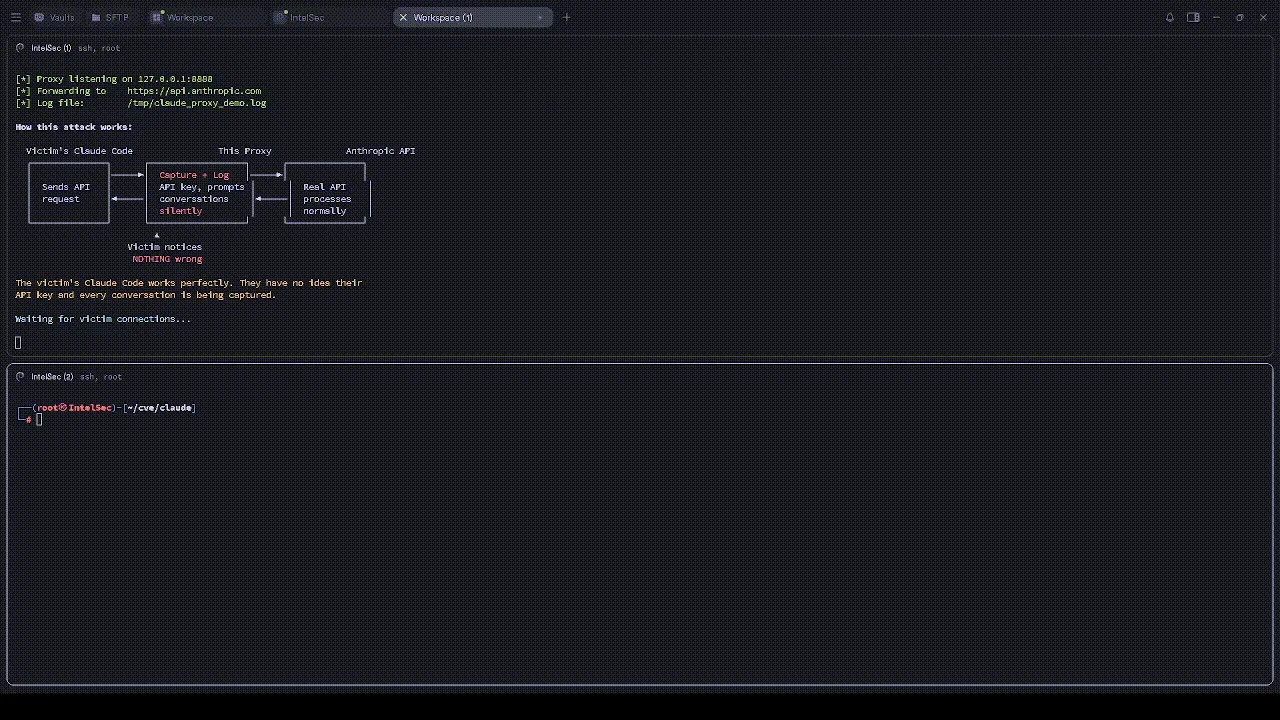 atiilla/cve-2026-21852-poc
Educational demo of three Claude Code vulnerabilities (hooks bypass, MCP injection, API key exfiltration) with attacker server, MITM proxy, and…
 knqyf263/remic
Vulnerability Scanner for Detecting Publicly Disclosed Vulnerabilities in Application Dependencies
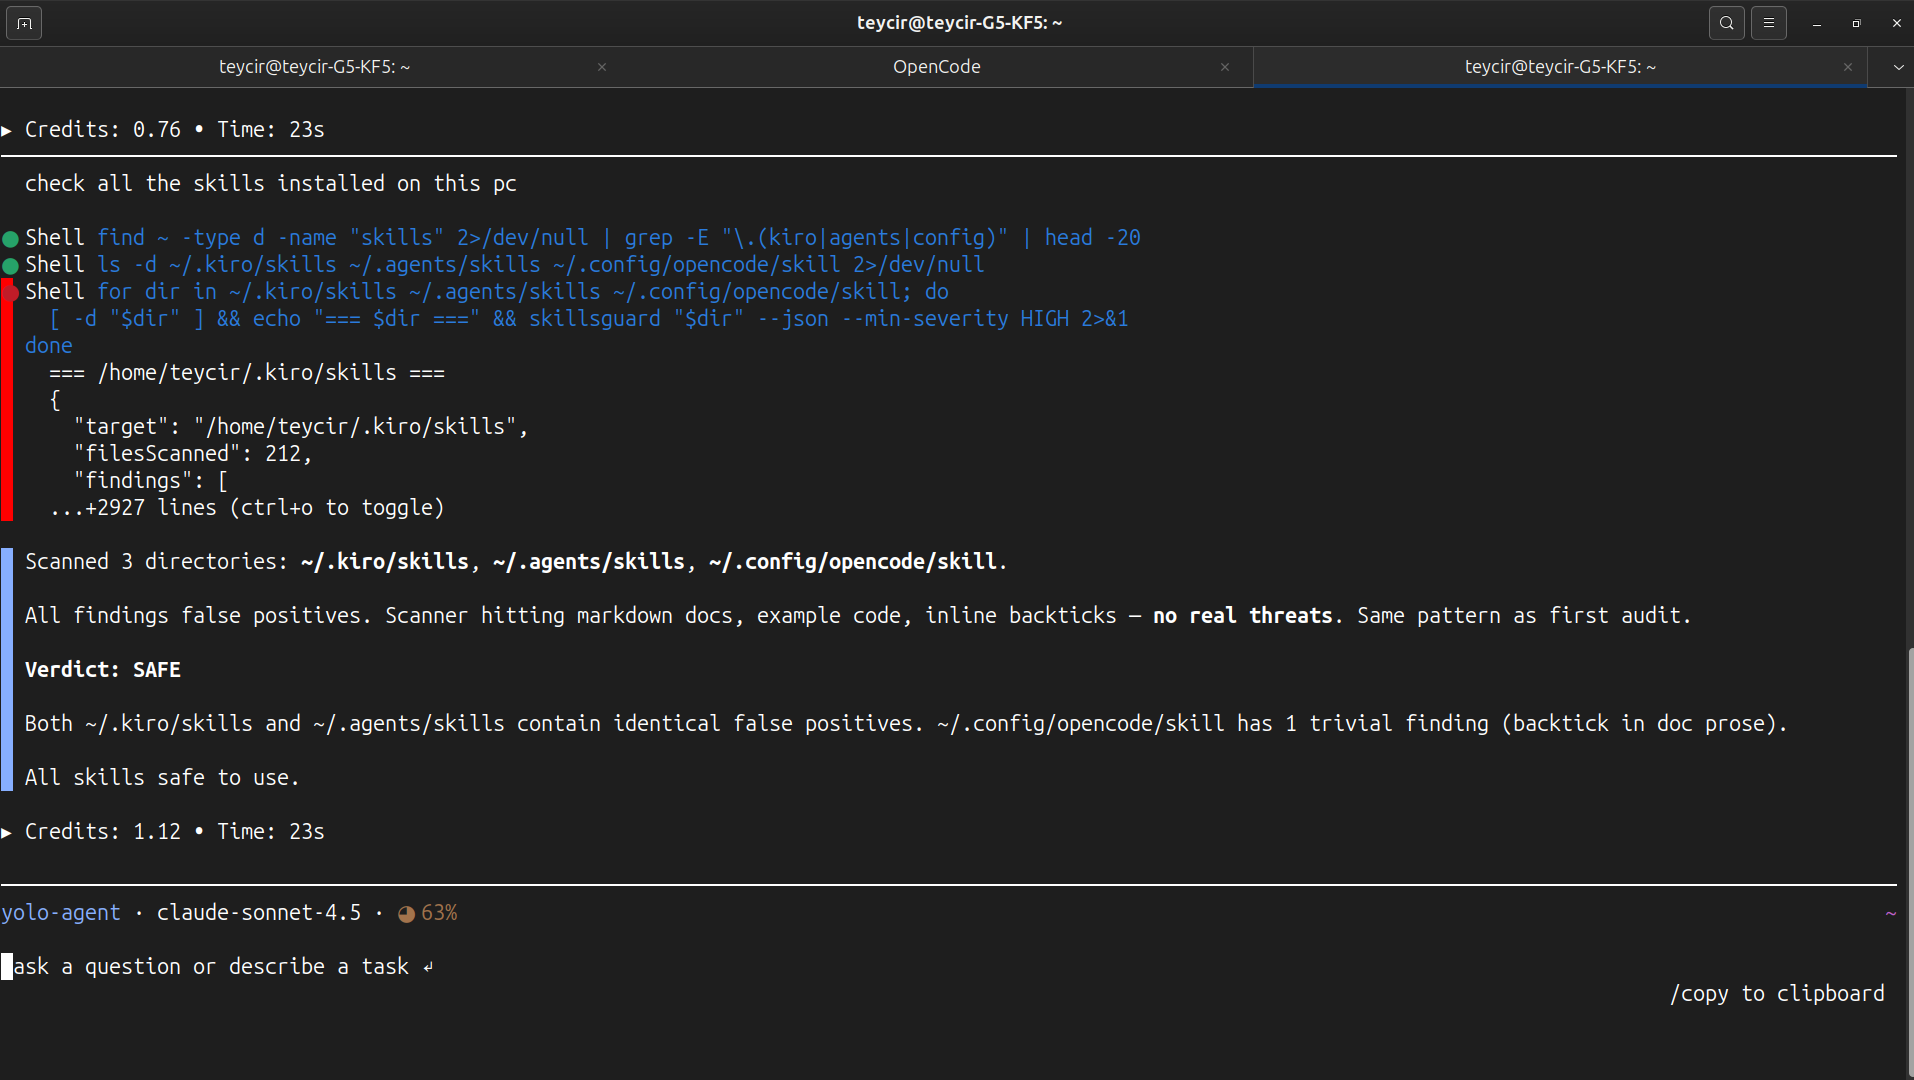 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…