
CVE-2026-5817-PoC
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
ai-securitycontainer-escapecontainer-security+4
gouldnicholas/cve-2026-5817-pocDocker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 kavin71725/cve-2025-12543-fix-for-wildfly
Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…
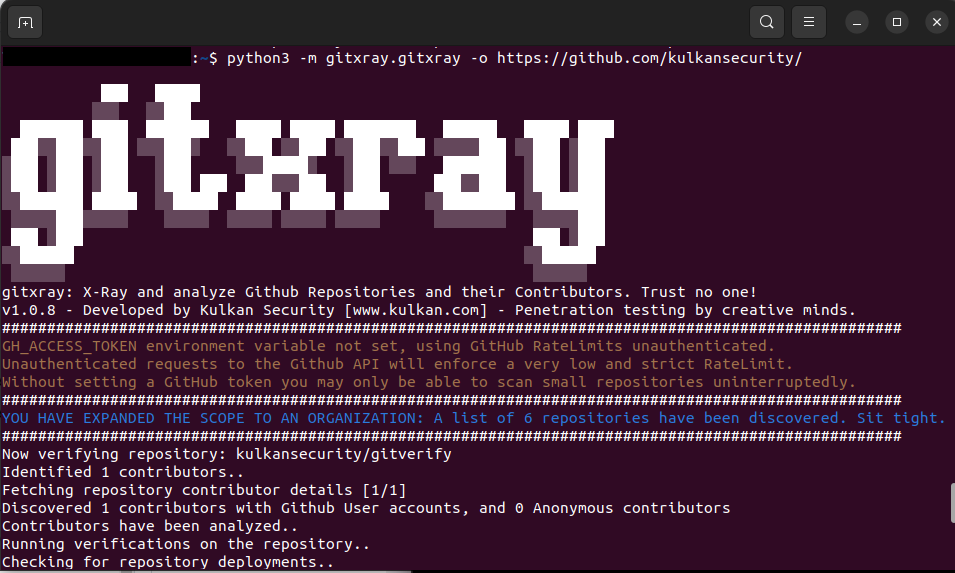 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
 owasp/docker-security
Getting a handle on container security
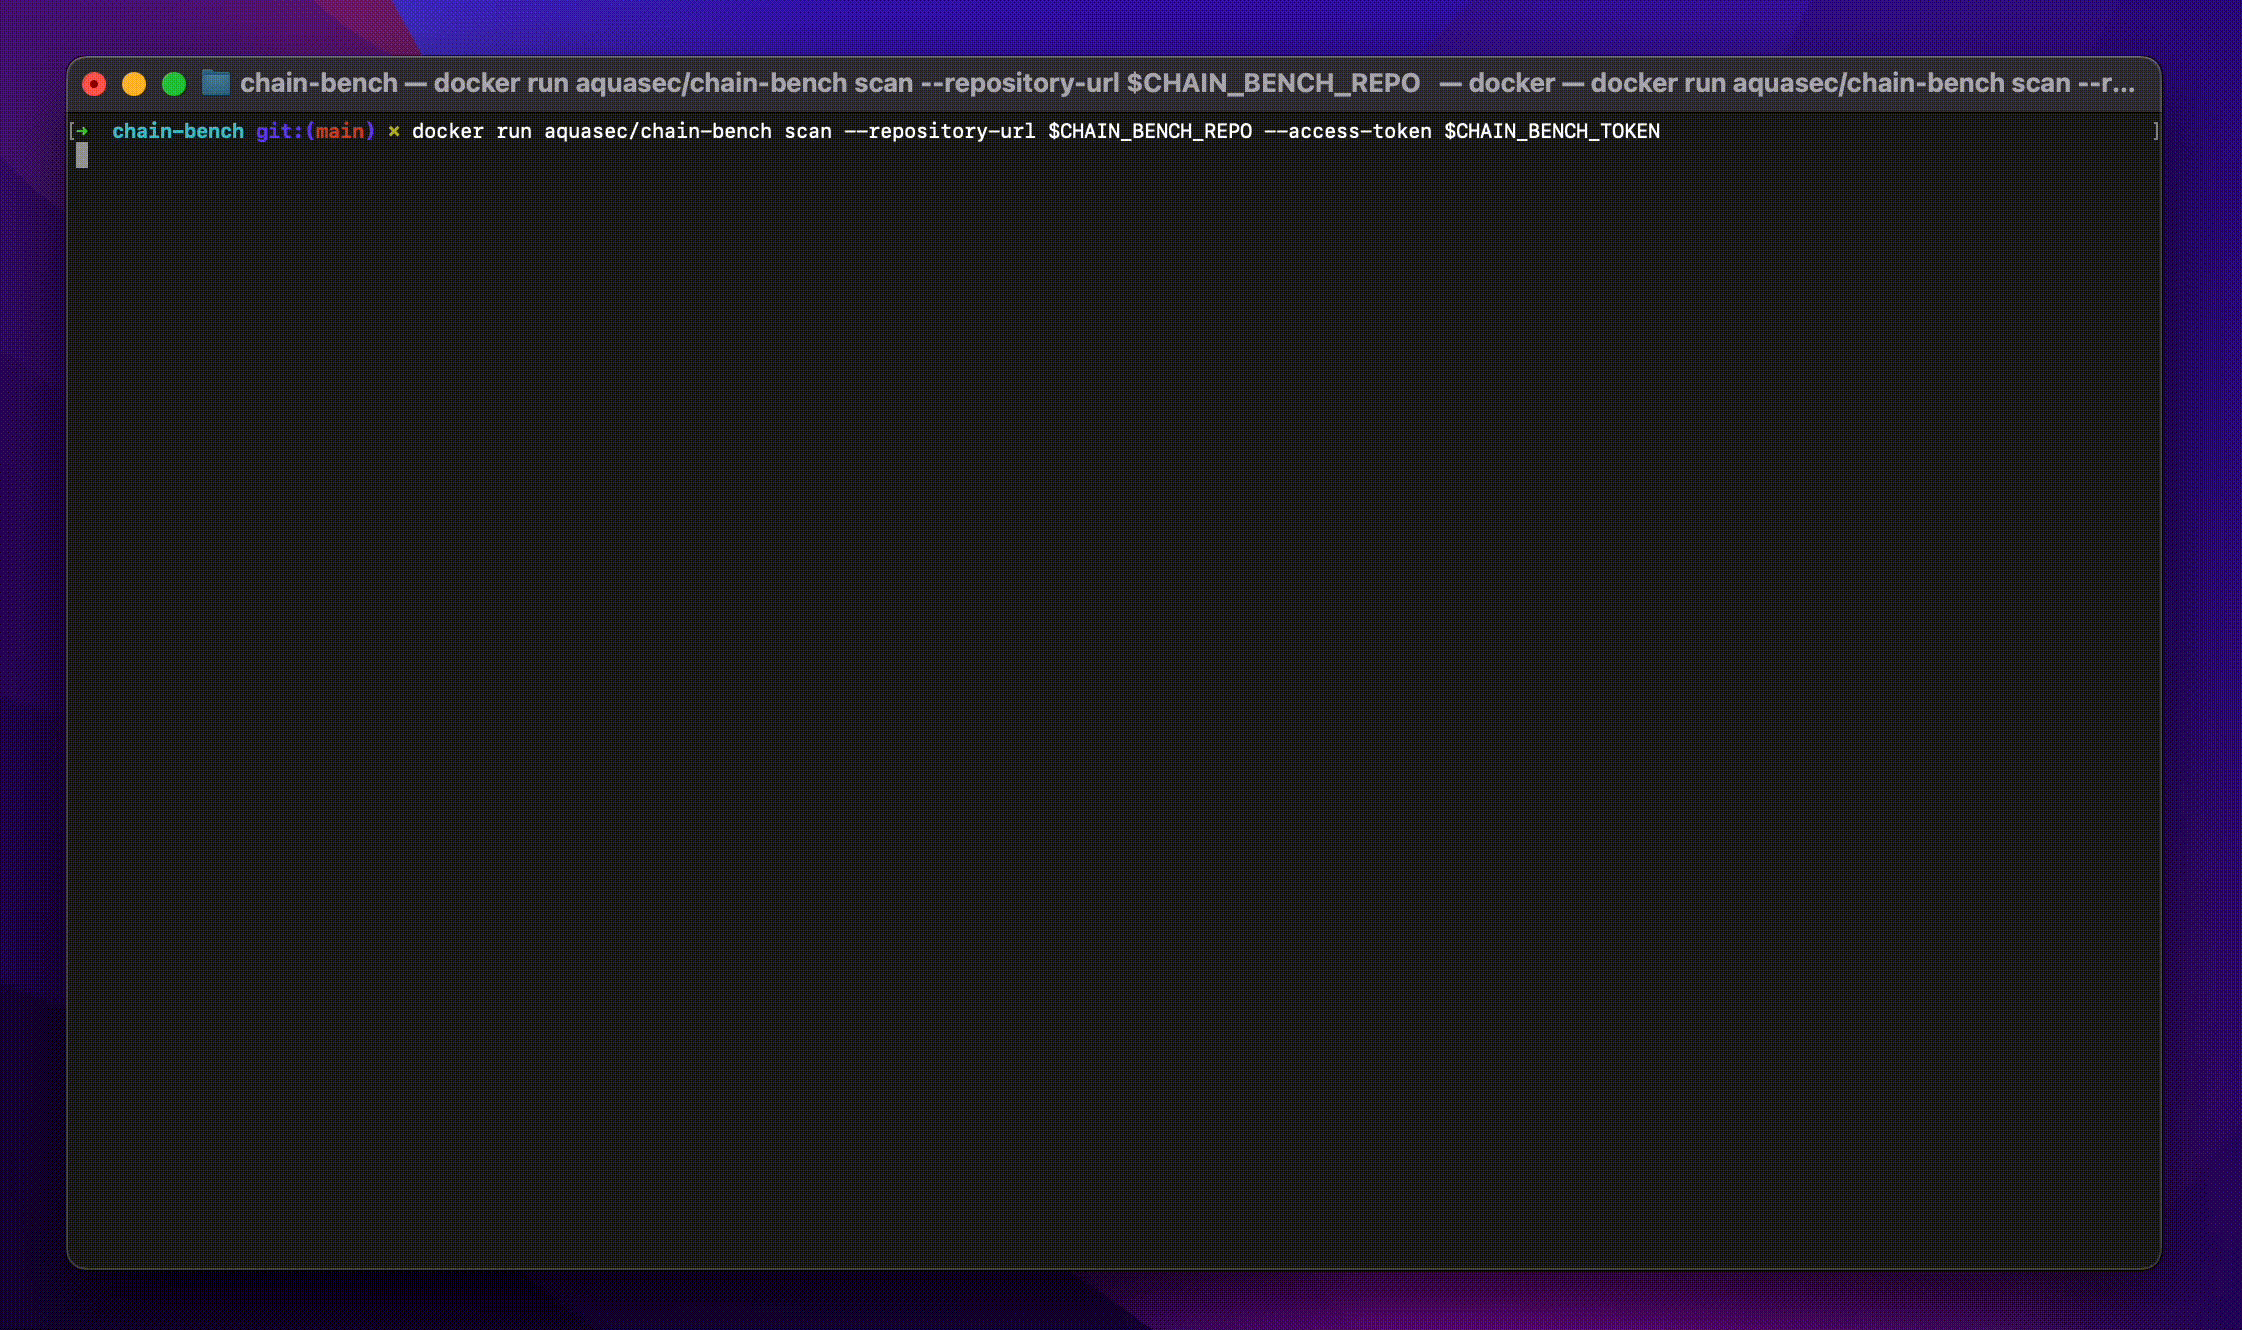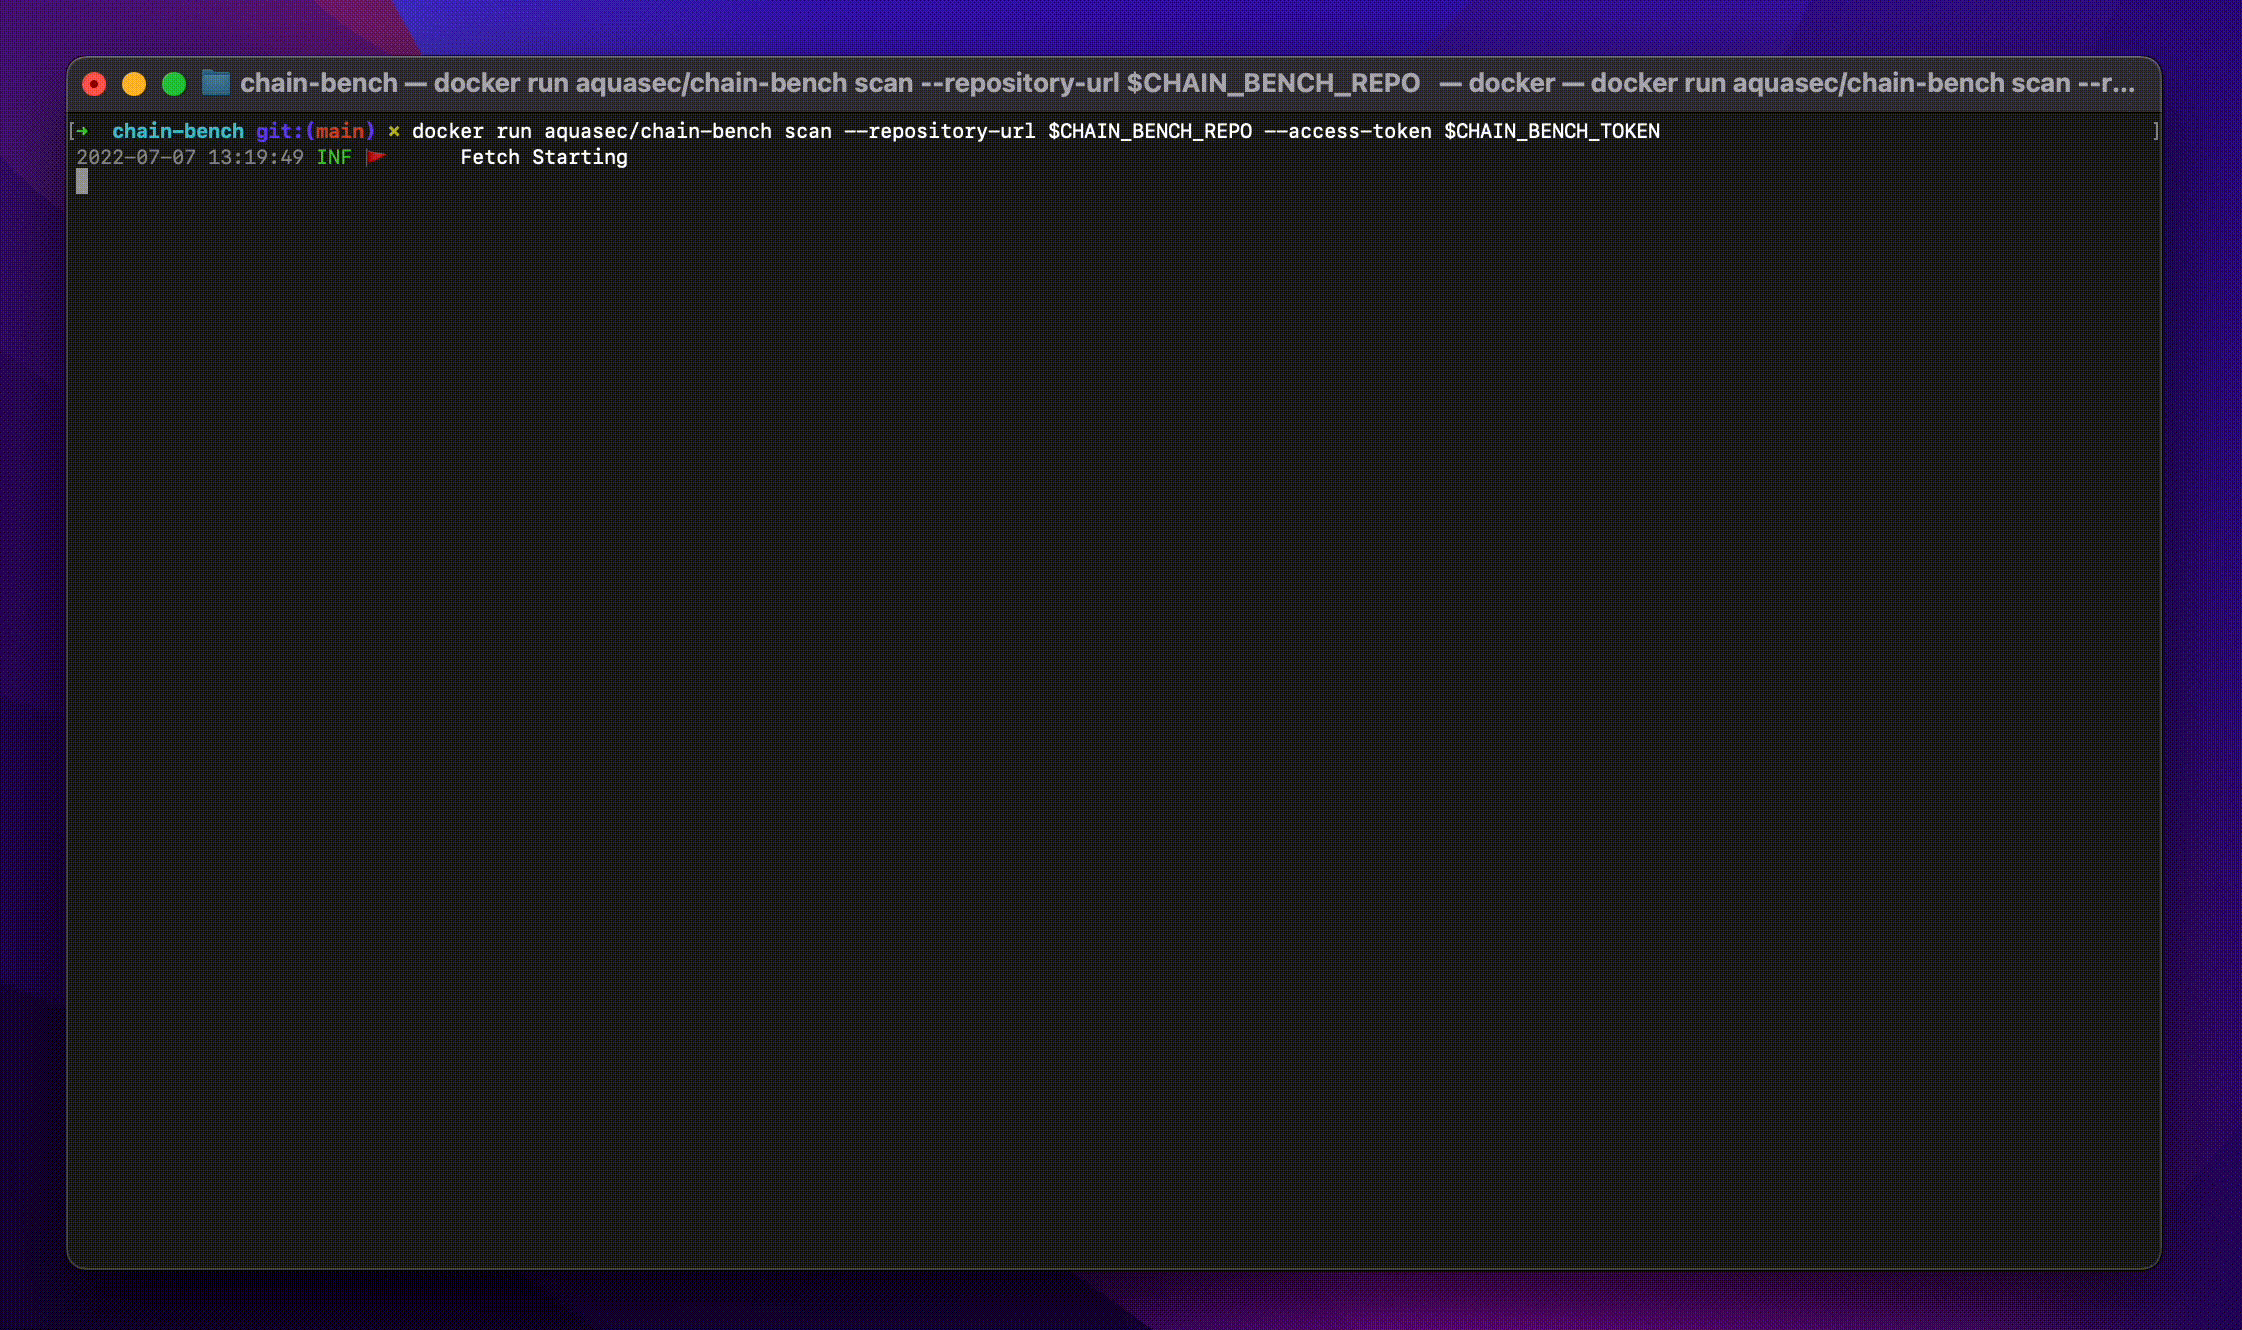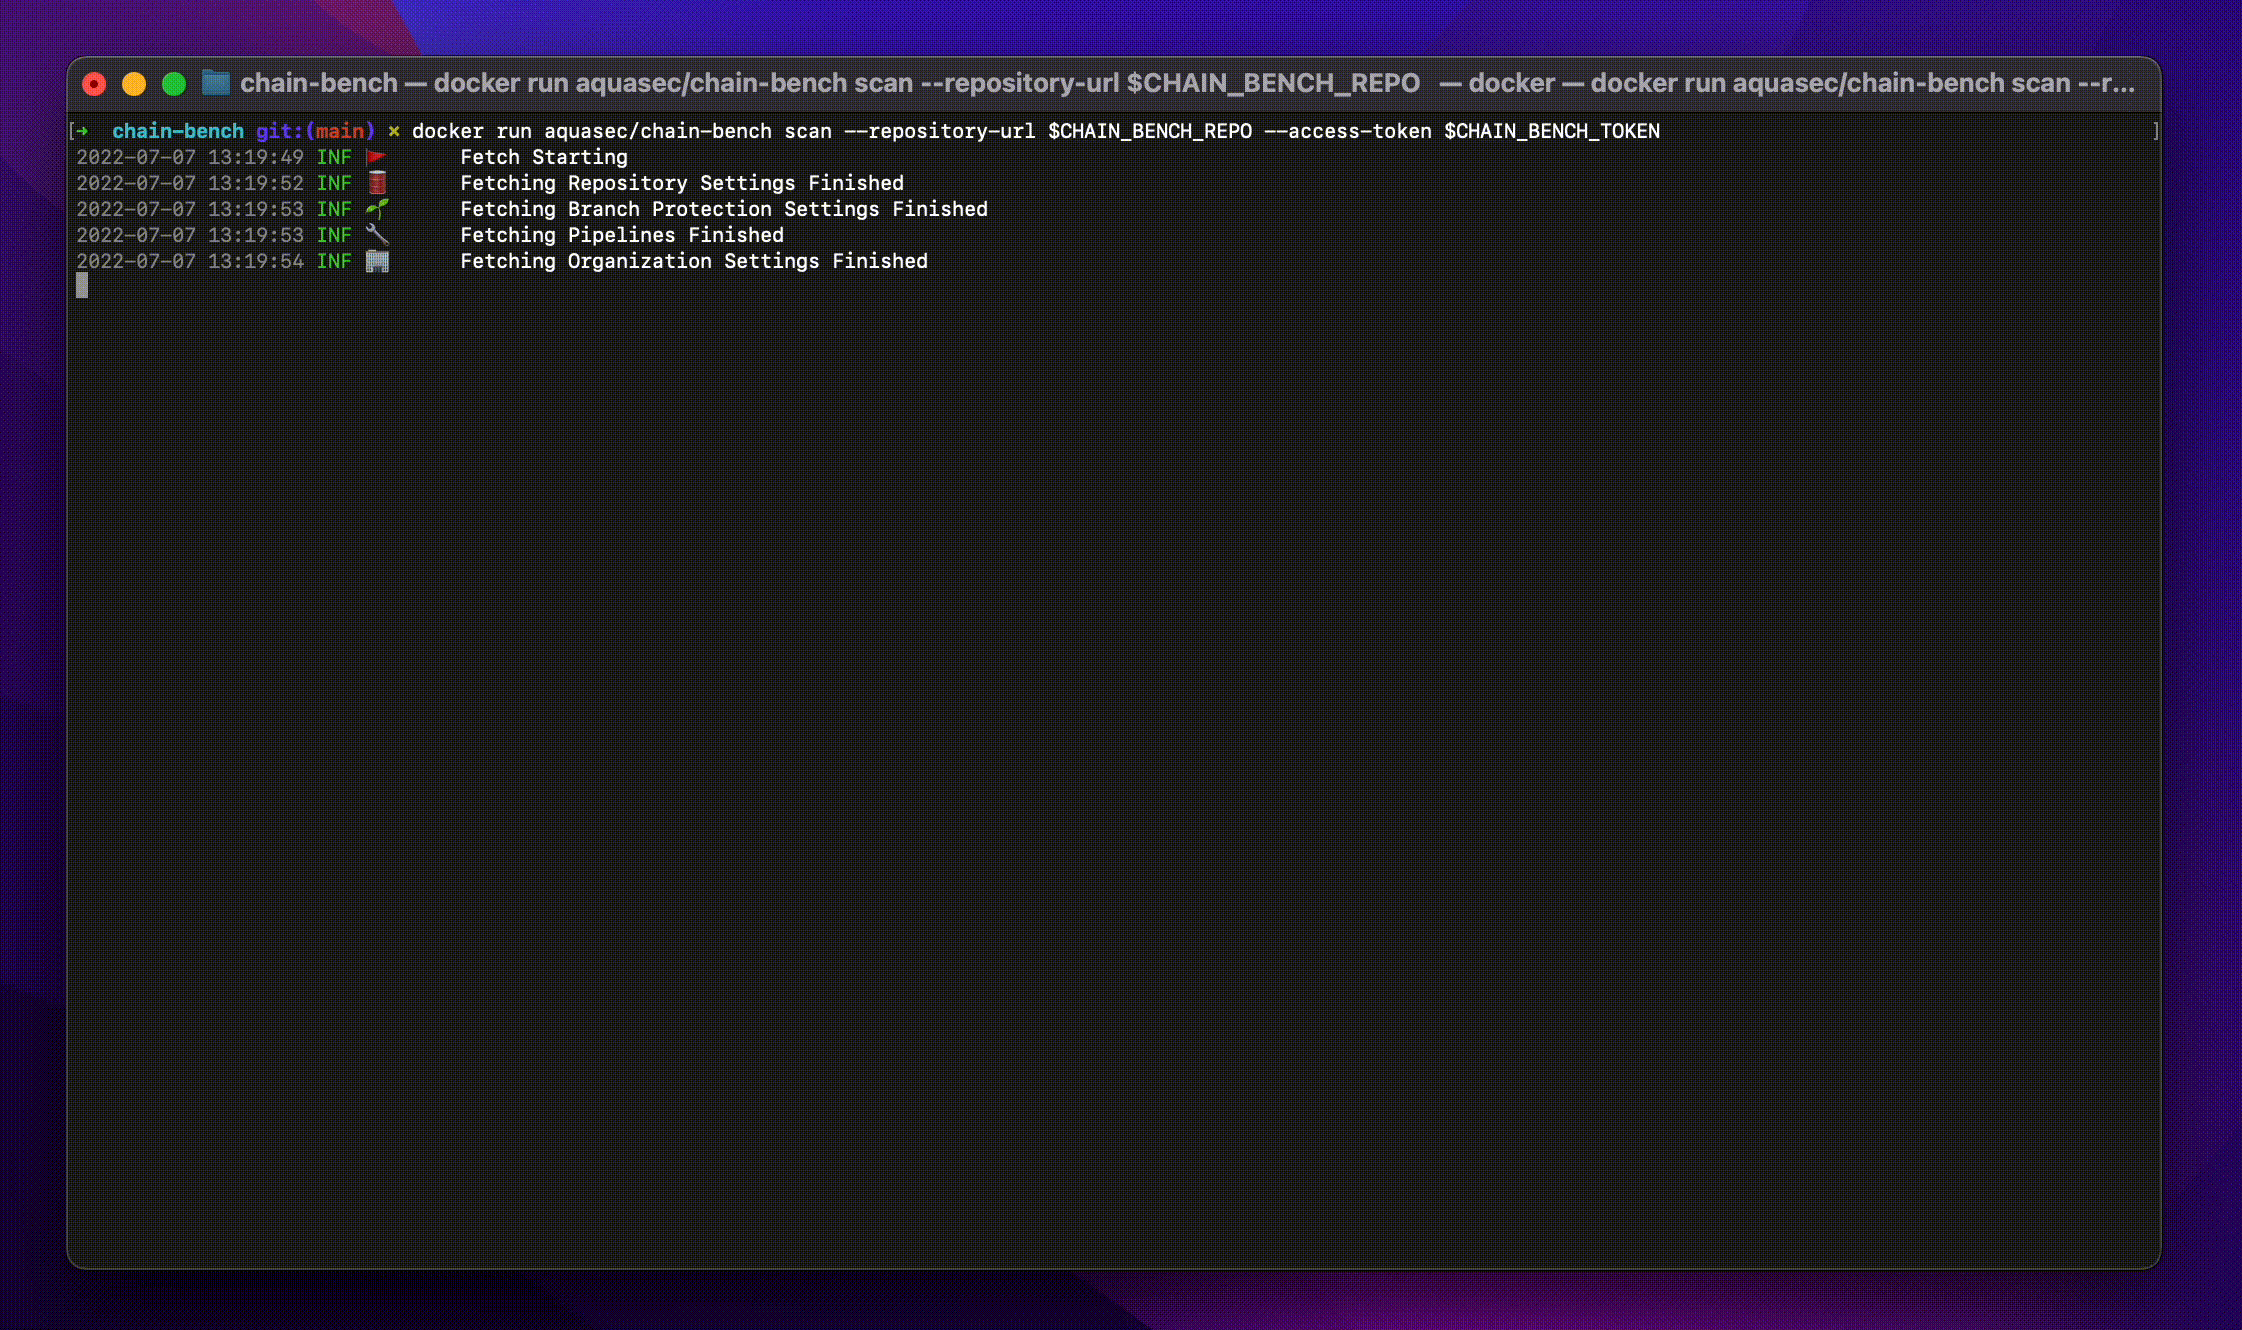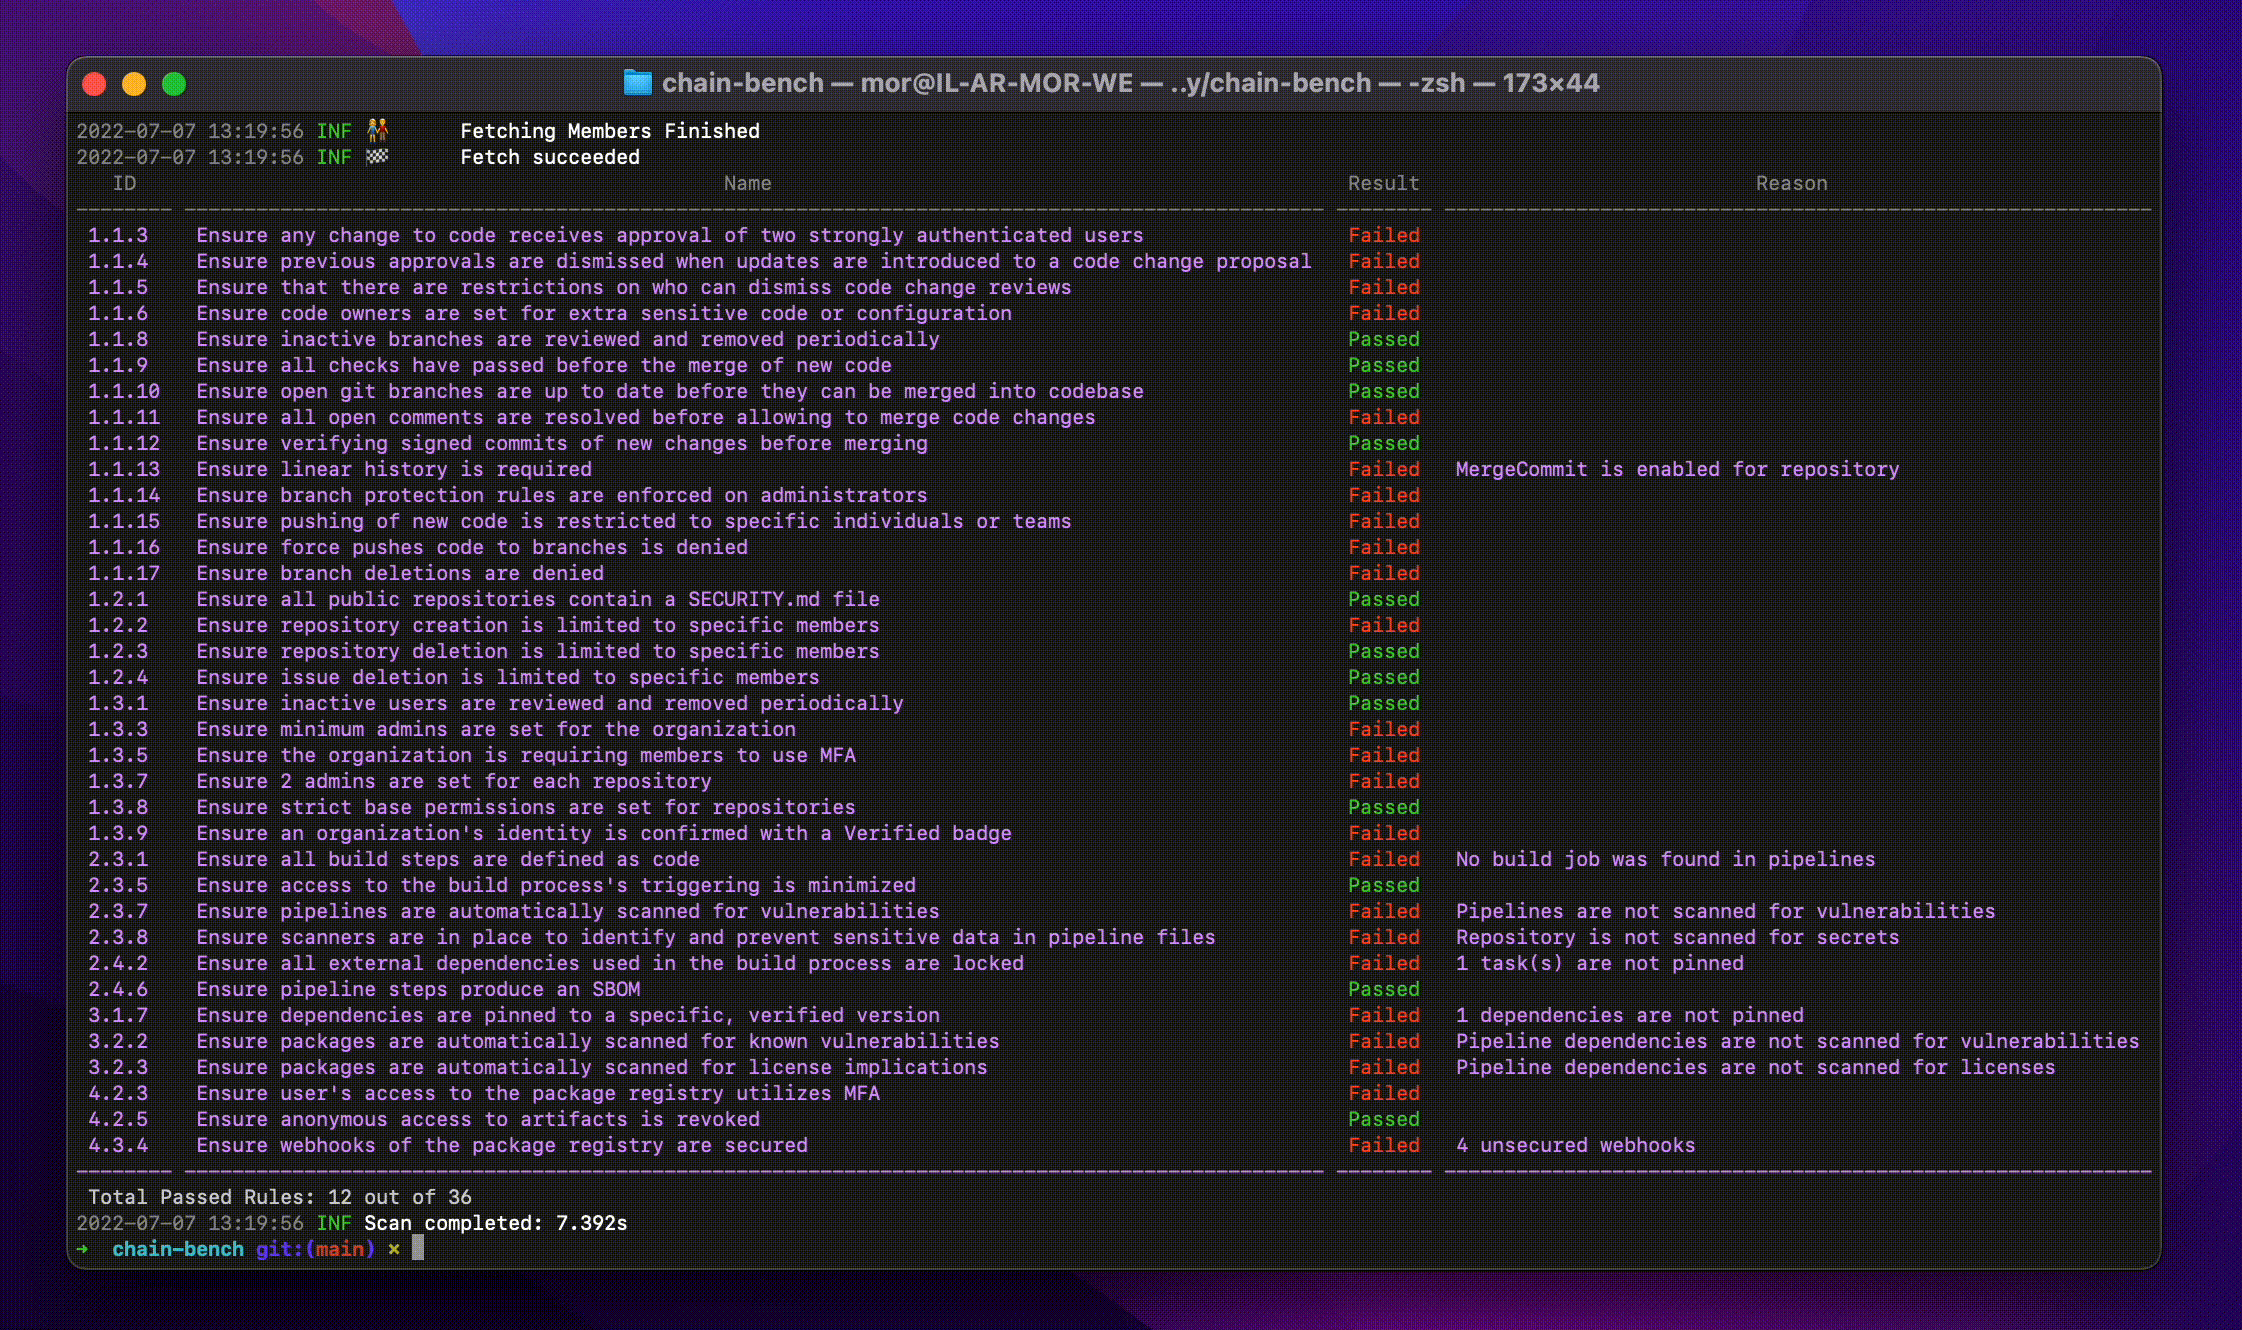 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
 code-with-amitk/centos7_cve-2021-3712_remediation
Production Ready Steps for Remediating a openssl CVE(https://nvd.nist.gov/vuln/detail/cve-2021-3712) on EOL CentOS7 box
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 node9-ai/node9-proxy
IAM for your AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run, and…
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 mhaggis/package-inferno
A Public Package Scanner for The Community
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 rotavori/dasel-melange-apko
dasel v3.3.1 packaged with Melange and shipped as a minimal apko image, patched for CVE-2026-33320
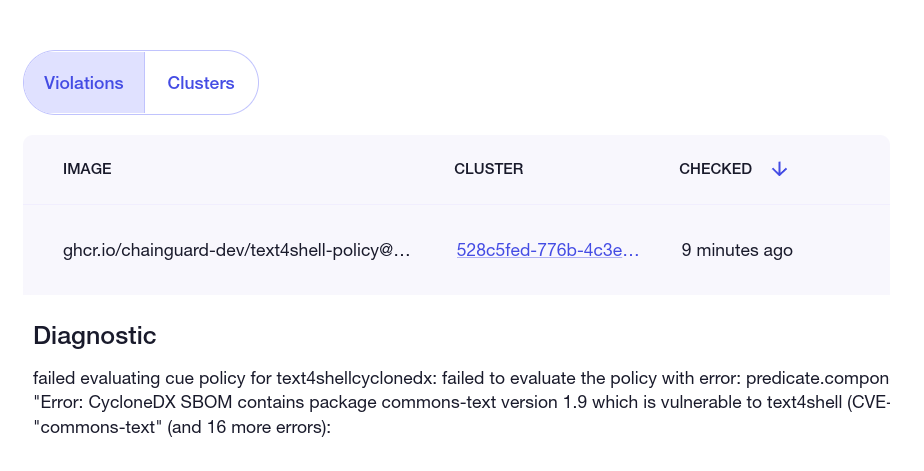 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
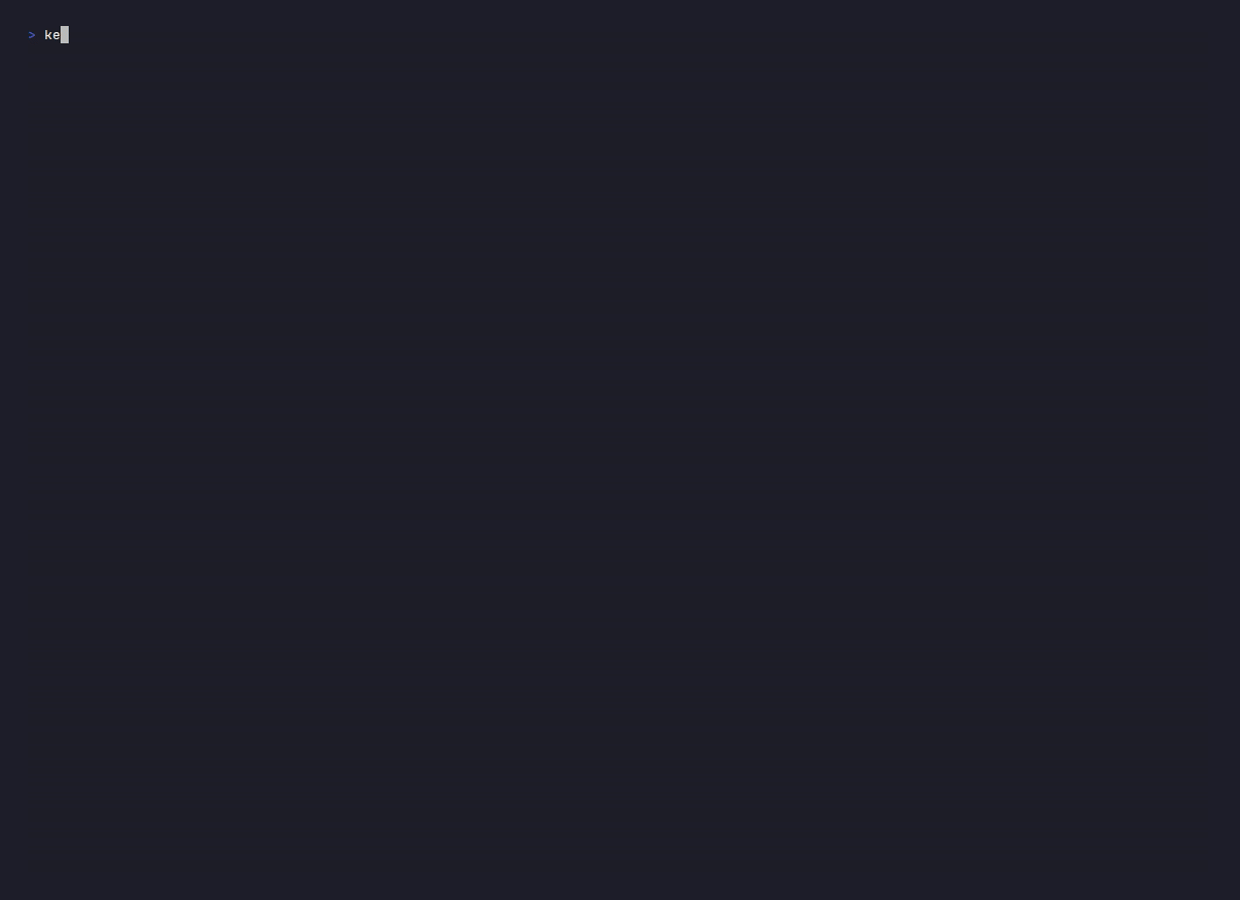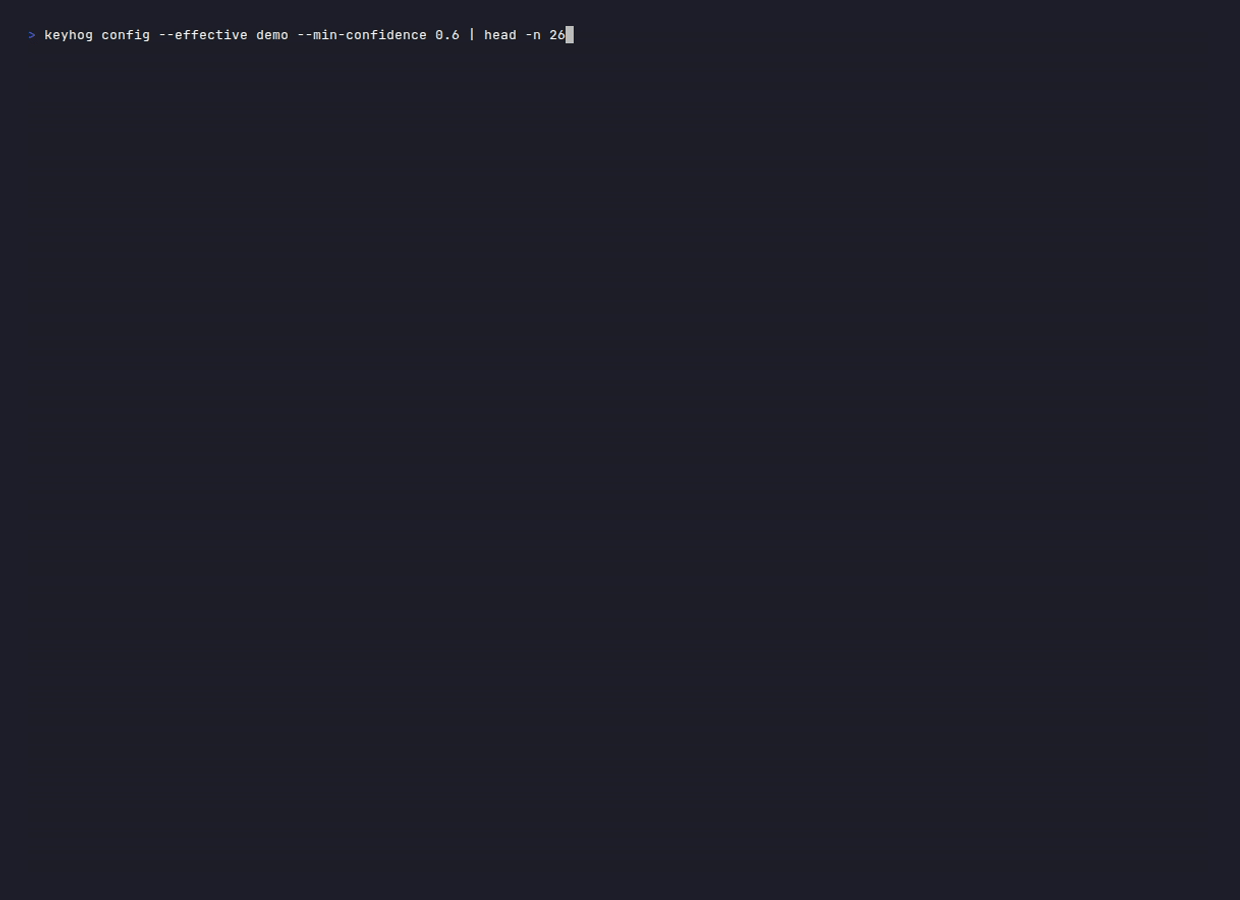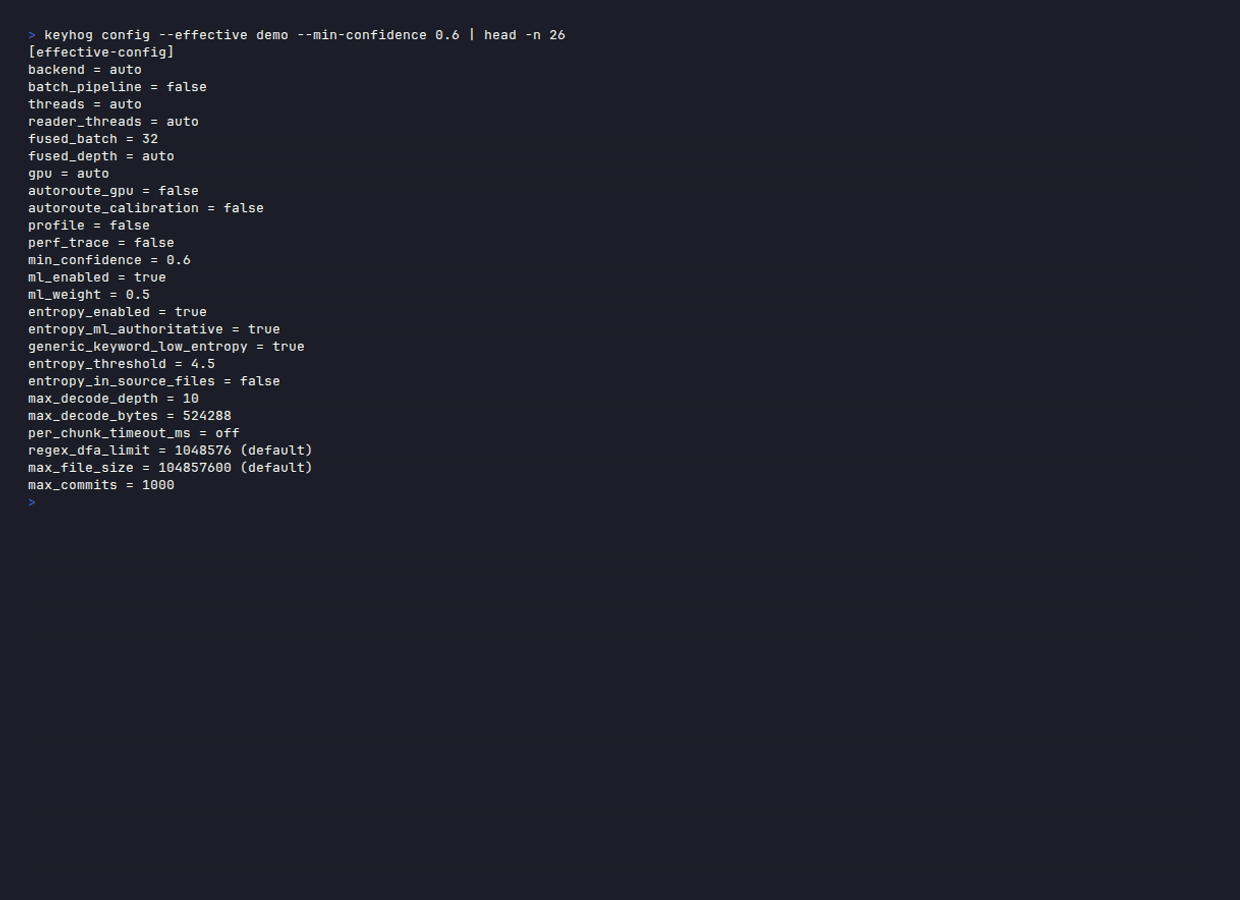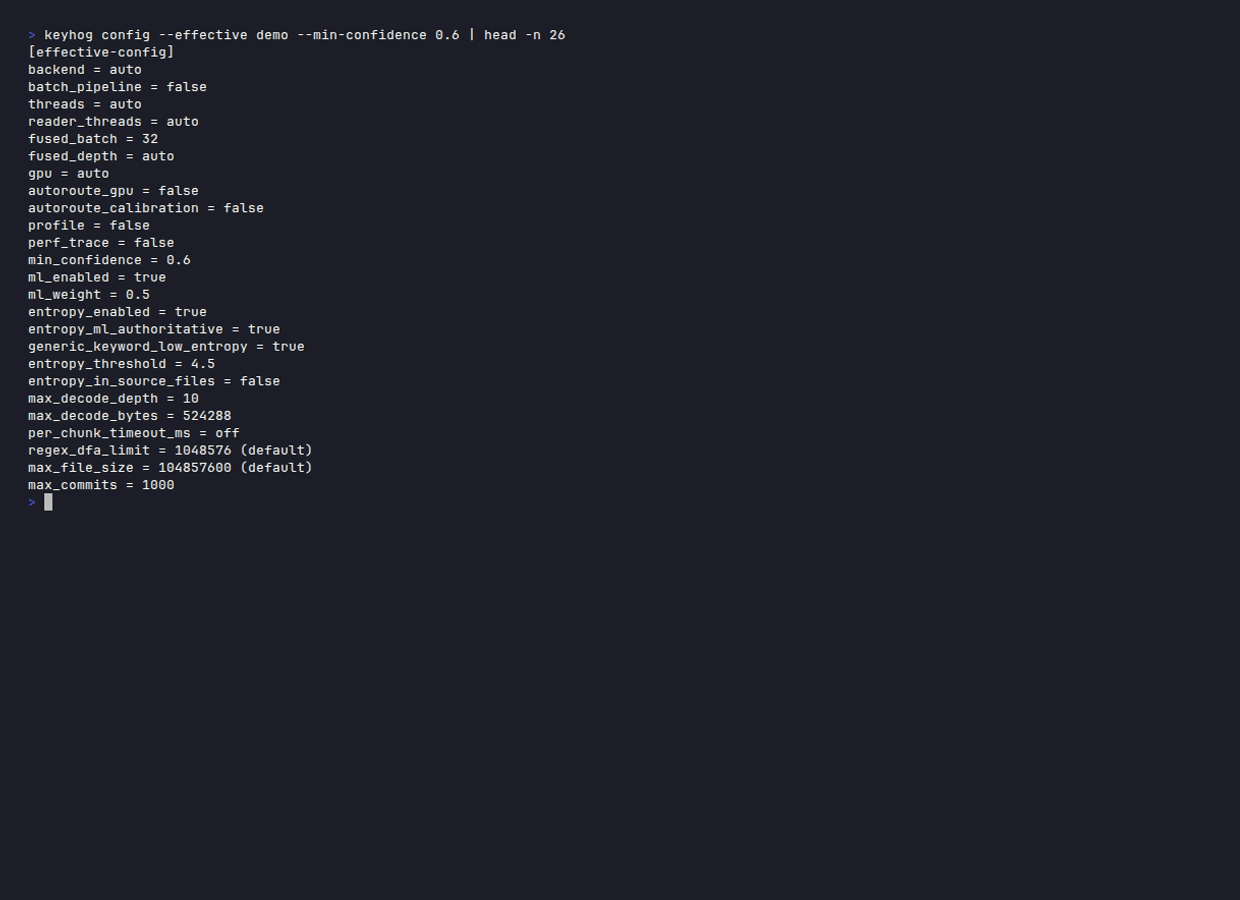 santhreal/keyhog
Open-source secret scanner in Rust