
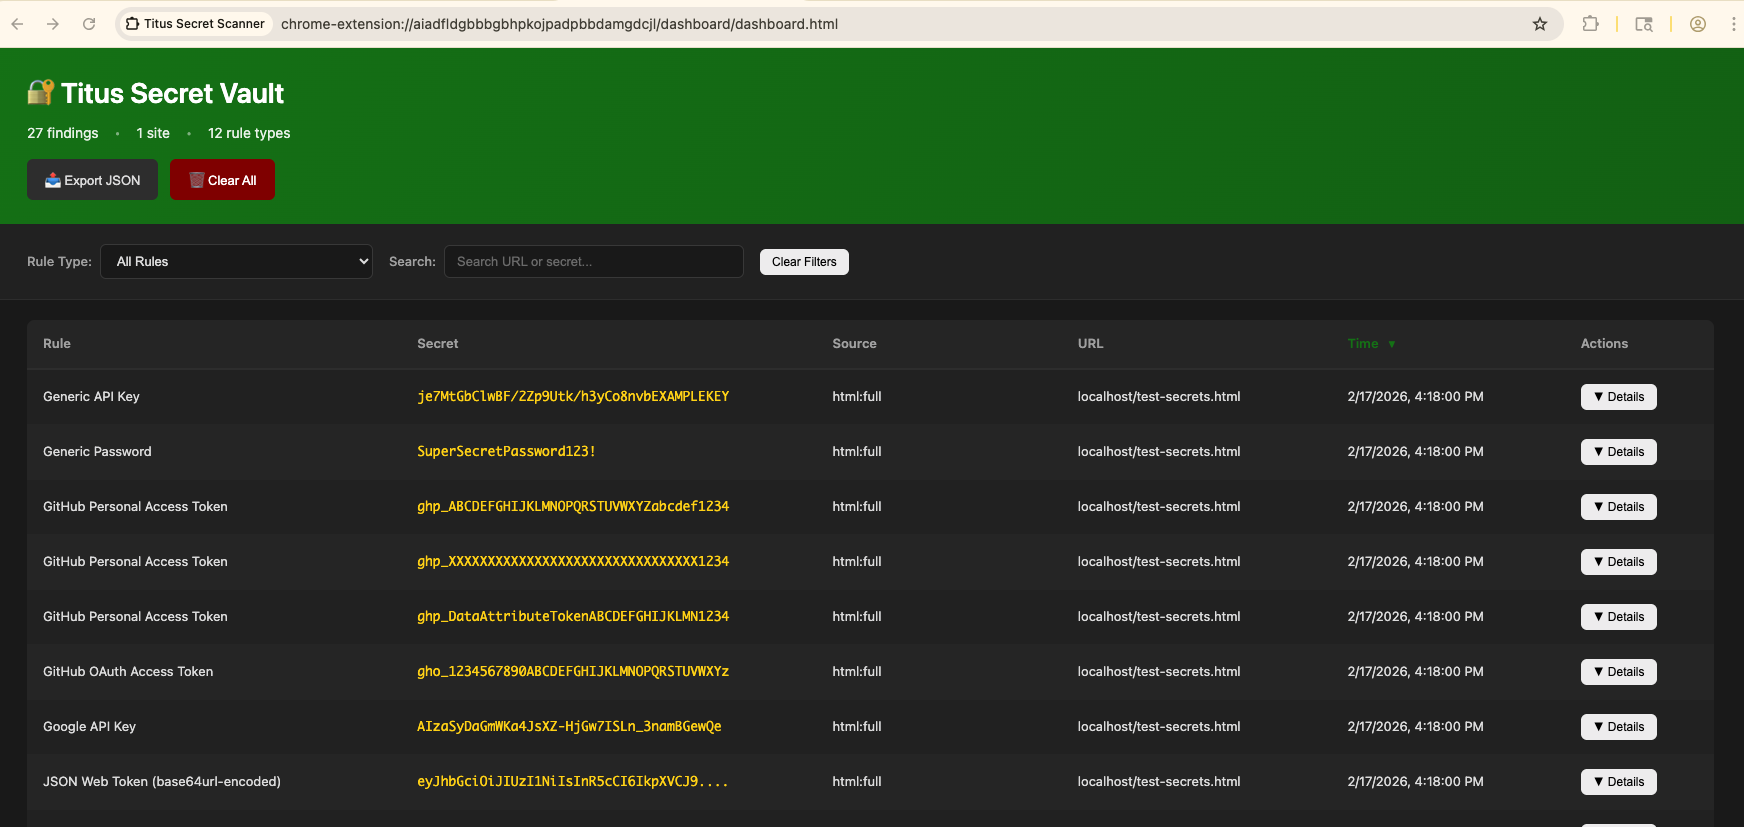
titus
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
code-analysiscontainer-securitydevsecops+6
667
praetorian-inc/titusHigh-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 yamory/cve-2021-32804
Docker-based reproduction environment for CVE-2021-32804, a path traversal vulnerability in node-tar affecting npm, with step-by-step exploitation…
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
 murataydemir/aws-sam-cli-vulnerabilities
Issue with AWS SAM CLI (CVE-2025-3047, CVE-2025-3048)
 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
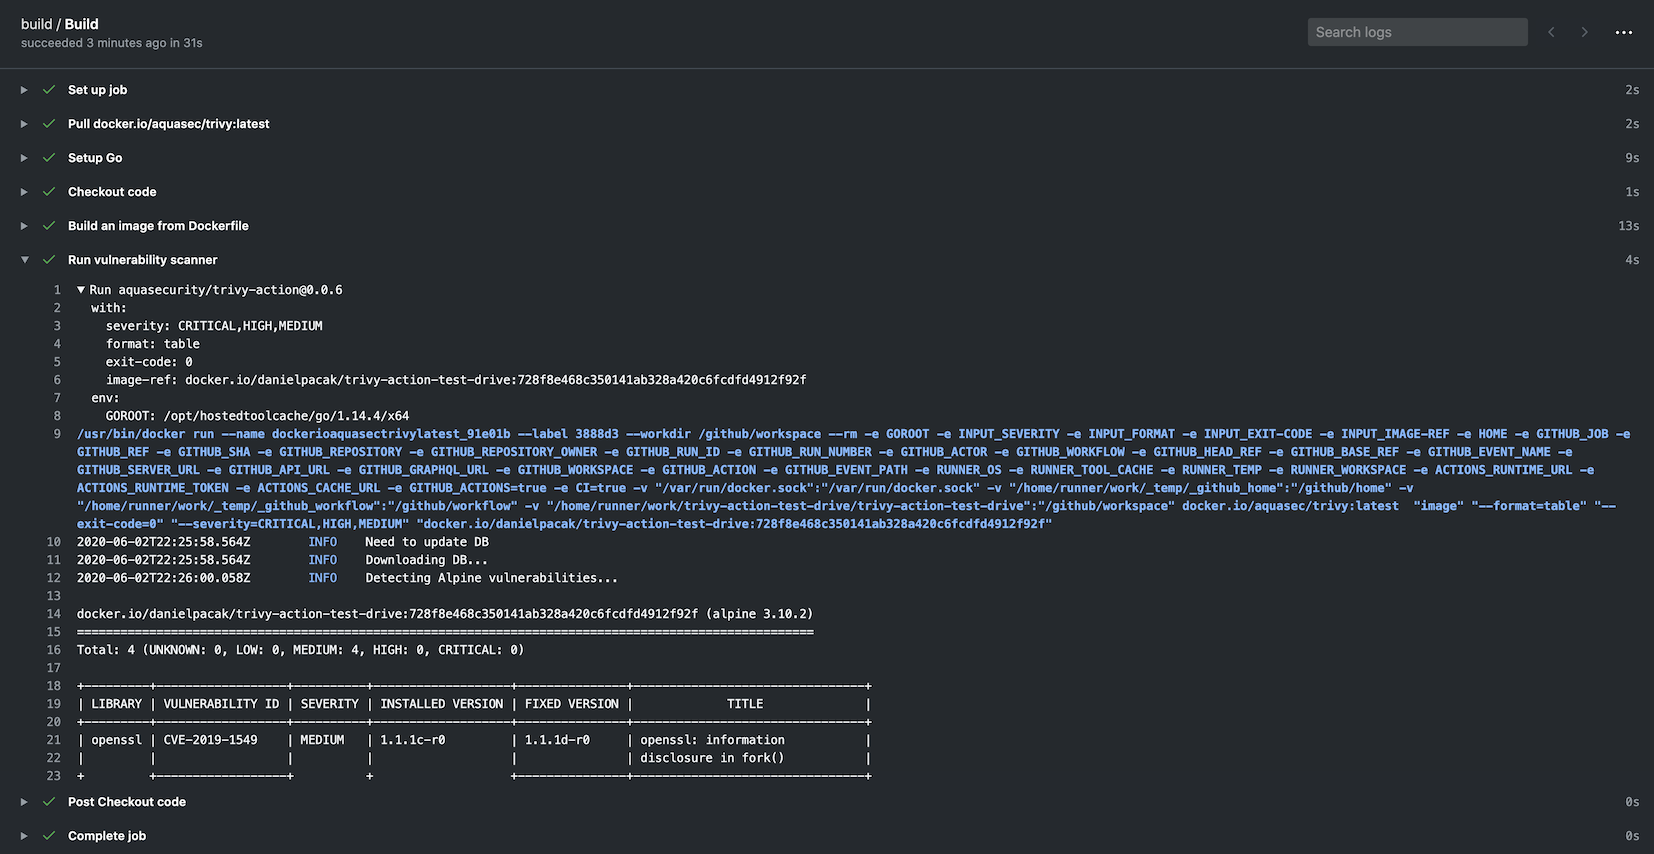 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 saku0512/cve-2026-84361-poc
Proof-of-concept for CVE-2026-84361, demonstrating command injection in Composer's Perforce driver via malicious P4PORT, with Docker-based…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
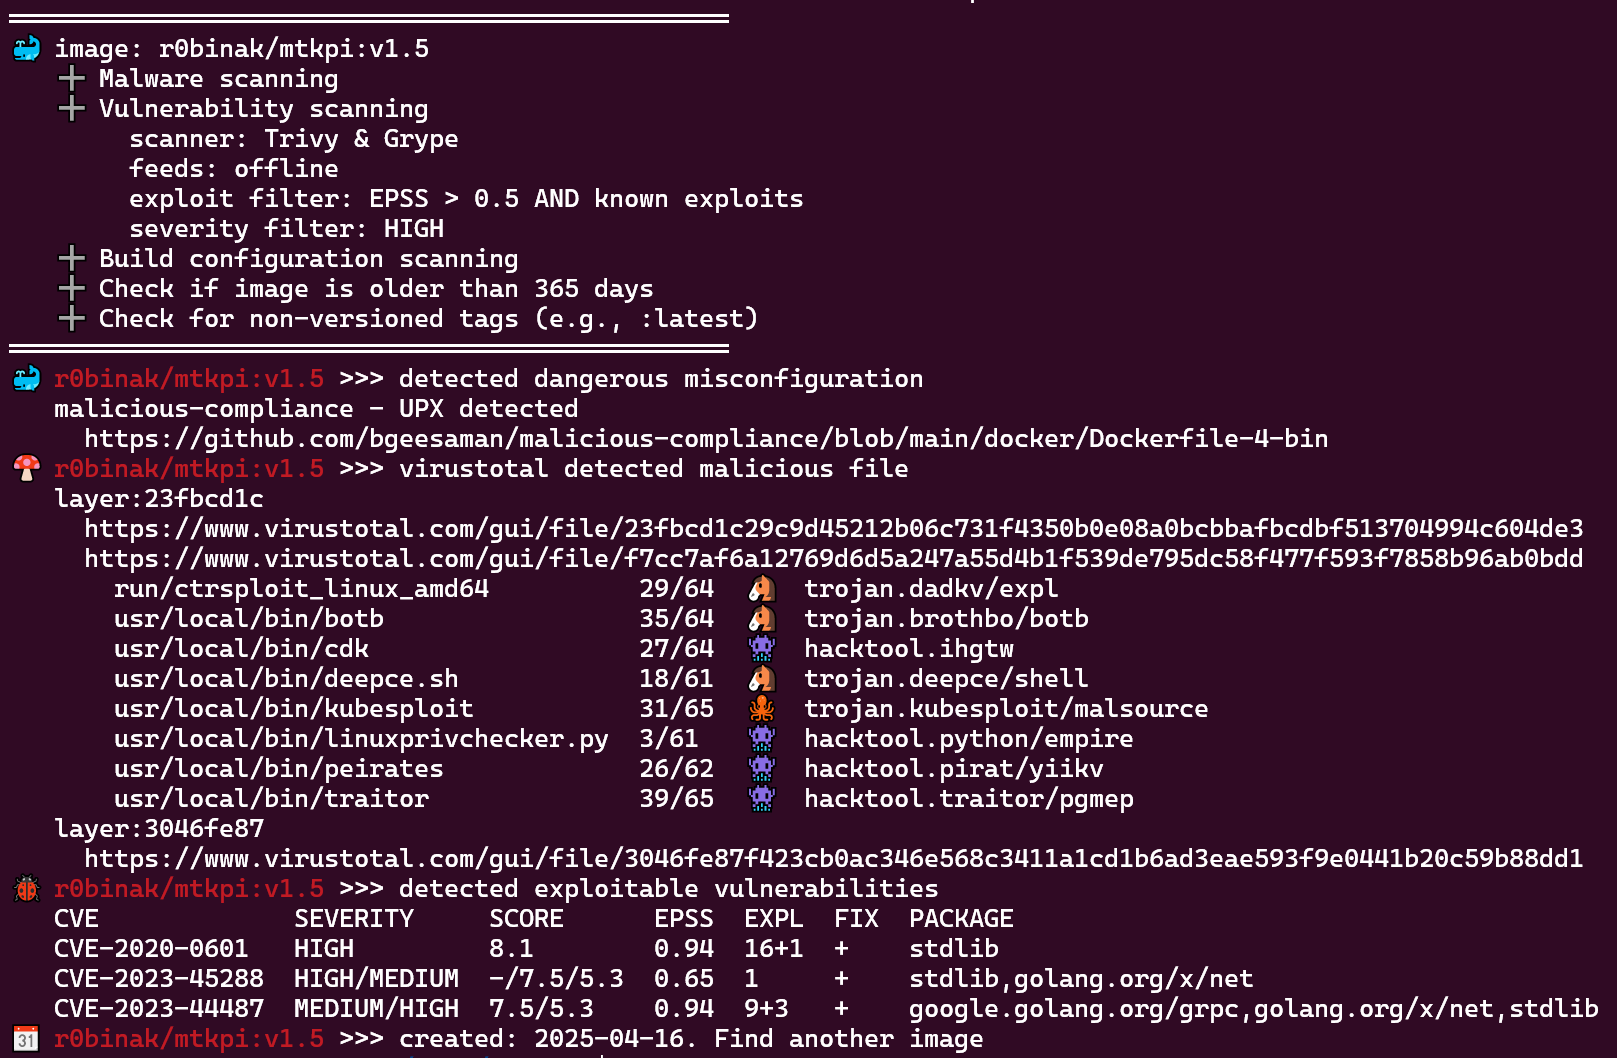 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 apaonum/brotli-cve-check
Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes