
minimal
 rtvkiz/minimal
Minimal CVE Hardened container image collection
cloud-securityconfiguration-auditingcontainer-security+3
rtvkiz/minimalMinimal CVE Hardened container image collection
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 git-pkgs/proxy
A lightweight caching proxy for package registries.
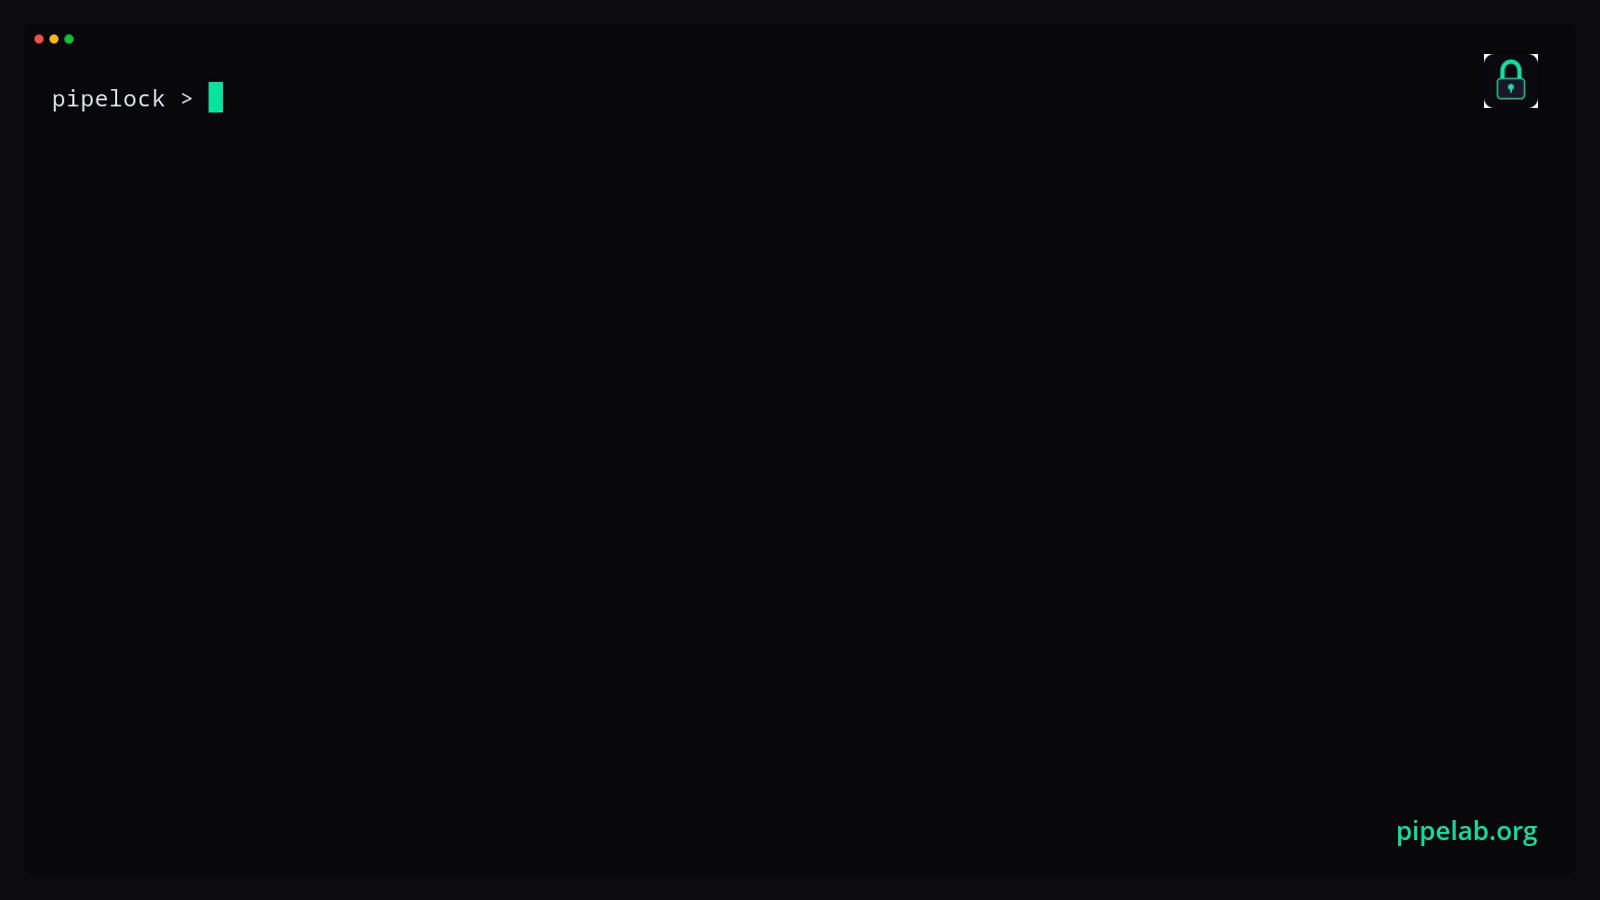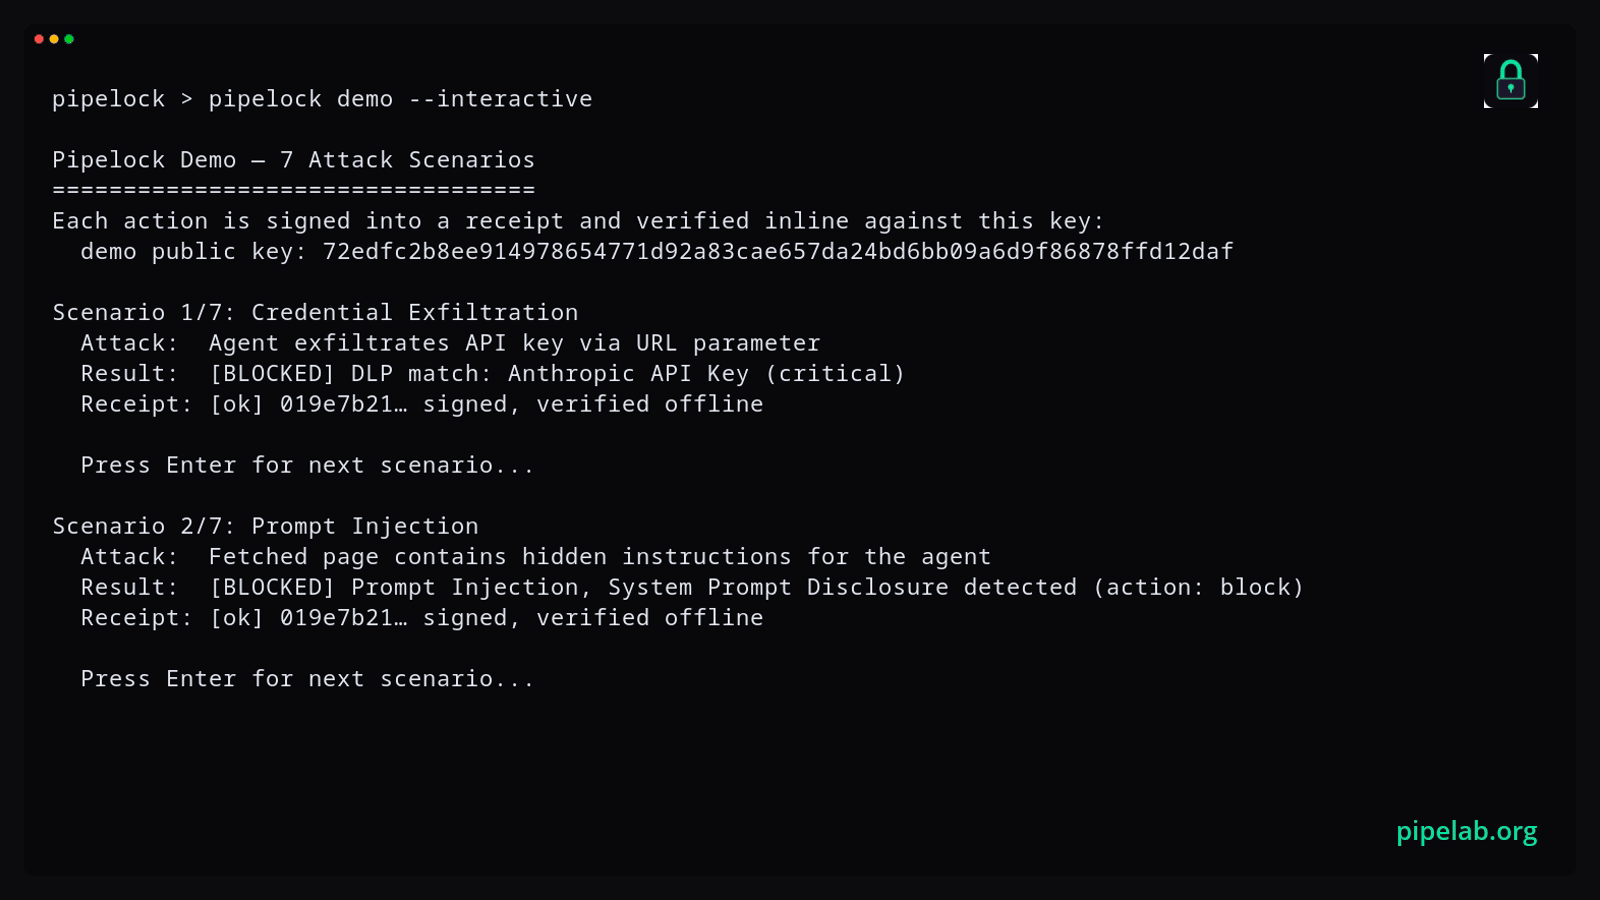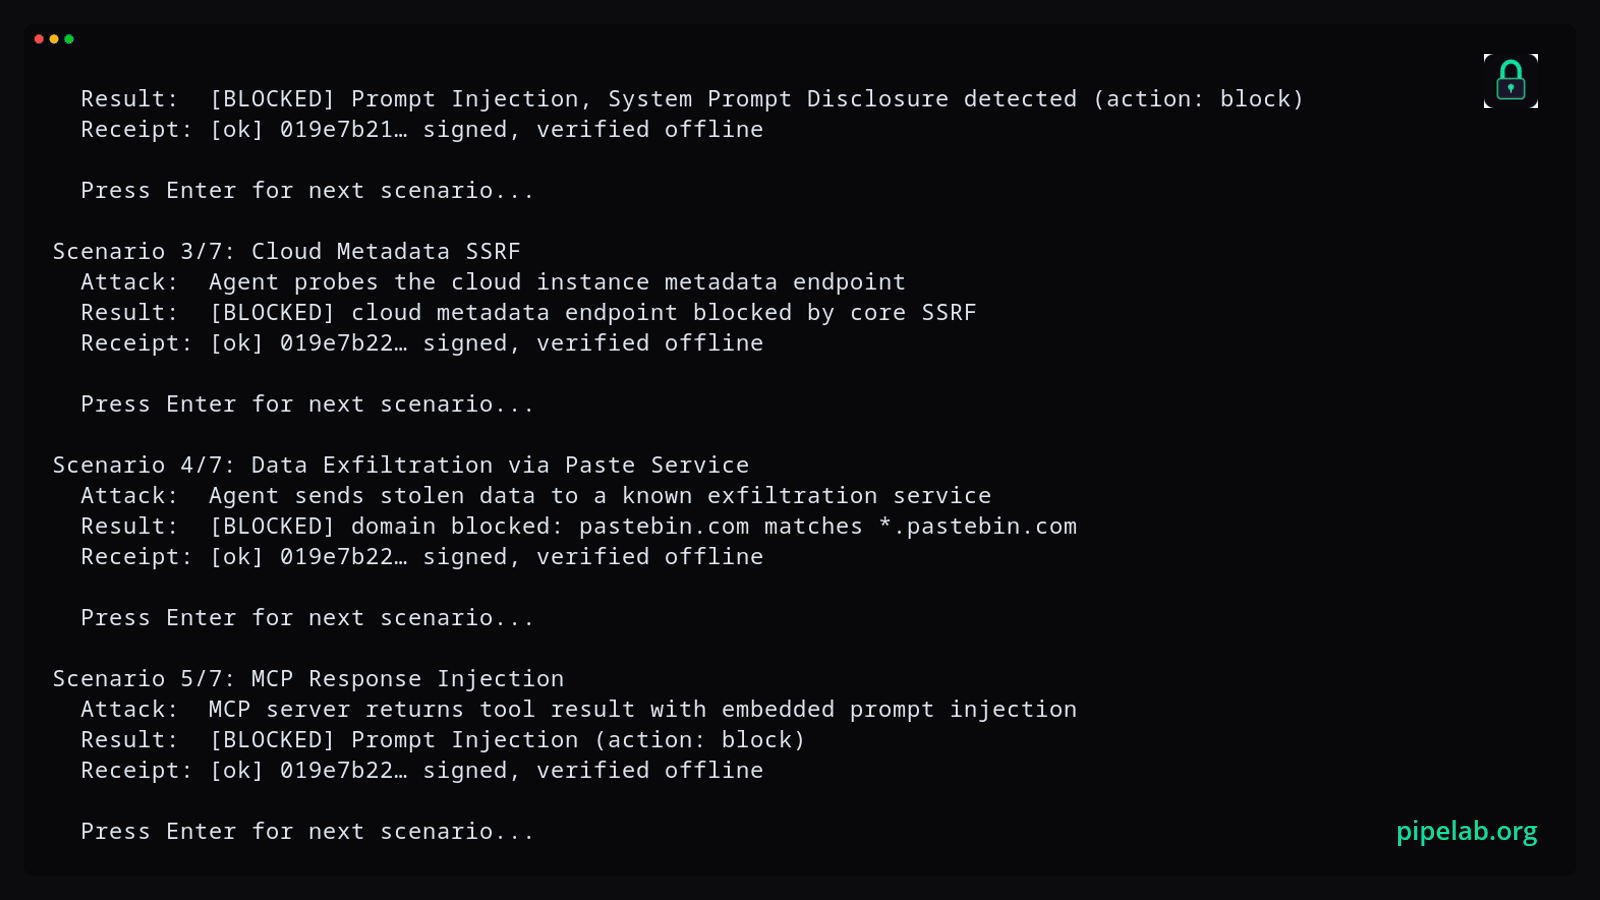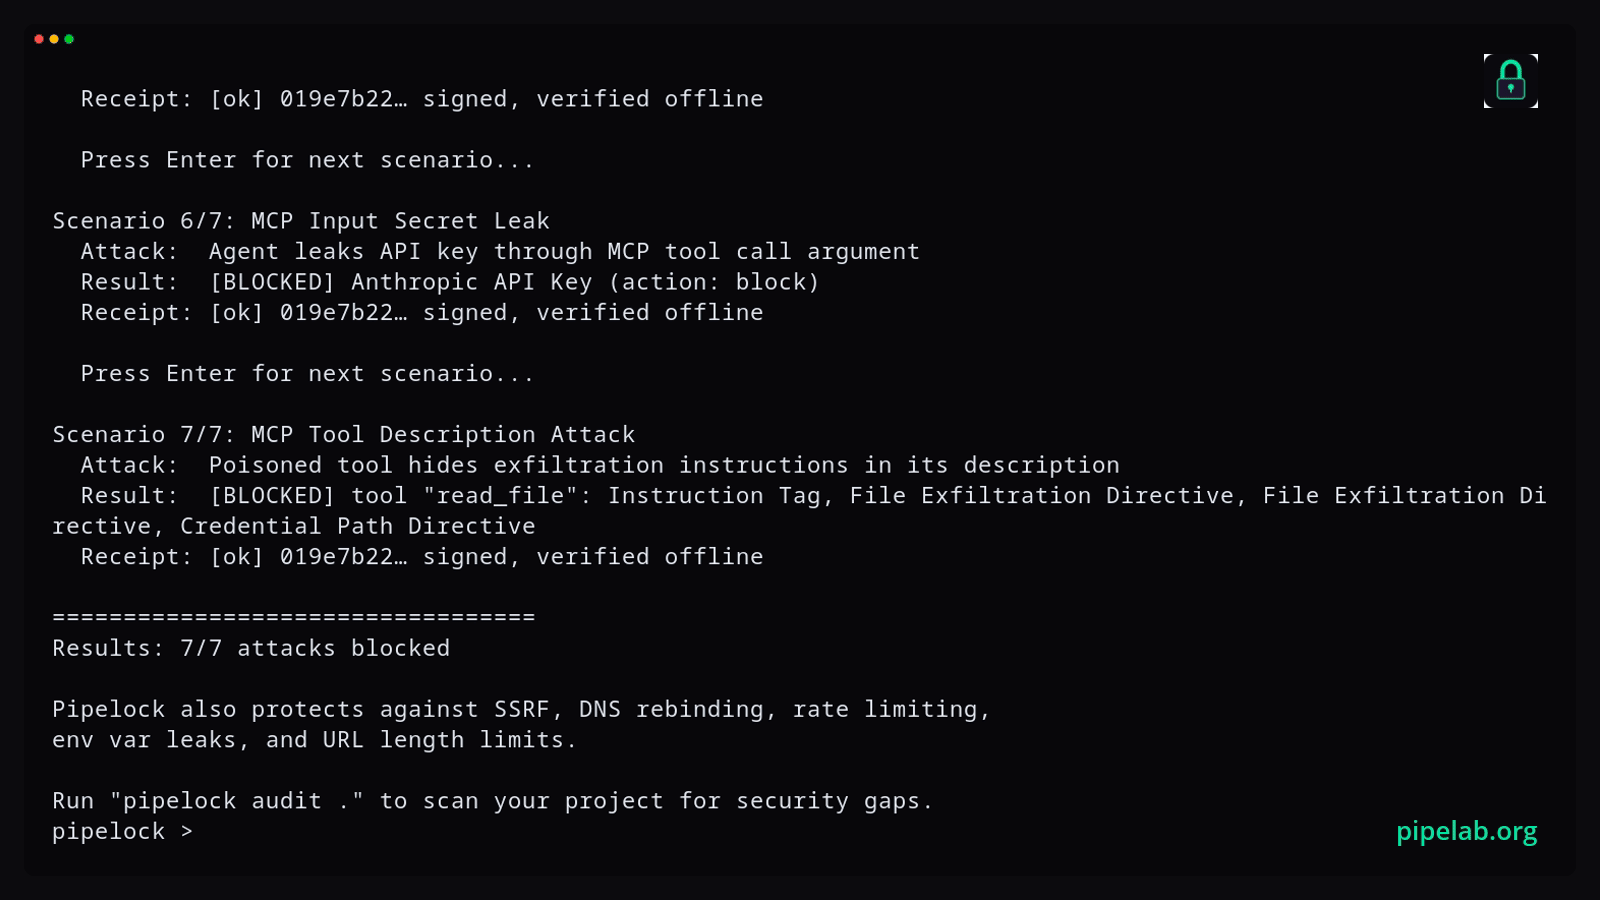 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 commonguy25/authproof-sdk
Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 mindersec/minder
Software Supply Chain Security Platform
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
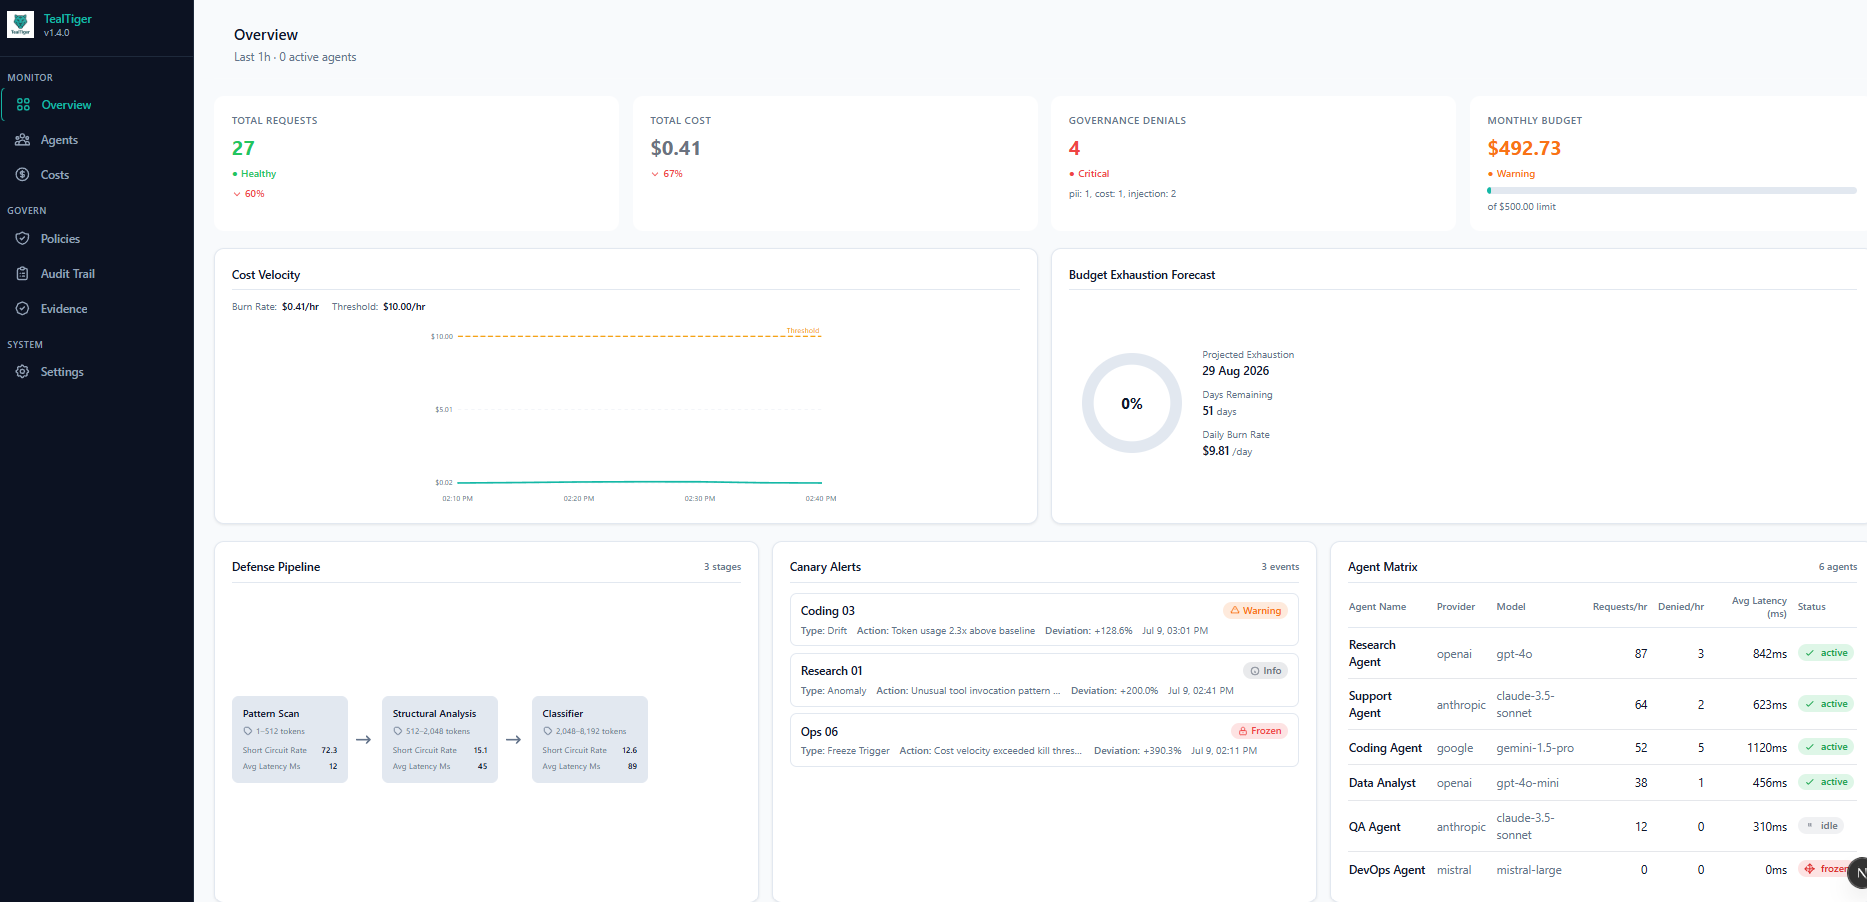 agentguard-ai/tealtiger
Powerful protection for AI agents - Open-source security and cost tracking for AI applications
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 anchore/grype
A vulnerability scanner for container images and filesystems
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
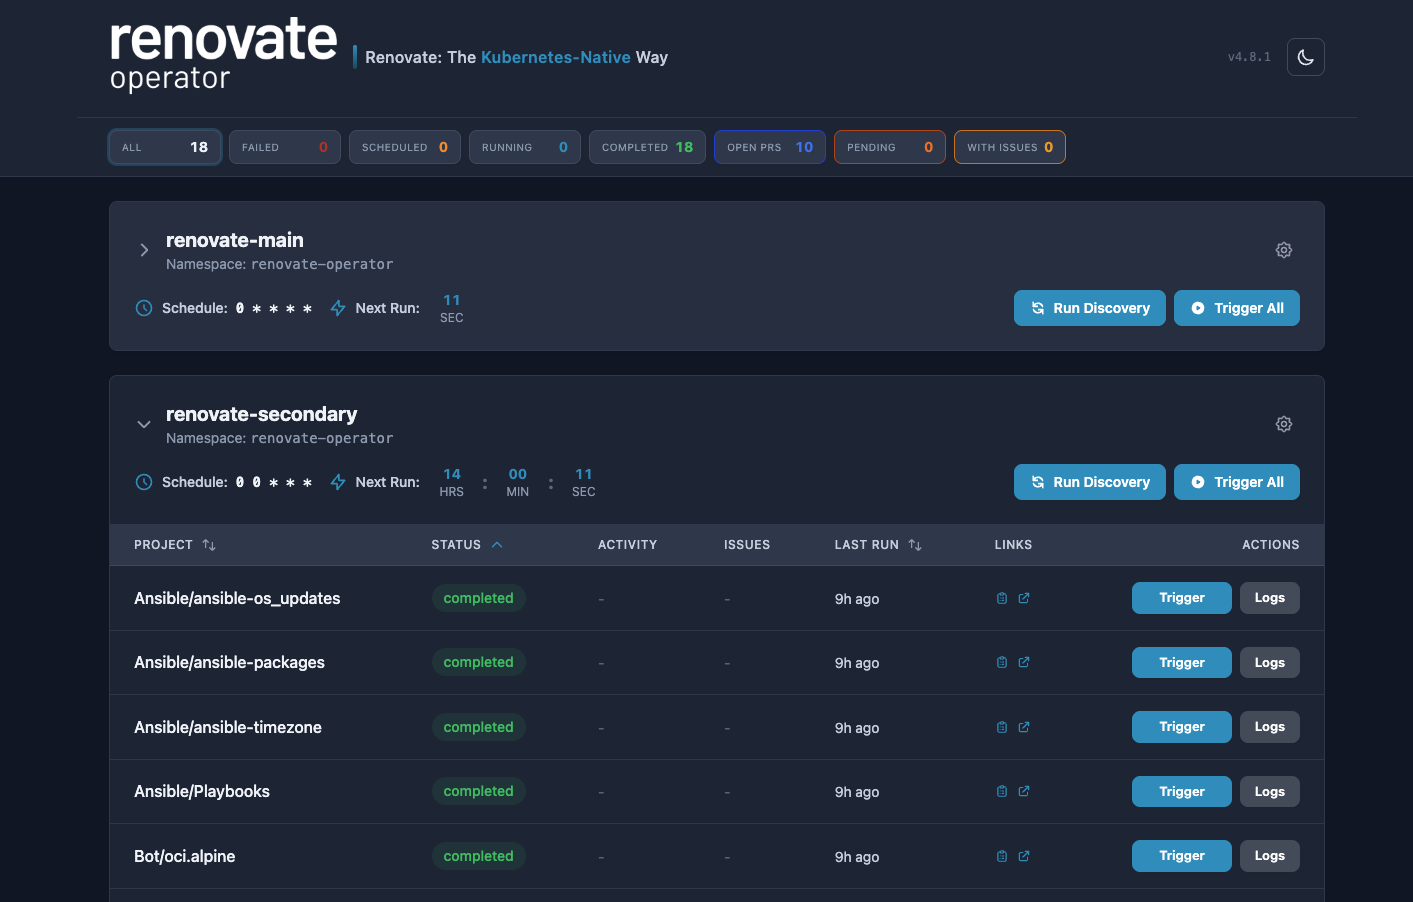 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes