

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.1k
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 anchore/grype
A vulnerability scanner for container images and filesystems
 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 safedep/vet
Protect against malicious open source packages 🤖
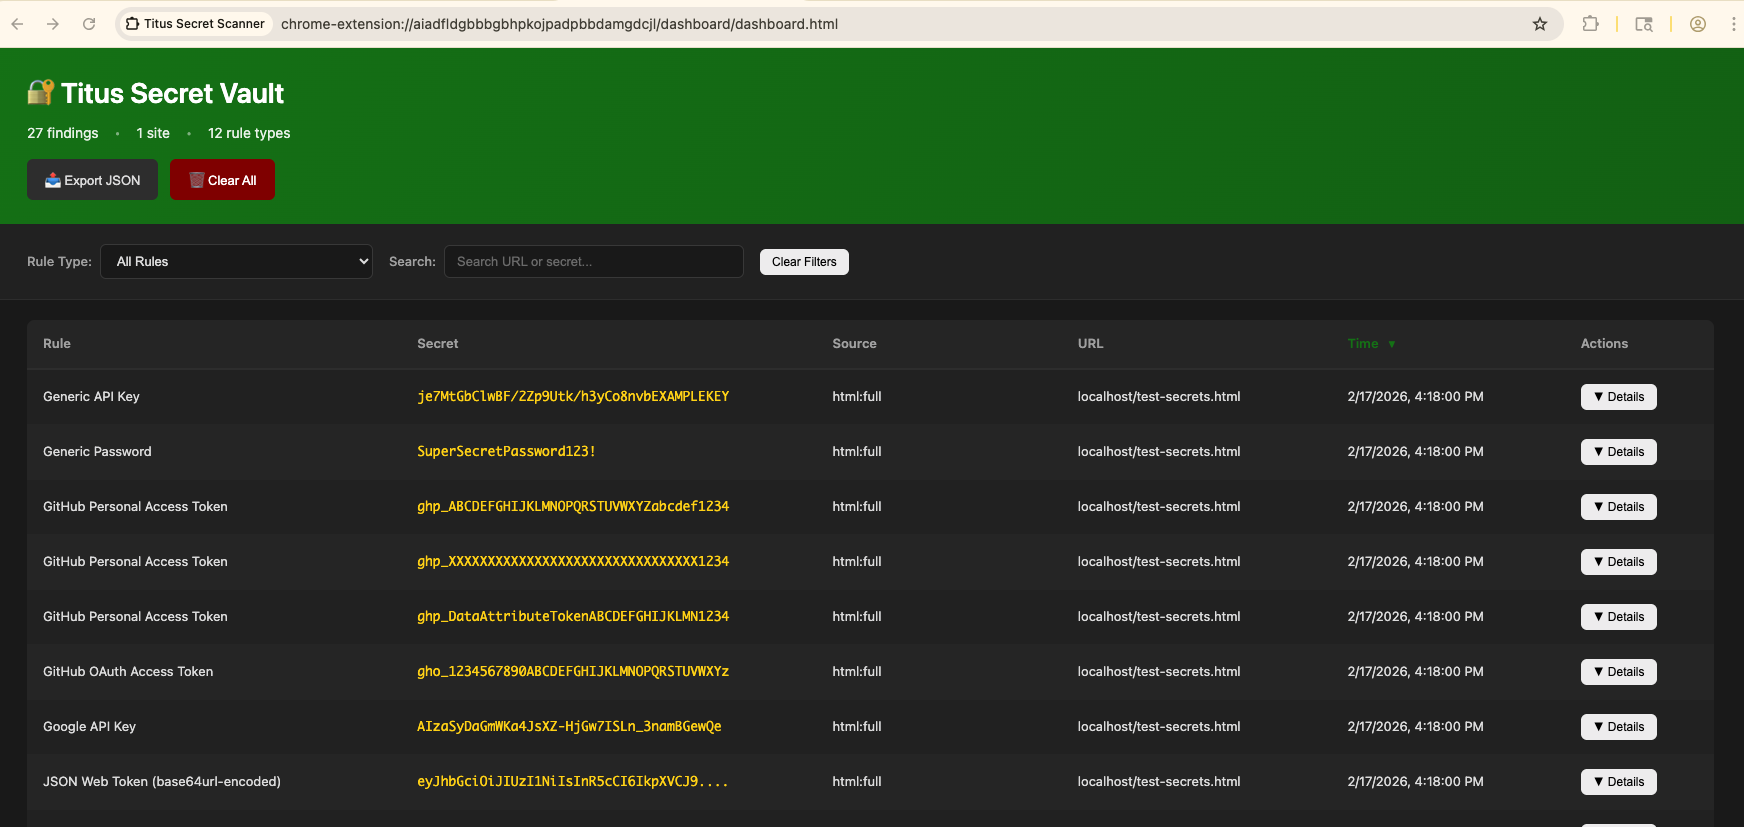 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
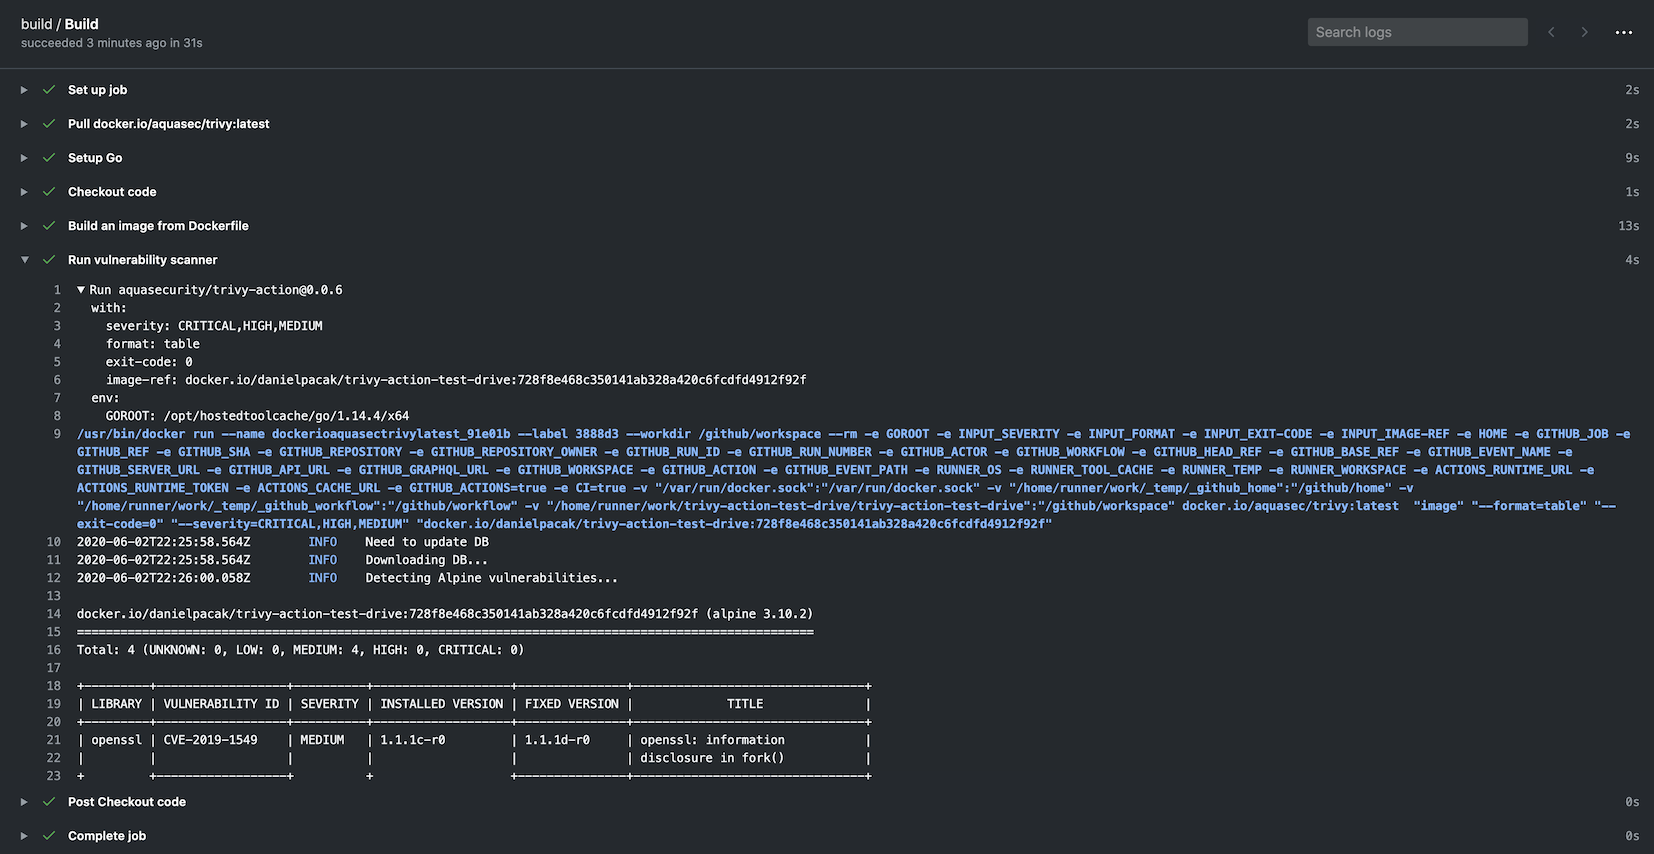 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 codesecurityteam/harbor
CVE-2022-46463 harbor公开镜像全自动下载脚本
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
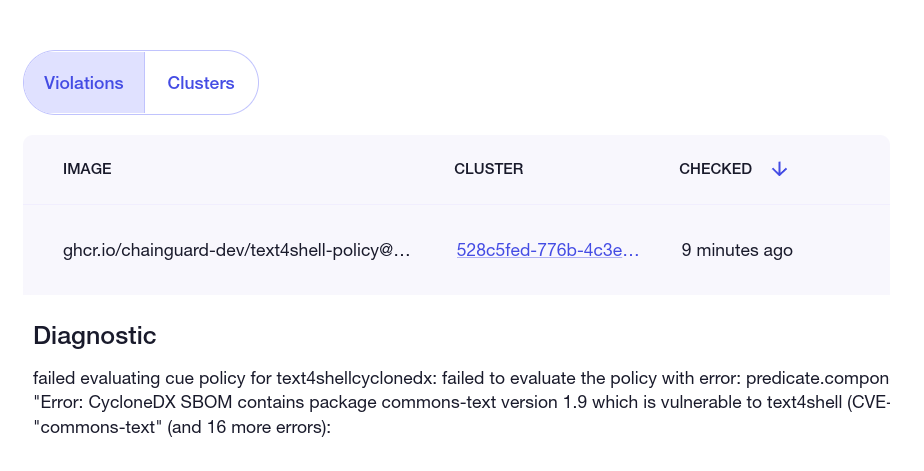 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…