Rock-ON
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
crawlerdns-subdomain-enumerationinformation-gathering+5
290
silverpoision/rock-onRock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
 thebinitghimire/nthim
Now, the Host is Mine! - Super Fast Sub-domain Takeover Detection!
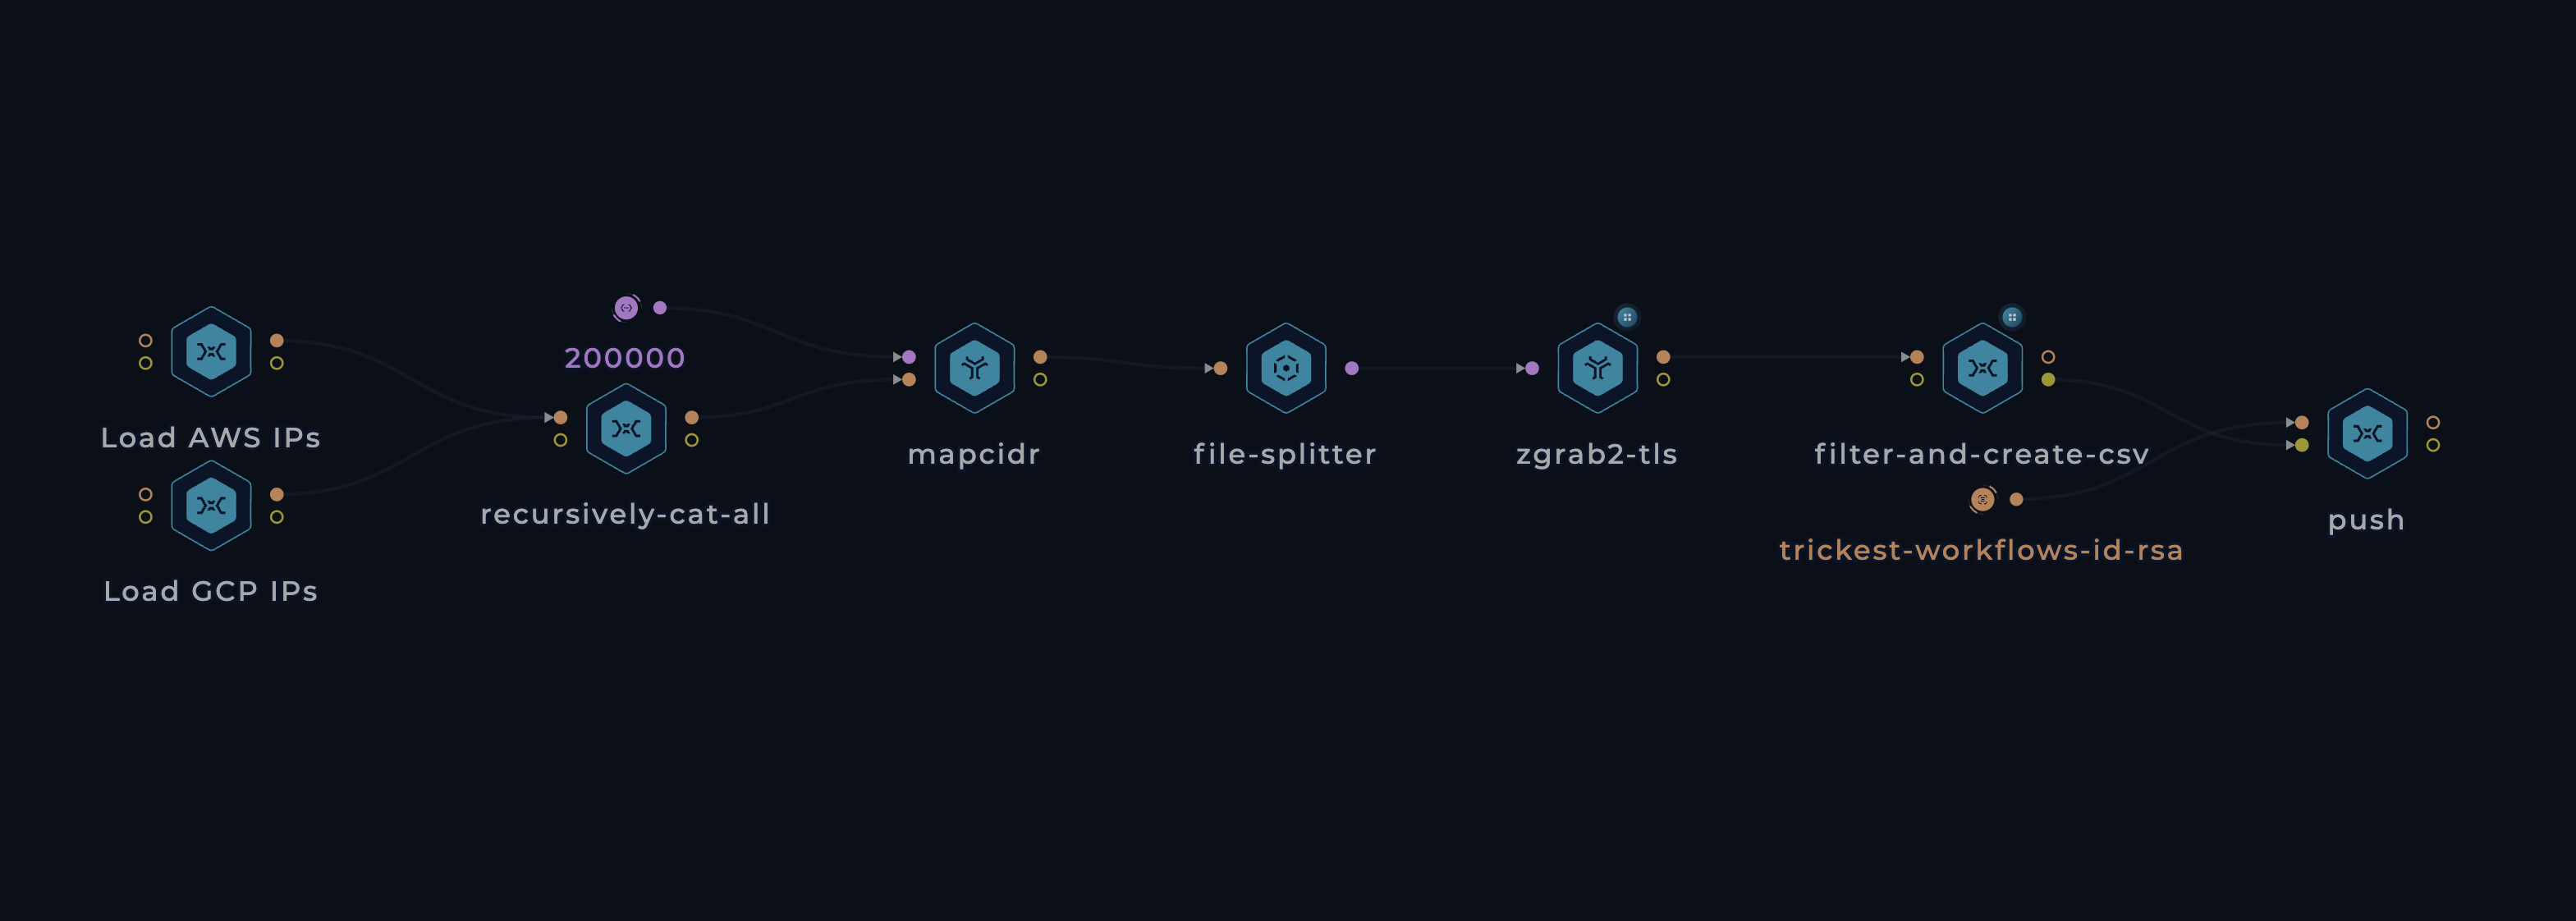 trickest/cloud
Monitoring the Cloud Landscape
 shivamrai2003/reconky-automated_bash_script
Reconky is an great Content Discovery bash script for bug bounty hunters which automate lot of task and organized in the well mannered form which…
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
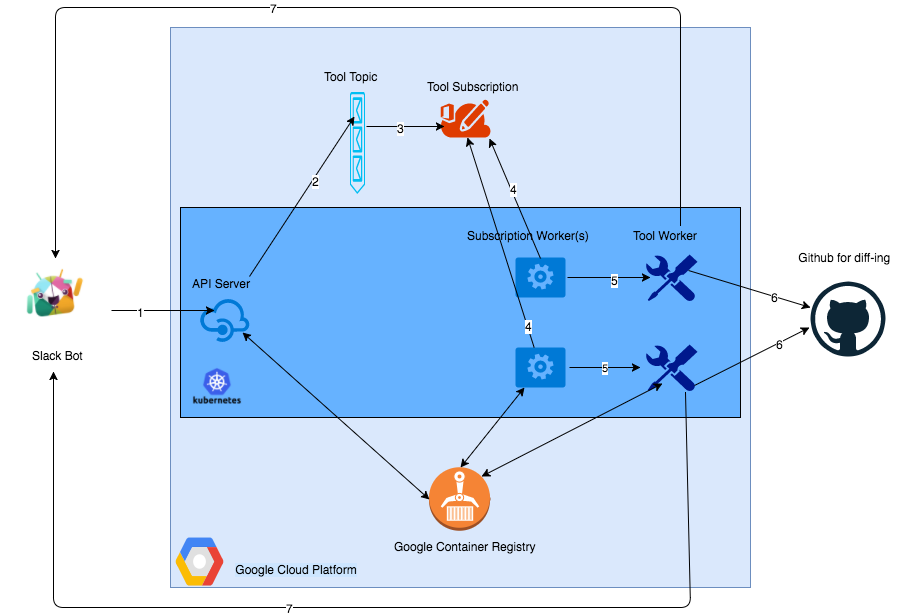 anshumanbh/kubebot
A security testing Slackbot built with a Kubernetes backend on the Google Cloud Platform
 dawgyg/bugbounty_tools
Collection of scripts and tools used during bug bounty work. This will be the location of my automation scripts created for my own personal use, and…
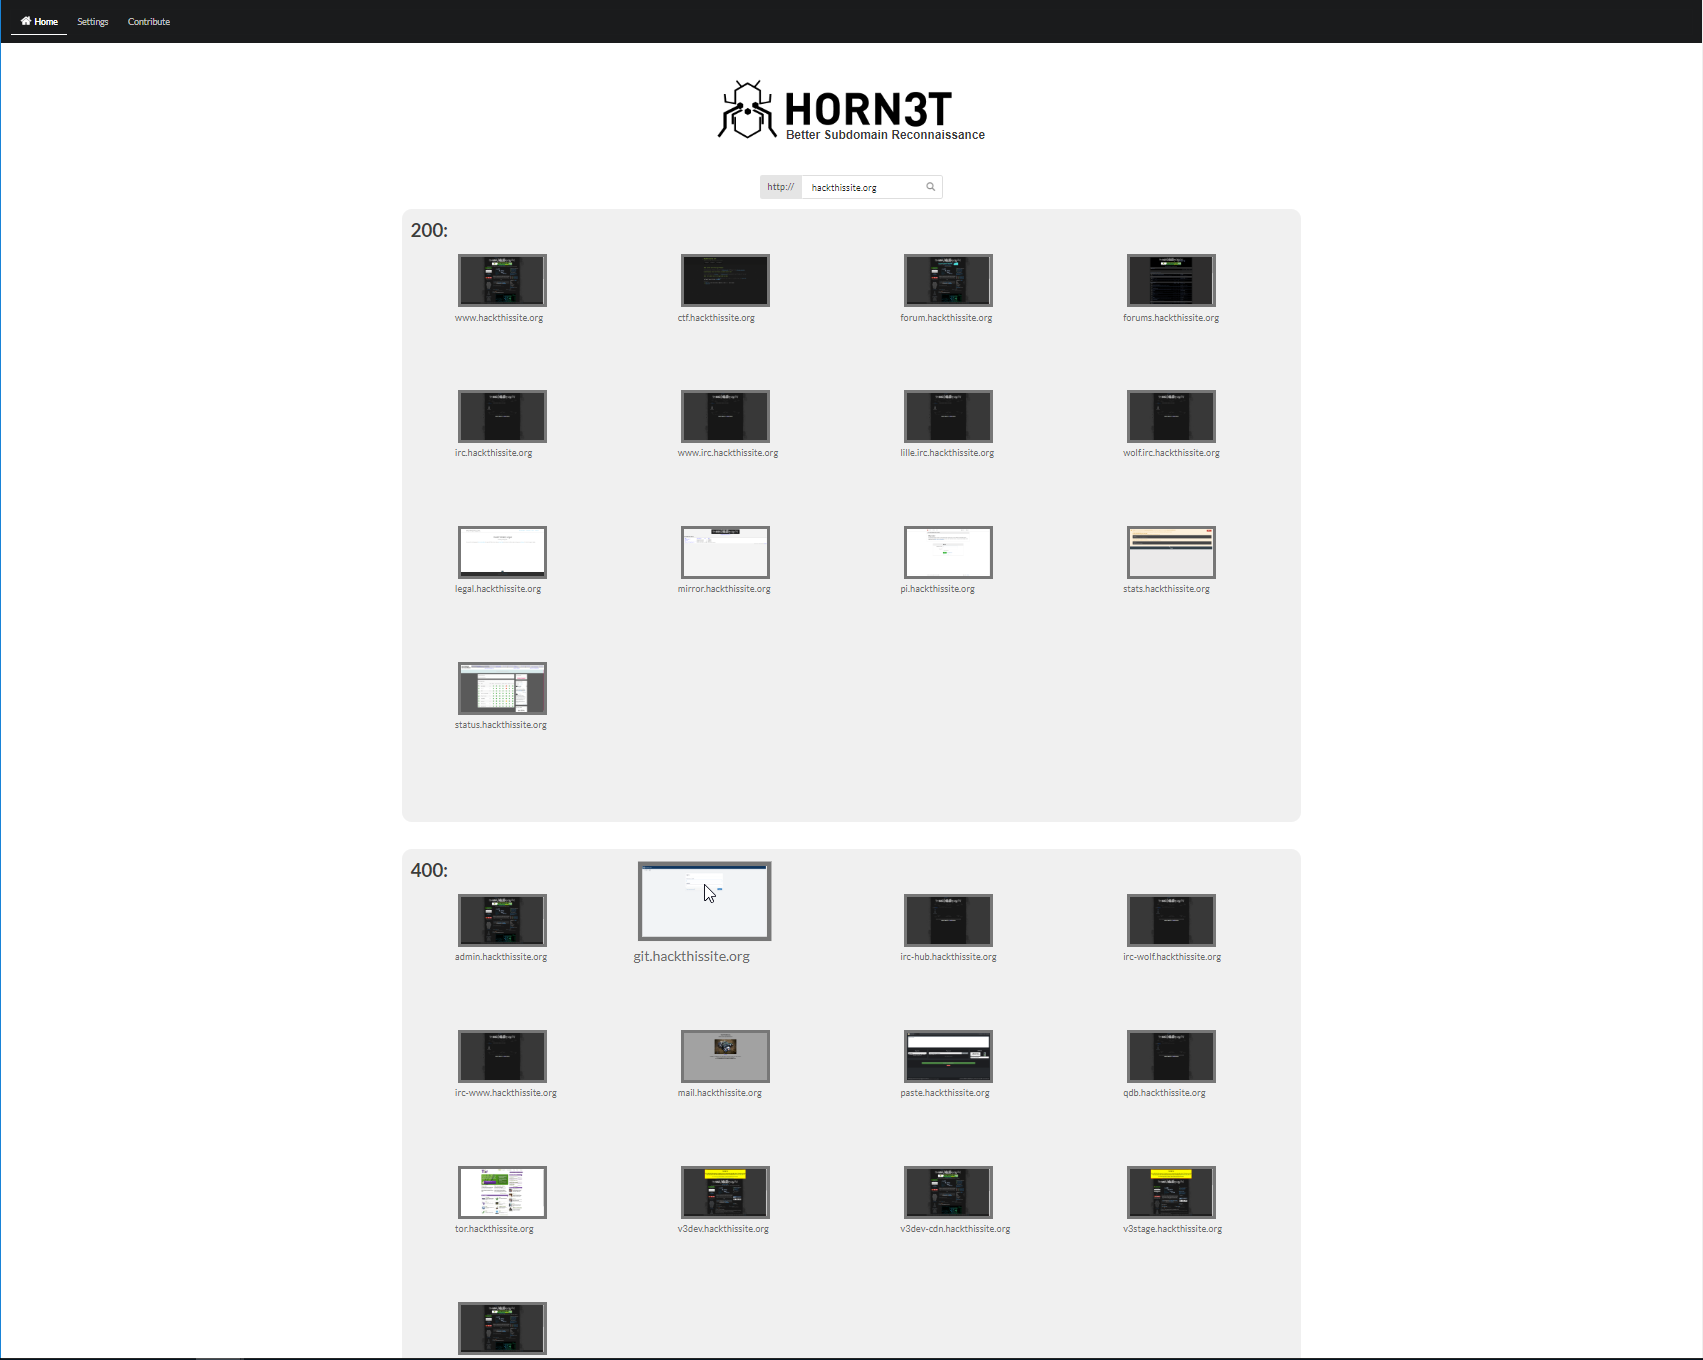 janniskirschner/horn3t
Powerful Visual Subdomain Enumeration at the Click of a Mouse
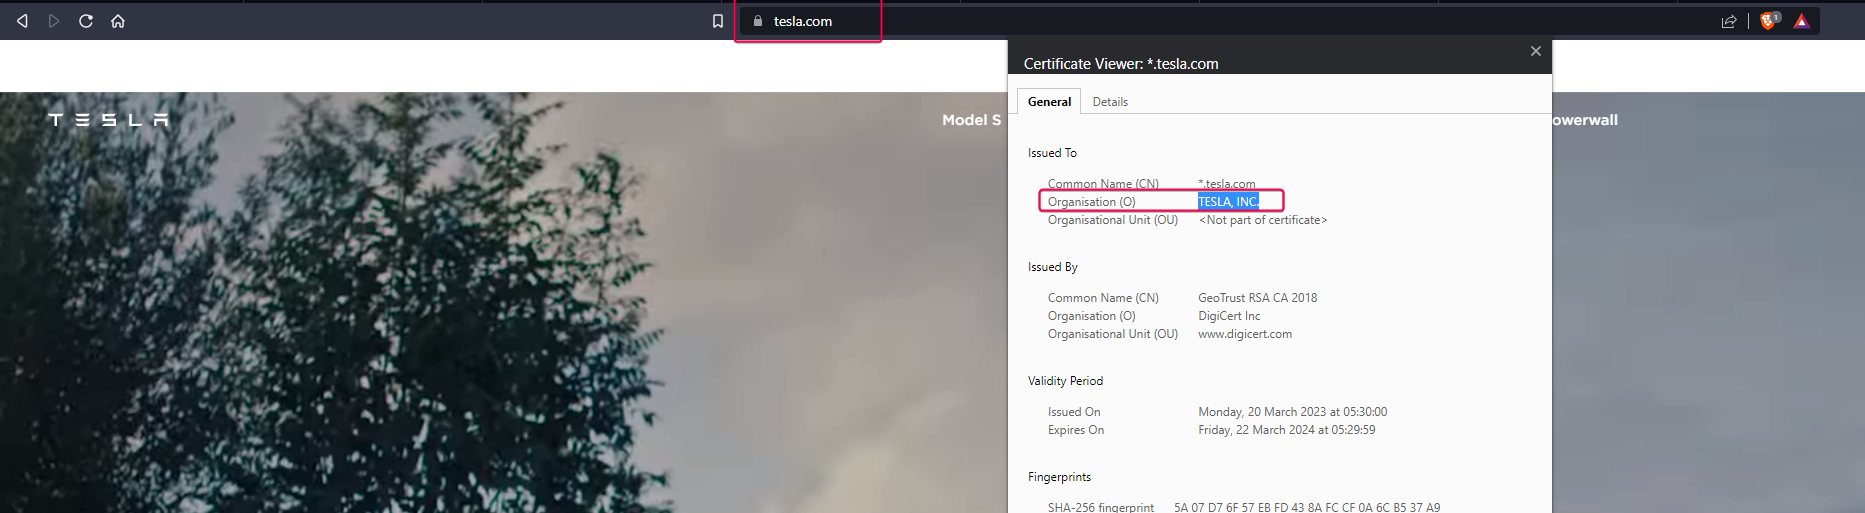 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 samhaxr/takeover-v1
Takeover script extracts CNAME record of all subdomains at once. TakeOver saves researcher time and increase the chance of finding subdomain takeover…
 jevalenciap/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
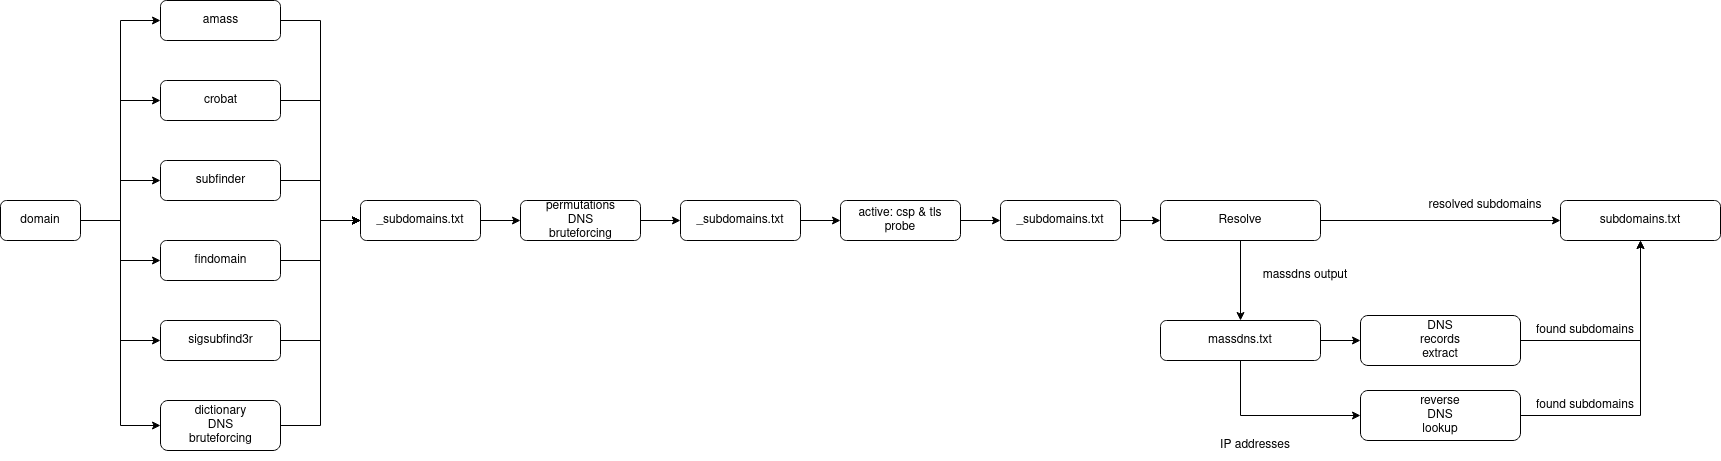 enenumxela/subdomains.sh
A wrapper around tools used for subdomain enumeration, to automate the workflow, on a given domain, written in bash.
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
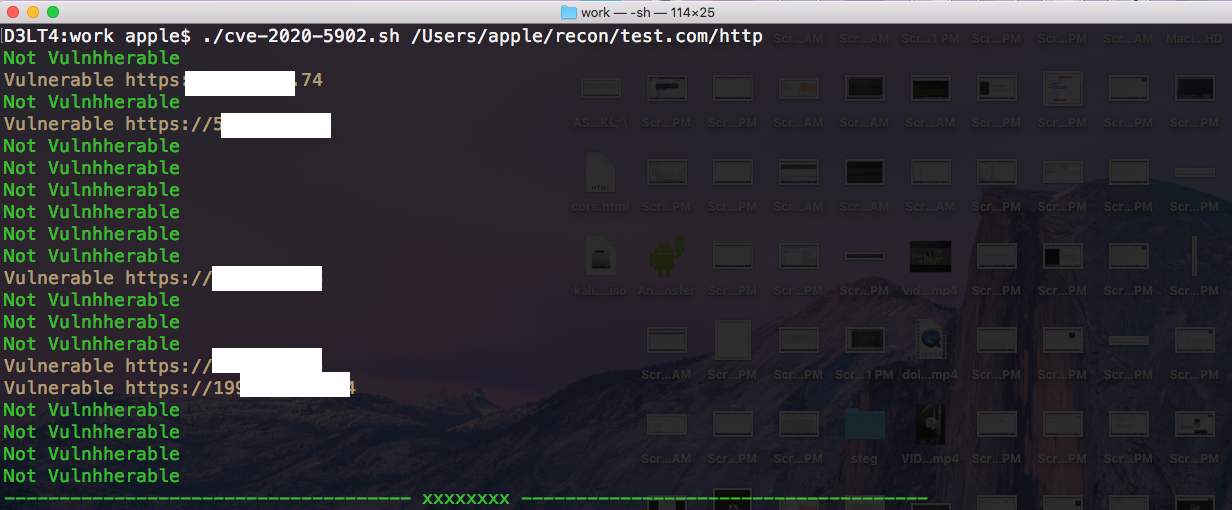 govindpalakkal/evilrip
It is a small script to fetch out the subdomains/ip vulnerable to CVE-2020-5902 written in bash
 jenderal92/reverse_ip_multithreading1
Multithreaded reverse IP lookup tool for discovering domains hosted on the same IP address.
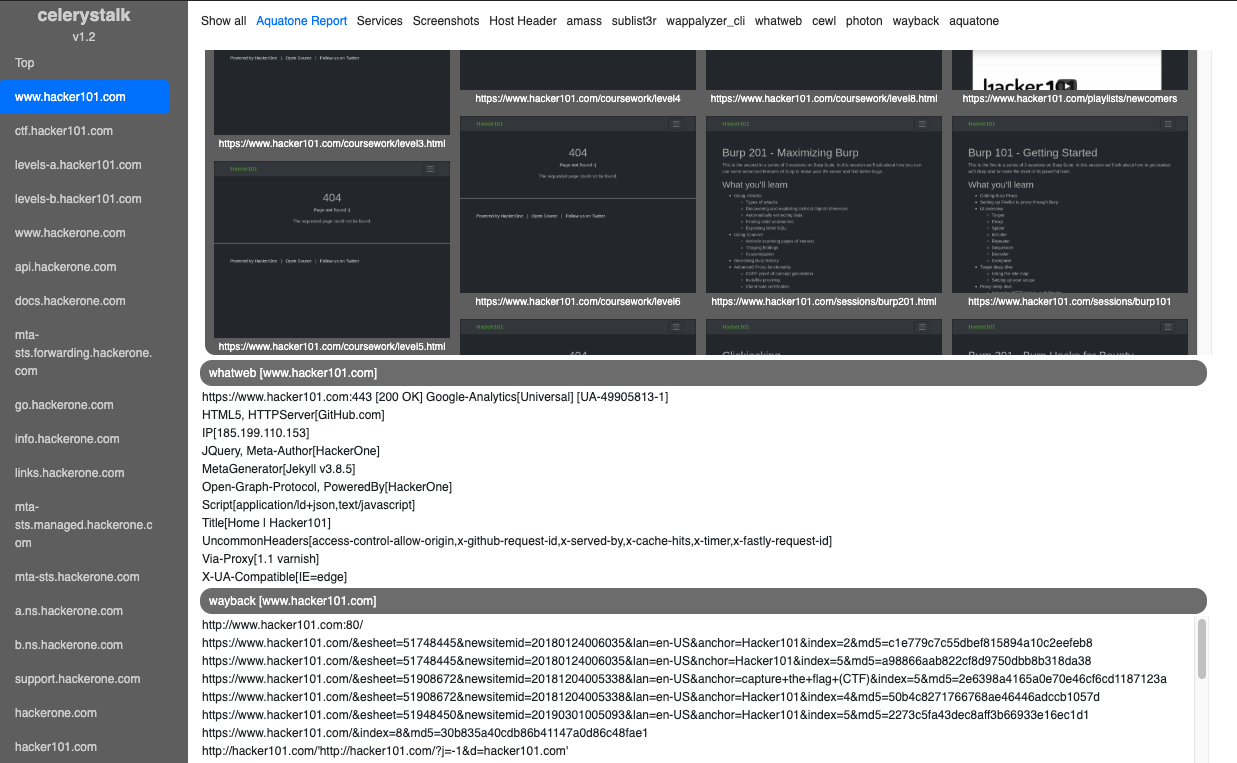 sethsec/celerystalk
An asynchronous enumeration & vulnerability scanner. Run all the tools on all the hosts.