

HOCig1_2
 hackersonlineclub/hocig1_2
HOCig- Automatic HOC Information Gathering Tool V 1.2
dns-analysisemail-securityinformation-gathering+5
11
hackersonlineclub/hocig1_2HOCig- Automatic HOC Information Gathering Tool V 1.2
 whitelisthackers/wosind
An OSINT tool for collecting public information.
 projectdiscovery/dnsx-action
Fast and multi-purpose DNS toolkit allow to run multiple DNS queries.
 himori123/-cve-2023-30845
Explore CVE 2023-30845 automatically across multiple subdomains
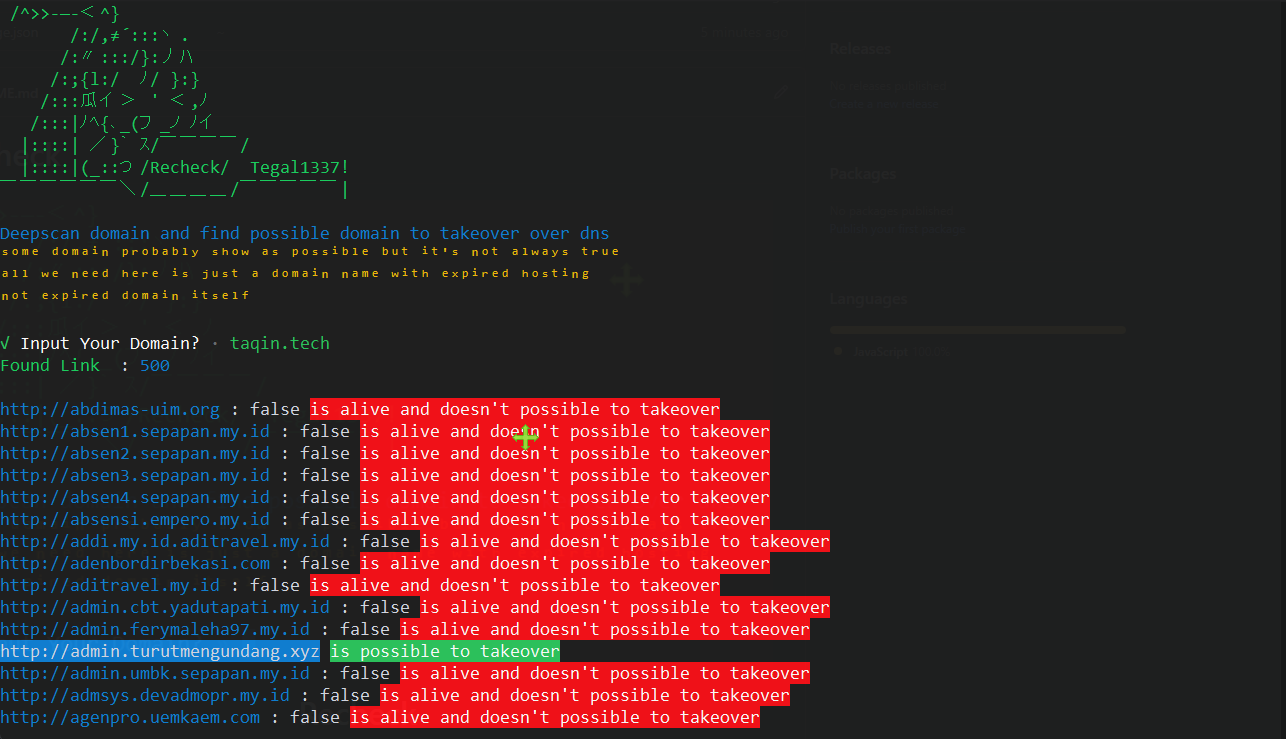 tegal1337/recheck
Deep scan domain and find all possible domain to takeover
 xpl0ited1/submonitor
Subdomain monitor with reporting capabilities to Slack, Discord and Telegram
 shifa123/cve-2020-13942-poc-
CVE-2020-13942 POC + Automation Script
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
 abaykan/getsubdomain
Get subdomain list and check whether they are active or not by each response code. Using API by c99.nl
 piratesshield/arise-xti
AI-driven external attack surface management pipeline: 28 modules for recon, subdomain/DNS enumeration, web/API/cloud vulnerability scanning, OSINT…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 cyberblackhole/domain-to-webapp
Bash script that enumerates subdomains via Subfinder, resolves IPs, and identifies live web applications hosted on a domain for reconnaissance and…
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 a3h1nt/sububy
Modular subdomain enumeration suite with certificate transparency, DNS brute-force, and API-based discovery. Includes post-enumeration modules for…
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).

 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 renatus-cartesius/reconswarm
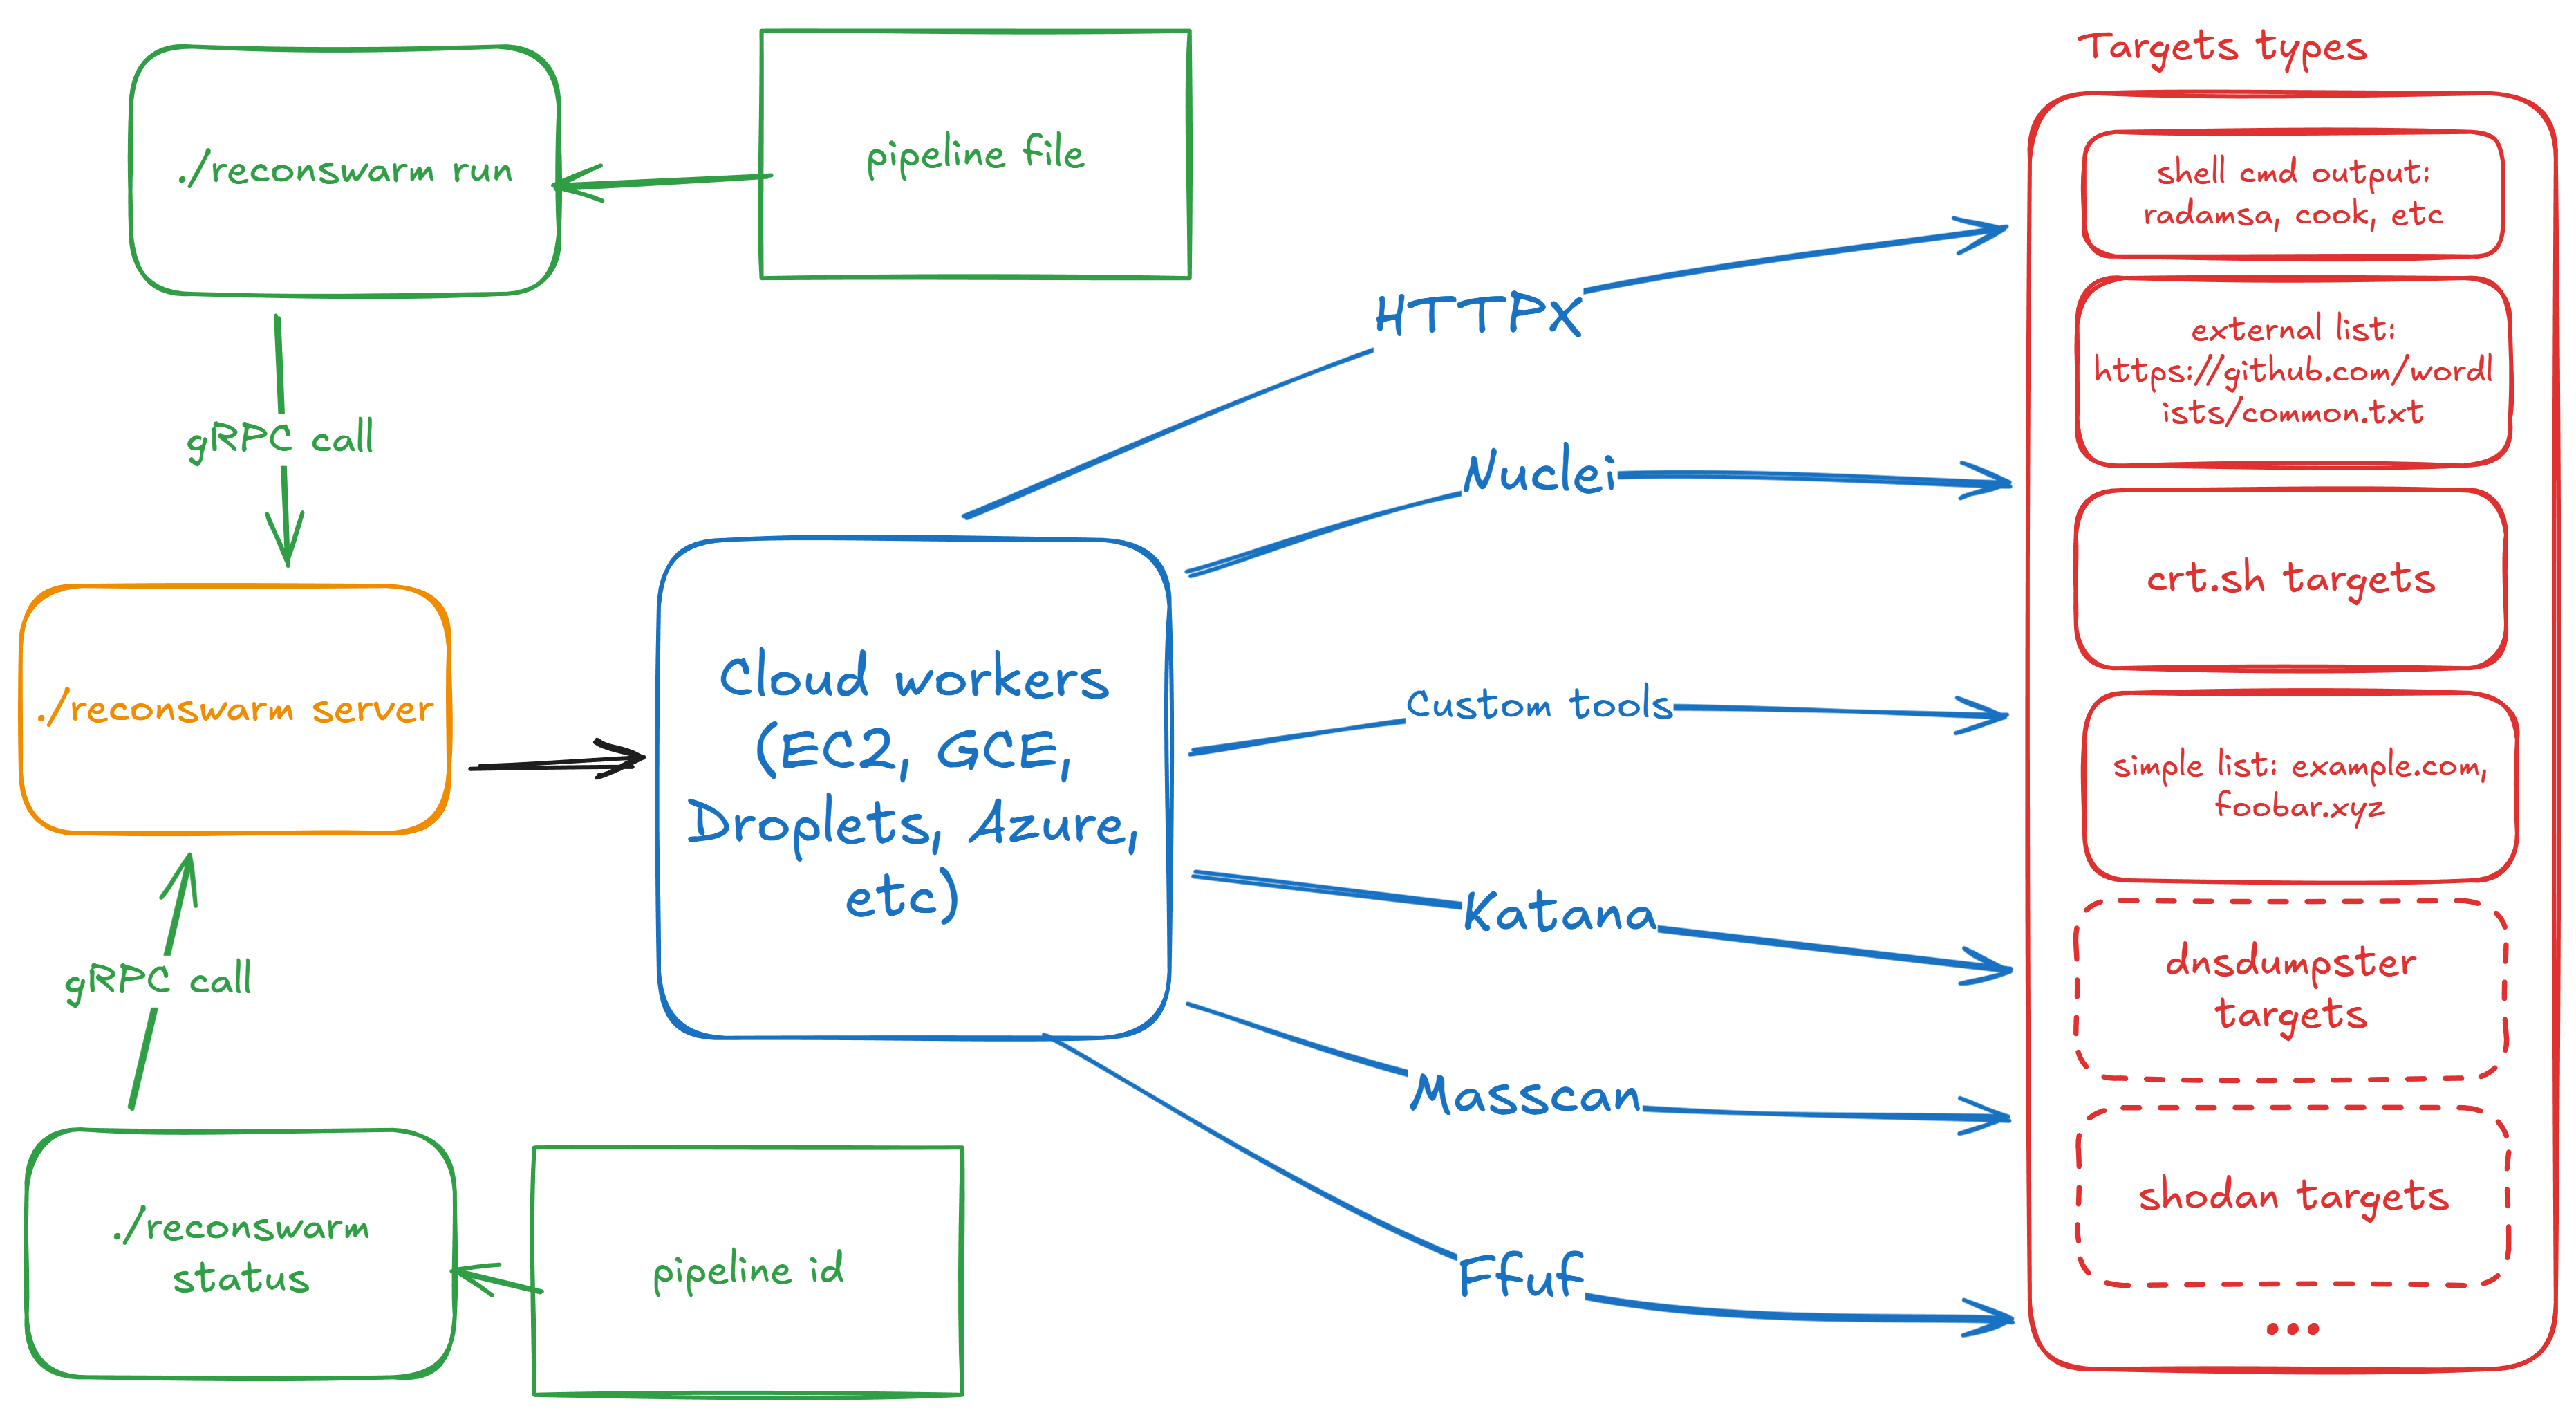
Extend your recon with cloud power