
 piratesshield/arise-xti
AI-driven external attack surface management pipeline: 28 modules for recon, subdomain/DNS enumeration, web/API/cloud vulnerability scanning, OSINT enrichment and CAPEC attack-path chaining.
Autonomous Recon, Intelligence, Security & Exposure — an AI-powered intelligent Attack Surface Management platform.
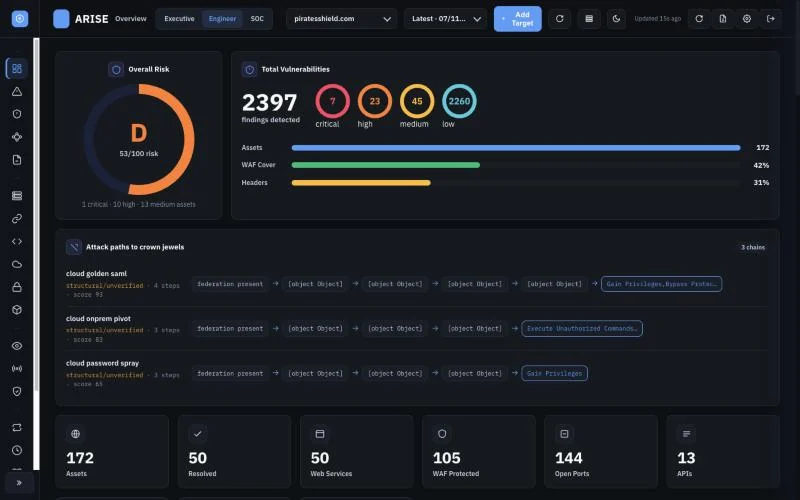
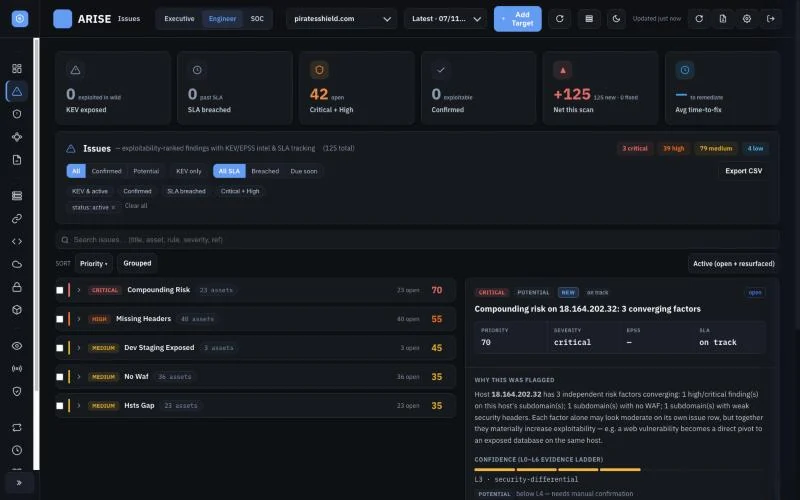
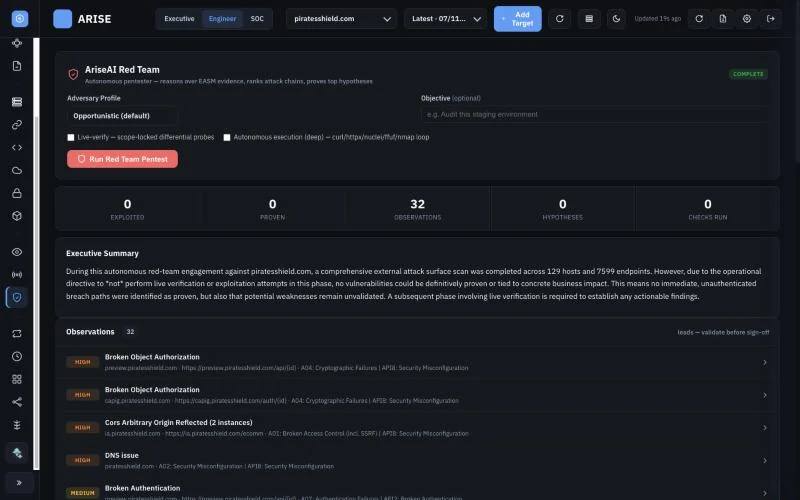
ARISE-XTI turns a single domain into a continuously-monitored external attack surface. A 28-module pipeline runs the full adversary workflow — discovery, enumeration, fingerprinting, web/API/cloud exploitation, OSINT and intel enrichment — then an autonomous AI pentester (AriseAI) reasons over every piece of evidence, ranks attack hypotheses, chains them into CAPEC v3.9 / MITRE ATT&CK kill chains and live-verifies the top candidates. Everything lands in a single Flask dashboard with KEV/EPSS-blended exploitability ranking, L0–L6 evidence ladder, SLA clocks and asset-ledger diffing.
What makes ARISE-XTI different
curl.| Overview — risk score, attack chains, asset ribbon | Issues — KEV/EPSS-ranked, SLA-tracked |
 |  |
| Attack Surface — adversary-perspective inventory | Attack Paths — CAPEC chains to crown jewels |
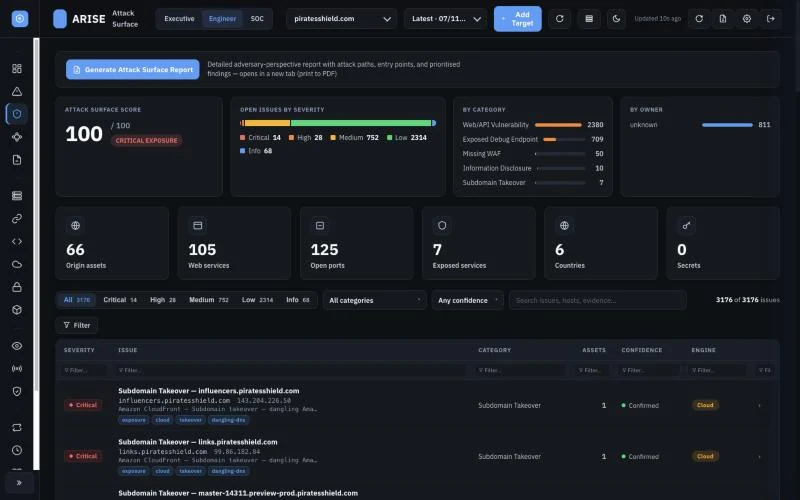 |  |
| CVEs — KEV/EPSS-blended | Assets — all hosts, IPs, WAF/CDN posture |
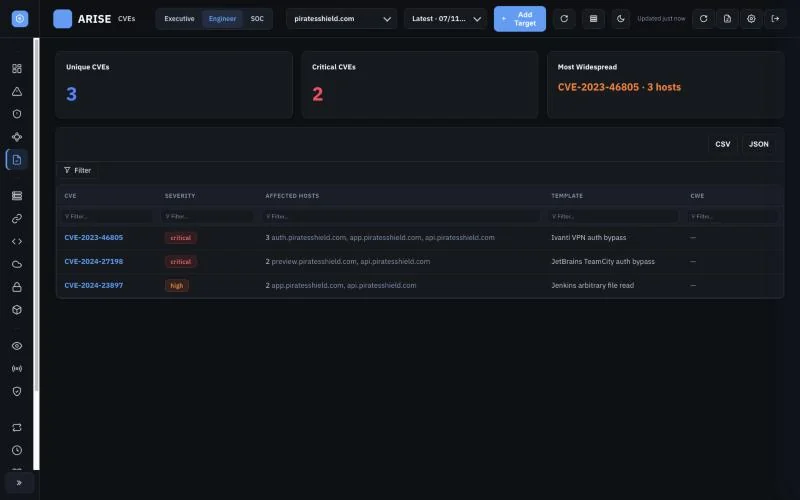 | 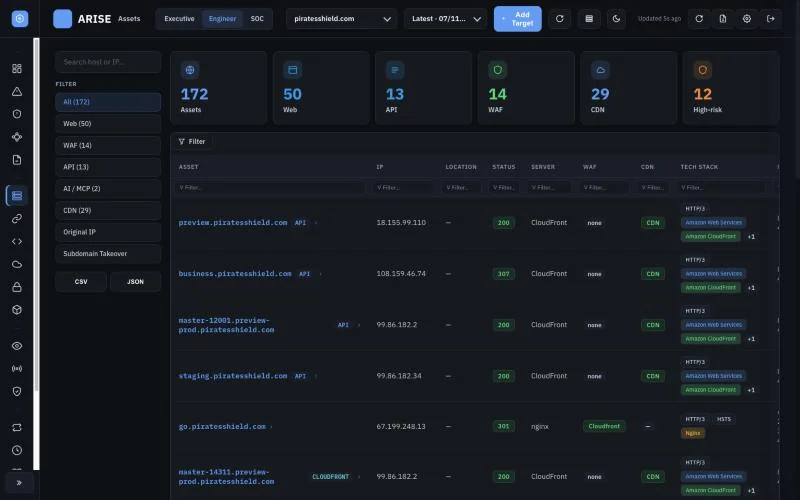 |
| URL Inventory — classified endpoints | API Security — BOLA/BFLA with evidence ladder |
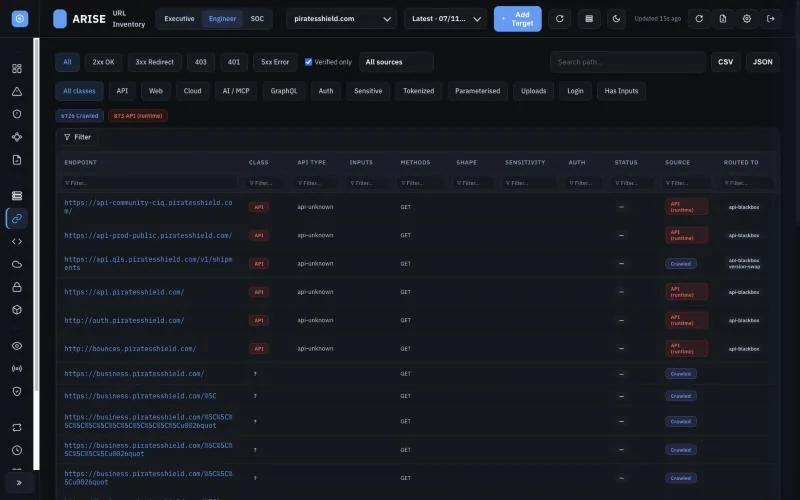 | 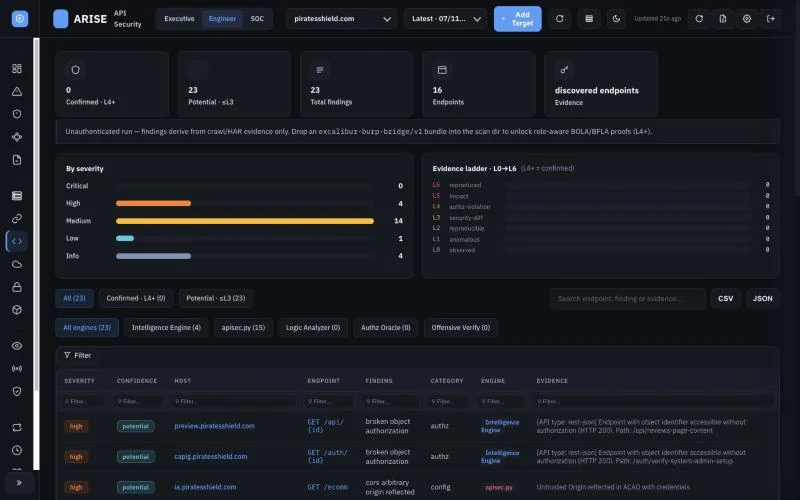 |
| Cloud — AWS/GCP/Azure + takeover chain | SSL / TLS — SSL-Labs-style per-host grades |
 | 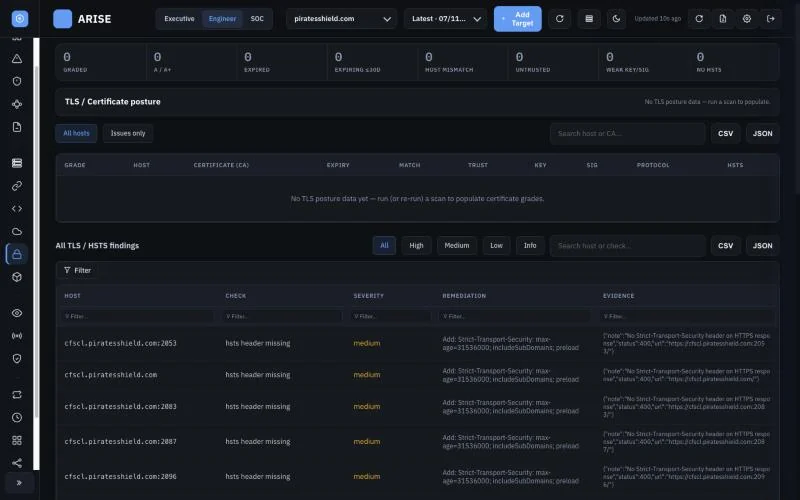 |
| SBOM — components × versions × hosts | OSINT — brand, breach, code, impersonation |
 | 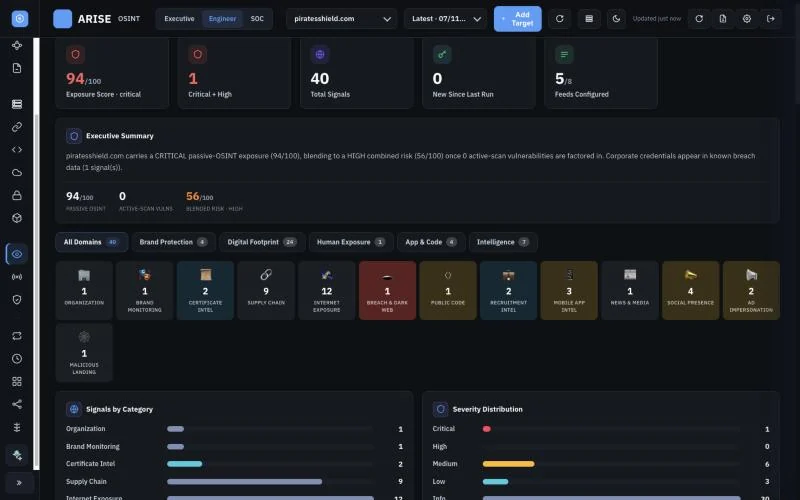 |
| Shodan — external-view correlation | Red Team — AriseAI autonomous pentester |
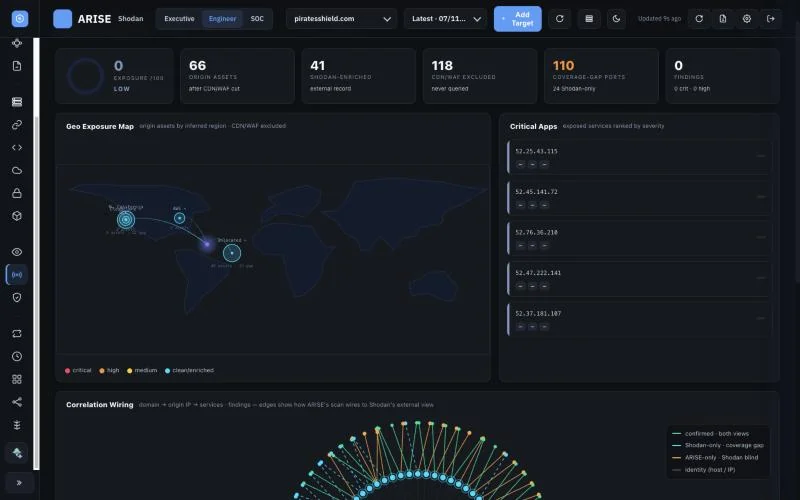 |  |
| Changes — asset / port / finding diff | |
 |
docker run -d --name arisexti -p 5059:5059 \
  -v arisexti-scans:/app/scans \
  -v arisexti-state:/app/state \
  piratesshield/arisexti:latest
Open http://localhost:5059 → log in with admin / admin.
Image: piratesshield/arisexti on Docker Hub.
./setup.sh                                          # one-shot installer (macOS/Linux)
./easm-pipeline.sh example.com                      # run a scan
python3 dashboard.py                                # open http://localhost:5059
Default login: admin / admin — change ARISE_ADMIN_PASSWORD before exposing the dashboard.
Pick one of the three paths below.
The official image on Docker Hub ships every binary (subfinder, nuclei, naabu, katana, dnsx, puredns, massdns, nmap, Chromium for Playwright, etc.) — no local Go toolchain, no brew/apt, no PATH fights.
# Pull the latest build
docker pull piratesshield/arisexti:latest

# Run the dashboard (host port 5059)
docker run -d --name arisexti \
  -p 5059:5059 \
  -v arisexti-scans:/app/scans \
  -v arisexti-state:/app/state \
  piratesshield/arisexti:latest

# Open http://localhost:5059 (admin / admin)
docker logs -f arisexti
With API keys (recommended — enables AI analyst, Shodan, Censys, etc.):
