
WAES
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
ctfeducationinformation-gathering+7
7010 months ago
shiva108/waesCPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
 e1abrador/sub.monitor
Self-hosted passive subdomain continous monitoring tool.
 janniskirschner/horn3t
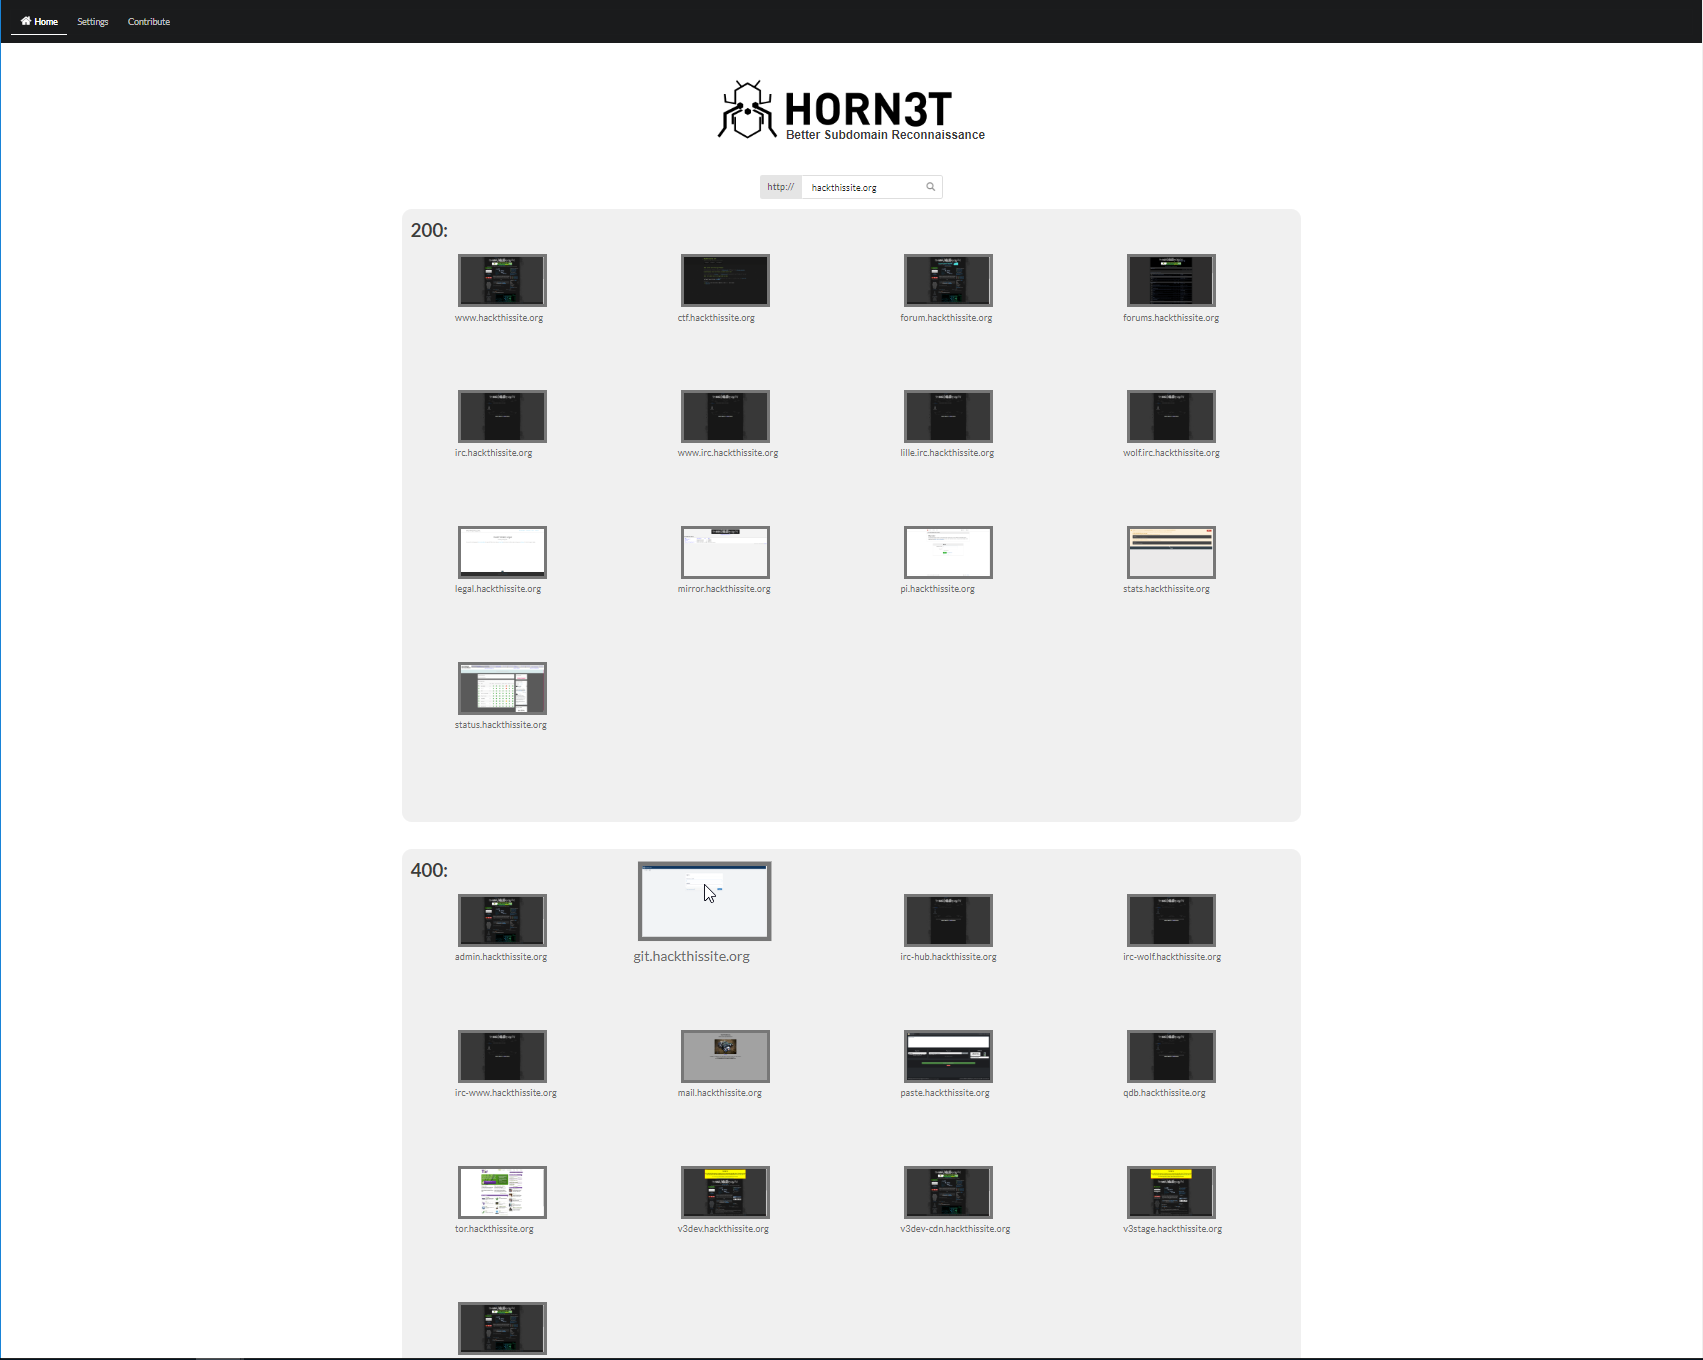
Powerful Visual Subdomain Enumeration at the Click of a Mouse
 billyv4/id-entify
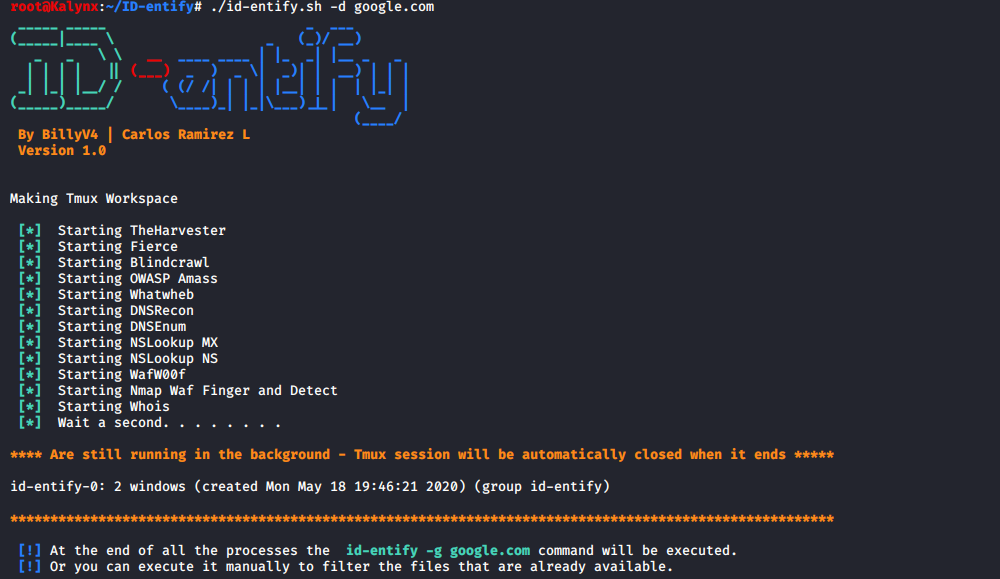
Search for information related to domain: Emails - IP addresses - Sub-Domains - Information on WEB technology - Type of Firewall - NS and MX records.
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 yuyudhn/azsubenum
DNS-based subdomain enumeration tool for Azure services, probing App Services, Storage Accounts, Databases, Key Vaults, and CDN endpoints via…
 smiegles/mass3
Multi-threaded DNS-based enumeration tool for discovering AWS S3 buckets using pre-compiled wordlists and custom DNS resolvers, with optional Docker…
 samhaxr/takeover-v1
Takeover script extracts CNAME record of all subdomains at once. TakeOver saves researcher time and increase the chance of finding subdomain takeover…
 cujanovic/subdomain-bruteforce-list
Large wordlist (34M+ entries) for subdomain bruteforcing and DNS reconnaissance during penetration testing and attack surface discovery.
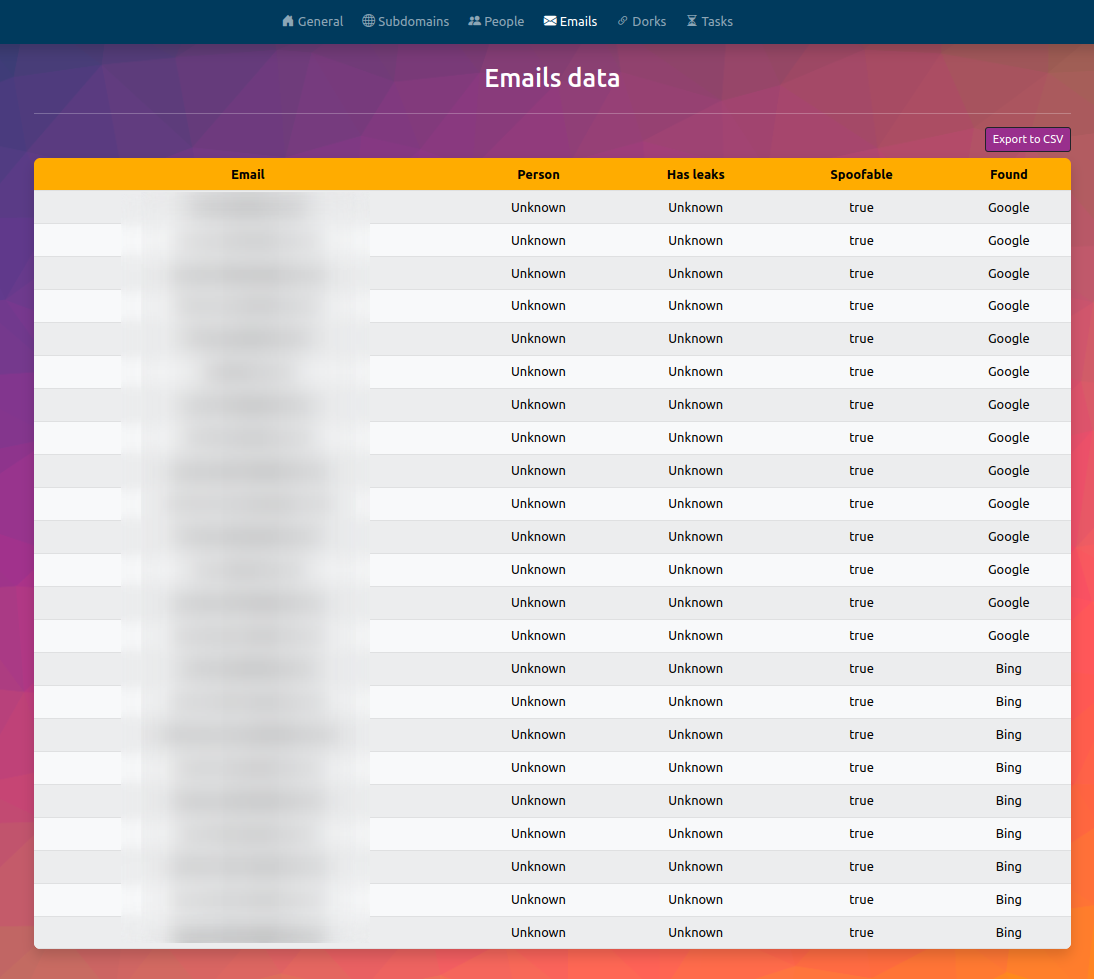 fundacio-i2cat/infohound
InfoHound is an OSINT to extract a large amount of data given a web domain name.
 0xbharath/domains-from-csp
A script to extract domain names from Content Security Policy(CSP) headers
 offxec/pavelow
PAVELOW Exploit Toolbox is a BASH script that corresponds with your KALI distro to better help your vulnerability hunting and exploiting proccess…
 jevalenciap/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
 pikpikcu/nuubi
Nuubi Tools (Information-ghatering|Scanner|Recon.)
 dariusztytko/vhosts-sieve
Searching for virtual hosts among non-resolvable domains
 n4xh4ck5/n4xd0rk
Listing subdomains about a main domain
 pry0cc/subgen
A really simple utility to concate wordlists to a domain name - to pipe into your favourite resolver!
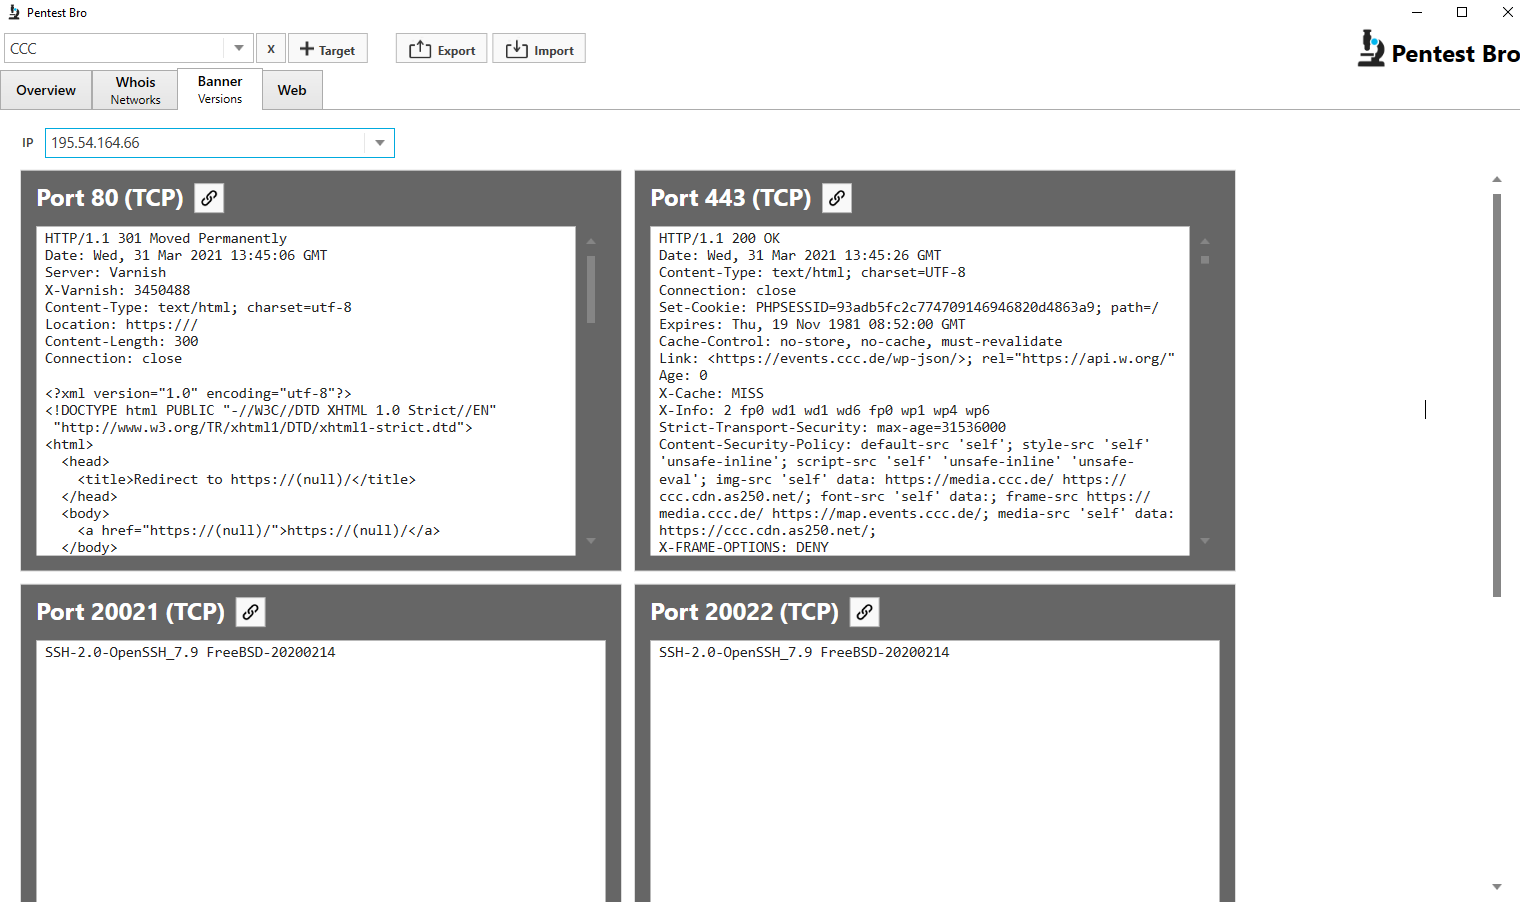 marius-rothenbuecher/pentestbro
Windows-based reconnaissance tool combining subdomain enumeration, port scanning, banner grabbing, whois lookups, and web path enumeration for…