
 yuyudhn/azsubenum
DNS-based subdomain enumeration tool for Azure services, probing App Services, Storage Accounts, Databases, Key Vaults, and CDN endpoints via permutation and resolution techniques.

AzSubEnum is a specialized subdomain enumeration tool tailored for Azure services. This tool is designed to meticulously search and identify subdomains associated with various Azure services. Through a combination of techniques and queries, AzSubEnum delves into the Azure domain structure, systematically probing and collecting subdomains related to a diverse range of Azure services.
AzSubEnum operates by leveraging DNS resolution techniques and systematic permutation methods to unveil subdomains associated with Azure services such as Azure App Services, Storage Accounts, Azure Databases (including MSSQL, Cosmos DB, and Redis), Key Vaults, CDN, Email, SharePoint, Azure Container Registry, and more. Its functionality extends to comprehensively scanning different Azure service domains to identify associated subdomains.
With this tool, users can conduct thorough subdomain enumeration within Azure environments, aiding security professionals, researchers, and administrators in gaining insights into the expansive landscape of Azure services and their corresponding subdomains.
During my learning journey on Azure AD exploitation, I discovered that the Azure subdomain tool, Invoke-EnumerateAzureSubDomains from NetSPI, was unable to run on my Debian PowerShell. Consequently, I created a crude implementation of that tool in Python.
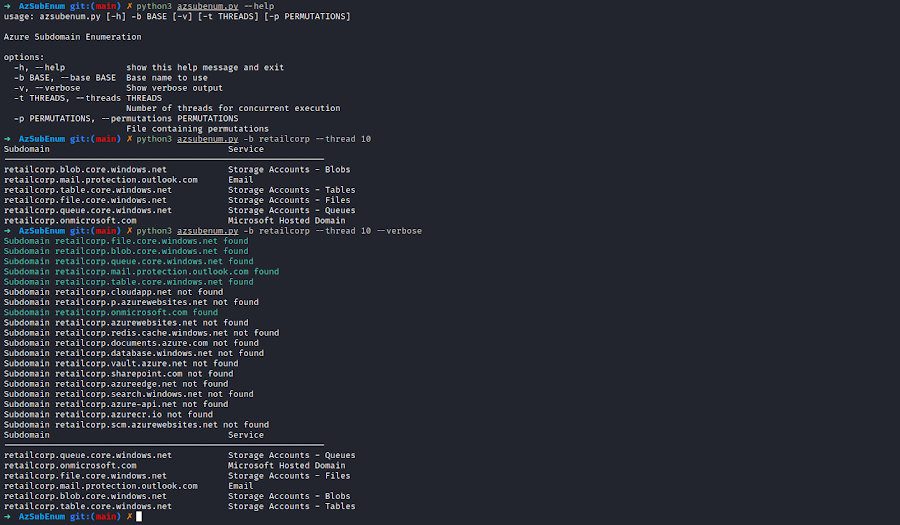
➜  AzSubEnum git:(main) ✗ python3 azsubenum.py --help
usage: azsubenum.py [-h] -b BASE [-v] [-t THREADS] [-p PERMUTATIONS]
                    [--blobsenum] [-bw BLOB_WORDLIST] [-bt BLOB_THREADS]

Azure Subdomain Enumeration and Blob Container Access Checker

options:
  -h, --help            show this help message and exit
  -b BASE, --base BASE  Base name to use
  -v, --verbose         Show verbose output
  -t THREADS, --threads THREADS
                        Number of threads for concurrent execution
  -p PERMUTATIONS, --permutations PERMUTATIONS
                        File containing permutations
  --blobsenum           Perform blob container enumeration
  -bw BLOB_WORDLIST, --blob-wordlist BLOB_WORDLIST
                        Path to a custom wordlist file for blob container
                        enumeration
  -bt BLOB_THREADS, --blob-threads BLOB_THREADS
                        Number of threads to use for blob container
                        enumeration
Basic enumeration:
python3 azsubenum.py -b retailcorp --threads 10
Using permutation wordlists:
python3 azsubenum.py -b retailcorp --threads 10 --permutations permutations.txt
With verbose output:
python3 azsubenum.py -b retailcorp --threads 10 --permutations permutations.txt --verbose
Blob container enumeration:
python3 azsubenum.py -b retailcorp --threads 10 --blobsenum
python3 azsubenum.py -b retailcorp --threads 10 --blobsenum -bt 10
python3 azsubenum.py -b retailcorp --threads 10 --blobsenum --blob-wordlist custom_wordlist.txt --blob-threads 10
Do you have any ideas on how to enhance this tool? Let's contribute!
BSD-3-Clause. Free to use, modify, and redistribute (including commercially), provided the copyright notices are retained. See LICENSE. Based on NetSPI/MicroBurst (BSD-3-Clause).
Any actions and or activities related to the material contained within this tool is solely your responsibility. The misuse of the information in this tool can result in criminal charges brought against the persons in question.






