
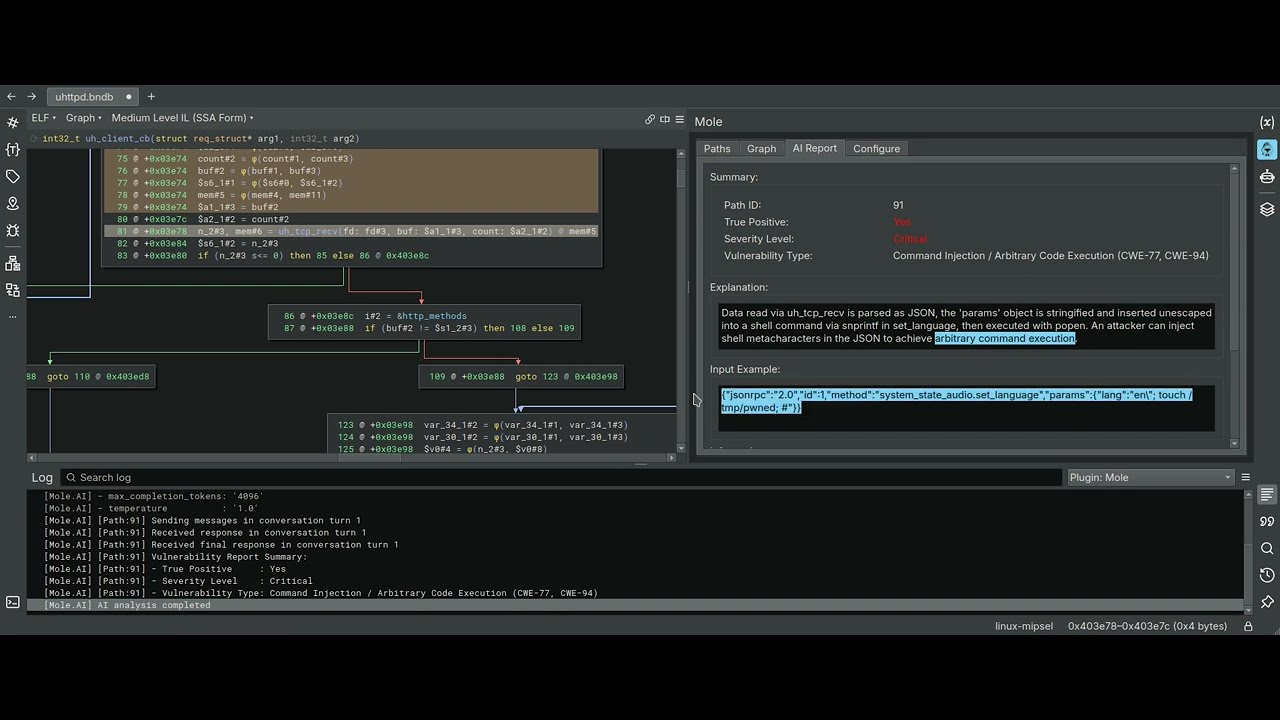
mole
 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
ai-assisted-reversingbinary-analysiscode-analysis+4
86
cyber-defence-campus/moleA Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 ea/xfg_analyzer
A Binary Ninja plugin that uses bruteforced XFG hashes to recover precise function prototypes
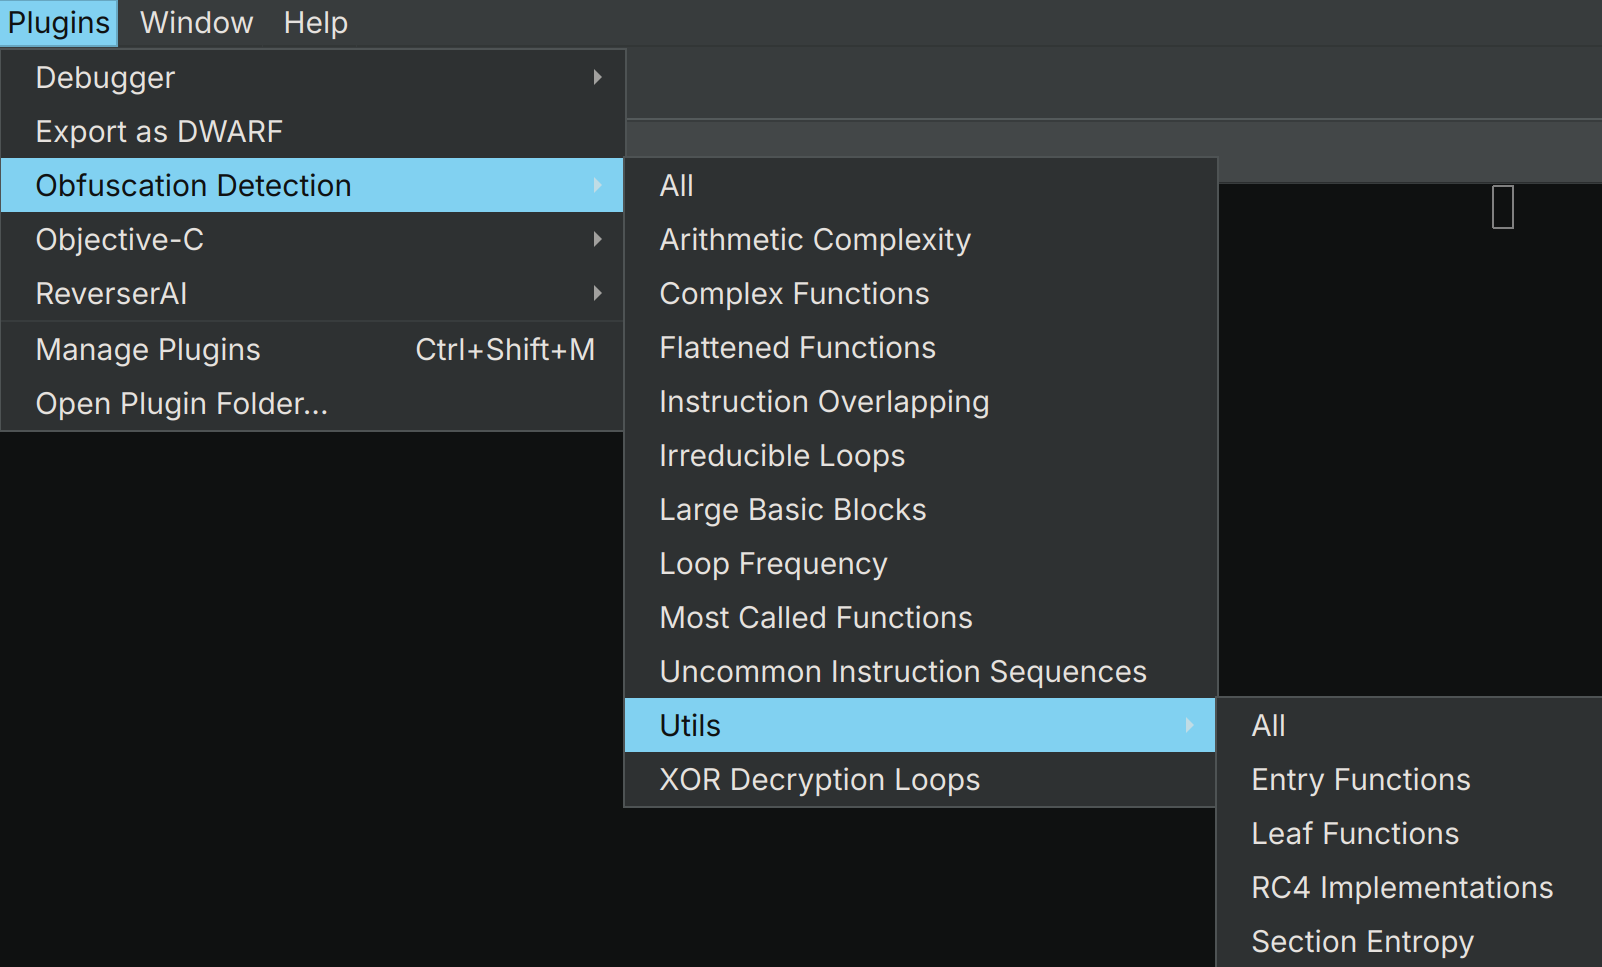 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 gmh5225/ghidra_svr_bridge
Binary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
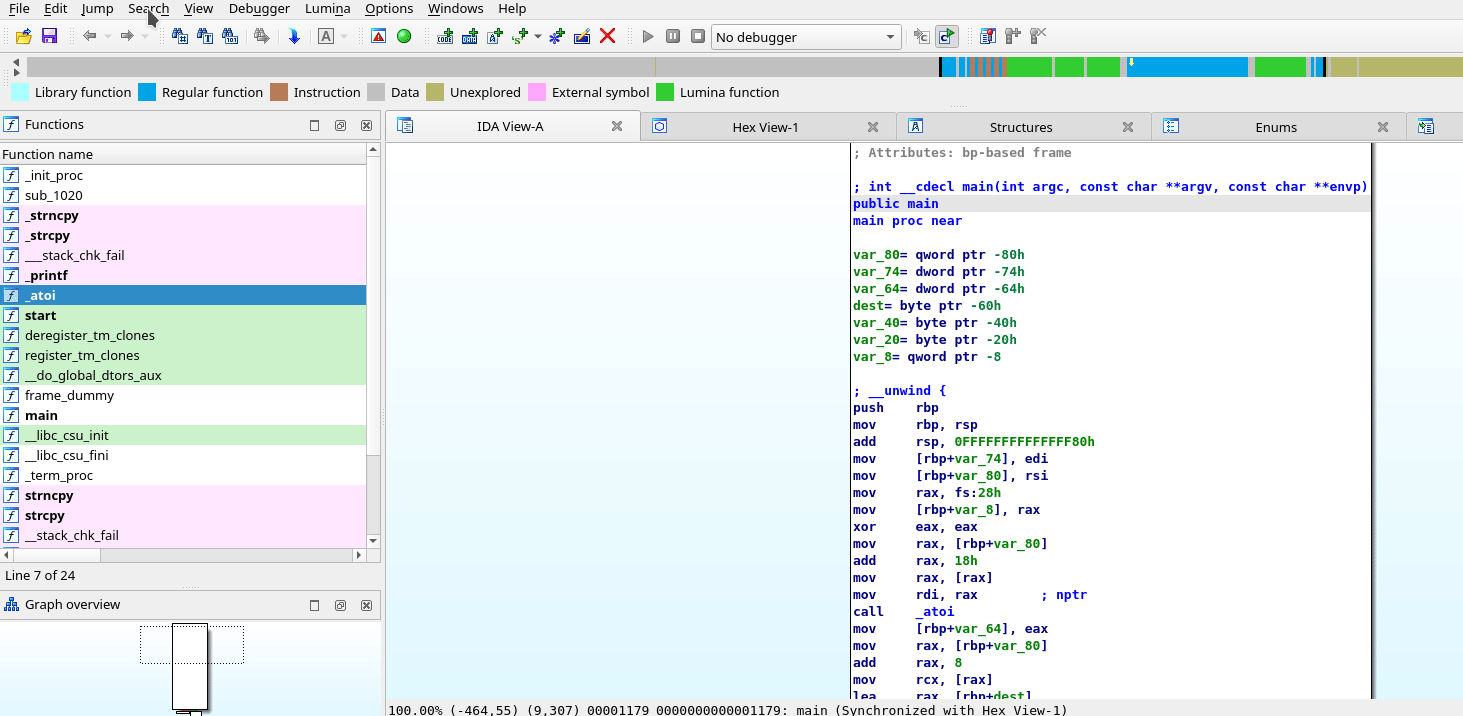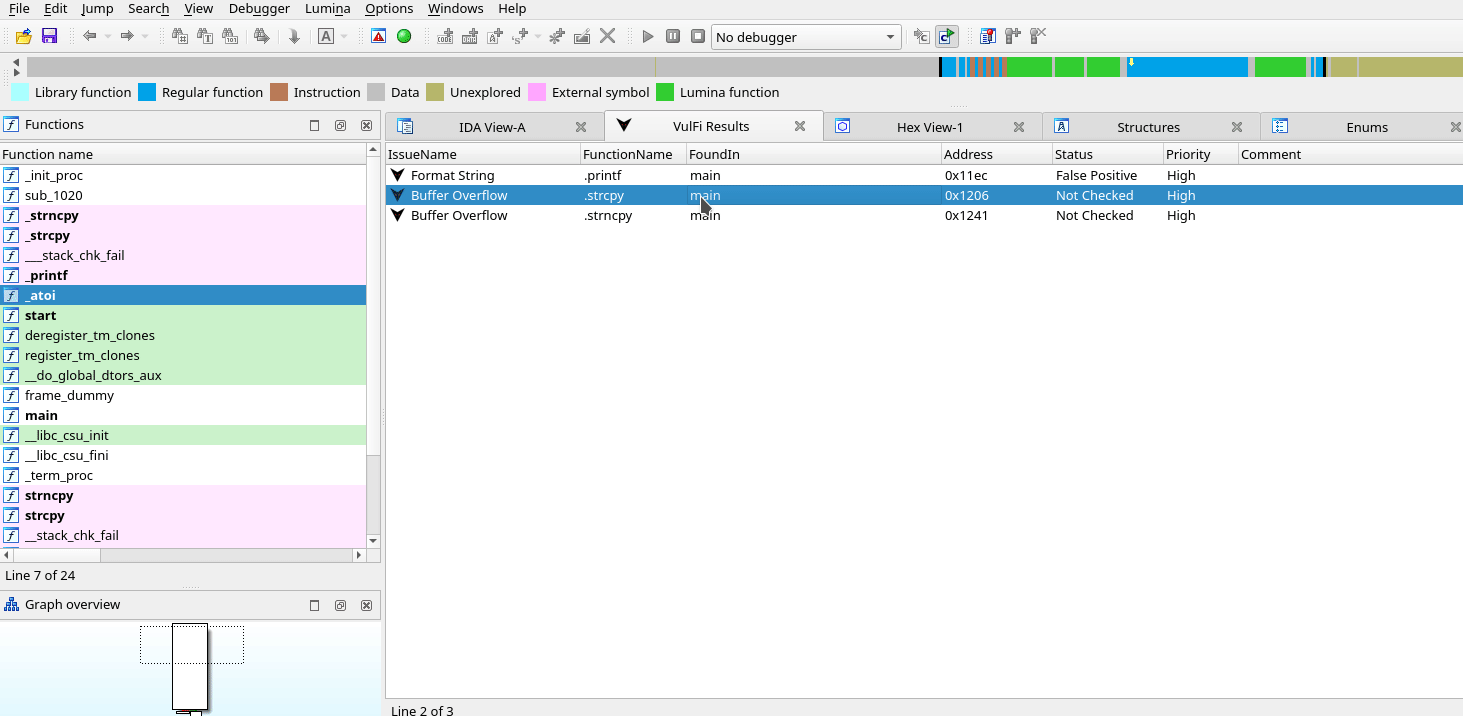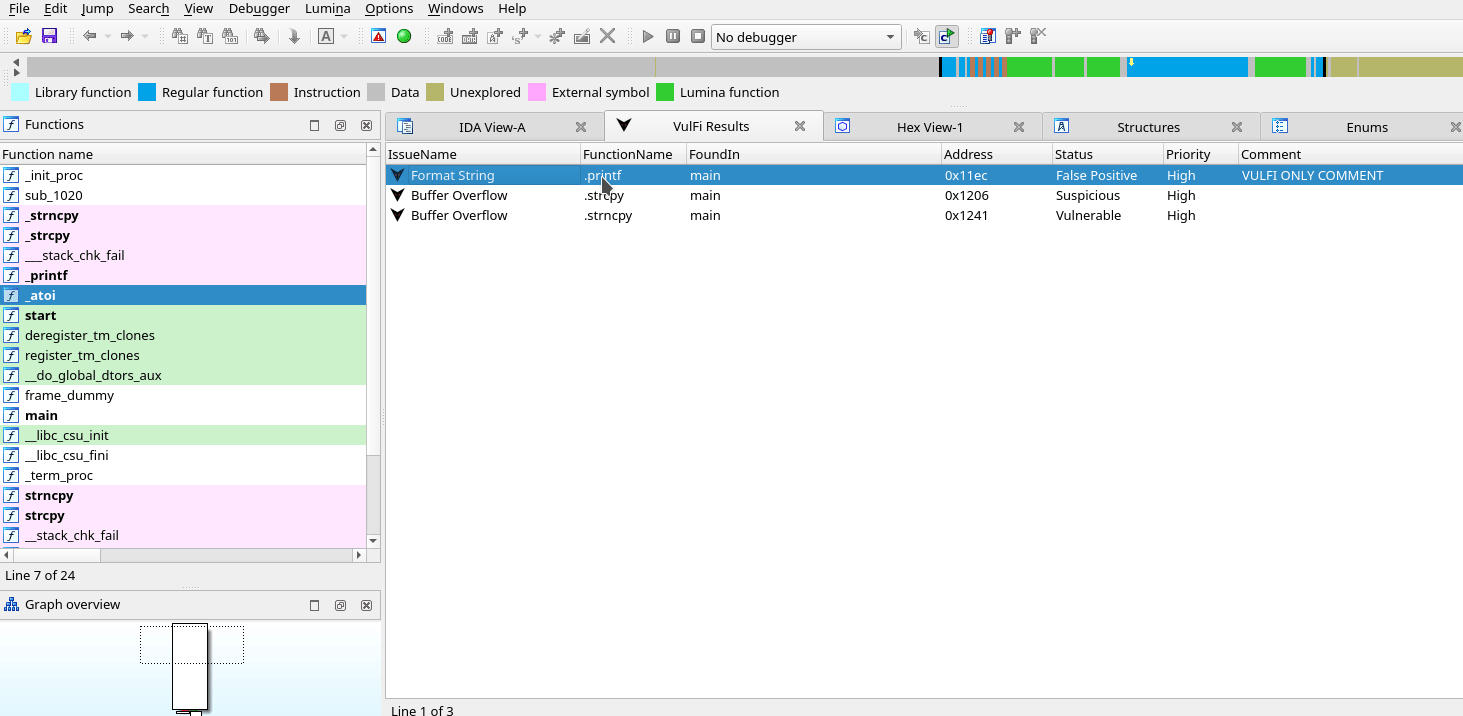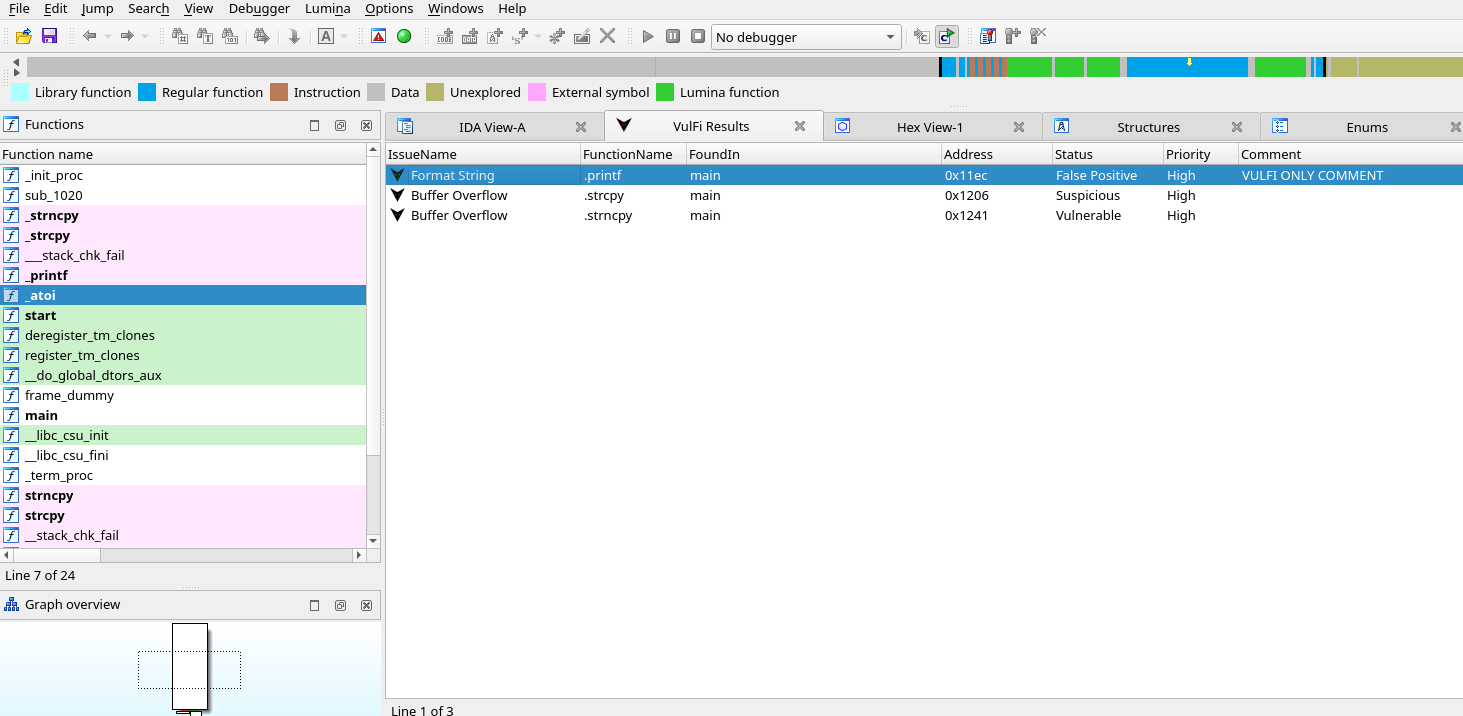 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules
 synacktiv/bip
Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
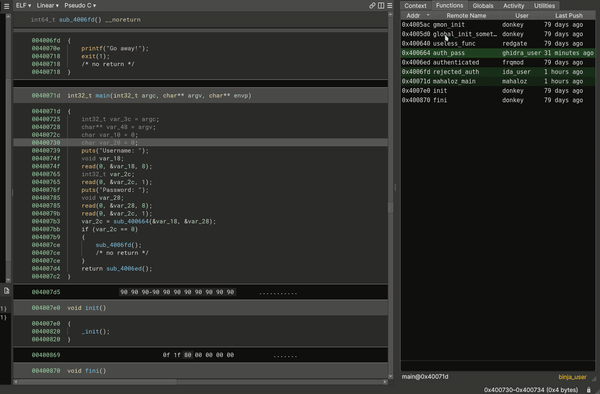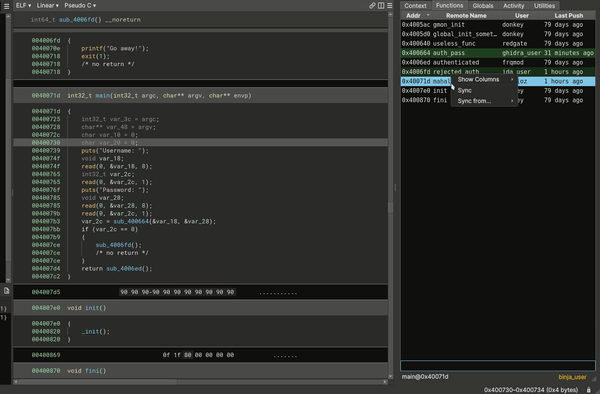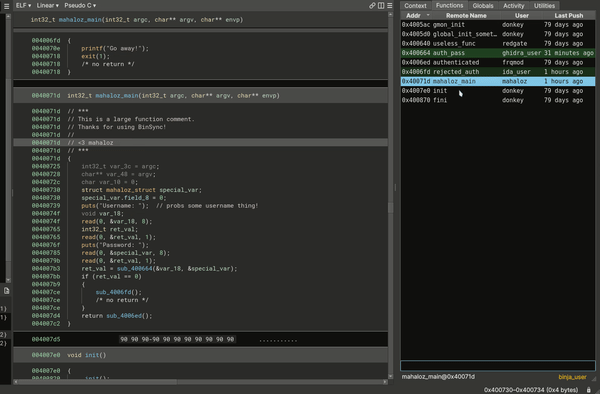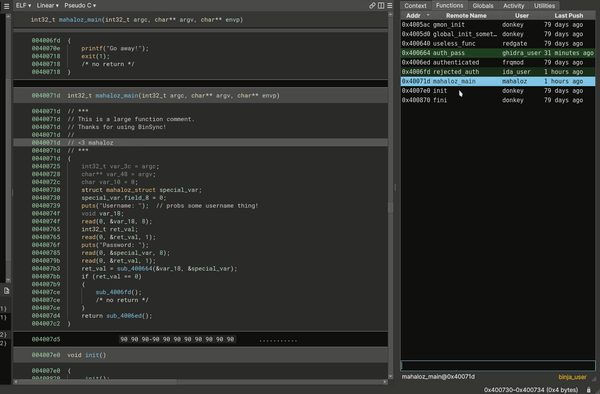 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
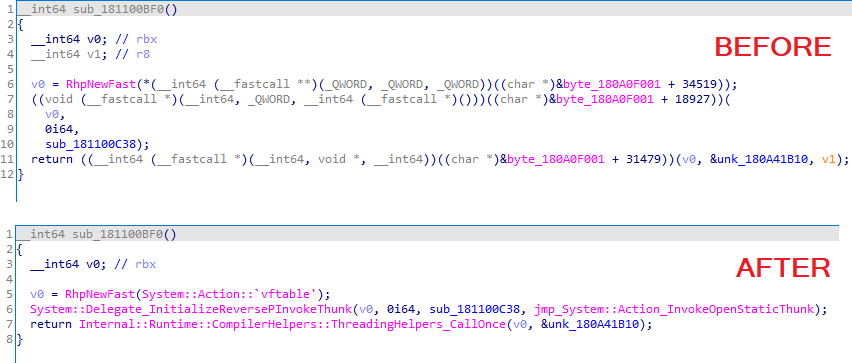 synacktiv/dotniet
IDA Pro plugin that imports runtime-resolved symbols in .NET Native binaries, parsing SharedLibrary.dll and its PDB to restore missing imports for…
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
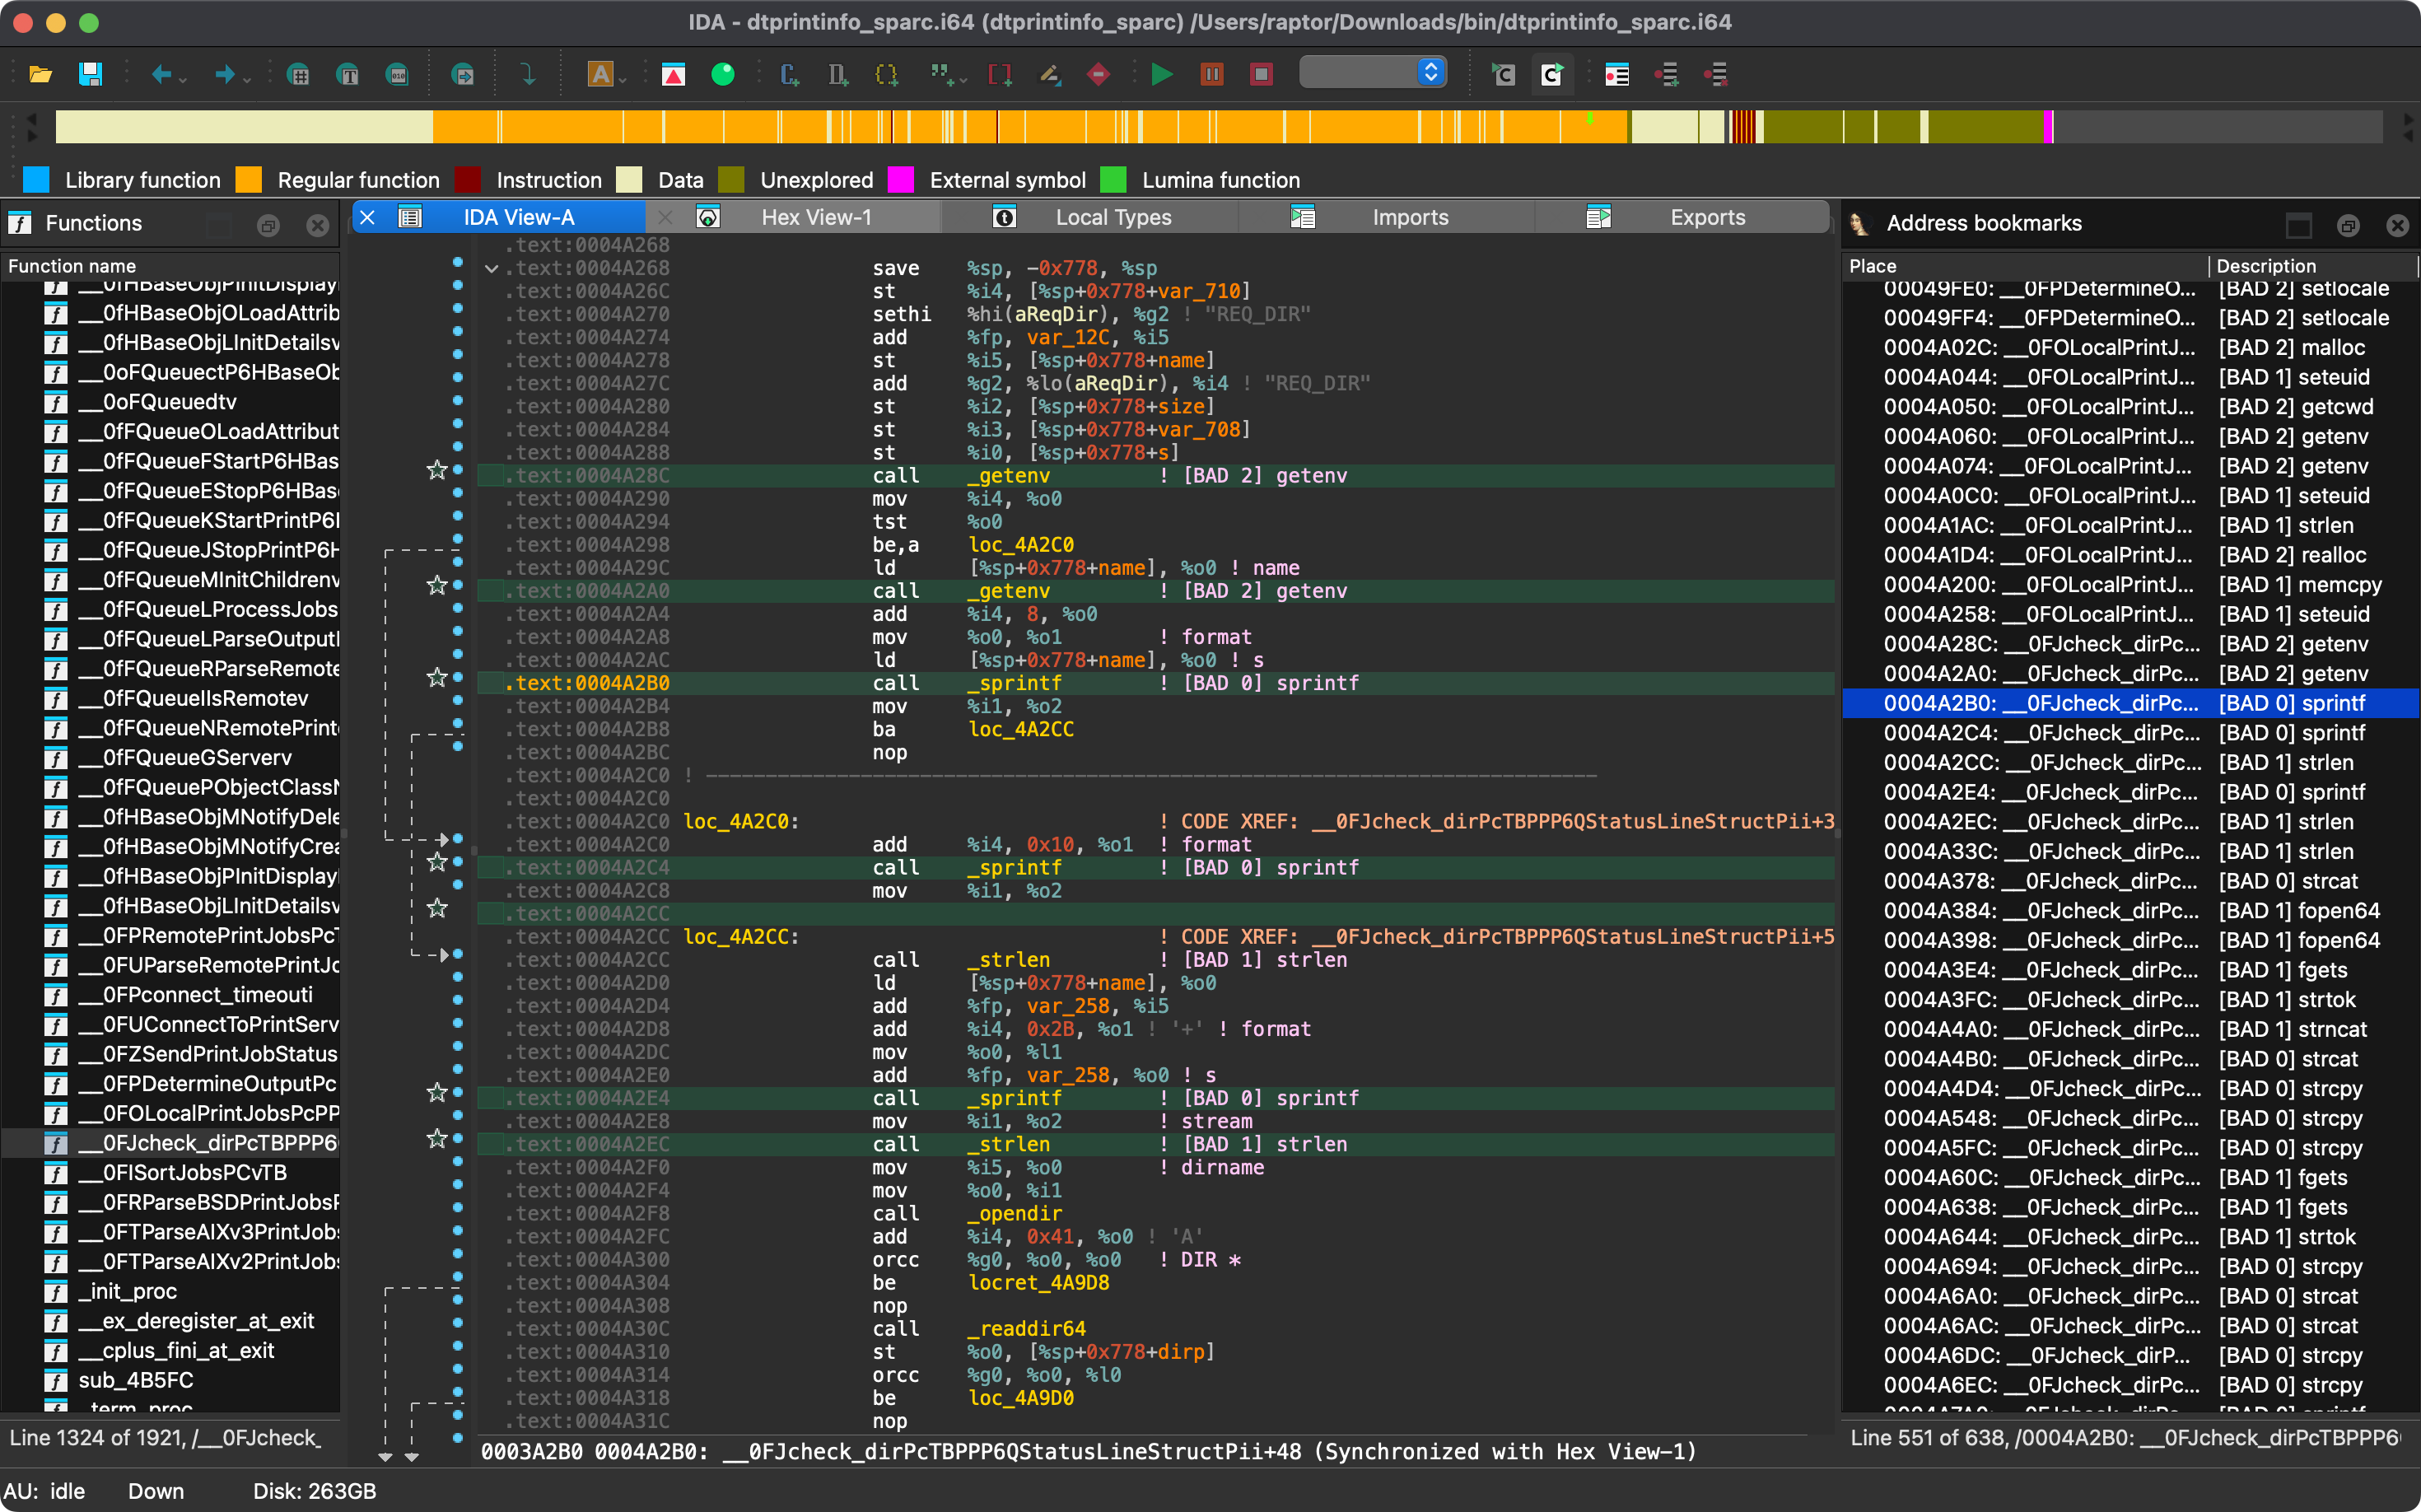 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 inettgmbh/checkmk-log4j-scanner
Checkmk extension that scans JAR, WAR, EAR, and AAR files for Log4j versions vulnerable to CVE-2021-44228 by inspecting META-INF pom.properties…
 ikkisoft/parrotng
Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!