msf_shellcode_analysis

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…

Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…

Educational lab demonstrating CVE-2020-7598 prototype pollution in minimist with a vulnerable Node.js/Express app, exploit payload, and…

Exploit for CVE-2018-6574, a Go command injection vulnerability. Provides a targeted payload for testing and validating the flaw in affected systems.

A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…

Documentation and reverse engineering of reCAPTCHA

Simple DDE object detector

CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.

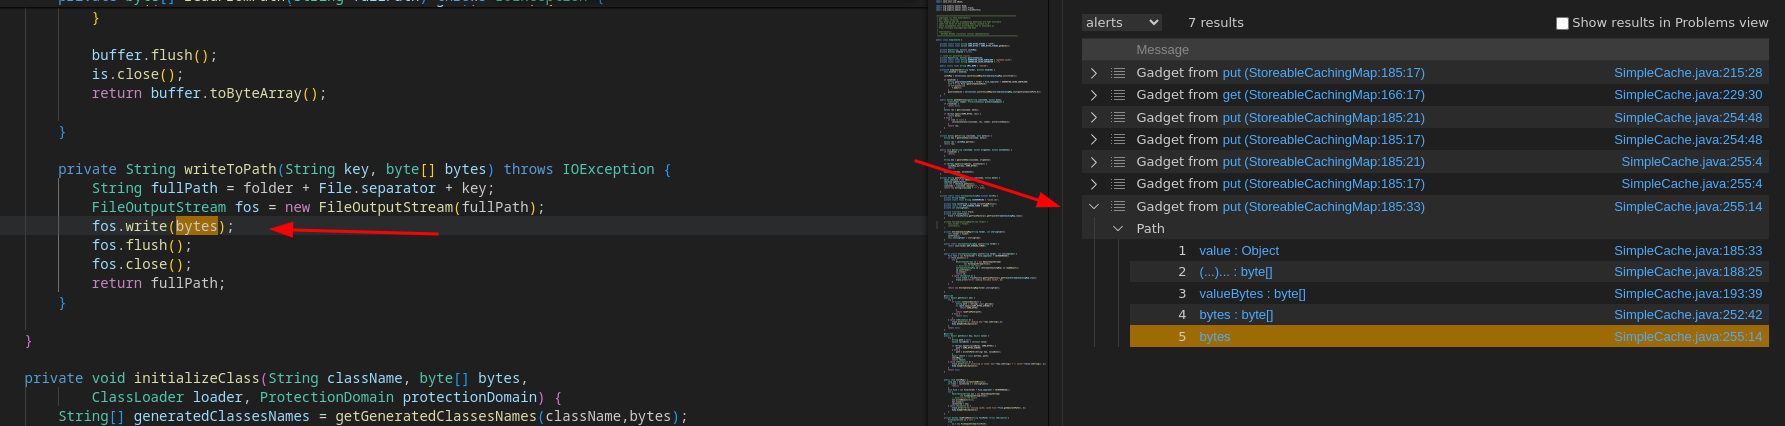
Finding Java/C# gadget chains with CodeQL

A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.

Generate malicious files using recently published bidi-attack (CVE-2021-42574)

library for importing functions from dlls in a hidden, reverse engineer unfriendly way