

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
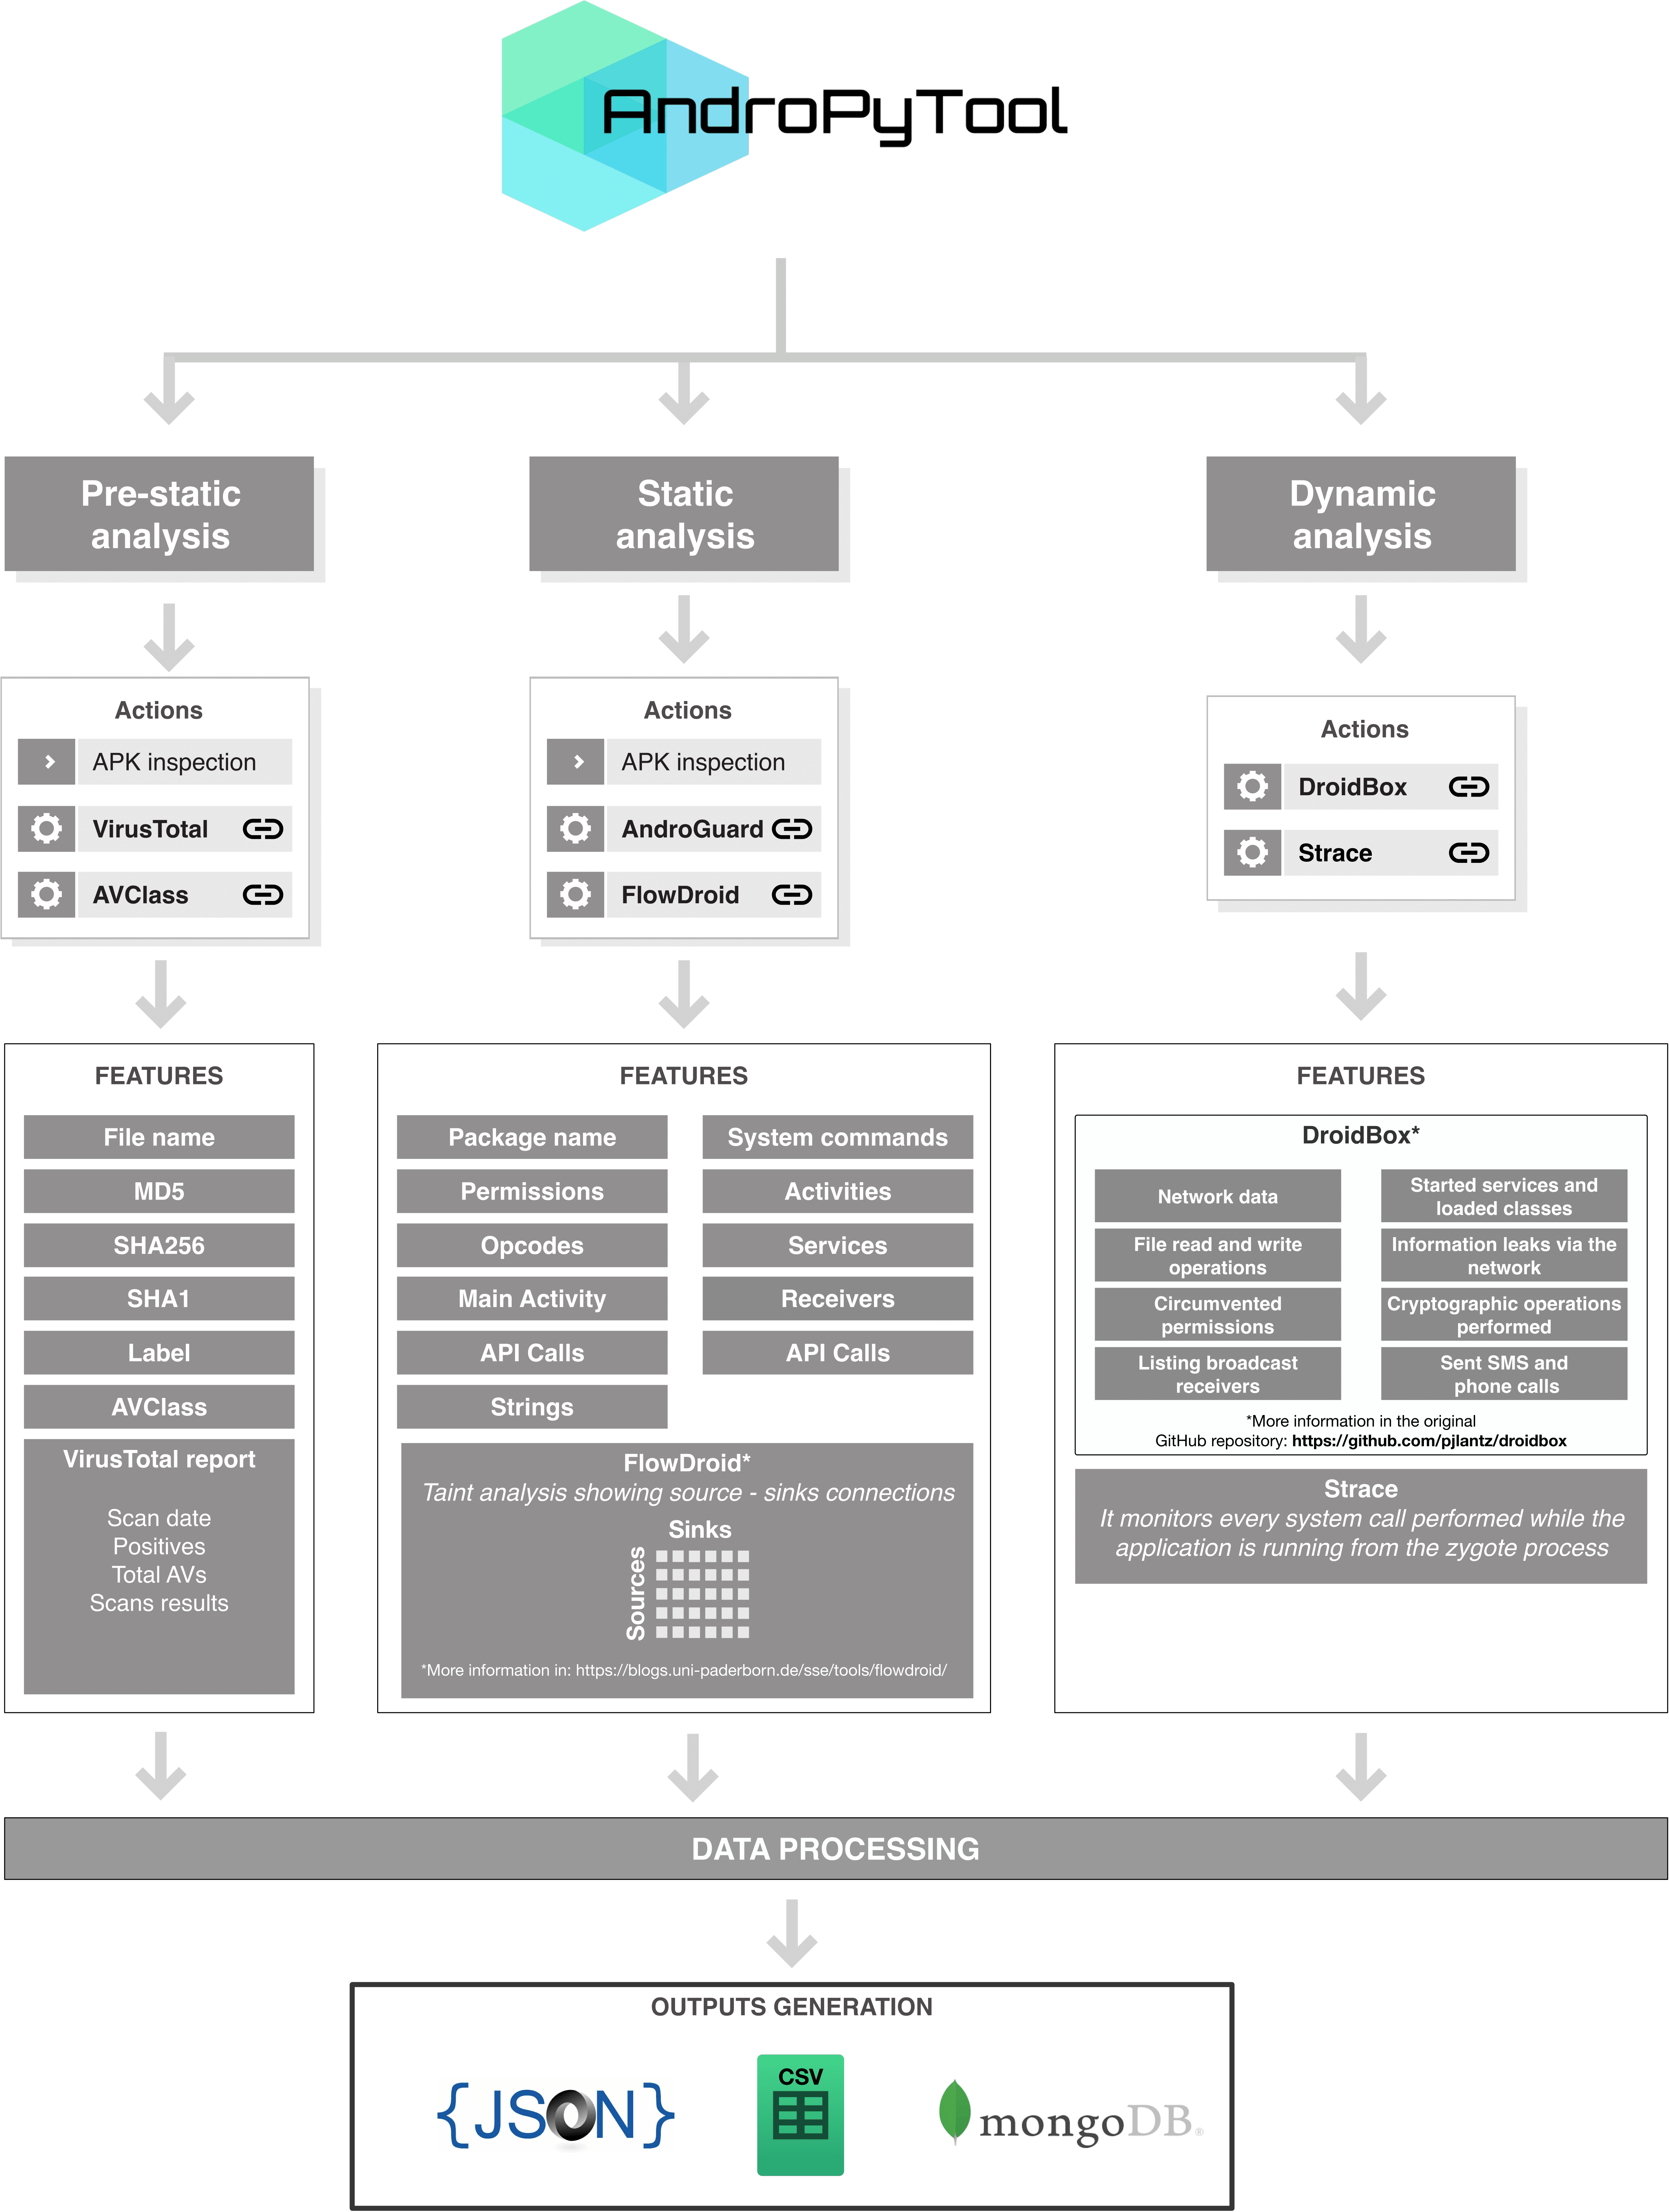 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 darioi/droidcarve
Android Reverse Engineering Framework
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
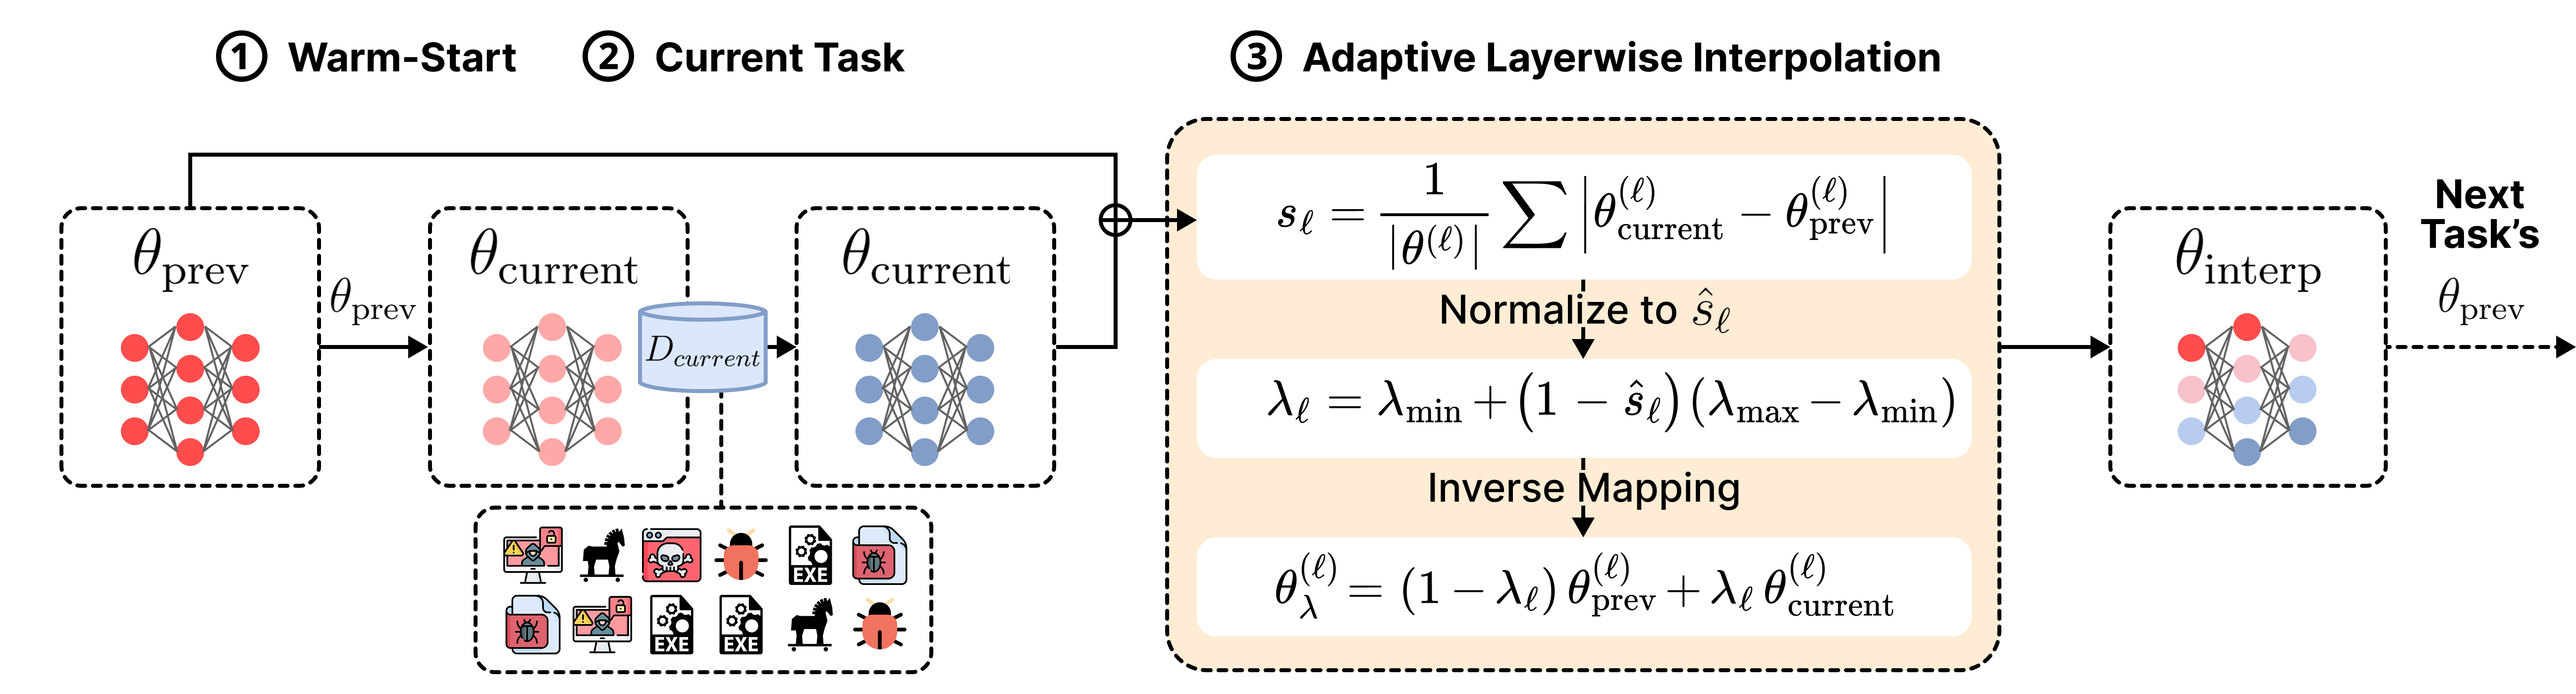 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 raptor-audit/raptor
Framework for auditing blockchain ecosystems, identifying smart contract vulnerabilities, and generating structured findings with multi-platform…
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 androbugs/androbugs_framework
AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…
 angr/angr
A powerful and user-friendly binary analysis platform!
 stefan2200/aparoid
Static and dynamic Android application security analysis
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool