

ScratchABit
 pfalcon/scratchabit
Easily retargetable and hackable interactive disassembler with IDAPython-compatible plugin API
binary-analysisdebuggersreverse-engineering+1
413
pfalcon/scratchabitEasily retargetable and hackable interactive disassembler with IDAPython-compatible plugin API
 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 ityonemo/clr
Checker for Lifetimes and other Refinement types
 tylabs/qs_old
Command line tool for scanning streams within office documents plus xor db attack
 crytic/caracal
Static Analyzer for Starknet smart contracts
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
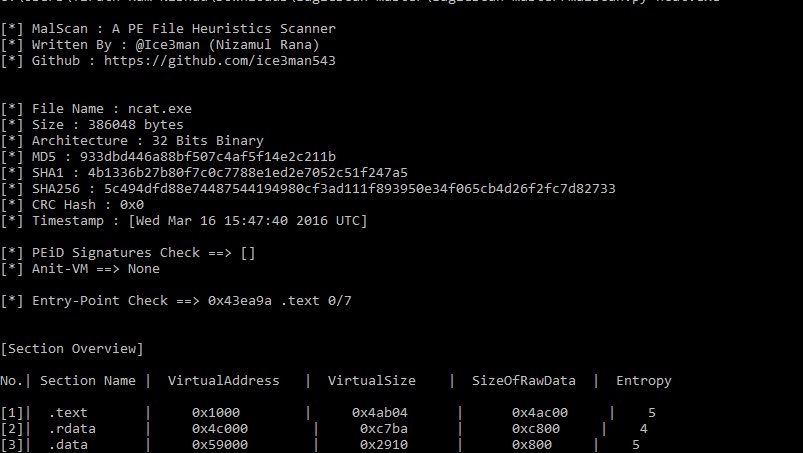 ice3man543/malscan
A Simple PE File Heuristics Scanners
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days
 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 oblivionsage/elfpeek
Minimal ELF inspector written in C for quick binary layout inspection